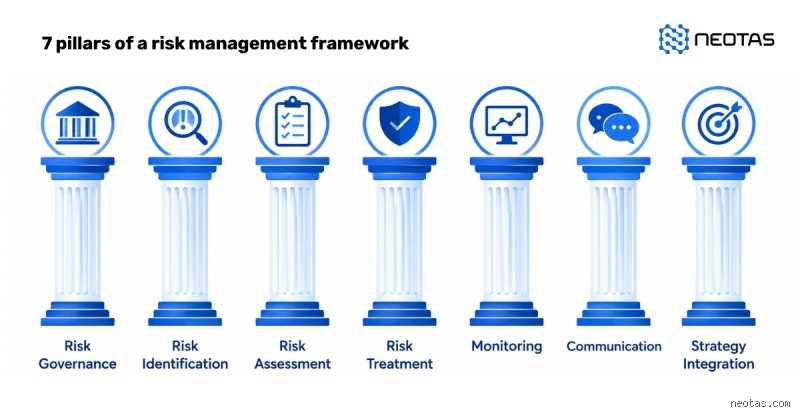
A risk management framework provides the foundational structure, governance mechanisms, methodologies, and feedback loops necessary to identify, assess, prioritize, mitigate, and monitor risks across the entire enterprise. Without a standardized framework, organizations inevitably fall prey to fragmented risk postures, where individual business units manage hazards in isolation, leadership lacks aggregated visibility, and emerging vulnerabilities slip through the structural cracks.
To build a robust, enduring, and agile defense against uncertainty, leading organizations design their governance models around seven key components of a risk management framework.
Component 1: Governance, Culture, and Tone at the Top
The most meticulously designed quantitative models, sophisticated risk registers, and automated monitoring tools are fundamentally powerless without an overarching institutional culture that prioritizes risk awareness and accountability. Therefore, the bedrock of any world-class risk management framework is Governance, Culture, and Tone at the Top.
Establishing clear accountability via the Three Lines Model
Governance begins with a transparent, unambiguous division of responsibilities. Modern risk governance heavily relies on the Three Lines Model (an evolution of the traditional Three Lines of Defense), which delineates roles among operational management, risk oversight functions, and internal auditing:
First Line (Operational Management): Business unit leaders, product owners, and operational teams own the risks directly generated by their day-to-day activities. They are responsible for designing and executing day-to-day controls and operating within established risk appetite boundaries.
Second Line (Risk Management and Compliance): Dedicated risk management, legal, and compliance functions establish the framework, define policies, provide independent oversight, and challenge the risk assumptions made by the first line. Crucially, the second line does not manage the risks directly; instead, they ensure that the first line manages them effectively.
Third Line (Internal Audit): Operating with total independence from both operational management and the risk management function, internal audit provides objective assurance on the overall effectiveness of governance, risk management, and internal control processes.
Cultivating psychological safety and Risk transparency
Culture is often described as "how things are done around here when no one is watching." In a healthy risk culture, bad news travels fast. Organizations must foster an environment of psychological safety where employees at all levels feel empowered, and legally protected, to raise their hands when they spot operational friction, ethical lapses, compliance breaches, or unmanaged vulnerabilities.
When leadership actively rewards transparency, treats failures as vital learning opportunities, and refuses to shoot the messenger, the enterprise builds a resilient immune system against systemic risk. Conversely, a toxic culture characterized by fear, overconfidence, and a "shoot for the numbers at all costs" mentality inevitably breeds catastrophic blind spots.
Component 2: Risk Appetite and Strategic Alignment
Risk management is not about eliminating every possible hazard; it is about making informed, calculated choices regarding which risks to accept, which to mitigate, and which to avoid entirely in pursuit of organizational objectives. This requires a crystal-clear articulation of Risk Appetite and Strategic Alignment.
Defining Risk Appetite and Risk tolerance
Risk appetite represents the aggregate level and types of risk that an organization is willing to accept in pursuit of its strategic objectives. It is a qualitative and quantitative statement of the board's and executive leadership's risk-taking philosophy.
While risk appetite defines the broad boundary lines at the macroeconomic level, risk tolerance drills down into specific, tactical boundaries. For example, an enterprise might have a high risk appetite for entering emerging technology markets, but it maintains a near-zero risk tolerance for compliance breaches regarding customer data privacy (e.g., GDPR or CCPA mandates).
Integrating Risk into Strategic planning
Too often, risk management is treated as an operational back-office function disconnected from the boardroom. A mature framework bridges this gap by embedding risk discussions directly into the strategic planning lifecycle:
Scenario Testing During Strategy Formulation: Before committing capital to a major expansion or merger, leadership must subject the strategic thesis to rigorous stress testing and "pre-mortems." Ask: If this strategy fails, what are the exact vectors of failure, and can the organization absorb the financial and reputational blow?
Dynamic Thresholds: Risk appetites must not remain static documents gathering dust on a shelf. They must evolve dynamically as market conditions shift, regulatory landscapes change, and the company's internal risk maturity matures.
Component 3: Comprehensive Identification and Taxonomy
You cannot manage what you do not see. The third pillar of a resilient risk management framework is systematic, exhaustive Risk Identification and Taxonomy. Organizations face a dizzying array of threats, ranging from predictable operational hazards to "black swan" systemic shocks. To categorize, analyze, and communicate these risks effectively, enterprises must establish a standardized risk taxonomy.
Categorizing the Risk universe
A well-structured risk taxonomy breaks down the enterprise threat landscape into logical domains, ensuring that no critical area is overlooked. Typical domains include:
Strategic Risk: Hazards related to high-level business decisions, such as failed mergers, shifting customer preferences, disruptive competitor innovations, or flawed long-term capital investments.
Operational Risk: Risks stemming from inadequate or failed internal processes, people, systems, or external events. This encompasses supply chain disruptions, human error, fraud, physical facility damage, and third-party vendor failures.
Financial Risk: Exposures driven by market fluctuations, credit defaults, liquidity shortages, and adverse interest rate or foreign exchange movements.
Compliance and Legal Risk: Vulnerabilities arising from violations of laws, regulatory mandates, industry standards, contractual obligations, or unexpected litigation.
Cybersecurity and Technological Risk: Threats related to data breaches, ransomware attacks, cloud outages, legacy system vulnerabilities, and artificial intelligence governance failures.
Active Identification methodologies
Organizations cannot rely solely on passive observation to uncover risks. A robust framework mandates active, continuous identification techniques:
Bottom-Up Risk Assessments: Workshops, surveys, and structured interviews with frontline employees who understand day-to-day operational realities.
Top-Down Enterprise Risk Assessments: Executive-led evaluations focusing on macro trends, regulatory shifts, and high-level strategic threats.
Loss Event Data Analysis: Post-incident reviews examining historical near-misses and actual loss events to ensure the same failures do not recur.
Emerging Risk Horizon Scanning: Utilizing artificial intelligence, predictive analytics, and expert advisory networks to monitor regulatory changes, geopolitical tensions, and technological breakthroughs before they directly impact operations.
Looking ahead to part 2
Establishing governance, setting risk appetite boundaries, and cataloging the organizational risk universe lay the crucial groundwork for an enterprise risk engine. However, identifying risks is only half the battle; organizations must possess the analytical rigor to evaluate their potential impact, deploy effective controls, monitor real-time indicators, and maintain continuous reporting.
In the upcoming second part of this expert guide, we will examine the remaining four pillars of a comprehensive risk management framework: Quantitative and Qualitative Risk Assessment, Risk Mitigation and Control Design, Monitoring, Key Risk Indicators (KRIs), and Reporting, and Continuous Review, Auditing, and Technological Integration.
...building upon the foundational elements of governance, identification, and quantitative or qualitative analysis, an enterprise risk management framework reaches its operational core through structured execution and oversight.
4. Risk Mitigation and treatment
Once risks have been identified, measured, and prioritized based on their potential impact and likelihood, organizations must determine how to respond. Risk mitigation involves selecting and implementing control measures to modify the risk.
There are generally four classic pathways for risk treatment:
Avoidance: Eliminating the activity, asset, or exposure entirely because the risk exceeds the organization's risk appetite.
Reduction (Mitigation): Taking proactive steps to lessen the probability of occurrence or the severity of the potential impact (e.g., implementing multi-factor authentication or upgrading infrastructure).
Transfer: Shifting the financial burden or operational responsibility of the risk to a third party, such as purchasing cyber insurance or outsourcing a high-risk operational function.
Acceptance: Acknowledging the risk because the cost of treatment outweighs the potential loss, or because the residual risk falls safely within acceptable tolerances.
Selecting the right treatment requires a cost-benefit analysis, ensuring that the resources deployed for mitigation align with the actual value protected.
5. Monitoring and Review
A risk management framework is not a static document that sits on a shelf; it is a dynamic, living system. External threats, regulatory landscapes, and internal business objectives evolve continuously, meaning risk profiles shift over time.
The monitoring and review component establishes mechanisms to track known risks, evaluate the ongoing effectiveness of implemented controls, and spot emerging vulnerabilities. This involves key risk indicators (KRIs), routine internal audits, and automated compliance tracking. Regular reviews ensure that if a control fails or a new threat vector appears, the organization can pivot its strategy rapidly rather than waiting for an annual review cycle.
6. Communication and Reporting
Transparency and accountability rely heavily on robust communication channels. Risk data must flow seamlessly across all levels of an organization, from front-line operational teams to executive leadership and the board of directors.
Effective reporting translates complex technical risk metrics into actionable business insights. Dashboards, heat maps, and regular risk register updates ensure that decision-makers understand their current risk exposure, the status of mitigation projects, and any urgent anomalies. External communication protocols must be established to keep regulators, shareholders, and stakeholders informed when material risk events occur.
7. Continuous improvement and Culture
The final pillar of a mature risk management framework is the commitment to continuous evolution and the cultivation of a risk-aware culture. Organizations must conduct post-incident reviews following any disruptive event to learn what failed and how the framework can be strengthened.
At an institutional level, fostering a healthy risk culture means ensuring that employees at every tier feel empowered to report vulnerabilities, question unsafe practices, and prioritize long-term resilience over short-term shortcuts. When risk management is embedded into the core organizational mindset, the framework transforms from a compliance checklist into a strategic advantage that drives sustainable, secure growth.