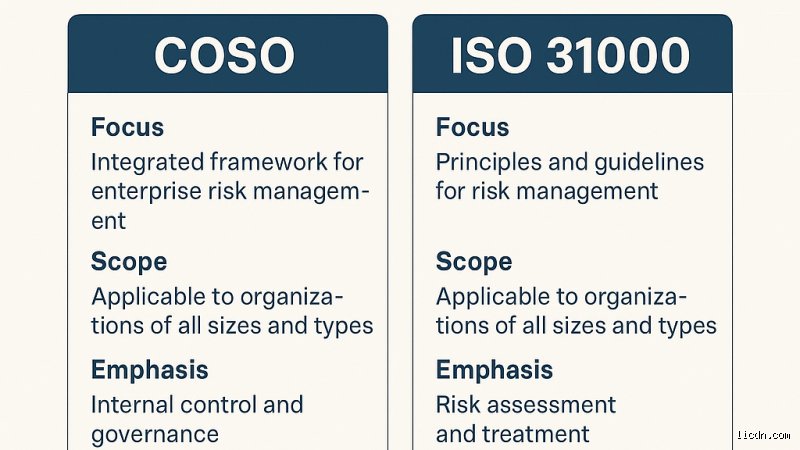
Navigating the Risk landscape: The evolution and philosophy of Enterprise Risk Management
While both frameworks share the ultimate objective of helping organizations identify, assess, and mitigate risks that threaten their strategic goals, their DNA, structural philosophies, and target audiences differ significantly. Understanding these nuances is essential for risk professionals, board members, and executive leaders who need a framework that matches their organization’s culture, regulatory environment, and maturity level.
The COSO ERM Framework: Integrating Risk with Strategy and Performance
The Committee of Sponsoring Organizations of the Treadway Commission (COSO) released its landmark Internal Control–Integrated Framework in 1992, followed by the initial Enterprise Risk Management–Integrated Framework in 2004. Recognizing that the risk landscape had evolved dramatically—pushed by digital transformation, complex supply chains, and unprecedented macroeconomic volatility—COSO released a major update in 2017 titled Enterprise Risk Management, Integrating with Strategy and Performance.
COSO’s defining philosophy is its explicit linkage between risk management and value creation. It posits that risk cannot be viewed in isolation from strategy; rather, risk is inherently embedded in the strategic choices an organization makes and its execution of those choices.
The 2017 COSO framework is structured around five interconnected components supported by twenty principles:
Governance and Culture: Sets the tone at the top, reinforcing the board's oversight responsibilities and defining the desired organizational culture, behavioral expectations, and commitment to integrity and ethical values.
Strategy and Objective-Setting: Requires organizations to evaluate risk while formulating their business strategy. This component ensures that the strategic objectives align with the organization's mission and vision while staying within its established risk appetite.
Performance: Focuses on the identification and assessment of risks that may impact the achievement of strategy and business objectives. Risks are prioritized by severity, and portfolio views of risk are established to understand how different risks interact.
Review and Revision: Examines how well the ERM practices are performing over time, prompting necessary adjustments in light of changing business contexts, internal transformations, and evolving threat vectors.
Information, Communication, and Reporting: Emphasizes the continuous flow of information up, down, and across the organization regarding risk, culture, and performance metrics to support informed decision-making.
COSO is deeply entrenched in the corporate governance fabric of North America and is heavily favored by publicly traded companies that must comply with rigorous internal control requirements (such as Sarbanes-Oxley). Its language is tailored heavily toward executive leadership, boards of directors, and financial stakeholders.
ISO 31000: The Universal, Principle-Driven standard
Published initially in 2009 by the International Organization for Standardization (ISO) and updated in 2018, ISO 31000: Risk management, Guidelines takes a fundamentally different structural approach. Unlike COSO, which carries deep roots in accounting, auditing, and financial internal controls, ISO 31000 was designed from the ground up as a truly universal, highly adaptable standard applicable to any organization, regardless of size, sector, industry, or geographic location.
ISO 31000 is not a rigid compliance checklist or a prescriptive control system; rather, it is a streamlined, principle-led guide designed to integrate seamlessly into any existing operational or managerial process.
The architecture of ISO 31000 rests on three distinct pillars:
The Principles of Risk Management: The foundational beliefs that create value. The standard asserts that risk management must be integrated, structured, comprehensive, customized, inclusive, dynamic, built on the best available information, and mindful of human and cultural factors.
The Framework: Designed to assist organizations in integrating risk management into their overall governance, strategy, planning, management, reporting, policies, values, and culture. It emphasizes leadership commitment, iterative design, and continuous evaluation.
The Process: A cyclical, hands-on operational workflow consisting of communication and consultation, establishing the scope/context, risk assessment (identification, analysis, and evaluation), risk treatment, and ongoing monitoring and review.
Because of its generalized, highly flexible architecture, ISO 31000 is widely embraced by global enterprises, government agencies, non-profits, and industries ranging from healthcare and engineering to manufacturing and higher education. It focuses less on what controls to implement and much more on how to cultivate an organizational mindset where risk-informed decision-making is second nature.
Structural architecture: Governance, Strategy, and integration
While both ISO 31000 and the COSO ERM (Enterprise Risk Management) frameworks share the fundamental objective of helping organizations systematically identify, assess, and mitigate risks to achieve their strategic goals, their underlying architectural philosophies diverge significantly. Understanding these structural differences is crucial for risk management professionals, internal auditors, and executive leadership teams tasked with implementing a robust governance system.
COSO ERM, officially titled Enterprise Risk Management, Integrating with Strategy and Performance, is explicitly built around the premise that risk cannot be separated from strategy and day-to-day business performance. Published by the Committee of Sponsoring Organizations of the Treadway Commission, COSO is heavily influenced by corporate governance, financial reporting requirements (historically tied to the Sarbanes-Oxley Act in the United States), and board-level oversight. Its architecture is organized into five interrelated components supported by twenty principles:
Governance and Culture: Sets the organization's tone, reinforcing the importance of risk awareness, board oversight, and ethical values.
Strategy and Objective-Setting: Integrates ERM with the strategic planning process, ensuring that business objectives align with the organization's stated risk appetite.
Performance: Identifies, assesses, and prioritizes risks that threaten the achievement of strategy and business objectives, developing appropriate risk responses.
Review and Revision: Evaluates how well the ERM practices are performing over time and what modifications are necessary in a dynamic operating environment.
Information, Communication, and Reporting: Focuses on continuous communication and leveraging technology to distribute risk insights across all operational layers.
In contrast, ISO 31000:2018 is designed as a universal, principles-based standard applicable to any type of organization, regardless of size, sector, or maturity. Rather than dictating a rigid structure or focusing predominantly on financial governance and strategic execution, ISO 31000 centers on creating and protecting value. Its architecture is built upon three core pillars:
Principles: Eight guiding tenets that characterize effective risk management (e.g., integrated, structured and comprehensive, customized, inclusive, dynamic, best available information, human and cultural factors, and continual improvement).
Framework: A blueprint that assists organizations in integrating risk management into their overall governance, leadership, planning, management, reporting, policies, and values.
Process: An iterative, step-by-step risk management workflow comprising communication and consultation, scope/context/criteria definition, risk assessment (identification, analysis, evaluation), risk treatment, and monitoring/review.
Process execution and practical application
When operationalized on the ground, the divergence in architecture translates into distinct workflows and expectations for risk practitioners.
COSO ERM treats risk management as an inherent part of corporate performance. When an enterprise sets its strategic plan, COSO demands that leadership explicitly evaluate the riskiness of that strategy. If the strategy requires aggressive expansion into volatile markets, COSO evaluates whether the organization's risk appetite accommodates that volatility. The framework places heavy emphasis on the concept of risk appetite as a boundary that guides decision-making at every organizational tier.
ISO 31000, meanwhile, views risk management as a core component of all organizational activities. Its process-oriented workflow is deeply practical and modular. The ISO risk assessment phase breaks down into three distinct sub-stages:
Risk Identification: Finding, recognizing, and describing risks that might help or prevent an organization from achieving its objectives.
Risk Analysis: Understanding the nature of risk and determining the level of risk, combining considerations of likelihood and consequence.
Risk Evaluation: Comparing the results of risk analysis with the established risk criteria to determine where additional action is required.
ISO 31000 explicitly incorporates both threats and opportunities. While COSO also addresses opportunities (defining risk as the possibility that events will occur and affect the achievement of strategy), ISO 31000's definition explicitly frames risk as the "effect of uncertainty on objectives," where an effect can be positive, negative, or a duality of both.
Comprehensive comparison matrix
To clearly distinguish between the two frameworks across key operational and strategic dimensions, consider the following comparative analysis:
| Dimension | ISO 31000:2018 | COSO ERM (2017) |
|---|---|---|
| Origin & Authority | International Organization for Standardization (ISO); voluntary global standard. | Committee of Sponsoring Organizations (U.S. private-sector initiative, highly influential in accounting/audit). |
| Primary Focus | Universal applicability; value creation and protection across any organizational activity. | Integration of risk with strategy, business performance, and corporate governance. |
| Core Structure | 8 Principles, a supporting Framework, and a 5-step iterative Risk Management Process. | 5 Components and 20 Principles mapped to operational and strategic lifecycles. |
| Target Audience | Risk managers, operational leaders, and organizations seeking an adaptable, scalable risk standard. | Boards of directors, executive management, internal auditors, and US-regulated corporations. |
| Compliance & Audit | Can be audited for alignment/maturity, but is not a certification standard for compliance. | Frequently utilized by internal audit functions to evaluate internal controls and governance maturity. |
| View of Risk | Uncertainty that can have positive (opportunity) or negative (threat) effects on objectives. | Possibility of events occurring that affect the achievement of strategy and business objectives. |
Culture, leadership, and human factors
An often-overlooked difference lies in how each framework addresses organizational culture and human behavior.
COSO ERM addresses culture under its first component (Governance and Culture). It emphasizes tone at the top, ethical behavior, board oversight, and the commitment of leadership to reinforcing risk awareness. It views culture through the lens of corporate accountability and alignment with stakeholder expectations.
ISO 31000 takes a more expansive, behavioral approach. It explicitly highlights human and cultural factors as a core principle. ISO recognizes that human behavior and culture significantly influence all activities of an organization at every level. It pushes practitioners to look beyond formal policies and examine how cognitive biases, communication styles, informal networks, and employee engagement shape risk perception and decision-making.
Making the choice: Strategic selection and hybrid adoption
Choosing between ISO 31000 and COSO ERM depends heavily on an organization’s geographic footprint, regulatory environment, and maturity level.
Organizations operating in heavily regulated North American markets, particularly publicly traded companies accustomed to internal control frameworks like COSO's Internal Control Integrated Framework, often find COSO ERM a natural extension of existing compliance and audit structures. It speaks the language of the board, financial controllers, and external auditors.
Conversely, organizations seeking a flexible, non-prescriptive standard that can be seamlessly embedded into engineering, project management, supply chain, or international operations often lean toward ISO 31000. Because ISO 31000 does not require complex component-by-component scoring or rigid compliance checklists, it offers greater agility for organizations looking to build a tailored risk management culture from the ground up.
In practice, many advanced enterprises adopt a hybrid approach. They utilize the strategic alignment and governance rigor of COSO ERM at the executive and board levels while applying the granular, practical risk assessment processes of ISO 31000 across operational units, projects, and functional departments. By leveraging the strengths of both frameworks, organizations can build a resilient, comprehensive risk management ecosystem that protects value while driving sustainable growth.