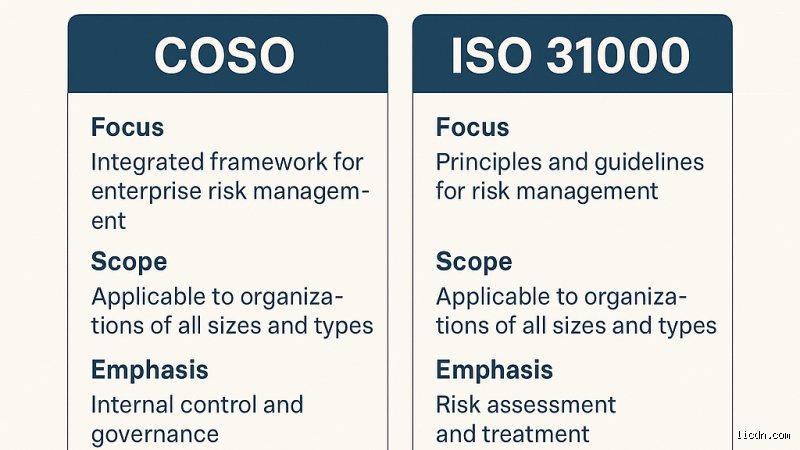
For risk leaders, board members, and chief executives tasked with selecting or refining this blueprint, two gold-standard frameworks inevitably emerge as the primary contenders: ISO 31000 and COSO ERM (Enterprise Risk Management—Integrating with Strategy and Performance). While both frameworks share the ultimate objective of safeguarding organizational resilience and enhancing long-term value, their philosophies, structural designs, operational mechanics, and cultural underpinnings diverge significantly.
Understanding these foundational differences is not merely an academic exercise; it is a strategic imperative. Selecting the wrong framework, or failing to adapt the right one to your organization’s unique culture, geography, and regulatory obligations, can result in bureaucratic bloat, siloed compliance exercises, or, worse, blind spots that expose the enterprise to catastrophic failure.
1. Philosophical origins and institutional DNA
To truly understand why ISO 31000 and COSO ERM behave differently in practice, one must examine where they came from and who built them. A framework’s institutional DNA heavily dictates its bias, its target audience, and its operational flavor.
ISO 31000: The global, Principles-Based universalist
Published initially in 2009 and updated significantly in 2018, ISO 31000 is a product of the International Organization for Standardization (ISO). It was forged through a massive, multi-year international consensus process involving risk professionals, engineers, and management experts from dozens of countries across the globe.
Because of its international pedigree, ISO 31000 is inherently globally minded, sector-agnostic, and culturally neutral. It was designed to apply to any organization, regardless of size, structure, public or private status, geography, or industry sector. Whether applied by a municipal government in Scandinavia, a hospital network in South Africa, or an oil and gas conglomerate operating across Latin America, ISO 31000 provides a flexible, overarching vocabulary.
Crucially, ISO 31000 is principles-based and non-certifiable. Organizations cannot undergo an external audit to receive an "ISO 31000 Compliance Certificate" (unlike ISO 27001 for information security or ISO 9001 for quality management). Instead, it serves as an authoritative guide that organizations adapt to build their own custom internal policies, manuals, and risk procedures. Its creators approached risk from a broad management and operational standpoint, treating risk as the "effect of uncertainty on objectives" that can manifest as both downside threat and upside opportunity.
COSO ERM: The Governance-Driven, US-Legacy specialist
In contrast, COSO ERM originates from the Committee of Sponsoring Organizations of the Treadway Commission, an initiative jointly sponsored by five major US-based professional accounting and auditing associations (including the AICPA, IIA, and IMA). Historically, COSO’s primary claim to fame has been its Internal Control, Integrated Framework (often used to satisfy Sarbanes-Oxley [SOX] Section 404 compliance in the United States).
The original 2004 COSO ERM framework was heavily control-oriented. However, the landmark 2017 update (Enterprise Risk Management, Integrating with Strategy and Performance), developed with extensive input from advisory firms like PwC, modernized the framework to focus heavily on strategy, performance, and decision-making.
Despite this modernization, COSO retains its North American roots and governance-heavy DNA. It is heavily favored by publicly traded companies, highly regulated financial institutions, and organizations where internal audit committees and boards of directors demand rigorous oversight, structured documentation, and direct lines of accountability. COSO views risk management not just as an operational tool, but as an integral component of corporate governance that dictates how strategy is formulated, executed, and monitored.
2. Structural anatomy: How each Framework is built
When you open the guidance documents, the structural differences between the two frameworks become immediately striking, particularly regarding length, prescriptive detail, and layout.
The architecture of ISO 31000: Compact, scalable, and Process-Centric
True to its standardization heritage, ISO 31000 is remarkably concise. Spanning only about 16 pages of core standard text (supported by guidance like IEC 31010 for risk assessment techniques), it does not overwhelm the reader with dense bureaucratic checklists. The architecture rests on three inseparable, mutually reinforcing pillars:
The Principles: Eight foundational tenets that define what makes risk management effective. These include ideas such as "risk management creates and protects value," "it is systemic and structured," "it is tailored to the organization," and "it is dynamic and iterative."
The Framework: Designed to assist management in integrating risk into overall organizational structures and functions. It consists of six components: Leadership and Commitment, Integration, Design, Implementation, Evaluation, and Improvement.
The Process: A systematic, repeatable operational cycle for managing risk day-to-day. This includes establishing the scope/context, risk assessment (identification, analysis, evaluation), risk treatment, communication and consultation, and monitoring and review.
This lean structure allows organizations to "drop in" the ISO 31000 process engine into existing operational units without imposing heavy administrative burdens.
The architecture of COSO ERM: Comprehensive, Component-Driven, and prescriptive
COSO ERM is a much heavier, more exhaustive document, stretching well over 100 pages, complete with detailed visual models, tables, and structured breakdowns. It is organized around five interrelated components and twenty core principles, creating an interconnected matrix that touches virtually every corner of an enterprise:
Governance and Culture: Sets the organization's tone, reinforcing board oversight, ethical values, desired organizational behaviors, and human capital practices.
Strategy and Objective-Setting: Integrates ERM directly into the strategic planning phase, analyzing business context, defining risk appetite, and evaluating alternative strategies.
Performance: The operational heart of risk identification, assessment, and prioritization, tied directly to the achievement of performance targets.
Review and Revision: Assesses how well the ERM practices are functioning over time and identifies necessary adjustments as business conditions shift.
Information, Communication, and Reporting: Focuses on leveraging data, communication channels, and technology to enhance risk reporting across all levels of the enterprise.
Each of the twenty principles within these five components comes with specific points of focus, providing detailed behavioral and structural expectations. For organizations with high compliance maturity, this level of prescription is comforting; for agile, fast-moving enterprises, it can occasionally feel heavy or rigid.
3. Scope, Focus, and strategic alignment
Another major point of divergence between ISO 31000 and COSO ERM lies in how they define the relationship between risk, strategy, and overall corporate purpose.
ISO 31000: Broad Value Creation and operational agility
ISO 31000 explicitly states that the primary purpose of risk management is the creation and protection of value. It treats risk as an inherent aspect of all organizational activities, applying equally to a factory floor, a research lab, a software deployment cycle, or a board room.
Because ISO 31000 does not strictly mandate that risk be tied to high-level strategic objectives in a prescribed way, operating managers find it exceptionally user-friendly. It empowers local business units to manage operational uncertainties dynamically using a shared risk taxonomy, without forcing them through heavy corporate strategy filters.
COSO ERM: Tight Integration with Strategy and Performance
COSO ERM takes a more centralized view. Its core premise is that enterprise risk management is fundamentally intertwined with strategy-setting and execution. COSO asserts that an organization’s strategy should be evaluated through a risk lens before it is locked in, and that performance measures must account for the risk profile assumed to achieve those targets.
While ISO 31000 looks broadly at value creation across all domains, COSO is laser-focused on ensuring that the board of directors and executive leadership have direct visibility into how risk appetite dictates strategic choices. Consequently, COSO treats risk management heavily through the lens of governance, corporate oversight, and internal control structures.
End of Part I. In Part II of this analysis, we will explore the practical implementation trade-offs, cultural impacts, auditing expectations, and how leading global enterprises successfully combine both frameworks into a unified, hybrid ERM model.
Structural and architectural comparison: Principles vs. Components
To fully understand where ISO 31000 and COSO ERM diverge, one must examine their core architectures. While both frameworks aim to protect and create value within an organization, they approach the mechanics of risk management from fundamentally different starting points.
ISO 31000: The Principles-Based approach
ISO 31000 is built upon a foundation of eight core principles, five framework components, and a three-step risk management process (Identification, Analysis, Evaluation, alongside continuous monitoring, communication, and consultation).
Universality: Because ISO 31000 relies on high-level principles rather than rigid compliance structures, it can be applied to any organization regardless of size, sector, or maturity. It does not demand a specific organizational chart or a dedicated Chief Risk Officer (CRO); instead, it integrates risk management into existing management systems.
Value Creation and Protection: The overarching objective of ISO 31000 is explicitly stated as the creation and protection of value. Risk is defined broadly as the "effect of uncertainty on objectives," meaning that uncertainty can present both upside (opportunities) and downside (threats) impacts.
Dynamic Adaptation: The framework emphasizes that risk management is iterative, continuous, and responsive to changes in the internal and external context. It treats risk management not as an annual audit exercise, but as an ongoing operational habit.
COSO ERM: The component- and Objective-Based approach
COSO ERM (formally updated in 2017 as Enterprise Risk Management, Integrating with Strategy and Performance) is heavily structured around twenty principles organized into five interrelated components:
Governance and Culture: Sets the organization's tone, reinforcing the importance of risk awareness, board oversight, and ethical values.
Strategy and Objective-Setting: Integrates ERM directly into the strategic planning process, ensuring that business objectives align with the organization's risk appetite.
Performance: Focuses on identifying and assessing risks that threaten the achievement of strategy and business objectives, prioritizing...Building upon the structural foundations of ISO 31000 and COSO ERM, a comprehensive analysis requires looking beyond their definitions and examining how they address governance, cultural dynamics, and strategic integration in practice. While both frameworks aim to protect and create value for organizations, their philosophical approaches diverge significantly when operationalized across complex global enterprises.
Governance, Culture, and organizational behavior
Risk management is fundamentally a human endeavor; frameworks fail or succeed based on organizational culture and governance structures. How do ISO 31000 and COSO ERM approach the human element?
The COSO ERM perspective: Culture and Performance
The updated 2017 COSO ERM framework explicitly links enterprise risk management with Strategy and Performance, organizing its structure around five interconnected components:
Governance and Culture
Strategy and Objective-Setting
Performance
Review and Revision
Information, Communication, and Reporting
COSO places Governance and Culture at the very bedrock of its model. Culture pertains to ethical values, desired behaviors, and understanding of risk in the entity. COSO explicitly ties risk to strategy execution, arguing that culture dictates how an organization evaluates business opportunities and handles missteps. It emphasizes board oversight, tone at the top, and defining operating structures that reinforce accountability.
The ISO 31000 perspective: Principles and Integration
ISO 31000:2018 is built around eight core principles, a framework, and a process. The principles dictate that risk management must be:
Integrated
Structured and comprehensive
Customized
Inclusive
Dynamic
Best available information
Human and cultural factors
Continual improvement
Rather than prescribing specific governance components, ISO 31000 treats leadership and commitment as the core drivers that integrate risk management into every part of the organization's governance structure. It explicitly highlights human and cultural factors, recognizing that human behavior and capabilities significantly influence risk management at all levels and times.
Strategic planning and Value Creation
A major evolution in modern risk management is the shift from risk avoidance (defensive compliance) to risk optimization (offensive value creation).
COSO ERM views risk through the lens of strategy. It asks: How does risk affect our ability to achieve our strategic objectives? It helps organizations evaluate alternative strategies, understand the implications of strategy on risk profiles, and manage performance variations. If an organization's primary goal is aligning risk with long-term strategic growth and shareholder value, COSO provides a rigorous, objective-driven blueprint.
ISO 31000 views risk more broadly as the effect of uncertainty on objectives. Objectives can be strategic, operational, financial, or reputational. ISO 31000 is intentionally agnostic to the specific nature of the objectives, making it equally applicable to a multi-billion-dollar enterprise, a non-profit foundation, or a local government agency managing infrastructure projects.
Reporting, Communication, and assurance
Transparency and communication loops ensure that risk information flows effectively from the front lines to the boardroom.
COSO maintains a strong legacy connection to internal control and financial reporting (stemming from the original 1992 COSO Internal Control framework). Consequently, COSO-based ERM naturally integrates with internal audit functions, Sarbanes-Oxley (SOX) compliance, and formal regulatory reporting requirements. It emphasizes periodic review, revision, and robust communication channels.
ISO 31000 promotes ongoing reporting and communication as part of the iterative risk management process. Because ISO emphasizes continuous monitoring and adaptation, its communication guidelines are designed to be dynamic and embedded within regular operational reporting rather than periodic compliance checks.
Implementation methodology: Choosing the right fit
Selecting between ISO 31000 and COSO ERM depends heavily on an organization's regulatory environment, geographic footprint, and existing internal architecture.
| Feature | ISO 31000:2018 | COSO ERM (2017) |
|---|---|---|
| Origin & Scope | International standard; universally applicable across all industries and entity types. | US-centric origins (COSO); heavily tailored for corporations, governance, and financial markets. |
| Primary Focus | Managing uncertainty and protecting/creating value through continuous principles and processes. | Integrating risk with strategy-setting, business performance, and corporate governance. |
| Structure | 8 Principles, a Framework, and a 5-step Process loop. | 5 Components and 20 Principles mapped to strategy and performance. |
| Compliance & Audit | Often used for management system certification (though ISO 31000 itself is not certifiable). | Closely aligns with internal control frameworks, audit committees, and regulatory compliance (e.g., SEC, SOX). |
| Flexibility | Highly adaptable due to its high-level, principles-based nature. | More prescriptive framework with structured components and principles. |
When to choose ISO 31000
Your organization operates globally and needs a framework that easily bridges diverse regulatory regimes and organizational types (public, private, or non-profit).
You already utilize other ISO management systems (such as ISO 9001 for quality or ISO 27001 for information security) and want seamless integration.
You require a flexible, scalable approach that can be tailored to specific projects, business units, or operational silos without heavy mandatory structures.
When to choose COSO ERM
Your organization is publicly traded, heavily regulated in the United States, or tightly bound to formal corporate governance mandates and audit committee oversight.
You want to explicitly couple your risk management processes directly with strategic planning, enterprise performance management, and executive compensation metrics.
Your stakeholders (investors, board members, regulators) are already familiar with COSO Internal Control frameworks and expect a unified governance vocabulary.
Conclusion and strategic synthesis
ISO 31000 and COSO ERM are not mutually exclusive enemies; they are complementary philosophies. Many sophisticated global enterprises adopt a hybrid approach, using the high-level, flexible principles of ISO 31000 to guide operational risk management across diverse global business units, while leveraging COSO ERM at the corporate executive level to satisfy rigorous board governance, strategic planning, and internal audit requirements.
Whichever framework an organization selects, the true differentiator of risk management success is not the documentation or the structural diagram on a slide deck. It is the cultivation of an open, resilient organizational culture where uncertainty is anticipated, risks are transparently evaluated, and decisions are made with a clear-eyed understanding of both potential rewards and consequences.