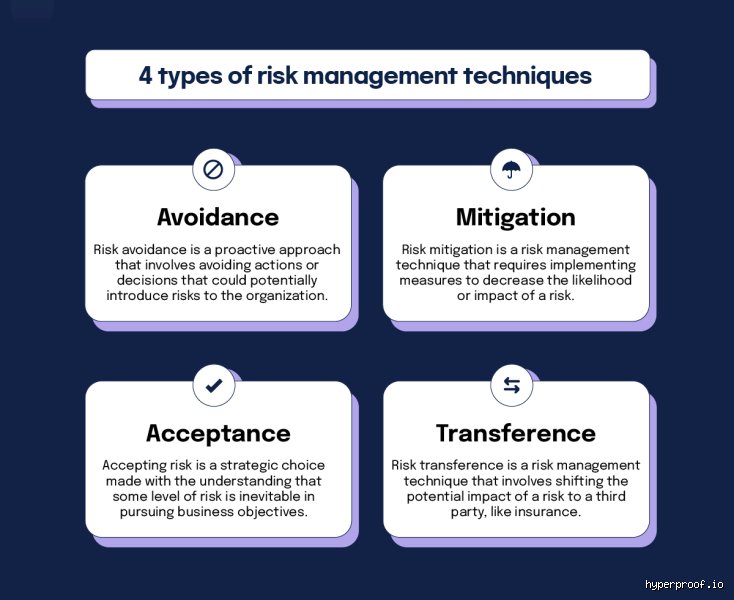
Risk management is no longer merely a defensive compliance checkbox confined to the back-office auditing department. Today, it has evolved into a strategic discipline that permeates every tier of an enterprise, from the boardroom to the front lines of daily operations. By systematically identifying, evaluating, and mitigating potential threats while simultaneously capitalizing on strategic opportunities, risk management provides leaders with the clarity and confidence needed to navigate complex environments.
To implement an effective risk management framework, organizations must first recognize that risk is not a monolithic entity. It manifests in diverse forms across different domains, requiring specialized approaches, methodologies, and expertise. This comprehensive first part of our expert guide explores the primary types of risk management, detailing how organizations classify, approach, and govern the multifaceted spectrum of uncertainty they encounter daily.
1. Enterprise Risk Management (ERM): The holistic blueprint
At the pinnacle of modern organizational governance sits Enterprise Risk Management (ERM). Unlike traditional, siloed approaches where individual departments managed their own localized hazards independently, ERM provides a coordinated, top-down, and comprehensive framework for managing all risks that could impact an organization’s ability to achieve its overarching strategic objectives.
The philosophy and scope of ERM
ERM shifts the organizational mindset from viewing risk purely as a threat to be avoided toward viewing it as a variable that must be balanced against potential rewards. It encompasses every department, business unit, and subsidiary, creating a unified risk taxonomy and a shared language across the enterprise.
By integrating risk management into strategic planning, capital allocation, and operational execution, ERM ensures that leadership does not make decisions in a vacuum. For example, when a retail corporation considers expanding into an international market, ERM evaluates not only the financial capital required but also the interplay of currency volatility, regulatory compliance, supply chain vulnerabilities, and reputational risks associated with the new demographic.
Core components of an ERM Framework
A robust ERM structure typically aligns with internationally recognized standards, such as the COSO (Committee of Sponsoring Organizations of the Treadway Commission) framework or ISO 31000. These standards emphasize several interconnected components:
Governance and Culture: Establishing a tone from the top where ethical behavior, risk awareness, and accountability are embedded in the corporate culture. The Board of Directors and executive leadership set the risk appetite, the amount of risk an organization is willing to accept in pursuit of its value creation goals.
Strategy and Objective-Setting: Aligning risk management with the organization's mission and strategic vision. This involves evaluating alternative strategies and ensuring that the chosen path does not expose the enterprise to catastrophic, unmitigated downsides.
Performance and Risk Identification: Systematically identifying events that could positively or negatively affect objective achievement. Risks are assessed based on their likelihood of occurrence and their potential impact (severity).
Review and Revision: Continuously monitoring the performance of risk management practices, adapting to changing market conditions, and updating risk profiles in real-time.
Information, Communication, and Reporting: Ensuring that relevant risk data flows seamlessly across all levels of the organization, enabling swift, informed decision-making.
By treating risk holistically, ERM breaks down organizational silos, prevents redundant risk mitigation efforts, and provides stakeholders, investors, and regulators with a transparent view of the organization's risk profile.
2. Financial Risk Management: Safeguarding the bottom Line
While ERM provides the overarching strategic umbrella, Financial Risk Management dives deep into the specific monetary and market-driven exposures that can threaten an organization's liquidity, solvency, and profitability. Financial risk is inherent in any business activity involving capital, credit, or cash flow.
Key categories of Financial Risk
Financial risk management focuses on several distinct sub-categories of exposure:
Market Risk: The possibility of losses resulting from adverse movements in market prices. This includes interest rate risk (how fluctuations in central bank rates impact borrowing costs and bond portfolios), foreign exchange (FX) risk (the vulnerability of international cash flows to currency exchange rate swings), and commodity price risk (how changes in the cost of raw materials like oil, steel, or agricultural goods affect profit margins).
Credit Risk: The risk that a counterparty, customer, or debtor will fail to meet their contractual obligations in accordance with agreed terms. This is a primary concern for commercial banks, lending institutions, and any business that extends trade credit to its customers.
Liquidity Risk: Divided into funding liquidity risk (the inability to meet short-term financial obligations when they come due, even if the firm is fundamentally solvent) and market liquidity risk (the inability to buy or sell an asset quickly enough without significantly impacting its market price).
Strategies and instruments in Financial Risk Management
To mitigate these exposures, financial risk managers employ a sophisticated suite of quantitative tools and financial instruments:
Hedging: Utilizing derivative contracts, such as forwards, futures, options, and swaps, to offset potential losses in physical or financial assets. For instance, an airline might use fuel futures to lock in jet fuel prices, protecting itself against sudden spikes in crude oil markets.
Value at Risk (VaR): A statistical technique used to measure and quantify the level of financial risk within a firm, portfolio, or position over a specific time frame. VaR answers the question: "What is my maximum expected loss, with a given level of confidence, over a normal market period?"
Stress Testing and Scenario Analysis: Simulating extreme, low-probability macroeconomic events (such as a severe recession, a sudden sovereign debt crisis, or a major geopolitical conflict) to evaluate how resilient the organization's capital reserves and cash flows would be under severe duress.
Effective financial risk management ensures that an organization maintains adequate capital buffers, optimizes its cost of capital, and remains financially resilient through economic cycles.
3. Operational Risk Management (ORM): Managing the internal engine
Every organization relies on a complex web of internal processes, human resources, technological systems, and external events to deliver its products and services. When these internal components fail, Operational Risk Management (ORM) steps in to identify, assess, and mitigate the resulting vulnerabilities.
Defining Operational Risk
The Basel Committee on Banking Supervision famously defined operational risk as "the risk of loss resulting from inadequate or failed internal processes, people and systems or from external events." Unlike financial risk, which can often be actively traded or hedged in open markets, operational risk is internal, ubiquitous, and frequently harder to quantify.
ORM breaks operational failures down into four primary root causes:
People: Human error, inadequate training, insider threats, high employee turnover, or unethical conduct.
Processes: Flawed internal workflows, inadequate quality control, regulatory non-compliance, or poor project management.
Systems: Technological outages, software bugs, hardware failures, and legacy infrastructure breakdowns.
External Events: Natural disasters, supply chain disruptions, geopolitical unrest, or criminal actions (such as physical theft or vandalism).
Methodologies for effective ORM
Managing operational risk requires a proactive approach centered on process resilience and continuous improvement:
Risk and Control Self-Assessments (RCSA): A bottom-up process where business units evaluate their own operational risks and the effectiveness of the internal controls designed to mitigate them. This encourages operational ownership and accountability at the grassroots level.
Key Risk Indicators (KRIs): Metrics used by organizations to provide an early warning signal of increasing operational risk exposures in various areas of the business. Examples include the number of system downtime hours, employee error rates, or unaddressed audit findings.
Loss Data Collection (LDC): Systematic tracking and analysis of historical operational loss events. By studying past failures, root-cause analyses can be performed to ensure that the same operational breakdown does not occur twice.
Business Continuity Planning (BCP) and Disaster Recovery (DR): Establishing comprehensive protocols to ensure that an organization can continue operating or quickly resume mission-critical functions in the aftermath of a severe operational disruption, such as a fire at a primary manufacturing plant or a widespread electrical grid failure.
4. Cybersecurity and Information Risk Management
In the twenty-first century, data is one of an organization’s most valuable assets, and digital infrastructure is its most vulnerable frontier. Cybersecurity and Information Risk Management has evolved from a specialized IT sub-discipline into a board-level imperative, driven by the exponential growth of digital transformation, cloud computing, and remote workforces.
The expanding threat vector
Information risk encompasses the threats to the confidentiality, integrity, and availability (the classic CIA triad) of an organization's data and digital systems. Modern information risk managers must contend with a rapidly evolving array of threats:
Ransomware and Malware: Sophisticated cyberattacks designed to encrypt organizational data, disrupt operations, and extort substantial financial payouts.
Phishing and Social Engineering: Psychological manipulation tactics aimed at deceiving employees into divulging sensitive credentials or authorizing fraudulent financial transactions.
Insider Threats: Risks posed by disgruntled, negligent, or compromised employees who possess legitimate access to sensitive corporate networks and intellectual property.
Supply Chain Cyber Vulnerabilities: Security breaches originating not within the primary organization itself, but through third-party vendors, software suppliers, or service providers who maintain access to corporate systems.
Frameworks for Information resilience
To counter these pervasive threats, information risk management relies on established standards and defensive architectures:
Risk Frameworks and Standards: Implementing frameworks such as the NIST (National Institute of Standards and Technology) Cybersecurity Framework, ISO/IEC 27001, and CIS Controls to establish structured benchmarks for security posture.
Defense-in-Depth: Deploying multi-layered security controls, including advanced firewalls, endpoint detection and response (EDR) software, rigorous identity and access management (IAM), multi-factor authentication (MFA), and zero-trust network architectures.
Vulnerability Management and Penetration Testing: Regularly scanning networks, applications, and hardware for known security flaws and employing ethical hackers to simulate real-world cyberattacks to uncover blind spots before malicious actors can exploit them.
Incident Response Planning (IRP): Formulating, testing, and refining clear operational protocols for containing, investigating, and recovering from security breaches when they inevitably occur.
5. Strategic and Reputational Risk Management
While operational, financial, and cyber risks deal largely with execution and protection, Strategic Risk Management (SRM) and Reputational Risk Management focus on the big picture: the long-term viability, vision, and public standing of the enterprise.
Strategic Risk: Navigating uncertainty in direction
Strategic risks are the uncertainties associated with an organization's high-level business decisions and strategic goals. If an executive team makes a major bet on a new product line, a massive merger or acquisition, or a complete pivot in business model, they are taking on strategic risk.
Strategic risk management involves:
Disruption Sensing: Monitoring macroeconomic, technological, and consumer trends to anticipate disruptive forces (such as artificial intelligence or changing sustainability expectations) that could render an existing business model obsolete.
Alternative Modeling: Utilizing game theory, red teaming, and strategic simulation exercises to stress-test major corporate decisions against competitor reactions and changing market dynamics.
Reputational Risk: Protecting the brand equity
Reputation is an intangible asset that takes decades to build and minutes to destroy. Reputational risk management involves identifying and mitigating events that could cause a severe loss of public trust, brand equity, or stakeholder confidence.
Because reputation is largely a reflection of how well an organization manages all other risk categories (a major cyber breach, a financial scandal, an environmental disaster, or a product safety failure all instantly translate into reputational damage), managing this domain requires seamless cross-functional communication, proactive public relations, robust ethical standards, and genuine corporate social responsibility (CSR).
Conclusion of part one
As we have explored, risk management is a multi-layered discipline requiring specialized frameworks tailored to distinct domains of uncertainty. Whether safeguarding financial capital through sophisticated hedging, protecting critical IT infrastructure against cyber threats, or governing enterprise-wide strategy, structured risk management forms the bedrock of organizational resilience.
In the second part of this expert guide, we will examine the tactical implementation phases of risk management, exploring cutting-edge quantitative methodologies, the integration of artificial intelligence and predictive analytics in risk assessment, and the future evolution of governance in a hyper-complex world.
5. Strategic Risk Management: Navigating the unknown
While operational and financial risks are relatively straightforward to measure through historical data and quantitative models, strategic risk operates in a fundamentally different realm. Strategic risks are the hazards that threaten a company's overarching business model, long-term goals, and fundamental value proposition. They arise from faulty strategic decisions, flawed execution, or rapid, unforeseen shifts in the business environment.
The nature of Strategic Vulnerability
Strategic risk is rarely caused by a single operational failure. Instead, it is typically the result of structural misalignment between an organization's capabilities and its external market. Common drivers of strategic risk include:
Disruptive Innovation: New technologies or business models that render existing products or services obsolete (e.g., traditional media houses failing to adapt to streaming, or taxi fleets disrupted by ridesharing platforms).
M&A Failures: Mergers and acquisitions that fail to realize projected synergies, cultural integration issues, or overpayment for target companies.
Geopolitical and Macroeconomic Shifts: Sudden trade restrictions, regulatory overhauls, currency devaluations, or political instability in key operational markets.
Reputational Erosion: Large-scale public relations crises, ethical lapses, or environmental disasters that permanently damage brand equity and customer trust.
Managing and mitigating Strategic Risk
Because strategic risks cannot be easily hedged with financial instruments or mitigated with standard safety protocols, organizations must adopt specialized governance frameworks:
Scenario Planning and Stress Testing: Developing multiple plausible future states (e.g., best-case, worst-case, and transformative technological shifts) to test the resilience of the current business model.
Agile Portfolio Management: Diversifying investments across core operations, adjacent markets, and exploratory innovation (often visualized as the "Three Horizons of Growth") to avoid over-reliance on a single revenue stream.
Active Board Oversight: Ensuring that the board of directors and executive leadership maintain a continuous dialogue regarding external threats, rather than reviewing strategy only during annual retreats.
6. Compliance and Regulatory Risk: Staying on the right side of the law
In an increasingly interconnected and globally regulated economy, compliance risk, often grouped under Governance, Risk, and Compliance (GRC), represents a critical exposure for enterprises of all sizes. Compliance risk is the potential for legal sanctions, material financial loss, or reputational damage resulting from a failure to act in accordance with industry laws, regulations, internal policies, or prescribed best practices.
The expanding Regulatory landscape
The modern regulatory environment is characterized by rapid evolution and extraterritorial reach. Key areas of compliance focus include:
Data Privacy and Cybersecurity: Regulations such as the European Union's General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA) impose stringent requirements on how consumer data is collected, stored, and processed, with severe financial penalties for non-compliance.
Financial Crimes and Anti-Money Laundering (AML): Financial institutions face rigorous mandates to verify customer identities, monitor transactions for suspicious activity, and prevent terrorist financing.
Environmental, Social, and Governance (ESG) Reporting: Regulatory bodies worldwide are moving toward mandatory disclosures regarding carbon footprints, supply chain labor practices, and board diversity.
Labor and Employment Standards: Adherence to local and international wage laws, workplace safety standards, and anti-discrimination policies.
Building a robust Compliance Framework
Mitigating compliance risk requires shifting from a reactive "tick-the-box" mentality to an integrated, proactive culture of integrity:
Regulatory Tracking and Horizon Scanning: Establishing dedicated legal and compliance teams to monitor pending legislation and anticipate upcoming regulatory changes before they take effect.
Automated Controls and Auditing: Implementing software solutions that continuously monitor transaction logs, data flows, and operational procedures to detect anomalies or policy breaches in real time.
Whistleblower Channels and Ethical Training: Fostering an environment where employees feel safe reporting unethical behavior without fear of retaliation, backed by regular, engaging compliance training across all organizational levels.
7. Emerging risks in the digital age: Cyber, AI, and climate
As the global business ecosystem evolves, traditional risk categories are being disrupted by modern, fast-moving phenomena. Organizations can no longer rely solely on legacy risk management models; they must actively address a new class of systemic threats.
Cybersecurity and Information security Risk
With the digitization of supply chains, remote workforces, and cloud-based infrastructures, the attack surface for malicious actors has expanded exponentially. Cybersecurity risk encompasses data breaches, ransomware attacks, insider threats, and intellectual property theft.
Mitigation Strategies: Implementing zero-trust architectures, multi-factor authentication, regular penetration testing, and comprehensive incident response plans that involve both technical teams and executive leadership.
Artificial intelligence and algorithmic Risk
As artificial intelligence (AI) and machine learning (ML) models become embedded in decision-making processes, from credit scoring and hiring to autonomous logistics, new risks emerge. These include algorithmic bias, "hallucinations" in generative models, intellectual property infringement, and a lack of explainability in automated decisions.
Mitigation Strategies: Establishing AI ethics boards, maintaining rigorous training data validation, enforcing "human-in-the-loop" protocols for high-stakes decisions, and complying with emerging AI-specific regulations (such as the EU AI Act).
Climate and Environmental Risk
Physical climate risks (extreme weather events disrupting supply chains and damaging physical assets) and transition risks (policy shifts, carbon taxes, and changing consumer preferences toward sustainability) pose existential threats to numerous industries, particularly agriculture, insurance, energy, and real estate.
Mitigation Strategies: Incorporating climate risk modeling into long-term capital allocation, greening supply chains, and diversifying geographic footprints to reduce vulnerability to localized environmental disasters.
8. Integrating Risk Management into corporate Culture
The most sophisticated risk management frameworks, quantitative models, and software tools will ultimately fail if risk awareness is treated merely as a bureaucratic checkbox rather than a core organizational value. True enterprise risk management (ERM) requires cultural embedding.
From silos to holistic Governance
Historically, risk management was treated as a siloed function, safety teams handled physical hazards, finance managed market exposure, and IT looked after cybersecurity. Modern best practice mandates a unified approach where risks are aggregated and evaluated holistically at the executive level.
The Three Lines Model:
First Line: Operational management owns and manages risks directly in day-to-day business activities.
Second Line: Risk management, compliance, and quality assurance teams oversee and facilitate risk policies.
Third Line: Internal audit provides independent, objective assurance on the effectiveness of governance and risk management processes.
Fostering psychological safety and open dialogue
A healthy risk culture depends heavily on psychological safety. Employees at all levels must feel empowered to raise red flags, report near-misses, and question existing assumptions without fear of negative career consequences. Organizations that punish messengers often find themselves blindsided by catastrophic failures that were foreseen by frontline workers long before they materialized.
9. Conclusion: The Future-Proof organization
Risk management is not about achieving a zero-risk state, an impossible goal that would inherently stifle innovation, growth, and profitability. Instead, it is about optimized risk-taking: making informed, deliberate choices about which uncertainties to embrace, which to mitigate, and which to avoid entirely.
By systematically addressing financial, operational, strategic, compliance, and emerging digital risks through an integrated framework, organizations can transform uncertainty from a source of paralyzing anxiety into a distinct competitive advantage. In a volatile and fast-changing global marketplace, the winners will not be those who avoid all hazards, but those who navigate them with agility, foresight, and resilience.