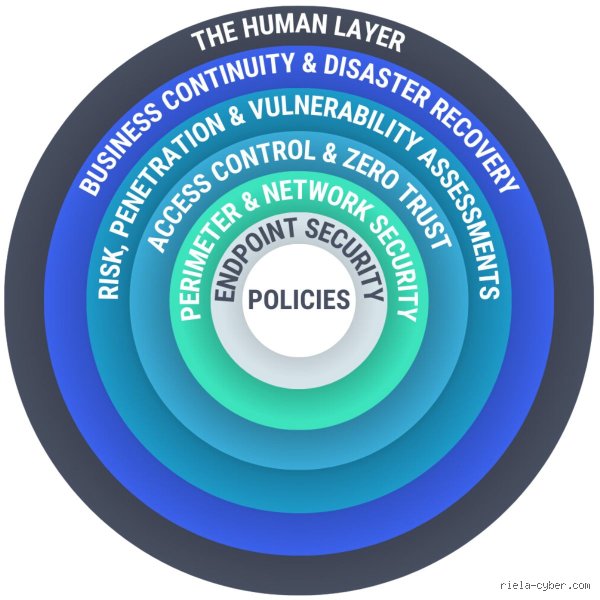
This comprehensive first part of our expert analysis explores the multi-layered paradigm of cybersecurity, breaking down why layered defense is indispensable and examining the outer and foundational tiers that shield modern enterprises and critical infrastructures from compromise.
The Philosophy of Defense-in-Depth
The core principle behind Defense-in-Depth is simple yet profound: redundancy and diversification of security controls. Borrowed from military strategy, DiD dictates that if one defensive barrier fails or is circumvented by an attacker, subsequent barriers must be in place to detect, impede, contain, and neutralize the threat before it achieves its objective.
Think of a medieval castle. A castle did not rely solely on its outer stone wall. It featured a moat, a drawbridge, iron portcullises, murder holes, inner baileys, and a heavily reinforced keep. Cybersecurity operates on the exact same premise. By deploying controls across multiple distinct layers, ranging from the human element to the physical hardware and the code running deep within applications, security architects ensure that an adversary faces escalating friction at every stage of an intrusion attempt.
+-------------------------------------------------------+
| Human & Operational Security |
+-------------------------------------------------------+
| Perimeter & Edge Defense |
+-------------------------------------------------------+
| Network Segmentation & Controls |
+-------------------------------------------------------+
| Endpoint Protection & Hardening |
+-------------------------------------------------------+
| Application Security & Code Integrity |
+-------------------------------------------------------+
| Data Confidentiality & Encryption |
+-------------------------------------------------------+
Layer 1: The Human element (Security Awareness & Culture)
It is an established axiom in the information security community that users are often the weakest link, yet they can simultaneously be transformed into the strongest line of defense. Technology alone cannot prevent a breach if an authorized user with legitimate credentials is manipulated into handing over access keys or executing malicious payloads.
The attack surface of Human psychology
Social engineering attacks, most notably phishing, spear-phishing, smishing, and business email compromise (BEC), bypass traditional technical controls by exploiting human cognitive biases such as trust, urgency, and fear. An attacker does not need to crack 4096-bit encryption if they can simply convince an employee to click a malicious link or provide their multi-factor authentication (MFA) code over a fake login portal.
Mitigating the Human risk Layer
Securing this layer requires a robust, continuous organizational culture rather than a once-a-year compliance checkbox video. Effective human-layer security includes:
Continuous Security Awareness Training: Regular, engaging educational modules that teach staff how to spot evolving indicators of compromise, such as mismatched sender domains, unusual requests for financial transfers, and subtle grammatical anomalies.
Simulated Phishing Campaigns: Controlled testing environments that measure organizational vulnerability and provide immediate, contextual "teachable moments" to employees who fall for simulated lures.
Zero-Trust Culture and Whistleblower Channels: Empowering employees to verify unusual instructions through out-of-band communication channels without fear of reprimand or hesitation.
Layer 2: Perimeter Security (Edge Protection & Gateways)
Once the human element is accounted for, the next traditional defensive tier is the perimeter. Historically, the perimeter was defined by the physical walls of an enterprise data center and the boundary where an internal local area network (LAN) met the untrusted public internet.
Although cloud computing, remote work, and mobile devices have blurred the traditional corporate boundary, the perimeter concept remains vital at the edge of every physical site, cloud Virtual Private Cloud (VPC), and branch office.
Core components of Perimeter Defense
Next-Generation Firewalls (NGFWs): Advanced network security systems that go beyond traditional port and protocol inspection to offer deep packet inspection (DPI), application awareness, and integrated intrusion prevention systems (IPS).
Secure Web Gateways (SWGs): Solutions that filter unwholesome or malicious internet traffic, protecting internal users from navigating to known command-and-control (C2) servers or downloading malware.
Virtual Private Networks (VPNs) and IPsec Tunnels: Encrypted communication channels that allow remote workers or branch offices to securely tunnel traffic back into the corporate network over untrusted public infrastructure.
The evolution: From Perimeter to Zero Trust
Because modern workforces operate everywhere from coffee shops to home offices, relying solely on a perimeter firewall is no longer sufficient. If an attacker compromises a single endpoint outside the perimeter, they could potentially tunnel inside. This limitation has driven the migration toward Zero Trust Network Access (ZTNA), which treats every connection attempt as untrusted regardless of whether it originates from inside or outside the traditional network boundary.
Layer 3: Network Security (Segmentation & internal Controls)
Assuming an adversary successfully breaches the perimeter, or bypasses it entirely via a compromised laptop or insider threat, they must not be granted free, unfettered lateral movement across the internal infrastructure. This is where network security and micro-segmentation take center stage.
Network Segmentation principles
In a flat, unsegmented network, once a piece of malware infects a single workstation, it can easily scan the local subnet, discover other vulnerable hosts, and propagate rapidly through protocols like SMB or RDP. Network segmentation divides the broader network into smaller, isolated domains or zones using VLANs, internal firewalls, and software-defined networking controls.
Zone-Based Policies: Separating corporate IT systems from operational technology (OT) environments, guest Wi-Fi networks, and sensitive financial databases.
Micro-Segmentation: Granularly isolating individual workloads or virtual machines within cloud environments so that even if one application server is compromised, the attacker's blast radius is strictly contained.
Intrusion detection and Prevention systems (IDS/IPS)
Internal network sensors monitor east-west traffic (traffic moving between internal systems) as well as north-south traffic (traffic entering and leaving the network). Behavioral anomaly detection engines analyze traffic flows for signs of unauthorized data exfiltration, lateral scanning, or abnormal protocol usage, triggering automated alerts or blocking actions in real time.
...Moving inward from the structural perimeters and network-level barriers, we arrive at the software and data assets that hackers are ultimately trying to reach. This brings us to the next critical layer of a robust defense-in-depth architecture: Application Security (AppSec).
Layer 4: Application Security (AppSec)
Modern businesses rely heavily on custom-built software, SaaS applications, and third-party APIs. Unfortunately, applications are often the most exposed attack surface because they are designed to be accessible to users. Application security involves hardening software against threats throughout its entire lifecycle, from design and development to deployment and maintenance.
Key components of Application Security include:
Secure Coding Practices: Training developers to write code that inherently resists common vulnerabilities, such as those cataloged in the OWASP Top 10 (e.g., SQL injection, cross-site scripting, and broken authentication).
Web Application Firewalls (WAF): Deploying WAFs to monitor, filter, and block HTTP/HTTPS traffic traveling to and from a web application, shielding the software from zero-day exploits and brute-force attacks.
Application Testing (SAST and DAST): Utilizing Static Application Security Testing (SAST) to analyze source code for flaws and Dynamic Application Security Testing (DAST) to evaluate running applications for external vulnerabilities.
API Security: Ensuring that Application Programming Interfaces, the digital glue connecting modern microservices, are properly authenticated, rate-limited, and encrypted to prevent unauthorized data exfiltration.
Layer 5: Data Security (the crown jewels)
At the very center of the security onion lies data. Whether it is customer Personally Identifiable Information (PII), intellectual property, or financial records, data is the ultimate target of cybercriminals. Data security focuses on protecting the data itself, regardless of where it resides (in transit, at rest, or in use).
To secure this layer effectively, organizations must implement:
Encryption: Applying robust cryptographic algorithms (such as AES-256 for data at rest and TLS 1.3 for data in transit) so that even if data is intercepted or stolen, it remains completely unreadable to unauthorized parties.
Data Loss Prevention (DLP): Utilizing software solutions that monitor data usage across endpoints, networks, and cloud environments to detect and block unauthorized sharing, copying, or exfiltration of sensitive information.
Data Classification and Discovery: Automatically scanning and labeling data based on sensitivity levels so that strict controls can be applied specifically to high-value assets.
Immutable Backups: Maintaining offline, read-only backups that are fundamentally insulated from ransomware encryption, ensuring business continuity in the event of a catastrophic breach.
Layer 6: Identity and Access Management (IAM)
In a modern perimeter-less enterprise where employees work remotely and cloud services span multiple continents, Identity is the new perimeter. Traditional network-based security is no longer sufficient when a user's credentials can be stolen via phishing. Identity and Access Management (IAM) ensures that the right individuals have appropriate access to technology resources.
Core pillars of modern IAM include:
Multi-Factor Authentication (MFA): Requiring two or more verification factors (e.g., a password plus an authenticator app or hardware token) to gain access, drastically reducing the risk posed by compromised passwords.
The Principle of Least Privilege (PoLP): Restricting user access rights to only what is strictly necessary to perform their specific job functions, limiting the "blast radius" if an account is compromised.
Role-Based Access Control (RBAC) and Attribute-Based Access Control (ABAC): Dynamically granting permissions based on user roles, device health, location, and time of access.
Privileged Access Management (PAM): Securing, controlling, and monitoring administrative accounts that possess supreme control over enterprise systems.
Layer 7: The Human Layer (Security Awareness and Culture)
Time and time again, cybersecurity reports highlight that the human element remains the weakest link in the security chain. Social engineering tactics like spear-phishing, business email compromise (BEC), and vishing bypass technological controls by manipulating human psychology.
Therefore, building a resilient human layer involves:
Continuous Security Awareness Training: Moving away from annual compliance tick-box training toward engaging, frequent, and real-world-simulated phishing exercises that teach employees how to spot anomalies.
Fostering a Just Culture: Creating an environment where employees feel safe reporting a suspicious link or a mistake immediately without fear of punitive action. Early reporting can mean the difference between a minor incident and a full-scale corporate breach.
Layer 8: Incident Response, resilience, and Business Continuity
No matter how many layers of security an organization implements, no defense is 100% impenetrable. A sophisticated adversary with enough time and resources can eventually find a crack. This is why the final layer of cyber security focuses on resilience and response, how an organization handles failure when it inevitably occurs.
A mature Incident Response (IR) framework includes:
Incident Response Plans (IRP): Documented, tested playbooks that outline exact roles, communication channels, and technical steps to take during a breach.
Security Orchestration, Automation, and Response (SOAR): Utilizing automation tools to triage alerts, isolate infected endpoints, and remediate threats at machine speed.
Disaster Recovery (DR) and Business Continuity Planning (BCP): Establishing clear strategies to restore operations, communicate with stakeholders, regulatory bodies, and customers, and learn from post-incident forensics.
The Synergy of Defense-in-Depth
The true power of understanding these layers does not lie in treating them as standalone silos, but in recognizing how they reinforce one another under the framework of Defense-in-Depth and Zero Trust Architecture ("Never Trust, Always Verify").
If a phishing attack bypasses the human layer (Layer 7) and steals a user's credentials, robust Multi-Factor Authentication (Layer 6) can block the login attempt. If the attacker manages to log in, network segmentation (Layer 2) can restrict their lateral movement. If they manage to traverse the network, file-level encryption (Layer 5) ensures the data they attempt to steal is completely unreadable.
Conclusion
In today’s hyper-connected, threat-laden digital landscape, cyber security is not a product you can purchase off the shelf; it is an ongoing, multi-layered discipline of risk management. By implementing comprehensive, overlapping layers of security across the perimeter, network, endpoints, applications, data, identities, and human processes, organizations can create a resilient posture capable of absorbing blows, neutralizing threats, and ensuring long-term digital survival.