The Illusion of Absolute Safety: Rethinking How We Protect What Matters
When most people picture security—whether it is safeguarding a high-tech corporate headquarters, securing a sprawling cloud database, or simply locking down a home network—they imagine a single, impenetrable fortress wall. You build the thickest barrier possible, put a heavy steel door on the front, and assume that anyone outside is kept away while everyone inside is completely safe.
The thing is, real-world security has never worked that way.
In both physical security and cybersecurity, relying on a single defensive boundary is a recipe for disaster. The moment an adversary slips past that one outer wall, the entire system collapses like a house of cards. Modern security experts long ago abandoned the idea of single-point protection in favor of a much more resilient philosophy: Defense in Depth.
Why One Layer Is Never Enough
Where it gets tricky is that people often confuse complexity with security. They assume that buying the most expensive firewall or installing the heaviest deadbolt automatically makes them invulnerable. But technology fails, physical locks can be picked, and human beings make mistakes.
Consider a modern digital enterprise. You might have a state-of-the-art perimeter defense system blocking external cyber threats at the network edge. But what happens when an employee accidentally clicks a phishing link on their laptop while working from a coffee shop? Suddenly, the threat isn't hammering at the front gate from the outside; it is already sitting comfortably inside your network, wearing an employee badge.
This is precisely why security is architected in layers. If Layer One fails, Layer Two catches the threat. If Layer Two is bypassed, Layer Three stands ready. That changes everything about how we assess risk, design systems, and respond to incidents. Instead of asking, "How do we keep everyone out forever?" we must ask, "How do we slow down, detect, and contain an adversary at every single stage of their movement?"
Layer One: Perimeter Security (The Outer Boundary)
The first layer of security is the outermost boundary. In the physical world, this is your fence, your security guards at the front gate, and the exterior doors of a building. In the digital realm, this corresponds to network firewalls, secure gateways, perimeter routers, and access control lists (ACLs) that monitor traffic flowing between the internal network and the outside internet.
For decades, organizations poured almost all of their security budget into this single layer. The strategy was simple: build a moat, draw the bridge, and trust everything inside the castle walls.
However, people don't think about this enough: the perimeter has effectively dissolved. With the rise of remote work, cloud computing, mobile devices, and Internet of Things (IoT) sensors, the traditional corporate network no longer has a neat, fixed boundary. Your employees are logging in from home networks, public Wi-Fi hotspots, and cellular connections all over the globe.
Key Functions of Perimeter Security
Traffic Filtering: Inspecting incoming and outgoing data packets to block known malicious signatures, suspicious IP addresses, and unauthorized connection attempts.
Access Control Checkpoints: Requiring robust authentication credentials before granting any external entity entry into the network ecosystem.
Intrusion Detection Systems (IDS): Monitoring network traffic for abnormal patterns that indicate active scanning or reconnaissance by malicious actors.
Despite its evolution, perimeter security remains a critical first line of defense. It absorbs the vast bulk of automated, mass-scale attacks—blocking millions of daily botnet scans, brute-force login attempts, and denial-of-service barrages before they ever reach internal assets.
Layer Two: Internal Network and Systems Security (The Maze Within)
Even the strongest perimeter defense can be breached. A determined attacker might exploit a zero-day vulnerability in an edge device, bribe an insider, or use social engineering to harvest legitimate user credentials. When that happens, the attacker is suddenly inside your perimeter.
This brings us to the second layer: internal network and systems security.
If Layer One is the castle wall, Layer Two is the labyrinth of interior doors, security checkpoints, and reinforced hallways inside the castle. The core philosophy here is network segmentation and least privilege access. Instead of treating the entire internal network as a trusted zone where everyone can roam freely, security architects divide the network into isolated subnetworks or zones.
Important Note: Assuming internal users or devices are inherently trustworthy is one of the most dangerous vulnerabilities an organization can maintain. Every internal segment must be treated with the same skepticism as the public internet.
Implementing Internal Defense
To build a robust second layer, organizations rely on several key tactical frameworks:
Micro-Segmentation: Breaking down the network into smaller, isolated zones so that if an attacker compromises a marketing workstation, they cannot easily pivot to access the financial database or customer records server.
Host-Based Firewalls and Endpoint Detection (EDR): Installing protective software directly on servers, laptops, and workstations to monitor internal processes, memory usage, and file modifications.
Internal Access Controls: Ensuring that users only have access to the specific files, applications, and systems required to perform their direct job duties—and nothing more.
When looking at how far traditional IT infrastructure has evolved to meet modern threat landscapes, we're far from it if we think a simple password policy and a perimeter firewall are enough to keep critical data safe. The internal network must be vigilant, self-monitoring, and aggressively defended against lateral movement.
Layer 2: Protecting the Core — Network and Endpoint Security
While perimeter defenses act as your first line of defense, modern security architecture operates on the realistic assumption that determined threats will eventually breach the outer gate. This is where Layer 2: Network and Endpoint Security comes into play. If the perimeter is your castle wall, Layer 2 is the system of inner courtyards, guarded corridors, and locked doors that prevent an intruder from roaming freely once inside.
Internal Network Segmentation
Once an attacker crosses the perimeter—perhaps via a compromised employee credential or a phishing email—a flat network allows them to move laterally across every connected system. Network segmentation divides your digital environment into isolated zones or subnets.
Critical Assets Isolation: Sensitive databases, financial records, and core infrastructure are placed behind strict internal firewalls.
Containment: If a workstation in the marketing department is infected with ransomware, segmentation prevents that malware from automatically spreading to the human resources or engineering servers.
Comprehensive Endpoint Protection
Every device that connects to your network—laptops, smartphones, tablets, and Internet of Things (IoT) gadgets—represents an endpoint and a potential entry point for threats. Traditional antivirus software that relies solely on signature matching is no longer sufficient against modern, polymorphic malware.
Endpoint Detection and Response (EDR): EDR solutions continuously monitor endpoint activities, using behavioral analysis to detect anomalies, suspicious process executions, and unauthorized data exfiltration in real time.
Mobile Device Management (MDM): In an era of remote work and Bring Your Own Device (BYOD) policies, MDM tools ensure that every device accessing corporate resources meets minimum security standards, such as disk encryption, up-to-date operating systems, and remote wipe capabilities in case of loss or theft.
Layer 3: Safeguarding the Crown Jewels — Data and Identity Security
At the heart of any security strategy is Layer 3: Data and Identity Security. This layer protects what matters most—your actual information and the identities of the people authorized to access it. Even if physical hardware is stolen or network perimeters are bypassed, robust data and identity controls ensure that information remains unreadable and unusable to unauthorized parties.
Identity and Access Management (IAM)
Identity has become the new perimeter. Protecting user identities is paramount in stopping credential-based attacks, which remain one of the leading vectors for corporate breaches.
Multi-Factor Authentication (MFA): Requiring two or more verification factors (something you know, something you have, or something you are) drastically reduces the likelihood of unauthorized access from stolen passwords.
Role-Based Access Control (RBAC): Implementing the Principle of Least Privilege (PoLP) ensures that users and applications only have access to the specific data and resources necessary to perform their jobs, minimizing the blast radius of a compromised account.
Zero Trust Architecture: Moving away from implicit trust based on network location, a Zero Trust model dictates that every user and device must be continuously authenticated, authorized, and validated before gaining access to applications and data.
Robust Encryption Practices
Data encryption transforms readable plaintext into unreadable ciphertext, ensuring that even if data is intercepted or stolen, it cannot be interpreted without the correct cryptographic keys.
Encryption in Transit: Protecting data as it travels across networks using protocols like HTTPS, TLS, and secure VPNs to prevent eavesdropping and man-in-the-middle attacks.
Encryption at Rest: Securing stored data on hard drives, cloud storage buckets, and backup archives using strong encryption algorithms (such as AES-256).
Key Management: Implementing secure key lifecycle management to ensure encryption keys are rotated, backed up, and stored separately from the data they protect.
Synergy in Action: Why Defense-in-Depth Matters
The true power of the three-layer security model lies not in any single layer, but in their synergistic integration. Each individual layer has inherent limitations and potential vulnerabilities. A firewall can be misconfigured; an endpoint can have a delayed patch; a user can fall victim to a sophisticated social engineering attack.
By stacking these defenses, you create a cumulative filtering effect. When an attack encounters multiple independent barriers, the probability of complete system compromise drops exponentially. If a phishing email bypasses the email gateway (Layer 1), the EDR tool flags the suspicious payload execution on the workstation (Layer 2), and the attacker is ultimately blocked from accessing sensitive databases because MFA and least-privilege policies restrict their lateral movement (Layer 3). This multi-layered resilience transforms security from a fragile glass house into a robust, adaptable fortress.
Conclusion: Building a Resilient Security Culture
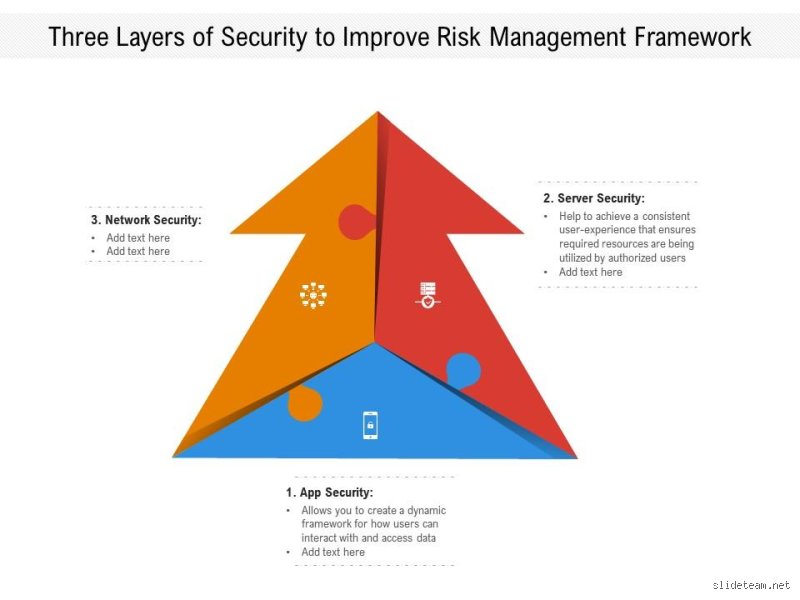
In an increasingly interconnected and threat-laden digital landscape, relying on a single security measure is a recipe for vulnerability. The three layers of security—perimeter defense, network and endpoint protection, and data and identity safeguarding—provide a comprehensive framework for achieving true resilience through defense-in-depth. By systematically assessing and strengthening each of these tiers, organizations and individuals alike can create a formidable barrier against evolving cyber threats.
However, technology and architecture alone are only half the battle. The most sophisticated security controls can be undermined by human error, making ongoing education, vigilance, and security awareness equally vital components of your strategy. Security is not a static product you purchase and install; it is an active, continuous process of adaptation, monitoring, and improvement. By embracing a multi-layered mindset today, you safeguard your digital assets, protect your privacy, and ensure a secure foundation for future innovation.
Why is a single layer of security never enough?
A single layer of security creates a single point of failure. If an attacker manages to bypass that one defense mechanism—whether through a software bug, a misconfiguration, or a stolen password—they gain total access to your environment. Multi-layered security ensures that even if one barrier fails, subsequent layers catch the threat before critical damage occurs.
What is the primary difference between perimeter security and endpoint security?
Perimeter security focuses on controlling the boundary between your trusted internal network and the outside world (using tools like firewalls, secure gateways, and VPNs). Endpoint security, on the other hand, focuses on protecting individual devices (such as laptops, phones, and servers) wherever they are located, recognizing that users often connect from outside traditional network perimeters.
How does the Principle of Least Privilege protect sensitive data?
The Principle of Least Privilege restricts user and application access rights to only what is strictly necessary to complete specific tasks. If a user's account is compromised, the attacker's ability to access or steal sensitive data is severely limited because that specific account lacks permissions to view the rest of the network's crown jewels.
Is multi-layered security only relevant for large enterprises?
No. Organizations of all sizes, as well as individuals, benefit from multi-layered security. While large corporations may deploy complex software suites and dedicated security teams, small businesses and individuals can implement multi-layered security effectively by combining reliable router firewalls, endpoint antivirus/EDR, strong passwords paired with multi-factor authentication (MFA), and encrypted cloud backups.