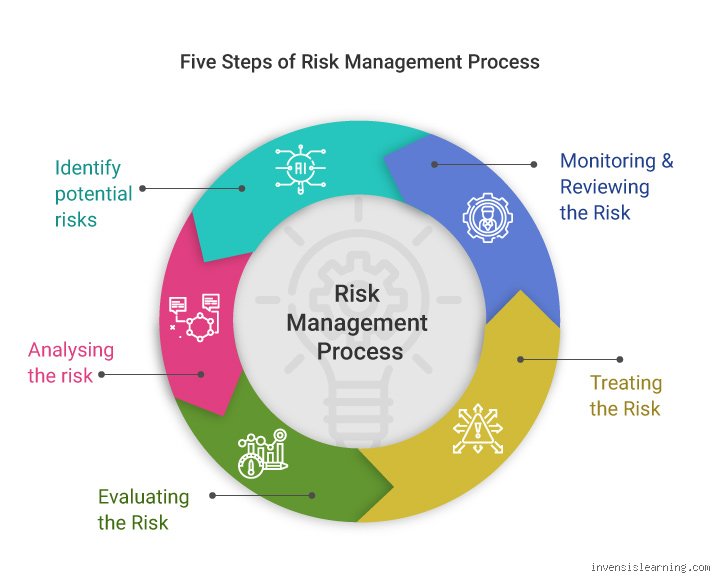
By systematically identifying vulnerabilities before they manifest as crises, decision-makers can allocate resources efficiently, protect vital assets, and capitalize on emerging market opportunities that cautious competitors might overlook. This comprehensive, expert-level guide breaks down the foundational mechanics of risk management, exploring its core principles, strategic significance, and the essential preliminary phases of the standard risk management lifecycle.
The Strategic imperative of Risk management
To understand why risk management is essential, one must first recognize what risk actually represents in an operational context. At its core, risk is the effect of uncertainty on objectives. It is measured in terms of the combination of the likelihood of an event occurring and the consequence or impact of that event should it materialize. Risks can be positive (opportunities) or negative (threats), though standard organizational frameworks place primary emphasis on mitigating threats while optimizing for upside potential.
Without a structured risk management methodology, organizations operate in a reactive posture. Problems are addressed only after they have erupted, leading to inflated financial costs, operational downtime, reputational damage, and immense stress for team members. Proactive risk management transforms this dynamic by shifting the organizational mindset from firefighting to horizon scanning.
Core benefits of a structured framework
Informed Decision-Making: When leadership possesses a clear, quantified understanding of potential threats, strategic choices become data-driven rather than intuitive guesses.
Optimized Resource Allocation: Budgets, personnel, and time can be directed toward high-impact vulnerabilities rather than wasted on improbable or trivial issues.
Enhanced Resilience: Organizations equipped with robust contingency plans absorb market shocks, supply chain disruptions, or regulatory changes much faster than unprepared peers.
Stakeholder Confidence: Investors, board members, regulators, and customers trust entities that demonstrate rigorous governance, ethical oversight, and operational stability.
Step 1: Establishing the Context and objectives
Before any risk can be identified, evaluated, or managed, you must establish the perimeter within which you are operating. This foundational phase is known as Context Establishment or Scope Definition. Every project, business unit, or strategic initiative exists within a unique ecosystem defined by internal and external parameters. Failing to define these parameters leads to misaligned risk assessments that waste valuable time and resources.
External Context
The external context encompasses the macro-environmental factors that sit entirely outside the direct control of the organization, yet exert a profound influence on its success. These include:
Regulatory and Legal Landscapes: Compliance mandates, local and international laws, industry standards, and impending legislative shifts.
Economic Variables: Inflation rates, currency fluctuations, interest rates, market volatility, and macroeconomic downturns.
Sociocultural Dynamics: Shifting consumer behaviors, demographic changes, cultural norms, and public relations sensitivities.
Technological Trends: Rapid innovation cycles, cybersecurity threat landscapes, and artificial intelligence disruptions.
Internal Context
The internal context involves the internal dynamics, capabilities, and constraints of the organization or project team itself. Key elements include:
Governance Structures: Lines of authority, decision-making hierarchies, accountability frameworks, and reporting channels.
Resource Availability: Financial capital, human talent, technological infrastructure, and physical assets.
Organizational Culture and Risk Appetite: The collective willingness of leadership and employees to accept risk in pursuit of strategic objectives. An aggressive tech startup possesses a vastly different risk appetite than a conservative financial institution managing pension funds.
By clearly documenting both external and internal contexts, risk practitioners establish clear boundaries, ensuring that subsequent risk identification efforts remain relevant, focused, and aligned with organizational goals.
Step 2: Risk Identification — uncovering the unknowns
Once the context is firmly established, the next critical phase is Risk Identification. This step is a comprehensive, systematic exercise designed to find, recognize, and record the risks that could help or hurt the achievement of defined objectives. Effective risk identification requires casting a wide net, combining structured analytical techniques with creative brainstorming, historical data analysis, and cross-functional collaboration.
If a risk is not identified during this phase, it cannot be analyzed, prioritized, or mitigated. It remains a blind spot capable of blindsiding the organization at the worst possible moment. Therefore, risk identification must be treated as an ongoing, iterative process rather than a one-time meeting held at the kickoff of a project.
Common categories of Risk
To ensure comprehensive coverage, risks are typically categorized into distinct domains:
Strategic Risks: High-level threats related to overall business direction, mergers and acquisitions, competitor actions, or changing customer demand.
Operational Risks: Failures in internal processes, human error, system outages, supply chain bottlenecks, or equipment breakdowns.
Financial Risks: Cash flow volatility, credit defaults, liquidity shortages, and unfavorable currency exchanges.
Compliance and Legal Risks: Breaches of regulations, contractual liabilities, intellectual property disputes, and labor law violations.
Reputational Risks: Negative publicity, social media backlash, product recalls, or ethical scandals that erode public trust.
Proven techniques for Risk Identification
Brainstorming and Workshops: Bringing together multidisciplinary teams—from engineering and finance to legal and customer support, to surface diverse perspectives and hidden vulnerabilities.
SWOT Analysis: Examining Strengths, Weaknesses, Opportunities, and Threats to uncover internal vulnerabilities exposed by external realities.
Root Cause Analysis (Fishbone / 5 Whys): Investigating historical failures or near-misses to identify the systemic underlying causes rather than just surface-level symptoms.
Checklists and Historical Data: Reviewing post-mortem reports, industry databases, and historical project logs to identify recurring pitfalls that plagued past initiatives.
Scenario Analysis: Posing "what-if" questions about extreme hypothetical events (e.g., "What if our primary cloud provider experiences a 48-hour outage next Tuesday?") to test operational robustness.
Looking ahead to part 2
Establishing context and identifying potential threats lay the essential groundwork for any successful risk management strategy. However, identification alone is insufficient; not all risks carry equal weight, and attempting to mitigate every minor uncertainty is neither practical nor financially viable.
In the upcoming second part of this expert guide, we will explore the subsequent stages of the risk management lifecycle, focusing on Risk Analysis and Evaluation (qualitative and quantitative measurement), Risk Treatment and Mitigation Strategies (avoidance, transfer, reduction, and acceptance), and the vital processes of Monitoring, Review, and Communication that ensure long-term organizational resilience.
Step 3: Risk Evaluation, prioritizing What matters
Once you have identified and analyzed your risks, you face a critical operational challenge: not all risks are created equal. Organizations operate with finite resources, time, and budget. Trying to mitigate every single identified risk with equal intensity is a recipe for operational paralysis and resource exhaustion. This is where Risk Evaluation comes into play.
Risk evaluation involves comparing the estimated level of risk against the organization’s pre-established risk criteria, risk appetite, and risk tolerance thresholds.
Establishing Risk Appetite and Tolerance
Risk Appetite: The amount and type of risk that an organization is willing to pursue or retain in pursuit of its strategic objectives.
Risk Tolerance: The acceptable deviation relative to a specific business objective or category of risk.
During this phase, decision-makers draw a line, often visualized on a risk matrix, between acceptable and unacceptable risk levels. Risks that fall below the threshold are typically accepted, provided they are monitored periodically. Risks that exceed the threshold demand immediate strategic intervention.
Qualitative vs. Quantitative Evaluation
Depending on your industry and data availability, evaluation can take two primary forms:
Qualitative Evaluation: Uses descriptive scales (e.g., High, Medium, Low; or a 1-to-5 scoring system) based on expert judgment, historical precedent, and stakeholder consensus. It is fast, intuitive, and ideal when precise numerical data is sparse.
Quantitative Evaluation: Employs mathematical models, statistical analysis, and financial simulations (such as Monte Carlo simulations) to assign concrete monetary values to potential losses. This is heavily utilized in finance, insurance, and large-scale engineering projects where historical loss data is robust.
Step 4: Risk Treatment and response Strategies, taking action
Knowing a risk exists and understanding its magnitude is useless without a deliberate response plan. Risk Treatment (often referred to as risk mitigation or risk response) is the process of selecting and implementing measures to modify the risk profile.
When crafting a response plan, risk management professionals generally rely on the classic Four T's framework (or Four A's):
1. Avoidance (Eliminate)
Risk avoidance involves changing your project plan, operational process, or strategic objective entirely to eliminate the threat.
Example: Deciding not to enter a foreign market characterized by extreme regulatory instability and currency volatility.
When to use: When the potential impact is catastrophic and no other mitigation strategy can bring the risk down to an acceptable level.
2. Mitigation (Control and Reduce)
Mitigation focuses on reducing either the probability of occurrence, the severity of the impact, or both. This is the most common response strategy in day-to-day business operations.
Example: Implementing redundant server backups and advanced firewalls to reduce the probability and impact of a cyber breach.
When to use: For high-probability, high-impact risks that cannot be avoided because the activity is core to the business mission.
3. Transfer (Share or Outsource)
Risk transfer involves shifting the financial burden or operational responsibility of a risk to a third party. While this does not eliminate the risk, it protects the organization from bearing its full impact.
Example: Purchasing comprehensive liability insurance, drafting robust indemnity clauses in vendor contracts, or utilizing outsourced cloud infrastructure with strict SLA guarantees.
When to use: When dealing with low-frequency, high-severity financial or legal liabilities.
4. Acceptance (Retain)
Risk acceptance means acknowledging that a risk exists, calculating that the cost of mitigating it outweighs the potential loss, and choosing to absorb the consequences if it occurs.
Example: Setting aside a contingency reserve fund to cover minor equipment failures rather than purchasing expensive maintenance contracts.
When to use: For low-impact, low-probability risks ("residual risks") where treatment costs would exceed the expected loss value.
Every chosen treatment strategy must be paired with a Risk Owner, a designated individual accountable for executing the response plan, along with explicit deadlines, milestones, and budget allocations.
Step 5: Monitoring, Review, and Communication, the continuous loop
Risk management is never a one-time exercise, a static binder on a shelf, or an annual compliance checkbox. The internal and external business environments are dynamic: markets shift, supply chains fracture, regulatory frameworks evolve, and new technologies emerge overnight. Therefore, the final step, Monitoring, Review, and Communication, is the lifeblood of an effective risk management framework.
Key Risk Indicators (KRIs) and metrics
To monitor risks effectively, organizations must establish quantitative Key Risk Indicators (KRIs). Unlike Key Performance Indicators (KPIs) which measure success toward a goal, KRIs serve as early warning systems that signal an increasing probability or impact of a specific risk event.
Example KRI: Tracking the average employee turnover rate in critical engineering roles to monitor the risk of intellectual property drain and project delays.
Periodic audits and retrospectives
Regular risk reviews ensure that:
Previously identified risks are declining in severity due to successful treatments.
New risks emerging from business growth or external shocks are captured and evaluated.
Risk owners are actively maintaining their mitigation controls.
Post-incident reviews (often called "post-mortems" or "after-action reviews") are conducted whenever a risk materializes, turning failures into invaluable lessons for future risk assessments.
Continuous Stakeholder Communication
Transparent communication ensures that front-line workers, middle management, and executive board members share a unified mental model of the organization's risk landscape. Risk registers and heat maps should be living dashboards accessible to decision-makers across departments, fostering a culture where raising concerns about potential hazards is rewarded, not penalized.
Institutionalizing a Risk-Aware Culture
Implementing these five steps, Identification, Analysis, Evaluation, Treatment, and Monitoring, transforms risk management from a reactive firefighting exercise into a proactive strategic advantage. Organizations that master this lifecycle do not eliminate uncertainty; rather, they develop the resilience and agility to navigate volatility, protect their capital, and capitalize on opportunities that cautious competitors miss.
| Risk Step | Primary Objective | Key Deliverables & Tools |
|---|---|---|
| 1. Identification | Discover all potential hazards and uncertainties | Brainstorming sessions, process flowcharts, historical loss data logs |
| 2. Analysis | Understand the nature, causes, and likelihood of risks | Root cause analysis (5 Whys), bow-tie diagrams, probability assessments |
| 3. Evaluation | Prioritize risks against organizational appetite | Risk matrices, cost-benefit analyses, threshold scoring models |
| 4. Treatment | Formulate and execute response strategies | Risk response plans, assignment of Risk Owners, contractual safeguards |
| 5. Monitoring | Maintain continuous oversight and adapt to change | KRIs, risk dashboards, scheduled audit cycles, incident post-mortems |