The bedrock of modern privacy legislation
To safeguard citizens against the potential harms of unregulated data harvesting, governments worldwide have instituted robust legal frameworks. Within the United Kingdom, the cornerstone of this regulatory architecture is the Data Protection Act 2018 (DPA 2018), working in tandem with the UK General Data Protection Regulation (UK GDPR). Together, these legislative instruments govern how personal information is handled by businesses, government departments, charities, and other organizations.
At the very heart of this framework lie the core tenets that dictate how data can be lawfully processed. For anyone navigating the complex landscape of corporate compliance, legal governance, or information technology, a foundational question frequently arises: How many key principles are actually embedded within the Data Protection Act 2018?
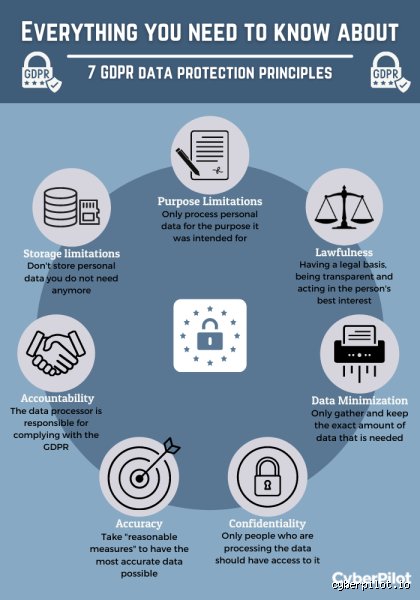
The short, authoritative answer is that the UK GDPR and the Data Protection Act 2018 are governed by seven core principles. These seven interrelated rules serve as the mandatory blueprint for all data processing activities. Far from being mere bureaucratic hurdles or optional suggestions, these principles are legally binding. Failure to adhere to them can result in devastating financial penalties, severe reputational damage, and criminal liability.
This comprehensive, multi-part expert article provides an in-depth exploration of the Data Protection Act 2018, meticulously breaking down the exact number of key principles, examining their operational implications, and analyzing how organizations can embed them into their everyday corporate DNA.
The legislative evolution: Understanding the DPA 2018 and UK GDPR
To fully appreciate the significance of these seven principles, it is essential to understand the historical and legislative context from which the Data Protection Act 2018 emerged. Prior to 2018, the UK's data protection regime was heavily rooted in the Data Protection Act 1998, which had been designed to implement the European Union's 1995 Data Protection Directive. However, as the digital landscape evolved—marked by the explosive rise of cloud computing, social media platforms, big data analytics, and smartphone proliferation—the 1998 Act quickly became outdated and ill-equipped to handle modern privacy threats.
In May 2018, the European Union introduced the General Data Protection Regulation (GDPR), representing a monumental shift in global privacy standards. Although the United Kingdom subsequently exited the European Union, the fundamental necessity to maintain high standards of data protection and seamless cross-border data flows led the UK government to enact the Data Protection Act 2018.
The DPA 2018 does three primary things:
It operationalizes and tailors the GDPR standards within the specific context of domestic UK law (forming what is now known as the UK GDPR).
It sets out separate, specialized frameworks for areas not directly covered by the EU GDPR, such as law enforcement data processing, intelligence services processing (MI5, MI6, GCHQ), and national security exemptions.
It outlines the structure, powers, and enforcement mechanisms of the Information Commissioner’s Office (ICO), which acts as the UK’s independent regulatory authority for data protection.
Despite the various schedules and chapters contained within the extensive text of the DPA 2018, Article 5(1) of the UK GDPR (which is explicitly imported and reinforced by the Act) outlines the definitive set of standards that apply to anyone handling personal data. These are universally recognized as the seven key data protection principles.
Overview of the seven principles
Before examining each principle in granular detail, it is helpful to list them side-by-side to understand how they form a cohesive, holistic shield around individual privacy. The seven key principles of the Data Protection Act 2018 and UK GDPR are:
Lawfulness, Fairness, and Transparency
Purpose Limitation
Data Minimization
Accuracy
Storage Limitation
Integrity and Confidentiality (Security)
Accountability
These principles do not operate in silos; rather, they overlap and reinforce one another. For example, an organization cannot achieve transparency without data minimization, nor can it ensure integrity without strict accountability measures.
In the remainder of this first part of our expert analysis, we will dive deep into the first three principles, exploring their legal definitions, practical challenges, and real-world compliance strategies.
Principle 1: Lawfulness, Fairness, and Transparency
Deconstructing the first rule
The first principle is arguably the most fundamental and far-reaching requirement of the entire legislative framework. It mandates that personal data must be processed lawfully, fairly, and in a transparent manner in relation to the data subject.
To unpack this principle, compliance experts break it down into three distinct conceptual pillars:
Lawfulness: An organization cannot simply collect and process personal data because it wants to or finds it convenient. Every single instance of data processing must have a valid legal basis (often referred to as a "lawful basis") explicitly listed under Article 6 of the UK GDPR. There are six available lawful bases:
Consent: The individual has given clear, unambiguous, and freely given permission for a specific purpose.
Contract: Processing is necessary because of a contract the organization has with the individual (e.g., fulfilling an online retail order).
Legal Obligation: Processing is required to comply with the law (e.g., reporting employee tax data to HM Revenue and Customs).
Vital Interests: Processing is necessary to protect someone’s life.
Public Task: Processing is necessary for official functions or tasks laid down by law.
Legitimate Interests: Processing is necessary for the organization’s legitimate interests (or those of a third party), provided those interests are not overridden by the fundamental rights and freedoms of the individual.
Fairness: This means that organizations must handle personal data in a way that is not unduly detrimental, unexpected, or misleading to the individuals concerned. Even if an organization has a technical legal basis for processing data, if the method of collection relies on deception, manipulation (such as "dark patterns" in user interface design), or causes unjustified harm, it violates the fairness requirement. Processing must align with what a reasonable person would expect under the circumstances.
Transparency: Transparency is inextricably linked to fairness. It requires organizations to be completely open, honest, and clear with individuals about who is collecting their data, why it is being collected, how it will be used, and who it will be shared with. In practice, this is typically achieved through concise, accessible, and easily understandable privacy notices or privacy policies. An individual should never have to hunt through dense, obscure legal jargon to discover how their personal life details are being utilized.
Practical compliance challenges
The primary challenge organizations face under the first principle is navigating the strict rules surrounding consent. Under the UK GDPR and DPA 2018, consent cannot be bundled, vague, or implied through pre-ticked boxes. It must be an active, affirmative, and easily withdrawable choice. If an organization relies on consent and fails to make its terms transparent, the entire data processing pipeline becomes illegal overnight, exposing the entity to hefty regulatory enforcement action.
Principle 2: Purpose Limitation
The scope of intended use
The second principle dictates that personal data must be collected for specified, explicit, and legitimate purposes and must not be processed further in a manner that is incompatible with those original purposes.
This principle is designed to prevent "function creep", a common corporate phenomenon where an organization collects customer or employee data for one specific reason and then quietly repurposes, sells, or monetizes that data for entirely unrelated commercial ventures without the individual's knowledge or consent.
Under the DPA 2018, when an organization collects data, it must clearly define why it is gathering that information at the point of collection. For instance, if a company collects a user's home address purely to ship a purchased pair of shoes, that data has a specified, explicit purpose: contract fulfillment and delivery. If the company subsequently decides to sell those addresses to a local real estate agency for direct mail marketing campaigns, it has violated the purpose limitation principle, because real estate marketing is entirely incompatible with shoe delivery.
Exceptions and further Processing
While purpose limitation is strict, the legislation recognizes certain public interest exceptions. Further processing for archiving purposes in the public interest, scientific or historical research purposes, or statistical purposes is generally considered compatible, provided that appropriate organizational and technical safeguards (such as data pseudonymization or anonymization) are implemented.
However, for standard commercial entities, if a new, secondary use for data arises that falls outside the scope of the original collection purpose, the organization must either obtain fresh, explicit consent or identify a new, legally robust lawful basis before proceeding.
Principle 3: Data Minimization
Quality over quantity
In the digital age, the prevailing corporate temptation has long been to hoard as much data as possible "just in case" it proves useful in the future. The third principle, Data Minimization, directly dismantles this practice.
According to this principle, personal data must be adequate, relevant, and limited to what is necessary in relation to the purposes for which they are processed.
Adequate: The data collected must be sufficient to properly fulfill the stated purpose. If an online bank needs to verify a customer’s identity to open an account, it needs enough data to do so effectively.
Relevant: There must be a rational, logical link between the data collected and the objective. Collecting information about a customer's musical preferences or favorite color is entirely irrelevant to opening a standard business bank account.
Limited to what is necessary: Organizations must restrict the volume of data collected to the absolute minimum required. If an online registration form only requires an email address and a password to create an account, demanding the user's home address, telephone number, mother's maiden name, and employment history violates data minimization.
The Risk-Reduction Benefit
Beyond legal compliance, data minimization serves as a vital cybersecurity defense strategy. Organizations that store massive, accumulated pools of unnecessary personal data expose themselves to catastrophic risk. In the unfortunate event of a data breach, hackers exfiltrate every piece of information stored on the server. By aggressively practicing data minimization, collecting only what is strictly necessary and deleting or anonymizing it when no longer required, organizations drastically shrink their "attack surface" and limit the potential harm inflicted upon individuals.
Looking ahead to part 2
The first three principles of the Data Protection Act 2018 establish a rigid framework governing why and how data is initially acquired and contextualized: it must be legal, fair, and transparent; it must serve a strictly defined purpose; and it must be restrained to the bare minimum necessary.
However, compliance does not stop at the point of collection. In the second part of this expert article, we will examine the remaining principles that govern the lifecycle of data: Accuracy, Storage Limitation, Integrity and Confidentiality (Security), and the overarching pillar of Accountability. We will also explore how these principles translate into actionable governance models for modern enterprises operating within the United Kingdom.
Deconstructing the framework: The final five principles
To fully grasp the architecture of the Data Protection Act 2018 (DPA 2018) and its harmonization with the UK GDPR, one must look beyond the initial requirements of lawfulness and purpose. The legislation establishes a comprehensive ecosystem designed to protect personal information throughout its entire lifecycle, from the moment of collection to its ultimate archiving or destruction.
Principle 3: Data minimisation
The third principle dictates that personal data must be adequate, relevant, and limited to what is necessary in relation to the purposes for which they are processed. In an era characterized by big data analytics and the temptation to harvest every available digital footprint, this principle acts as a vital restraint.
Adequacy and Relevance: Organisations must ensure they hold enough information to properly fulfill their stated objective, but nothing more. Collecting extraneous details "just in case" they might prove useful later is a direct violation.
Practical Application: If a digital subscription form requires only a user’s email address to deliver a newsletter, requesting home addresses, telephone numbers, and dates of birth breaches data minimisation. Controllers must routinely audit their intake forms, databases, and application fields to strip away non-essential data collection vectors.
Principle 4: Accuracy
Data must be accurate and, where necessary, kept up to date. Every reasonable step must be taken to ensure that personal data that is inaccurate, having regard to the purposes for which it is processed, is erased or rectified without delay.
The Ongoing Duty: Accuracy is not a static milestone achieved at the point of entry; it is an active, continuous obligation. When individuals notify an organization of a change in circumstances (such as a new residential address or updated contact details), systems must reflect these modifications promptly.
Challenging Data: If an individual disputes the accuracy of their data and its correctness cannot be immediately verified, organizations may be required to temporarily restrict processing while the matter is investigated.
The lifecycle and Security guardians
As data moves deeper into an organization's architecture, storage limitations and security controls take center stage.
Principle 5: Storage Limitation
Personal data must be kept in a form which permits identification of data subjects for no longer than is necessary for the purposes for which the personal data are processed.
[Data Ingestion] ---> [Active Processing Period] ---> [Retention Review] ---> [Secure Deletion / Anonymisation]
Retention Schedules: Organizations cannot adopt an indefinite "keep everything forever" strategy. They must establish rigorous data retention schedules that define precise lifecycles for different categories of information (e.g., retaining financial records for tax purposes for six years, but purging temporary visitor logs after thirty days).
Exceptions: The principle allows for longer retention periods only if the data is being processed solely for archiving purposes in the public interest, scientific or historical research, or statistical purposes, subject to appropriate technical safeguards.
Principle 6: Integrity and Confidentiality (Security)
Often referred to as the security principle, this mandate requires personal data to be processed in a manner that ensures appropriate security, including protection against unauthorized or unlawful processing and against accidental loss, destruction, or damage, using appropriate technical or organizational measures.
Defense in Depth: Compliance relies on a combination of robust technological defenses, such as end-to-end encryption, multi-factor authentication, secure firewalls, and regular vulnerability testing, and stringent organizational policies, including mandatory staff cybersecurity training and strict role-based access controls.
Minimizing Human Error: Because insider threats and accidental exposure remain major vectors for data breaches, this principle demands that access to personal data is restricted strictly on a need-to-know basis, guarding against casual internal curiosity as well as external cyberattacks.
The apex principle: Accountability
While the first six principles govern how data is handled, the seventh principle transforms compliance from a passive checklist into an active corporate culture.
Principle 7: Accountability
The accountability principle states that the data controller is responsible for, and must be able to demonstrate compliance with, all the preceding principles. It is not enough to simply follow the rules; an organization must possess the documentation, audit trails, and governance frameworks necessary to prove it.
Documentation and Evidence: Accountability requires maintaining comprehensive records of processing activities, executing Data Protection Impact Assessments (DPIAs) for high-risk processing, drafting crystal-clear internal privacy policies, and appointing Data Protection Officers (DPOs) where mandated.
Regulatory Scrutiny: In the event of an investigation or a data breach, the Information Commissioner’s Office (ICO) will look directly at an organization's accountability measures. Companies that can demonstrate a proactive, well-documented approach to privacy governance are far better positioned to mitigate regulatory penalties.
Navigating compliance in a Data-Driven world
The seven core principles of the Data Protection Act 2018 form an interconnected, mutually reinforcing blueprint for modern data governance. By intertwining transparency, minimization, accuracy, security, and absolute accountability, the framework shifts the burden of proof squarely onto organizations.
For businesses and public bodies alike, treating these principles not as bureaucratic hurdles, but as foundational pillars of trust, is essential. Mastering the DPA 2018 framework fosters a culture of digital respect, safeguarding fundamental human rights while enabling safe, responsible innovation in an increasingly connected global economy.