We've all clicked "Accept All Cookies" a million times without looking. The thing is, most people treat the EU General Data Protection Regulation like some boring digital wallpaper that tech companies just throw at us. That changes everything and nothing all at once, because beneath the legal jargon lies a radical blueprint for how personal data should be handled.
Where it gets tricky is that businesses love to talk about compliance like it's just a checklist, while regulators view it as a fundamental human right. We're far from it when it comes to companies actually getting it right every single time. To understand why this legislation still shakes up the global tech landscape years after its rollout, we have to look past the corporate PR and dive straight into the engine room: the core data protection principles.
The Bedrock of Digital Privacy: Article 5 Explored
If you want to understand European data privacy laws, you don't need a law degree; you just need to look at Article 5 of the GDPR. This section sets out the golden rules for processing personal data. These aren't suggestions or best practices you can swap out when budgets get tight—they are the mandatory pillars holding up the entire regulatory framework. People don't think about this enough, but every single app on your phone, every corporate database, and every marketing email campaign is secretly being measured against these exact standards.
Let's break down how these principles operate in the real world, stripping away the legalese to see what they actually demand from organizations holding our digital footprints.
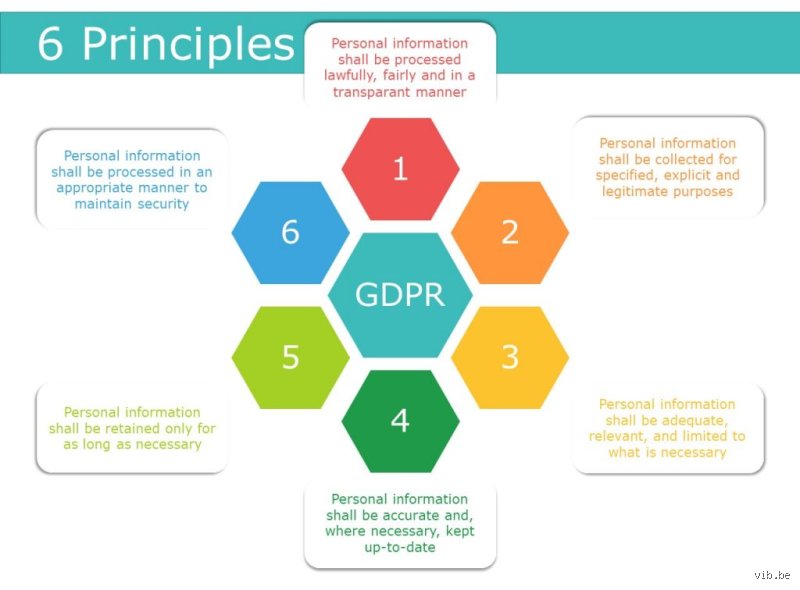
1. Lawfulness, Fairness, and Transparency: The Trust Triangle
The first principle states that personal data must be processed lawfully, fairly, and in a transparent manner in relation to the data subject. That sounds neat on paper, but where it gets tricky is balancing those three elements.
Lawfulness: The Legal Hook
You cannot just collect data because it feels useful. Organizations must have a valid legal basis—often called a "lawful ground"—to touch your data. The GDPR outlines six of these grounds, ranging from explicit consent and contractual necessity to compliance with a legal obligation or the vague concept of "legitimate interests." The thing is, organizations love to lean on legitimate interests when they aren't sure if your consent would hold up. But regulators have made it clear: if your processing activity overrides the fundamental rights and freedoms of the individual, that ground crumbles.
Fairness: Avoiding the Digital Trap
Fairness means you aren't blindsiding people. It stops organizations from using data in ways that are unjust, discriminatory, or wildly unexpected. Even if a company has a technical legal basis to collect your data, doing so through dark patterns—manipulative user interface designs that trick you into clicking "agree"—fails the fairness test immediately.
Transparency: Death of the 50-Page Privacy Policy
Transparency is the antidote to the old era of hidden clauses. For years, companies hid their data practices inside impenetrable walls of text. The GDPR says no: privacy notices must be concise, transparent, intelligible, and easily accessible, using clear and plain language. If a teenager or a busy parent can't reasonably understand what a company is doing with their location data or browsing history within a couple of minutes, the transparency principle has failed.
2. Purpose Limitation: The "No Scope Creep" Rule
Have you ever signed up for a fitness app that asked for your email, and then suddenly noticed it wants access to your contacts, your exact GPS coordinates, and your photo gallery? That is where purpose limitation steps in to draw a hard line.
This principle dictates that personal data must be collected for specified, explicit, and legitimate purposes and not further processed in a manner that is incompatible with those initial purposes.
Why Scope Creep is a Trap
The thing is, data is addictive. Once a company gets their hands on a user's information, the temptation to monetize it in new, unexpected ways—or feed it into a machine learning model—is massive. Purpose limitation acts as a digital leash.
If a company collects your home address to ship you a physical product, they cannot turn around and sell that address to a home insurance broker just because they realized there's money to be made. Further processing for archiving purposes in the public interest, scientific or historical research, or statistical purposes is sometimes granted exceptions, but for commercial businesses, the rule is strict: stick to the script you promised the user.
3. Data Minimization: Collecting Less to Protect More
People don't think about this enough, but the safest data breach is the data you never collected in the first place. This is the heart of data minimization: personal data must be adequate, relevant, and limited to what is necessary in relation to the purposes for which they are processed.
The End of "Just in Case" Data Hoarding
For decades, the corporate mindset was "collect everything right now, figure out what it's worth later." Massive data lakes filled with birth dates, mother's maiden names, and transaction histories sat waiting to be targeted by hackers. Data minimization flips that script.
Where it gets tricky for developers and product managers is designing systems that deliberately ignore information. If a simple age-verification check requires only knowing whether a user is over 18, forcing them to upload a scanned passport containing their full name, exact date of birth, photo, and passport number violates this principle. You are gathering a heavy payload of sensitive identifiers when a simple binary check would have done the job.
4. Accuracy: Keeping the Record Straight
Data changes. People move, change their phone numbers, update their email addresses, and alter their preferences. The accuracy principle requires that personal data must be accurate and, where necessary, kept up to date; every reasonable step must be taken to ensure that personal data that are inaccurate, having regard to the purposes for which they are processed, are erased or rectified without delay.
The Real-World Fallout of Bad Data
Why does this matter beyond keeping a clean CRM? Imagine an automated credit-scoring system or a background-checking algorithm making a decision about your financial future based on a misspelled name, an old debt that was actually settled, or a crossed wire in a database.
The accuracy principle puts the burden squarely on the organization to maintain hygienic records. If a user tells a company, "Hey, this piece of information you have on me is wrong," the organization can't just shrug and leave it in the system. They have a legal duty to correct it or wipe it out. That changes everything for industries built on automated profiling, forcing them to build robust feedback loops for correction.
Looking Ahead at the Core Framework
These first four principles—Lawfulness, Fairness, and Transparency; Purpose Limitation; Data Minimization; and Accuracy—form the operational bedrock of the entire EU privacy ecosystem. They shift the power dynamic away from passive consumers and toward individuals who retain sovereignty over their digital lives.
We're far from it being a frictionless transition, as companies constantly push the boundaries of what constitutes "legitimate interest" or "necessary minimization." But understanding these initial pillars gives you the exact lens needed to evaluate every app, website, and database you interact with on a daily basis.
<h2>Mastering Storage Limitation and Data Accuracy</h2> <p>Continuing our exploration of the core tenets enshrined in Article 5 of the European Union General Data Protection Regulation, storage limitation and data accuracy form the operational backbone of everyday data lifecycle management. Storage limitation dictates that personal data must not be kept in a form that permits the identification of data subjects for any longer than is strictly necessary for the purposes for which those records are processed. Organizations cannot simply hoard information indefinitely under the assumption that it might prove useful at some indeterminate point in the future. Instead, controllers must establish explicit retention schedules, regular review protocols, and automated deletion routines to purge or permanently anonymize files once their operational utility has expired.</p> <p>Hand in hand with retention is the principle of accuracy. Personal data must be factually correct and, where necessary, kept up to date. Enterprises bear an affirmative duty to take every reasonable step to ensure that inaccurate entries are erased or rectified without undue delay, having full regard to the purposes for which they are handled. In practice, this requires deploying validation checks at data entry points, updating customer or employee records upon notification of change, and maintaining verification loops. Failing to keep data accurate not only violates the regulation but can also cause severe operational errors and misguided automated decisions that directly harm the individuals concerned.</p> <h2>Enforcing Integrity, Confidentiality, and Accountability</h2> <p>The final foundational pillars detailed within the primary provisions of the legislation center on security and proof of compliance. The principle of integrity and confidentiality mandates that personal data must be processed in a manner that ensures appropriate security. This involves robust technical and organizational safeguards designed to protect against unauthorized or unlawful processing, accidental loss, destruction, or structural damage. Organizations must implement comprehensive cybersecurity measures such as end-to-end encryption, multi-factor authentication, rigorous access controls, network segmentation, and tested incident response plans to thwart modern threat vectors.</p> <p>However, implementing these security controls is only half the battle; an organization must also be able to prove its adherence through accountability. The accountability principle explicitly places the burden of proof on the data controller. It is not enough to simply claim compliance with the law; entities must actively demonstrate that their processing operations align with every single tenet outlined in Article 5. This calls for maintaining detailed processing records, executing data protection impact assessments for high-risk operations, appointing data protection officers where mandated, and embedding privacy by design and by default into every engineering and administrative workflow.</p> <h2>Navigating Lawful Bases and Practical Implementation</h2> <p>To operationalize these core principles successfully, controllers must anchor every single data processing activity to one of the six lawful bases specified under Article 6 of the regulation. These grounds include obtaining unambiguous consent from the data subject, fulfilling a contractual obligation, complying with a legal requirement, protecting vital interests, performing a task carried out in the public interest, or pursuing a legitimate interest that is not overridden by the fundamental rights and freedoms of the individual. Establishing the correct legal basis must happen before any data collection begins, ensuring that transparency and lawfulness are maintained from the outset.</p> <p>Ultimately, treating the European data protection principles as a mere checklist is a failing strategy for modern enterprises. True compliance requires a cultural shift toward proactive digital stewardship. By weaving purpose limitation, minimization, security, and accountability into the daily DNA of corporate operations, businesses minimize legal liabilities while simultaneously building deep, lasting trust with their customer base. In an interconnected global economy where data is a primary currency, respecting these fundamental rights is both a strict regulatory obligation and a distinct competitive advantage.</p>