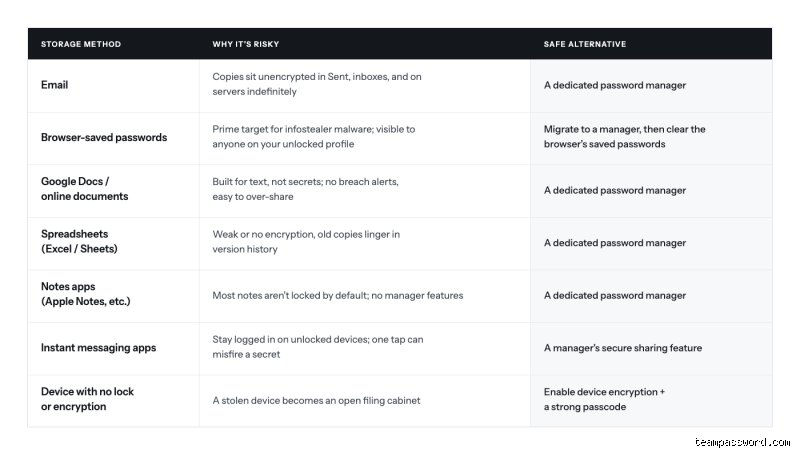
When cybersecurity experts are asked, "What is the worst way to store a password?" the answer rarely points to just a single mistake. Instead, it involves a widespread habit of convenience over security. To understand how to protect your digital identity, you must first understand the primary methods that are not safe for storing passwords, and why attackers love them.
The root cause: Password fatigue and human behavior
Before diving into the specific unsafe storage methods, it is vital to understand why people use them. The average internet user juggles dozens of online accounts. Security best practices dictate that every single one of these accounts should have a unique, long, complex password featuring a mix of uppercase letters, lowercase letters, numbers, and symbols.
Asking a human brain to memorize twenty different 16-character randomized strings like xK9#mP2$vL8@qW5! is an impossible task. This phenomenon is known in the cybersecurity community as password fatigue. When overwhelmed by the sheer volume of credentials they need to remember, users naturally look for shortcuts. Unfortunately, these shortcuts often hand the keys of the kingdom directly to malicious actors.
Let’s examine the first major category of unsafe password storage: physical documentation.
Unsafe method #1: The Physical sticky note or notebook
It sounds like a trope from an old spy movie, but one of the most common, and catastrophic, ways people store passwords is by writing them down on a physical medium. This includes:
A sticky note attached to the bezel of a computer monitor.
A piece of paper tucked underneath a keyboard or mousepad.
A dedicated notebook kept on a desk or inside an unlocked desk drawer.
Why It Fails
Physical security is the foundation of overall security. While digital hackers rely on malware, phishing, and brute-force algorithms, physical adversaries rely on opportunity and observation.
The "Visual Hack" (Tailgating and Shoulder Surfing): If you write your passwords on a sticky note attached to your monitor or laptop, anyone who walks past your desk, visits your room, or sits near you in a public space (like a library or coffee shop) can see your master keys instantly. This requires zero technical skill, just working eyes.
The Vulnerability of Shared Spaces: For teenagers and students, bedrooms, dorms, and classrooms are frequently visited by friends, siblings, parents, or classmates. A notebook containing every single password you own is an open invitation for curiosity, mischief, or malicious intent.
No Audit Trail: If someone logs into your account using a password they stole from a physical note, there is often no digital log or warning indicating how they obtained it. You are left wondering how your account was compromised when the vulnerability was sitting right in plain sight on your desk.
Unsafe method #2: Unencrypted Plain-Text Digital Files
When people realize that physical sticky notes are risky, they often transition to digital methods. However, storing passwords in a digital format without proper encryption is just as hazardous. Common examples include:
A text file named passwords.txt or logins.txt saved directly on a computer’s desktop.
A Microsoft Word document, Google Doc, or Apple Notes file containing an unorganized list of usernames and passwords.
A spreadsheet (like Excel or Google Sheets) with columns labeled "Website," "Username," and "Password."
Why It Fails
At first glance, saving a file on your computer or in the cloud feels secure because it isn't lying on a physical desk. However, plain text is readable text. It lacks any form of cryptographic protection.
Malware and Infostealers: The internet is crawling with automated malware designed specifically to scan local hard drives for files with names like "passwords," "credentials," or "login." If your computer is ever infected with an infostealer, often downloaded accidentally through cracked software, sketchy game mods, or phishing links, these text files and spreadsheets are among the first targets exfiltrated back to the attacker.
Cloud Sync Vulnerabilities: If you store an unencrypted password document in a cloud storage service (like iCloud, Google Drive, or OneDrive) for the sake of accessibility, you are trusting the security of that cloud account entirely. If your main cloud account gets compromised through a weak password or a phishing attack, every single password you own is downloaded by the attacker in one fell swoop.
Accidental Sharing: It is shockingly easy to accidentally share a Google Doc or a cloud-synced note with the wrong person, or leave a link set to "Anyone with the link can view." A single misclicked button can expose your entire digital life to the public internet.
Unsafe method #3: Built-In Browser Storage without a master Password
Modern web browsers (like Google Chrome, Microsoft Edge, and Safari) offer a very tempting feature: the built-in password manager. When you log into a new website, a pop-up asks, "Do you want to save this password?" Click yes, and the browser auto-fills it for you the next time you visit.
While modern browsers do encrypt these databases locally, using them without secondary protection (such as a strong operating system login password, biometric lock, or a browser master password) introduces massive risks.
Why It Fails
The convenience of browser autofill makes it a double-edged sword.
Physical Access Equals Total Access: If you leave your laptop or phone unlocked and walk away for just two minutes, anyone who picks up your device can open your browser settings, reveal your stored passwords in plain text with a single click, and compromise every account you have tied to that browser profile.
Session Hijacking and Cookie Theft: If malware manages to compromise your active operating system session, attackers don't even need to crack your passwords, they can often steal the browser's decrypted session tokens or export the entire password database directly from the browser's local application data folder.
Ecosystem Lock-in and Vulnerability: Relying solely on a browser locks# The Anatomy of Credential Security: Identifying Unsafe Password Storage Methods in the Modern Threat Landscape
The Digital identity crisis
In an era where our entire lives, from financial portfolios and healthcare records to social interactions and professional workflows, are tethered to digital accounts, the password remains the primary digital gatekeeper. Yet, despite decades of security awareness campaigns, data breaches, and credential-stuffing attacks, human behavior regarding password management continues to be the single greatest vulnerability in cybersecurity.
When organizations or individuals ask, "Which is not a safe method for storing passwords?" the answer is often multifaceted, spanning a spectrum from glaringly obvious mistakes to subtle, everyday habits that feel convenient but expose users to catastrophic risk.
To build a resilient security posture, we must first dismantle the illusion of safety. This comprehensive first part of our expert analysis explores the myriad ways people improperly store credentials, dissecting the mechanics of why these methods fail, how threat actors exploit them, and why convenience consistently undermines security.
1. The hall of shame: Unsafe Password Storage Methods defined
Before exploring the nuances of secure cryptographic vaults, it is critical to identify the practices that represent absolute hazards in credential management. Any method that exposes plaintext credentials, relies on obscurity rather than encryption, or centralizes access without adequate multi-factor protection falls squarely into the category of an unsafe method.
The most prominent unsafe password storage methods include:
Plaintext Digital Files: Storing passwords in unencrypted text files (passwords.txt), word processors (passwords.docx), or spreadsheets (credentials.xlsx) stored locally or in standard cloud folders.
Physical and Analog Recording: Writing passwords on sticky notes attached to monitors, notebooks left on desks, or slips of paper hidden inside desk drawers or phone cases.
Unprotected Browser Storage: Relying solely on default browser autofill features without a hardened master password, device-level biometric locks, or zero-knowledge encryption architectures.
Memory and Mental Reuse: Memorizing a single, weak password and utilizing it across dozens of distinct services, apps, and platforms.
Insecure Messaging and Notes Apps: Texting passwords to oneself, emailing them via unencrypted protocols, or storing them in cloud notes apps (like standard Apple Notes or Google Keep without advanced note-level protection) that lack end-to-end encryption at rest.
Each of these methods introduces a specific vector of vulnerability, transforming a secret credential into an easily accessible asset for attackers, malware, or opportunistic onlookers.
2. Deep dive: Plain text and unencrypted Digital Files
Saving passwords in a simple text document or spreadsheet is one of the oldest and most dangerous mistakes in computing. While it offers the immediate gratification of quick access and easy updates, it completely disregards the reality of modern endpoint security threats.
The Threat of malware and Infostealers
Modern cybercrime relies heavily on automated malware strains known as infostealers (e.g., RedLine, Racoon, Vidar). These malicious payloads are often downloaded inadvertently through cracked software, phishing links, or compromised advertisements. Once inside a system, infostealers do not randomly guess passwords; instead, they systematically scan local drives, desktop directories, and document folders for specific keywords like password, login, bank, credentials, or accounts.
If an attacker finds a file named passwords.txt sitting on a desktop or buried in a documents folder, the malware exfiltrates the file in milliseconds. Because the data is stored in plain text, no decryption, brute-forcing, or cryptographic cracking is required. The attacker instantly gains a complete, unmasked map of the victim's digital life.
The flaw of standard Cloud syncing
Many users attempt to solve the "lost file" problem by saving their plain text password lists in cloud storage services or syncing them across devices. While cloud providers employ robust security for their infrastructure, storing unencrypted credential files in standard cloud storage introduces significant risks:
Account Compromise: If a user’s primary cloud account is compromised via a phishing attack or weak primary password, every file within that cloud repository, including the plaintext credential list, is immediately accessible to the intruder.
Third-Party Inspection: Standard cloud platforms process data in environments where metadata, accidental public link sharing, or internal misconfigurations can expose files.
Compromised Endpoints: If a synced device is stolen or accessed while unlocked, the cloud-synced file is readymade for extraction.
3. The pitfalls of Physical and Analog Storage
In an age dominated by sophisticated cyberattacks, physical security is sometimes mistakenly viewed as completely distinct from digital security. However, analog methods of storing passwords introduce unique vulnerabilities that are just as devastating as digital breaches.
The sticky note paradox
The iconic image of a yellow sticky note plastered to the bottom of a keyboard or the bezel of a computer monitor remains an enduring symbol of corporate and domestic security negligence. While it provides instant visual recall, it violates the most fundamental rule of credential management: physical proximity equals total compromise.
Tailgating and Visitor Access: Offices, coworking spaces, coffee shops, and even homes are frequently visited by cleaners, delivery personnel, guests, or unauthorized individuals. A sticky note requires zero technical skill to exploit; it merely requires a quick glance.
The Shared Workspace Threat: In environments where desks are shared or hot-desking is practiced, visible passwords invite malicious insiders or curious colleagues to harvest credentials with absolute impunity.
Physical notebooks and diaries
Some users, distrustful of digital security, choose to write all their complex passwords down in a dedicated notebook or journal. While superior to a sticky note in terms of visibility (since a closed book is not openly displayed), a physical notebook presents distinct logistical hazards:
Loss and Theft: Laptops, backpacks, and purses are routinely lost or stolen. A physical notebook containing credentials to financial accounts, email, and corporate networks represents a catastrophic physical leak.
Lack of Revocation: If a digital password manager is compromised, accounts can be locked, sessions revoked, and credentials changed instantly. If a physical notebook is stolen, the victim may not notice its absence for days, leaving a window of vulnerability during which attackers can systematically test every listed credential.
4. Browser-Based Vulnerabilities and Unprotected Storage
Web browsers have evolved into comprehensive digital ecosystems, offering built-in password managers designed to streamline user experience across web sessions. While modern browser security has improved drastically, incorporating master passwords, hardware-backed encryption, and synchronization safeguards, relying on unprotected or default browser storage remains a significant risk factor.
The danger of Shared device Access
The primary vulnerability of default browser password storage surfaces in shared environments. Whether it is a family computer, a shared household tablet, or a public terminal, browsers often persist login sessions and autofill credentials automatically.
If a browser is not secured behind a robust master password, operating system PIN, or biometric check, anyone who physically accesses the device can open the browser settings, reveal masked passwords with a single click, and seamlessly log into sensitive accounts.
Browser profile Theft and Infostealers
Beyond casual physical access, browsers are primary targets for specialized malware. Infostealers are specifically engineered to target browser profile databases (such as those maintained by Chromium-based browsers like Google Chrome and Microsoft Edge, as well as Firefox).
While browsers encrypt stored passwords using operating-system-level mechanisms (like Windows DPAPI or macOS Keychain), advanced malware running with user privileges can often extract and decrypt these credentials directly from memory or local profile directories, bypassing the browser's user interface entirely.
5. Mental shortcuts: The illusion of memory and Password Reuse
While not a "storage" method in the traditional physical or digital sense, relying on human memory to manage dozens of complex credentials invariably leads to unsafe behavioral workarounds.
When individuals attempt to memorize their passwords, cognitive limitations force them into predictable patterns:
Password Recycling: Using the same password (or minor variations of it, such as Spring2025! and Summer2025!) across multiple platforms. This enables credential stuffing attacks, where automated bots take a leaked password from a low-security breach (like a compromised gaming forum) and test it against high-value targets (like banking or email portals).
Predictable Simplicity: Crafting passwords that are easy to remember (e.g., pet names, birthdays, favorite sports teams), making them exceptionally vulnerable to brute-force and dictionary attacks.
Conclusion of Part 1
Understanding what constitutes an unsafe method for storing passwords is the essential first step toward digital self-defense. Whether it is a plaintext document sitting on a vulnerable hard drive, a sticky note on a monitor, or an unprotected browser cache, these methods bypass the cryptographic safeguards necessary to protect modern identities.
In Part 2 of this expert analysis, we will explore the architectural blueprint of secure credential management, examining how modern password managers, zero-knowledge encryption frameworks, and multi-factor authentication permanently eliminate these vulnerabilities.
...continuing our exploration of digital security practices, let us examine further vulnerabilities that often go unnoticed by casual internet users. While saving passwords on sticky notes or in basic plaintext text documents are classic examples of insecure storage, modern digital habits have introduced more sophisticated, yet equally dangerous, methods of mishandling credentials.
Beyond Plaintext: Hidden dangers in everyday Storage
As individuals become more aware of basic cybersecurity risks, they frequently migrate away from physical paper or simple Notepad files, only to adopt other habits that provide a false sense of security. Understanding what not to do is just as important as knowing the right tools to use.
1. Unencrypted spreadsheets and document Files
A very common pitfall is storing a list of usernames and passwords inside an Excel spreadsheet, a Word document, or a cloud-synced notes app (like Apple Notes or Google Keep) without an active, robust encryption layer.
The Vulnerability: Many users believe that because a file is stored on a password-protected computer or inside a cloud account, it is safe. However, if malware infiltrates your device, or if your cloud account experiences a credential leak or unauthorized access, these files are instantly readable.
The Exception: While some spreadsheet programs allow password-protection or encryption (e.g., password-protecting an Excel workbook), the encryption algorithms used in older versions can be easily cracked with modern brute-force tools, making this a suboptimal and risky choice compared to dedicated cryptographic vaults.
2. Relying solely on Browser Auto-Fill without master protection
Modern web browsers (Chrome, Safari, Firefox, Edge) offer built-in password managers that save credentials conveniently. While these tools have improved drastically in recent years, storing your entire digital identity in a browser without adequate secondary authentication can be perilous.
The Vulnerability: If a malicious actor gains physical access to your unlocked computer, or if a piece of malware (infostealer trojan) targets your browser profile data, all stored credentials can be extracted in seconds.
The Mitigation: If you use a browser-based password manager, it must be locked behind a strong master password, a device PIN, or biometric verification (such as FaceID or fingerprint scanning) rather than auto-logging you in every time the browser opens.
3. Reusing and Tweak-Patterning passwords
Though technically a usage habit rather than a storage method, password reuse is intimately tied to storage failures. When people find remembering unique passwords difficult, they often store one "master" password in an unsafe place and use slight variations of it across dozens of sites.
The Vulnerability: If a minor website or forum suffers a data breach and leaks your password in plaintext or weak hashes, attackers immediately run automated credential stuffing attacks against your email, banking, and social media accounts using that exact password and its variations. One weak link compromises your entire digital footprint.
The Anatomy of a secure alternative
To replace these dangerous habits, cybersecurity experts recommend shifting away from human memory and ad-hoc storage toward automated, cryptographic solutions.
Dedicated Password managers
The gold standard for credential storage is a reputable, zero-knowledge password manager (such as Bitwarden, 1Password, or Dashlane). These applications use advanced encryption standards (like AES-256) locally on your device before syncing any data to the cloud.
Zero-Knowledge Architecture: This means the service provider has zero knowledge of your master password or your vault contents. Even if the company's servers are compromised, your data remains indecipherable ciphertext without your unique master key.
Random Generation: Password managers eliminate the human element of creating weak, memorable passwords by generating long, complex, completely random strings for every single account you own.
The Rise of Passkeys
Looking toward the future, the industry is increasingly adopting passkeys, a replacement for passwords that provides faster and more secure sign-ins to websites and apps. Based on public-key cryptography, passkeys bind your account to a trusted device (like your phone or computer) using biometrics or a PIN. Because there is no password string to steal, store, or guess, passkeys completely eliminate the risks associated with poor password storage methods.
Multi-Factor Authentication: The safety net
Even the best password storage strategy can occasionally face hurdles if a master password is exposed through phishing. This is why Multi-Factor Authentication (MFA) or Two-Factor Authentication (2FA) is non-negotiable.
What it does: MFA requires you to provide two or more verification factors to gain access to an account. These typically include something you know (your password), something you have (an authenticator app or hardware security key), or something you are (biometrics).
Why it matters: Even if an attacker discovers that you stored your password on an insecure sticky note or an unencrypted file, they cannot access your account without also possessing your physical phone or hardware token.
Conclusion
Securing your digital life begins with eliminating convenience-driven shortcuts. Storing passwords on sticky notes, in unencrypted text files, inside basic spreadsheets, or reusing them across platforms leaves your personal data wide open to automated threats and opportunistic breaches.
By abandoning these unsafe methods in favor of zero-knowledge password managers, embracing passkeys, and enforcing multi-factor authentication across all critical accounts, you transform your security posture from vulnerable to resilient. In an era where digital threats evolve daily, adopting robust storage hygiene is no longer optional, it is an essential practice for navigating the modern internet safely.