At the heart of defending this hyper-connected ecosystem lies Information Security (InfoSec). Far from being a mere IT afterthought or a collection of random software tools, InfoSec is a comprehensive, rigorous discipline grounded in enduring core principles. This first installment of our comprehensive expert series unpacks the foundational architecture of information security, exploring the philosophy, mechanisms, and models that keep our digital civilization functioning.
The modern paradigm: Why InfoSec matters now more than ever
To understand the core principles of information security, one must first dismantle a common misconception: InfoSec is not exclusively about technology. While firewalls, encryption algorithms, and intrusion detection systems are vital tools, technology is only one pillar of a successful security posture. The other two pillars are people and processes.
Information security is the practice of protecting information—both physical and digital—from unauthorized access, use, disclosure, disruption, modification, or destruction. Its ultimate objective is to preserve the value of organizational and personal assets while maintaining business continuity and trust. When security fails, the consequences ripple outward. A single breached database can expose millions of Social Security numbers, medical histories, and credentials, leading to devastating financial loss, identity theft, and eroded public trust.
To prevent these catastrophes, security architects and practitioners rely on time-tested frameworks that govern how data is handled throughout its lifecycle. Chief among these frameworks is the venerable CIA Triad.
The bedrock: Dissecting the CIA Triad
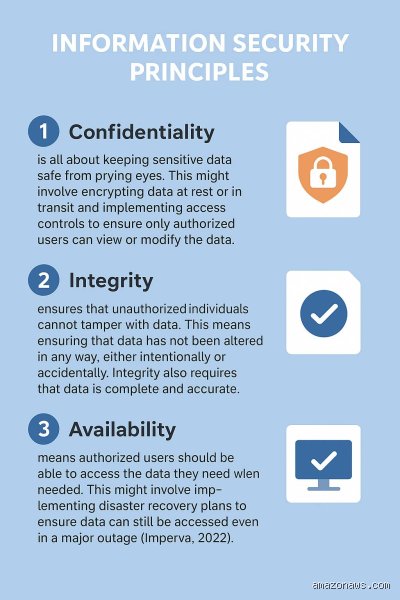
For decades, the CIA Triad, comprising Confidentiality, Integrity, and Availability, has served as the undisputed North Star of information security. Every security policy, technology investment, and risk assessment maps back to one or more of these three pillars. Let us examine each component in meticulous detail.
1. Confidentiality: Shielding Data from prying Eyes
Confidentiality ensures that sensitive information is accessed only by authorized individuals, entities, or processes, and is strictly withheld from those lacking proper clearance. Think of it as the digital equivalent of a bank vault or a classified document stamped "Eyes Only."
Achieving confidentiality requires a multi-layered defense strategy:
Encryption: Transforming plaintext into unreadable ciphertext using complex mathematical algorithms (such as AES-256). Encryption is applied both at rest (stored on hard drives or cloud buckets) and in transit (moving across networks via protocols like TLS/HTTPS).
Access Control Models: Implementing the principle of Least Privilege, which dictates that users and systems are granted only the bare minimum permissions necessary to perform their specific duties. Mechanisms like Role-Based Access Control (RBAC) and Multi-Factor Authentication (MFA) enforce strict boundaries.
Data Classification: Categorizing data based on sensitivity (e.g., Public, Internal, Confidential, Restricted) so that appropriate security controls can be applied proportionally.
When confidentiality is breached, such as through a corporate data leak or a man-in-the-middle interception, organizations face severe regulatory penalties, loss of intellectual property, and reputational damage.
2. Integrity: Maintaining truth and Trust in Digital assets
While confidentiality guards who sees data, Integrity guards what happens to data. Integrity ensures that information remains accurate, complete, and trustworthy throughout its entire lifecycle. It prevents unauthorized creation, alteration, or deletion of data, whether caused by malicious actors, software bugs, or hardware failure.
Imagine a financial ledger where an attacker covertly alters a decimal point to siphon funds, or a software update package infected with malware during transit. Without robust integrity controls, these alterations would go unnoticed.
Key mechanisms upholding integrity include:
Cryptographic Hashing: Algorithms like SHA-256 generate a unique, fixed-size digital fingerprint (hash) of a file or data packet. If even a single bit of the data changes, the resulting hash changes drastically, immediately signaling tampering.
Digital Signatures: Providing cryptographic proof of the origin and integrity of a message or software document, guaranteeing that it has not been forged or altered in transit.
Version Control and Audit Logs: Tracking every modification made to a system, database, or document, enabling administrators to trace changes back to specific users and timestamps.
3. Availability: Ensuring resilient Access when it counts
The final pillar of the triad, Availability, ensures that information, network resources, and critical services are accessible to authorized users whenever they are needed. A system can have flawless confidentiality and absolute integrity, but if legitimate users cannot access it, the system is effectively useless.
Availability is the primary target of Denial-of-Service (DoS) and Distributed Denial-of-Service (DDoS) attacks, where malicious actors flood servers with junk traffic until they crash under the load. It is also threatened by hardware failures, natural disasters, power outages, and ransomware infections that lock up critical databases.
To achieve high availability, architects rely on:
Redundancy and Failover: Designing systems with duplicate components (such as backup generators, redundant network paths, and mirrored servers) so that if one fails, another takes over instantly without service interruption.
Load Balancing: Distributing incoming network traffic across multiple servers to prevent any single machine from becoming a bottleneck or failing under heavy load.
Disaster Recovery and Backups: Establishing rigorous backup routines (such as the 3-2-1 backup rule) and tested recovery plans to restore operations rapidly after a catastrophic event.
Expanding the architecture: Beyond the core Triad
While the CIA Triad provides the foundational philosophy, modern cybersecurity frameworks expand these principles to address the complexities of modern digital environments. Two crucial extensions form the backbone of identity and trust management:
Authenticity and Non-Repudiation
Authenticity verifies that a user, device, or data source is genuine and exactly who or what they claim to be. In an age of sophisticated phishing and deepfakes, verifying provenance is critical.
Non-Repudiation ensures that a party in a transaction cannot deny the authenticity of their signature on a document or the sending of a message that they originated. This is vital for legal, financial, and contractual digital transactions.
Accountability and Auditability
Every action within a secure system must be traceable to a specific, accountable entity. Accountability ensures that users can be held responsible for their actions through comprehensive logging, monitoring, and non-repudiation controls. Without accountability, detecting insider threats or investigating breaches becomes virtually impossible.
Looking ahead to Part 2
As we have established, information security is built upon a sophisticated interplay of confidentiality, integrity, availability, and their extended governance principles. However, understanding these concepts is only the starting point.
In Part 2 of this expert series, we will transition from abstract principles to practical implementation, exploring how organizations construct defense-in-depth strategies, deploy zero-trust architectures, navigate human risk management, and anticipate the cybersecurity challenges of the next decade.
...Building upon the foundational framework of the CIA Triad (Confidentiality, Integrity, and Availability) explored in the first half of this article, modern information security requires a robust set of operational principles. Securing enterprise environments, cloud infrastructure, and personal data goes far beyond basic encryption and firewalls; it demands a philosophy of architecture and governance designed to anticipate, withstand, and recover from sophisticated threats.
Below is the continuation and conclusion of our expert guide, exploring the advanced core principles that dictate modern cybersecurity defense.
4. The Principle of Least Privilege (PoLP)
One of the most effective security controls in any organization is the Principle of Least Privilege (PoLP). Simply put, PoLP dictates that every user, process, application, and system component must be given only the minimum levels of access, or privileges, necessary to complete its specific, authorized task, and nothing more.
Why Least Privilege matters
Historically, users and internal systems were often granted broad, sweeping permissions for the sake of convenience. An employee in marketing might have had access to financial servers, or a standard web application might run with root-level database permissions. When an account like this is compromised through phishing or malware, the attacker inherits those broad privileges, turning a localized incident into a catastrophic enterprise-wide breach.
Implementing PoLP drastically reduces the blast radius of a security incident. Key implementation strategies include:
Just-In-Time (JIT) Access: Elevating privileges only when needed for a specific task and automatically revoking them afterward.
Role-Based Access Control (RBAC): Assigning permissions based on organizational roles rather than individual identities, ensuring consistency and auditability.
Privileged Access Management (PAM): Specialized tools to monitor, vault, and secure administrative accounts that hold elevated powers.
5. Defense in Depth (DiD)
In cybersecurity, relying on a single protective barrier, no matter how robust, is a recipe for disaster. Attackers are persistent, adaptable, and equipped with automated tools capable of bypassing perimeter defenses. This is where Defense in Depth (DiD), also known as layered security, becomes indispensable.
+-------------------------------------------------------+
| Perimeter Defense |
| (Firewalls, DDoS Protection) |
| +-----------------------------------------------+ |
| | Network Layer | |
| | (VLANs, Micro-segmentation) | |
| +-----------------------------------------------+ |
| | Host & Endpoint Security | |
| | (EDR, Antivirus, Patching) | |
| +-----------------------------------------------+ |
| | Application Security | |
| | (WAF, Input Validation, AuthN) | |
| +-----------------------------------------------+ |
| | Data Security | |
| | (Encryption at Rest/Transit) | |
| +-----------------------------------------------+ |
The Layered Approach
Defense in Depth deploys multiple independent security controls across different layers of an IT architecture. If an attacker successfully breaches the outer perimeter firewall, they encounter internal network segmentation. If they bypass the network controls, they face endpoint detection and response (EDR) software on individual workstations. Beyond that, critical data remains encrypted at rest and in transit, rendering it unreadable even if stolen.
By overlapping these defenses, organizations ensure that the failure of one control does not automatically result in total system compromise. It buys precious time for security operations centers (SOCs) to detect, isolate, and neutralize threats before they achieve their objectives.
6. Separation of Duties (SoD)
To prevent fraud, error, and abuse of power, information security incorporates the principle of Separation of Duties (SoD). SoD requires that no single individual or entity should have end-to-end control over a critical, high-risk process or transaction.
In Software Development: The developer who writes code should not be the same person who pushes it directly into the production environment without independent code review and security testing.
In Financial Operations: The person who initiates a high-value wire transfer should not have the authorization to approve and release the funds.
By dividing critical tasks among multiple parties, organizations introduce natural checks and balances. Collusion between multiple bad actors becomes necessary to bypass the control, significantly raising the barrier for malicious activity.
7. Fail-Safe defaults and resiliency
Systems inevitably encounter errors, unexpected inputs, power outages, and cyber attacks. How a system responds under duress is defined by the principle of fail-safe defaults.
Designing for Failure
In secure system design, the default configuration should always lean toward maximum security rather than maximum availability or convenience. For example:
If an authentication server crashes or loses network connectivity, the default state of the downstream access control systems should be deny access rather than granting open access to keep business operations running.
If an encryption process encounters an unhandled exception, the data must not be written in plaintext; instead, the transaction must abort safely.
Coupled with fail-safe defaults is resiliency and redundancy, ensuring that critical systems can maintain operations or recover rapidly through immutable backups, disaster recovery sites, and automated failover mechanisms.
8. Zero Trust: The modern Security paradigm
For decades, enterprise security relied on a "castle-and-moat" model: everything inside the corporate network perimeter was trusted, while everything outside was viewed with suspicion. With the rise of cloud computing, remote workforces, and mobile devices, that traditional perimeter has effectively dissolved.
Enter Zero Trust.
The core philosophy of Zero Trust, popularized by the mantra "Never trust, always verify," assumes that threats exist both outside and inside traditional network boundaries. Under a Zero Trust architecture:
Explicit Verification: Every access request must be authenticated, authorized, and encrypted based on all available data points, including user identity, location, device health, service or workload, data classification, and anomalies.
Least Privilege Access: As discussed earlier, users are restricted with Just-In-Time (JIT) and Just-Enough-Access (JEA) models.
Assume Breach: Organizations minimize blast radius by segmenting access, deploying end-to-end encryption, and utilizing analytics to gain visibility into threat behavior.
The human element and future horizons
Information security is fundamentally a socio-technical challenge. While cryptographic algorithms, firewalls, and artificial intelligence-driven anomaly detection tools form the technical backbone of modern defense, the human element remains both the most critical asset and the most vulnerable attack vector. Phishing, social engineering, and accidental misconfigurations continue to account for the vast majority of successful breaches.
Mastering the core principles of information security, Confidentiality, Integrity, Availability, Least Privilege, Defense in Depth, and Zero Trust, is not merely an IT compliance checkbox. It is an evolving mindset. As technology marches forward into eras defined by quantum computing and autonomous AI agents, these core principles will remain the unchanging compass guiding organizations toward a secure, resilient digital future.