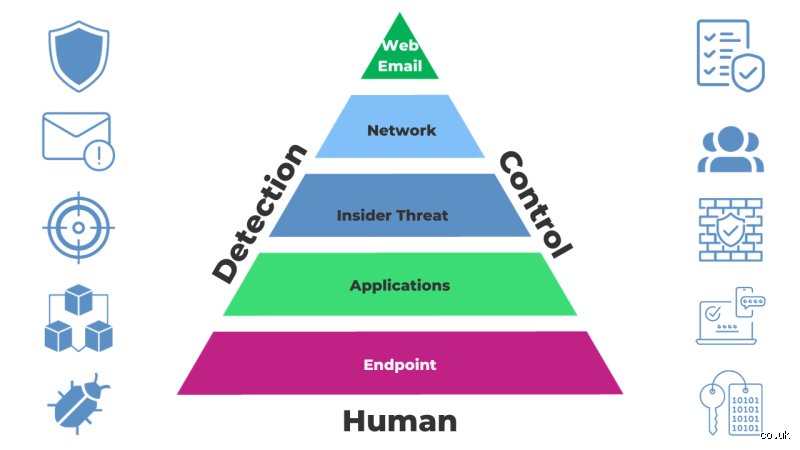
The landscape of modern cybersecurity has fundamentally transformed, leaving behind the days when a single, heavily fortified perimeter could guarantee an organization's digital safety. Because threat actors are increasingly sophisticated—relying on automated exploits, zero-day vulnerabilities, and highly targeted social engineering campaigns—traditional security paradigms have completely crumbled. Today, organizations can no longer afford to treat cybersecurity as a castle-and-moat architecture where everything outside is untrusted, and everything inside is assumed to be safe.
Instead, the modern digital ecosystem demands a philosophy of Defense in Depth, a military-inspired strategy that deploys multiple, overlapping security controls to protect sensitive assets. If a single layer fails—whether due to human error, a software bug, or a clever phishing attack—subsequent layers stand ready to detect, contain, and mitigate the threat before it can cause catastrophic damage. (This core philosophy is the bedrock of resilient enterprise architecture.)
In this comprehensive first part of our expert series, we will dissect the foundational principles of layered security, explore its underlying architecture, and examine the first critical tiers of defense that every robust cybersecurity framework must implement.
The Philosophy of Defense in Depth: Why One Layer Is Never Enough
To truly understand layered security, one must first dismantle the illusion of absolute prevention. No firewall is impenetrable, no employee is entirely immune to manipulation, and no software codebase is 100% free of vulnerabilities. Recognizing this harsh reality is the first step toward building an effective defense strategy. But how can security leaders protect critical infrastructure when failure is statistically inevitable?
The answer lies in risk mitigation through redundancy and compartmentalization. Layered security operates on the principle that the probability of a catastrophic breach decreases exponentially when an attacker is forced to bypass multiple, independent barriers. Imagine a high-security bank vault: it does not rely solely on a heavy steel door. It features motion detectors, silent alarms, time locks, security guards, reinforced concrete walls, and biometric scanners. If a thief manages to pick the lock on the front door, they are immediately confronted with laser grids and security personnel.
Digital security must mirror this physical resilience. By distributing security controls across different tiers—physical, network, host, application, and data—organizations create a gauntlet for unauthorized actors. Every additional layer increases the attacker's time, cost, and exposure, dramatically raising the likelihood that their malicious activity will be detected and neutralized long before they reach their ultimate objective.
Core Element 1: Physical Security (The Foundational Layer)
It is a common misconception that cybersecurity exists purely in the ethereal realm of code, packets, and cloud servers. However, even the most advanced encryption algorithms and zero-trust network policies are rendered completely useless if an unauthorized individual can walk into a server room with a USB drive or walk away with physical hardware. Physical security forms the bedrock upon which all other digital security layers are built.
Access Control and Perimeter Hardening
Physical security begins at the outermost boundary of an organization's facilities and extends all the way down to individual server racks. Data centers and server rooms must incorporate multi-factor physical authentication mechanisms, such as smart cards, biometric scanners (retinal or fingerprint recognition), and mantrap portals that prevent tailgating.
Furthermore, surveillance systems—including high-definition closed-circuit television (CCTV) cameras with motion tracking and night vision—must continuously monitor all access points, hallways, and server enclosures. And organizations must maintain rigorous logs of every physical entry and exit, cross-referencing visitor badges with digital access logs to detect anomalies.
Environmental Controls and Hardware Integrity
Protecting hardware is not just about keeping unauthorized people out; it also involves safeguarding equipment from environmental hazards and physical tampering. Key physical security components include:
Climate Control: Maintaining strict temperature and humidity ranges to prevent hardware degradation and overheating.
Fire Suppression Systems: Deploying advanced, non-water-based suppression systems (like clean agent gases) that extinguish fires without destroying electronic components.
Power Redundancy: Utilizing Uninterruptible Power Supplies (UPS) and backup diesel generators to ensure continuous operation and prevent data corruption during power outages.
Tamper-Evident Seals: Applying cryptographic and physical tamper-evident seals to critical network switches, routers, and server chassis to detect unauthorized hardware modifications.
Core Element 2: Perimeter and Network Security
Once physical security is established, the focus shifts to the network boundary—the digital frontier where internal enterprise networks interface with the outside world, most notably the internet. In the era of remote work, cloud adoption, and mobile devices, the traditional network perimeter has dissolved, but network-level controls remain vital choke points for filtering and inspecting traffic.
Next-Generation Firewalls (NGFWs) and Intrusion Systems
At the vanguard of network defense are Next-Generation Firewalls. Unlike traditional stateful firewalls that merely inspect IP addresses and port numbers, NGFWs perform deep packet inspection (DPI), analyzing the actual payloads of network traffic for malicious signatures, unauthorized protocols, and anomalous behavior.
Complementing firewalls are Intrusion Detection Systems (IDS) and Intrusion Prevention Systems (IDS/IPS). While an IDS passively monitors network traffic and alerts administrators to suspicious patterns, an IPS actively blocks traffic in real-time when it identifies known attack signatures or policy violations.
Network Segmentation and Micro-Segmentation
Flat enterprise networks—where every device can communicate with every other device once inside the network—are a security nightmare. If an attacker compromises a single endpoint, such as a marketing laptop, they gain lateral movement across the entire corporate network, eventually reaching crown-jewel databases.
To combat this, organizations must implement rigorous network segmentation. By dividing the network into distinct zones or Virtual Local Area Networks (VLANs)—separating guest Wi-Fi, IoT devices, corporate workstations, and financial databases—security teams can isolate breaches and restrict lateral movement.
Modern architectures take this a step further with micro-segmentation, leveraging software-defined networking to create granular security perimeters around individual workloads or containers. (This ensures that even if a threat actor penetrates the outer network boundary, they find themselves trapped in a tiny, heavily monitored micro-zone with nowhere to pivot.)
...Building upon the foundational principles of defense-in-depth, a truly robust cybersecurity posture requires a meticulous integration of multiple protective barriers. When one defensive layer fails or is bypassed by an adversary, the subsequent layers must trigger alarms, impede lateral movement, and mitigate potential damage.
Below is the continuation and comprehensive conclusion of our expert analysis into the essential building blocks of a modern layered security framework.
3. Application Security: Protecting the Software We Rely On
Applications are often the primary interface between an organization and its users, making them prime targets for malicious actors. Securing this layer involves addressing vulnerabilities throughout the entire software development lifecycle (SDLC).
Web Application Firewalls (WAFs): A WAF acts as a specialized shield for web-based applications, inspecting HTTP traffic and filtering out malicious requests such as SQL injection, cross-site scripting (XSS), and remote file inclusion before they reach the application backend.
Secure Coding Practices: Developers must be trained to write code that anticipates hostile inputs. Utilizing frameworks with built-in protections and conducting regular peer reviews significantly reduces the introduction of critical flaws.
Vulnerability Scanning and Penetration Testing: Automated static and dynamic application security testing (SAST/DAST) tools help identify flaws during development, while periodic manual penetration testing uncovers complex logic errors that automated tools might miss.
4. Data Security and Encryption: Safeguarding the Crown Jewels
Ultimately, data is the primary asset that cybercriminals seek to exfiltrate or ransom. Even if attackers breach perimeter and endpoint defenses, robust data security ensures that the information they access remains unintelligible or heavily restricted.
Encryption at Rest and in Transit: Utilizing advanced cryptographic standards (such as AES-256 for stored data and TLS 1.3 for data moving across networks) ensures that intercepted or stolen files cannot be read without the proper cryptographic keys.
Data Loss Prevention (DLP): DLP solutions monitor data usage across endpoints, networks, and cloud storage, blocking unauthorized transfers or accidental sharing of sensitive information like intellectual property, financial records, or personally identifiable information (PII).
Secure Backup and Recovery: An unalterable, isolated backup strategy (often referred to as the 3-2-1-1 rule: three copies of data, two different media types, one offsite copy, and one immutable copy) remains the ultimate safety net against catastrophic ransomware attacks.
5. Identity and Access Management (IAM): The New Perimeter
With the proliferation of cloud computing and remote work, the traditional network perimeter has dissolved. Identity has effectively become the new security perimeter. Managing who has access to what resources is critical.
Multi-Factor Authentication (MFA): Requiring multiple forms of verification (such as a password combined with a push notification, hardware token, or biometrics) drastically mitigates the risk of compromised credentials.
Role-Based Access Control (RBAC) and Least Privilege: Users and systems should only be granted the minimum level of access necessary to perform their specific duties, restricting lateral movement if an account is compromised.
Zero Trust Architecture: Moving away from implicit trust based on network location, a Zero Trust model continuously verifies every user and device trying to access resources, regardless of whether they are inside or outside the corporate network.
6. The Human Element: Security Awareness and Culture
Technology alone cannot prevent every breach. Employees are often targeted through social engineering techniques like phishing, pretexting, and business email compromise (BEC). Transforming the workforce from a vulnerability into an active line of defense is essential.
Continuous Security Awareness Training: Regular, engaging training sessions help employees recognize emerging threats and understand organizational security policies.
Simulated Phishing Campaigns: Periodic testing allows organizations to measure their security culture, identify departments or individuals requiring extra support, and reinforce safe habits in a controlled environment.
A Blameless Reporting Culture: Encouraging employees to report suspicious emails or accidental mistakes without fear of punitive action ensures faster incident detection and remediation.
7. Incident Response, Monitoring, and Orchestration
No security architecture is entirely impenetrable. Therefore, rapid detection and containment capabilities are just as critical as preventative controls.
Security Information and Event Management (SIEM): SIEM platforms aggregate logs and telemetry from across the entire digital ecosystem, using correlation rules and threat intelligence to surface anomalous activities in real time.
Endpoint Detection and Response (EDR) / Extended Detection and Response (XDR): These tools provide deep visibility into endpoint activity, allowing security teams to hunt for threats, isolate infected machines, and automatically terminate malicious processes.
Incident Response Planning and Tabletop Exercises: Organizations must have a documented, tested incident response plan outlining roles, communication protocols, and containment strategies to ensure a coordinated response during a crisis.
Conclusion: The Synergy of Defense-in-Depth
Layered security is not a static checklist; it is a dynamic, evolving strategy. By combining robust network controls, diligent endpoint protection, rigorous application security, unbreakable data encryption, stringent identity management, a vigilant workforce, and agile incident response, organizations create a resilient ecosystem. When one layer encounters a sophisticated threat, the remaining layers stand ready to absorb, detect, and neutralize the impact, ensuring business continuity and maintaining trust in an increasingly interconnected digital world.
What specific layer of security does your organization currently find most challenging to maintain and optimize?