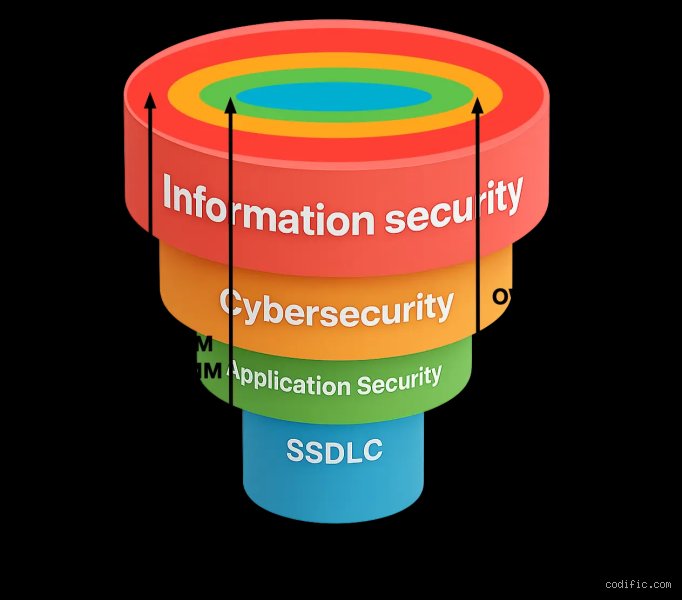
The Architecture of Resilience: Understanding the Four Layers of Cybersecurity (Part 1)
In the modern digital economy, the question for organizations is no longer if they will face a cyber attack, but when. As threat actors become increasingly sophisticated—leveraging automated tools, artificial intelligence, and targeted social engineering—traditional perimeter defenses have proven entirely insufficient. A single security control, no matter how robust, represents a single point of failure. If an attacker breaches that outer gate, the entire internal network lies exposed.
This reality has driven the adoption of Defense-in-Depth, a strategic security architecture that relies on multiple, overlapping layers of protection. By dividing security into distinct, sequential barriers, organizations ensure that even if one layer is compromised, subsequent layers contain, detect, and mitigate the threat before catastrophic damage occurs.
While comprehensive security frameworks can expand into numerous granular sub-components, they fundamentally consolidate into four critical structural layers: the Network and Perimeter Layer, the Endpoint Layer, the Application Layer, and the Data/Identity Layer. In this first part of our expert analysis, we will explore the foundational philosophy of layered security and deep-dive into the first two essential pillars defending modern digital infrastructure.
The Philosophy of Defense-in-Depth
The core principle behind layered security is borrowed from historical military architecture. Medieval castles did not rely solely on a massive outer wall; they featured moats, drawbridges, inner curtain walls, reinforced gates, and guarded keeps. If an enemy breached the outer wall, they still faced a gauntlet of obstacles, giving the defenders time to regroup, respond, and neutralize the threat.
In cybersecurity, Defense-in-Depth operates on the exact same logic. The framework relies on three core operational functions:
Prevention: Stopping threats before they breach a barrier.
Detection: Identifying unauthorized access or suspicious behavior in real time.
Mitigation and Response: Containing an active threat to minimize its "blast radius."
Compartmentalization is key. When a network or system is properly layered, a compromised user account or a malicious email attachment does not automatically translate into total system collapse. Instead, each layer acts as a tripwire and a roadblock, forcing attackers to expend resources, time, and effort—drastically increasing the likelihood that they will be detected and stopped.
Layer 1: The Network and Perimeter Layer (The Outer Gatekeeper)
The Network and Perimeter Layer serves as the initial technical boundary between an organization’s internal digital environment and the untrusted expanse of the public internet. Historically, this layer was visualized as a hard outer shell—the traditional corporate firewall keeping external threats out while keeping internal users safe.
However, with the rise of cloud computing, remote workforces, and Internet of Things (IoT) devices, the traditional corporate "perimeter" has largely dissolved. Today, the network layer must be understood not as a static wall, but as an intelligent, dynamic transit hub that controls, inspects, and filters all data moving in, out, and across internal segments.
Core Components of Network Security:
Next-Generation Firewalls (NGFWs): Unlike legacy firewalls that only inspect basic ports and IP addresses, NGFWs incorporate deep packet inspection (DPI), application awareness, and integrated intrusion prevention. They analyze the actual content of network traffic to block malicious payloads while allowing legitimate business communications.
Intrusion Detection and Prevention Systems (IDS/IPS): These systems actively monitor network traffic for anomalous patterns, known attack signatures, and unauthorized behavior. While an IDS issues alerts when suspicious activity is spotted, an IPS takes automated action—such as dropping malicious packets or resetting a connection—to block the threat instantly.
Network Segmentation and VLANs: A critical vulnerability in flat networks is lateral movement: once an attacker gains access to one low-level device, they can roam freely across the entire enterprise. Network segmentation divides the internal architecture into isolated zones (e.g., separating finance databases from guest Wi-Fi or development environments), ensuring that a breach in one area remains strictly contained.
Virtual Private Networks (VPNs) and Secure Access Service Edge (SASE): For remote workers, network security requires encrypted tunnels. Modern architectures are transitioning from traditional VPNs to advanced SASE frameworks, which combine network security functions with zero-trust network access (ZTNA) to ensure that remote connections are verified continuously.
The primary objective of the network layer is visibility and filtration. By monitoring data in transit, organizations can intercept perimeter breaches, block denial-of-service (DDoS) floods, and prevent unauthorized external entities from establishing a foothold.
Layer 2: The Endpoint Layer (Securing the Frontline Devices)
Even the most robust network perimeter cannot stop an employee from plugging in an infected USB drive, clicking a malicious link on a personal laptop at a coffee shop, or falling victim to a sophisticated spear-phishing campaign. Because users and their devices operate across various environments, Endpoint Security represents the next vital line of defense.
An "endpoint" refers to any physical or virtual device that connects to an organizational network. This includes traditional desktop computers, corporate laptops, mobile smartphones, tablets, point-of-sale (PoS) terminals, and enterprise servers. Because endpoints are where human interaction meets digital execution, they remain one of the most frequently targeted entry points for threat actors.
Advanced Technologies in Endpoint Protection:
Endpoint Detection and Response (EDR): Traditional signature-based antivirus software looks for known malware files. However, modern cyberattacks frequently use fileless malware, legitimate administrative tools (living-off-the-land techniques), and zero-day exploits that bypass traditional scans. EDR solutions continuously monitor endpoint behavior, recording process executions, memory modifications, and network connections to detect subtle indicators of compromise (IoCs) in real time.
Automated Patch Management: Software vulnerabilities are software bugs that hackers can exploit to gain control of a system. Cyber criminals constantly scan for unpatched software. Rigorous, automated patch management ensures that operating systems, browsers, and third-party applications are updated promptly as soon as security vendors release fixes.
Mobile Device Management (MDM) and Unified Endpoint Management (UEM): As mobile work models expand, organizations must secure corporate data on personal or mobile devices. MDM solutions allow IT administrators to enforce security baselines, push encrypted containers for corporate applications, and remotely wipe sensitive data if a device is lost or stolen.
Host-Based Firewalls and Application Control: Endpoints often require their own localized defenses. Host-based firewalls restrict incoming and outgoing network connections at the device level, while application whitelisting (or software restriction policies) ensures that only pre-approved, verified applications can execute on the machine, blocking unauthorized or malicious executables cold.
The endpoint layer acts as the frontline garrison of cybersecurity. Because endpoints are inherently exposed to human error and external environments, deploying rigorous behavioral monitoring, strict device policies, and automated patch management ensures that compromised devices can be isolated before they infect the wider network infrastructure.
End of Part 1. In Part 2 of this expert analysis, we will explore the remaining layers of the cybersecurity framework: the Application Layer and the Data/Identity Layer, examining how organizations secure software logic and safeguard their most valuable digital assets.
Layer 3: Application Security—Securing the Software We Rely On
With perimeter defenses and endpoints secured, attention must turn to the software applications that drive modern business operations. Applications are the primary interface through which users interact with data and systems, making them prime targets for malicious actors. Application Security (AppSec) involves embedding security protocols throughout the entire software development lifecycle (SDLC) to protect applications from external threats.
Modern applications are rarely built entirely from scratch; they frequently rely on open-source libraries, third-party APIs, and cloud services. While this accelerates development, it also expands the attack surface. A single vulnerability in a third-party dependency can compromise an entire system.
Core Components of Application Security
Secure Coding Practices: Developers must be trained to recognize and avoid common coding flaws, such as those cataloged in the OWASP Top 10 (e.g., injection flaws, broken authentication, and security misconfigurations).
Static and Dynamic Testing (SAST & DAST): Automated tools should scan source code for vulnerabilities during development (SAST) and test running applications for runtime flaws (DAST).
Web Application Firewalls (WAF): Deployed at the application edge, a WAF filters and monitors HTTP traffic between a web application and the Internet, blocking common attack vectors like SQL injection and cross-site scripting (XSS).
API Security: As microservices and APIs become the backbone of software architecture, securing endpoints against unauthorized access, parameter tampering, and rate-limiting abuse is paramount.
By addressing vulnerabilities early in the development phase—a methodology often referred to as Shift-Left Security—organizations can drastically reduce the cost and complexity of remediation while delivering more resilient software.
Layer 4: Data Security—The Ultimate Target
Ultimately, cybersecurity is not just about protecting networks, endpoints, or applications; it is about protecting data. Data is the currency of the digital age, and its unauthorized disclosure, theft, or corruption can lead to devastating financial, legal, and reputational consequences. Data Security focuses on safeguarding sensitive information wherever it resides—whether at rest, in transit, or in use.
A comprehensive data security strategy must account for the fluid nature of data. Unlike physical assets, data can be copied, transferred, and accessed globally in milliseconds. Therefore, protection mechanisms must be granular and data-centric.
Key Pillars of Data Security
Encryption: Encryption is the cornerstone of data protection. Data must be encrypted at rest (stored in databases, hard drives, or cloud buckets) using robust algorithms like AES-256, and in transit (moving across networks) using protocols such as TLS 1.3.
Data Loss Prevention (DLP): DLP software monitors and restricts data transfers, ensuring that sensitive information (such as Personally Identifiable Information, intellectual property, or financial records) does not leave the corporate network or unauthorized cloud environments.
Access Management and Principle of Least Privilege (PoLP): Users and applications should only be granted access to the specific data necessary to perform their legitimate functions. Implementing Role-Based Access Control (RBAC) and attribute-based controls prevents lateral movement during a breach.
Backup and Recovery: Even the best security defenses can fail. Immutable, regularly tested backups ensure that if data is corrupted or encrypted by ransomware, the organization can restore operations without paying extortion demands.
The Synergy of Defense-in-Depth
Examining these four layers individually reveals a critical truth: no single layer is foolproof. A clever phishing attack might bypass human awareness training; a zero-day exploit might slip past an endpoint detection agent.
This is where the concept of Defense-in-Depth becomes essential. By layering multiple defensive controls, organizations create a redundant safety net. If an attacker breaches the perimeter or evades network monitoring, they must still confront endpoint controls, application restrictions, and data encryption.
Modern frameworks like Zero Trust Architecture operationalize this philosophy by continuously verifying every user, device, and connection request, regardless of whether they originate from inside or outside the traditional corporate network. In a Zero Trust model, implicit trust is eliminated, and security checks are enforced across all four layers simultaneously.
Conclusion
Navigating today's threat landscape requires a shift away from reactive, piecemeal security measures toward a cohesive, multi-layered strategy. By harmonizing protection across the Network/Perimeter, Endpoints, Applications, and Data, organizations build a resilient architecture capable of weathering sophisticated cyber onslaughts.
As technology continues to evolve—driven by advancements in artificial intelligence, cloud computing, and IoT—the cybersecurity landscape will undoubtedly grow more complex. However, the foundational principle remains unchanged: robust security is not a single product or a static firewall, but a continuous, multi-dimensional commitment to resilience.
Key Takeaway: True security is achieved not by fortifying a single wall, but by building concentric rings of defense where every layer supports, validates, and reinforces the others.
What specific layer of your organization's cybersecurity infrastructure do you feel is currently most vulnerable, and what steps are you taking to address it?