Decoding the Privacy blueprint: What exactly is a PIA and where did it formally begin?
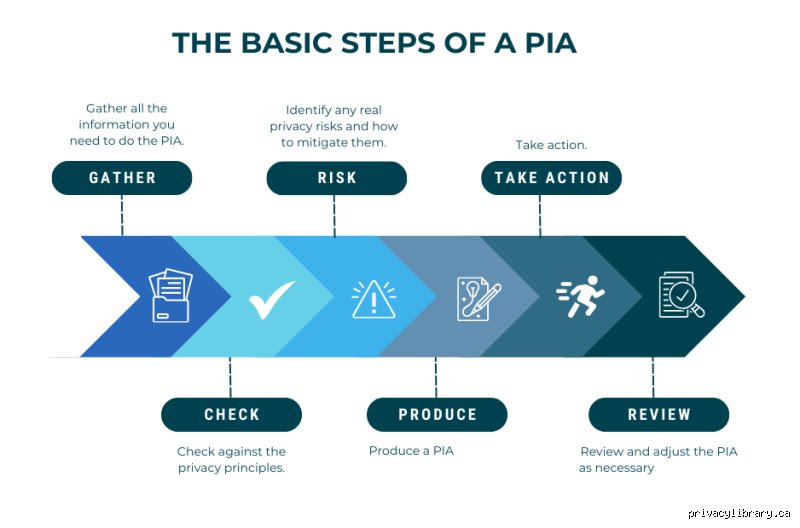
People often confuse a PIA with a standard security audit, but they are entirely different animals. A privacy impact assessment is an ongoing process designed to identify and mitigate privacy risks before a new technology, system, or policy goes live. Think of it as building a smoke detector into your data architecture rather than trying to put out a roaring fire after a massive data breach. Early privacy frameworks emerged in the 1970s, specifically with the US Privacy Act of 1974, which laid the initial groundwork for how government agencies handle personal data. Yet, the corporate world largely ignored these concepts for decades because there were no real teeth to enforcement.
The evolving definitions in modern legislation
The definition of a PIA has evolved from a vague checklist into a highly technical, legally binding roadmap. It requires organizations to map data flows, evaluate necessity, and assess risks to individual freedoms. If you are launching a mobile app that tracks user location in real-time, you cannot just say you protect data; you must document the exact mechanism of protection. There's no consensus on the absolute best methodology, but the core objective remains unyielding: ensuring accountability.
A precursor to the Data Protection Impact Assessment
The hard part is the nomenclature. In many jurisdictions, particularly within the European Union, the traditional PIA has been absorbed and codified into something more stringent known as a Data Protection Impact Assessment (DPIA). Are they identical? Not quite, but for the sake of corporate survival, treating them as close cousins is the safest bet. The historical shift happened because reactive privacy management simply failed to stop massive corporate surveillance and systemic leaks, forcing lawmakers to demand proactive compliance.
The global legal matrix: When does a PIA become a Non-Negotiable obligation?
Here is where we need to look at actual statutory laws because the global patchwork is a minefield for compliance officers. Under the European General Data Protection Regulation (GDPR) Article 35, a DPIA is legally required whenever processing is likely to result in a high risk to the rights and freedoms of natural persons. This is not a polite suggestion. If you fail to conduct one when required, the European Data Protection Board (EDPB) can hit your organization with administrative fines of up to 10 million Euros or 2% of global annual turnover, whichever is higher.
The American landscape: Federal mandates and State-Level chaos
Across the Atlantic, the United States presents a fractured reality that drives corporate lawyers insane. At the federal level, Section 208 of the E-Government Act of 2002 explicitly mandates that all federal agencies conduct a PIA before developing or procuring information technology that collects identifiable information. But what about the private sector? There is no overarching federal law for private companies, but states have rushed to fill the vacuum. The California Consumer Privacy Act (CCPA), as amended by the CPRA, alongside newer 2025 and 2026 statutes in states like Virginia and Colorado, now require formal risk assessments for businesses processing sensitive personal data or engaging in automated decision-making.
The rest of the world: From Canada to the Asia-Pacific
But wait, we are far from finished. Canada’s Personal Information Protection and Electronic Documents Act (PIPEDA) heavily rewards organizations that utilize PIAs, while its public sector counterpart, the Privacy Act, makes them mandatory for government institutions. Over in the Asia-Pacific region, Australia’s Privacy Act 1988 empowers the Privacy Commissioner to direct an entity to conduct a PIA for high-risk projects. The real issue is that borders do not matter to digital data, meaning a company based in Texas dealing with users in Munich must comply with European mandates, rendering local omissions irrelevant.
High-Risk Data scenarios where skipping a Assessment invites regulatory fury
Let us look at a concrete example to ground this theory. Imagine a healthcare tech startup based in Boston that develops an AI-driven diagnostic tool using biometric data. Because they are processing sensitive genetic indicators, they trigger mandatory assessment clauses across multiple jurisdictions simultaneously. In 2024, a major European health app was fined heavily not because they had a breach, but simply because their internal documentation could not prove they had evaluated the algorithmic bias of their platform prior to launch. Pre-emptive documentation is your only shield when the regulators come knocking on your door.
Automated processing, profiling, and AI systems
If your company uses automated processing to evaluate credit scores, insurance premiums, or housing applications, you are squarely in the crosshairs of modern privacy laws. Why? Because automated profiling can systematically disadvantage specific demographics without human oversight. Lawmakers know this, which explains why any systematic and extensive evaluation of personal aspects based on automated processing requires a mandatory assessment. You cannot hide behind proprietary algorithms anymore.
Large-Scale public monitoring and biometrics
And what about the physical world? If a retail conglomerate decides to install facial recognition cameras across 50 stores in London to track shoplifters, they are legally obligated to execute a rigorous assessment beforehand. The scale of the monitoring matters just as much as the data type. Processing biometric data for unique identification constitutes a special category under modern law, and skipping the assessment phase is a guaranteed way to secure a spot on the front page of tech news for all the wrong reasons.
Strategic alternatives and complements: Is a PIA enough to protect your organization?
It is unclear why some executives treat a PIA as a magical silver bullet that solves all compliance headaches. It is merely one component of a holistic governance framework. Relying solely on a single assessment while ignoring day-to-day data hygiene is like buying a top-tier home security system but leaving the back door wide open. You must pair these assessments with robust Data Protection Officers (DPOs) and continuous technological monitoring.
Contrasting PIAs with Privacy by Design and regular audits
A PIA is a snapshot in time, whereas Privacy by Design (PbD) is an engineering philosophy. Privacy by Design requires embedding data protection protocols directly into the source code and operational infrastructure from day one. In contrast, regular IT security audits look backward to see what went wrong, while a PIA looks forward to predict what might go wrong. They are complementary instruments, yet companies frequently misuse them as substitutes to save money on consulting fees. The upshot: they end up with fragmented compliance strategies that crumble under scrutiny.
Common pitfalls and dangerous misconceptions
The "one and done" checklist delusion
Many organizations treat a Privacy Impact Assessment as a bureaucratic checkbox to satisfy auditors before a product launch. You fill out the form, file it away in a digital drawer, and never look at it again. This is a catastrophic mistake. Data flows are dynamic, shifting constantly as software developers push weekly updates or marketing teams integrate new third-party trackers. If your processing operations change significantly, that static document becomes completely useless. The problem is that compliance is a living organism, not a mummified artifact.
Confusing a PIA with a standard risk Assessment
Executives frequently assume that their existing information security frameworks cover privacy vulnerabilities. It is a classic blunder. While a standard risk assessment focuses heavily on protecting organizational assets from external hackers, a true assessment evaluates risks directly to the individual citizens. A system can be perfectly secure from cybercriminals, yet completely violate a user's autonomy through excessive data harvesting. Confusing security with data privacy will inevitably land you in regulatory crosshairs.Relying solely on automated templates
Software vendors will eagerly promise that their expensive platforms can automate your entire compliance journey. They lie. Automated tools can certainly inventory assets, but they cannot evaluate the ethical nuances of proportionality or societal impact. Relying blindly on software algorithms to judge whether your data processing is fair creates a false sense of security.
The hidden leverage: Strategic risk reduction
Transforming liability into commercial advantage
Most corporate legal teams view compliance through a lens of fear, focusing entirely on avoiding astronomical financial penalties. Still, this defensive posture misses a massive competitive opportunity. By embedding a rigorous evaluation process into your early product design phase, you drastically reduce downstream engineering costs. Fixing a structural privacy flaw in an already deployed database architecture is a financial nightmare. Proactive data lifecycle mapping saves millions.Building radical trust with enterprise clients
In the modern business-to-business landscape, enterprise buyers are terrified of vendor risk. When you can hand a prospective corporate client a comprehensive, meticulously documented assessment, you instantly bypass months of grueling legal friction. It proves you treat data stewardship with absolute seriousness. This is why forward-thinking companies now utilize these documents as powerful sales enablement tools rather than mere regulatory shields.
Frequently asked questions
Does every single instance of data processing mean a PIA is a legal requirement?
No, the mandate is strictly tied to high-risk processing operations rather than routine data handling. Under Article 35 of the European GDPR, for example, you must conduct an assessment specifically when utilizing new technologies or performing systematic profiling. Statistics from European supervisory authorities indicate that over 70% of formal privacy investigations involve companies that failed to recognize when their processing crossed this high-risk threshold. Automated tracking in public spaces or large-scale processing of health metrics automatically triggers this statutory obligation. Therefore, routine administrative payroll activities generally escape this specific burden.What are the financial consequences if an organization ignores this obligation?
Neglecting this mandatory evaluation when high-risk factors are present invites severe regulatory wrath. Under modern frameworks, supervisory authorities possess the administrative power to levy fines reaching up to 20 million Euros or 4% of global annual turnover, whichever is higher. Regulatory compliance data from recent enforcement actions shows that supervisory bodies are increasingly using these structural omissions to calculate maximum penalties. But financial pain is only part of the story, as regulators routinely issue temporary or permanent bans on the underlying data processing itself. Such an injunction can instantly cripple a company's core product line.Who should actually write and sign off on this assessment?
The responsibility for authoring this document lies squarely with the project owner or data controller, not the Data Protection Officer. The DPO occupies an independent advisory role, meaning they must review the completed document and provide formal guidance rather than doing the heavy lifting themselves. Industry surveys reveal that 65% of successful compliance frameworks utilize cross-functional squads including engineers, product managers, and legal experts to accurately map data flows. (Admittedly, getting software developers and lawyers to speak the same language requires immense patience.) The final accountability, however, remains anchored to executive leadership.A Shift in Perspective
We must stop treating data governance as an annoying roadblock engineered by pedantic bureaucrats. The reality is that the regulatory landscape is shifting permanently toward absolute transparency, and organizations must adapt or face extinction. Is a PIA a legal requirement? Yes, whenever your operations jeopardize human dignity through unmonitored digital surveillance or aggressive algorithmic profiling. Yet, viewing this obligation through a lens of mere legal compulsion is missing the entire point. True data stewardship is no longer about doing the bare minimum to dodge a fine. As a result, organizations that embrace this rigorous evaluation process as a core philosophy will dominate the trust economy, while the corner-cutters will inevitably perish under the weight of class-action lawsuits and shattered reputations.