The universal imperative of Security
In an increasingly interconnected world, security is no longer a peripheral concern relegated to physical guards at office doors or basic passwords on personal computers. Whether we examine global financial markets, national critical infrastructure, enterprise cloud architectures, or our personal digital lives, security serves as the invisible architecture upon which modern civilization operates. Without a foundational understanding of security concepts, individuals and organizations are rendered entirely vulnerable to systemic collapse, espionage, fraud, and disruption.
To master the field of security—whether information security, cybersecurity, physical security, or operational resilience—one must first look past the complex array of tools, firewalls, encryption algorithms, and protocols. At its core, security is fundamentally about risk management, trust preservation, and resilience. It is an ongoing, dynamic discipline characterized not by a state of absolute safety, but by a continuous balance between protection, usability, and cost.
This comprehensive, multi-part expert exploration breaks down the fundamental concepts of security, tracing them from timeless philosophical axioms to cutting-edge architectural frameworks.
1. The core pillars: The classical CIA Triad
Every discussion of information and system security inevitably begins with the CIA Triad. While originally formulated to address digital data, the triad applies universally to any system designed to process, store, or transmit assets of value. The triad consists of three interdependent pillars: Confidentiality, Integrity, and Availability.
[Confidentiality]
/ \
/ \
/ \
[Integrity] --------- [Availability]
Confidentiality: Protecting Data from unauthorised Disclosure
Confidentiality ensures that sensitive information is accessed only by an authorized person, and that unauthorized individuals or systems are strictly prevented from viewing it. Achieving confidentiality requires a delicate balance of policy, cryptography, and access controls.
Encryption at Rest and in Transit: Data must be scrambled using cryptographic algorithms (such as AES-256 for data storage or TLS for data moving across networks) so that even if intercepted or stolen, the information remains unreadable ciphertext without the proper decryption keys.
Access Control Models: Systems employ frameworks like Role-Based Access Control (RBAC) or Attribute-Based Access Control (ABAC) to govern who can view specific assets.
The Principle of Least Privilege (PoLP): A cornerstone of confidentiality, PoLP dictates that users, programs, and processes should be given only the bare minimum privileges necessary to perform their specific functions, no more, no less.
Integrity: Ensuring accuracy, completeness, and Trust
Integrity addresses the trustworthiness of data and systems. It ensures that information has not been altered, tampered with, or destroyed by unauthorized entities, and that system modifications occur only in a controlled, authorized manner.
Cryptographic Hashing: Algorithms like SHA-256 take an input file or message and generate a unique fixed-size string (a hash). Even a single-bit change in the original data radically alters the resulting hash, providing a tamper-evident seal.
Digital Signatures: Utilizing asymmetric cryptography, digital signatures verify both the authenticity of the sender and the integrity of the message content.
Version Control and Audit Trails: Maintaining immutable logs and strict change management ensures that any unauthorized modification can be tracked, investigated, and rolled back.
Availability: Maintaining operational resiliency
Availability ensures that information, network resources, and critical services are accessible to authorized users whenever they are needed. A system with perfect confidentiality and integrity is completely useless if legitimate users are locked out or if the system is crippled by disruption.
Redundancy and High Availability: Critical systems eliminate single points of failure by implementing redundant hardware, load balancers, and failover clusters across geographically diverse data centers.
Denial of Service (DoS/DDoS) Mitigation: Protecting infrastructure against volumetric attacks that attempt to exhaust bandwidth, memory, or processing power.
Disaster Recovery (DR) and Business Continuity (BC): Comprehensive strategies, including frequent offline backups, cold/warm/hot sites, and tested recovery protocols to ensure rapid restoration following hardware failures, natural disasters, or ransomware attacks.
2. Extending the Triad: Authenticity, Non-Repudiation, and accountability
While the CIA Triad forms the bedrock of security architecture, modern environments require an expanded lexicon to address complex identity verification, legal liability, and tracing mechanisms.
Authenticity and Identification
Before granting access or trusting data, a system must verify the identity of an entity (whether human, device, or software).
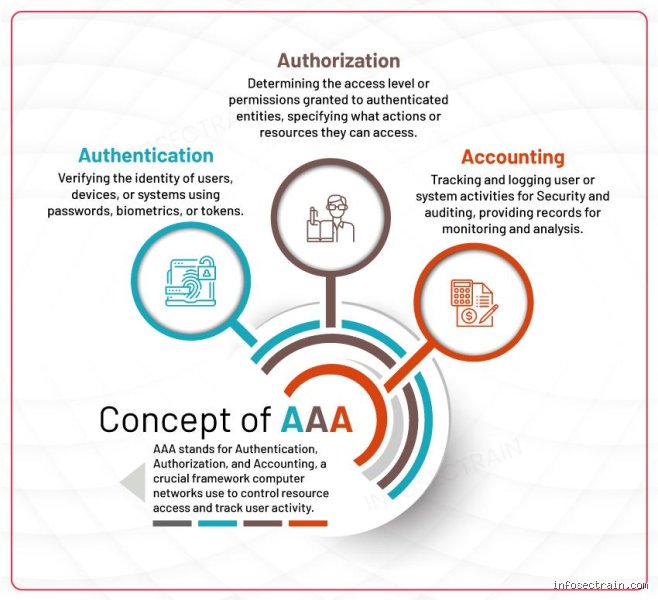
Authentication Factors: Rely on what you know (passwords, PINs), what you have (smart cards, hardware tokens, smartphone authenticators), or what you are (biometrics like fingerprints or facial recognition).
Multi-Factor Authentication (MFA): Combining two or more independent authentication factors dramatically reduces the risk of unauthorized access resulting from compromised credentials.
Non-Repudiation
Non-repudiation provides undeniable proof of an action, transaction, or communication, ensuring that neither party can successfully deny having initiated, authorized, or received it. This is typically achieved through cryptographic digital signatures and secure, unalterable auditing logs, making it essential for e-commerce, legal contracts, and forensic investigations.
Accountability
Accountability dictates that every action within a system can be traced back to a specific, identifiable entity. When security controls fail or anomalous behavior occurs, organizations must be able to answer the fundamental forensic question: Who did what, when, and from where? Accountability transforms security from a passive shield into an active deterrent.
3. Defense in Depth (DiD): The layered Security paradigm
Historically, physical and digital security relied heavily on the "Castle-and-Moat" model: build a thick perimeter wall, secure the drawbridge, and assume that everything inside is entirely safe. In the modern era of cloud computing, remote work, mobile devices, and sophisticated lateral movement by attackers, the perimeter model has completely collapsed.
Enter Defense in Depth (DiD), also known as layered security. DiD operates on the fundamental assumption that any single security control can and eventually will fail. Therefore, multiple independent layers of security are deployed sequentially so that if an attacker bypasses one defense, subsequent layers still block or detect the intrusion.
[ Outer Perimeter: Physical Security & Firewalls ]
└── [ Network Layer: Segmentation & IDS/IPS ]
└── [ Endpoint Layer: EDR & Patch Management ]
└── [ Application Layer: Input Validation & WAF ]
└── [ Data Layer: Encryption & Least Privilege ]
Physical Security: Protecting hardware, data centers, and facilities from unauthorized physical access, theft, or environmental hazards (fire, power loss).
Perimeter & Network Security: Utilizing Next-Generation Firewalls (NGFW), Virtual Private Networks (VPNs), network segmentation, and Intrusion Detection/Prevention Systems (IDS/IPS) to control traffic flow and isolate subnets.
Endpoint Security: Securing end-user devices (laptops, mobile phones, servers) using Endpoint Detection and Response (EDR) software, host-based firewalls, and rigorous patch management.
Application Security (AppSec): Ensuring software is engineered securely by performing code reviews, static/dynamic analysis (SAST/DAST), and implementing Web Application Firewalls (WAF) to block injection attacks and cross-site scripting.
Data Security: Protecting the ultimate target, the data itself, through classification, robust encryption, data loss prevention (DLP) policies, and rigorous backup regimes.
4. The Human element: Recognizing and managing the Human Attack surface
Across all security domains, technology is rarely the weakest link; human psychology remains the primary vector for exploitation. Attackers exploit cognitive biases, trust, curiosity, fear, and helpfulness through tactics collectively known as social engineering.
Phishing and Spear Phishing: Deceptive communications designed to trick individuals into revealing credentials or downloading malicious payloads.
Pretexting and Impersonation: Fabricating scenarios or posing as authority figures (IT support, executives, vendors) to manipulate targets into bypassing security protocols.
Insider Threats: Risks posed by employees, contractors, or business partners who either maliciously abuse their access or inadvertently cause breaches through negligence.
Mitigating the human risk requires moving away from treating users as liabilities and instead treating them as the "Human Firewall." This is achieved through continuous, engaging security awareness training, fostering a blameless culture of reporting, and designing user interfaces that make secure behaviors frictionless and intuitive.
Building upon the foundational pillars of information security, traditionally embodied by the Confidentiality, Integrity, and Availability (CIA) Triad, modern security engineering demands an architectural shift toward proactive resilience, contextual verification, and holistic risk management.
In this continuation of our expert analysis, we examine the advanced operational frameworks and strategic principles that translate abstract security theories into robust, enterprise-grade defenses.
1. The Principle of Least Privilege (PoLP) and Zero Trust Architecture
For decades, traditional network security relied on a "castle-and-moat" model: once a user or device authenticated at the perimeter, they were largely trusted to move laterally within the network. In an era defined by sophisticated credential theft, cloud distribution, and remote workforces, this perimeter-based trust is dangerously obsolete.
Modern security pivots entirely on two complementary paradigms:
The Principle of Least Privilege (PoLP): Every user, application, and system process must be restricted to only the minimal permissions necessary to perform its legitimate function. If a database administrator only requires read access to a specific schema during business hours, elevated write privileges or after-hours access should be programmatically denied. This drastically shrinks the blast radius if an account is compromised.
Zero Trust Architecture (ZTA): Coined by John Kindervag, Zero Trust operates on the mantra "Never trust, always verify." Under ZTA, implicit trust based on network location (such as being inside the corporate office LAN) is eliminated. Every access request, regardless of whether it originates from inside or outside the perimeter, must be continuously authenticated, authorized, and encrypted based on dynamic telemetry, including user identity, device health, behavioral anomalies, and data sensitivity.
2. Defense-in-Depth (DiD)
No single security control is infallible. A firewall can be misconfigured; an endpoint detection agent can be bypassed by zero-day malware; a user can fall victim to a targeted phishing campaign. Because absolute prevention is mathematically impossible, security architects rely on Defense-in-Depth (DiD), also known as layered security.
DiD deploys multiple independent layers of security controls distributed across different tiers of an IT environment:
Perimeter Controls: Web Application Firewalls (WAF), Distributed Denial of Service (DDoS) mitigation, and edge gateways.
Network Controls: Micro-segmentation, Virtual Private Networks (VPNs) with multi-factor authentication (MFA), and intrusion detection/prevention systems (IDS/IPS).
Host and Endpoint Controls: Endpoint Detection and Response (EDR), disk encryption, host-based firewalls, and regular patch management.
Application Controls: Secure coding practices (OWASP Top 10 mitigation), input validation, static/dynamic code analysis (SAST/DAST), and API gateways.
Data Controls: End-to-end encryption at rest and in transit, tokenization, and strict Data Loss Prevention (DLP) policies.
If an attacker breaches the perimeter, they must encounter subsequent barriers, such as network segmentation or file-level encryption, preventing lateral movement and data exfiltration.
3. Threat modeling and proactive risk assessment
Reactive security, waiting for an incident to occur before deploying a patch, is a losing battle. Organizations must anticipate adversary behaviors through systematic threat modeling.
Threat modeling is a structured engineering process for identifying security requirements, quantifying threats, and prioritizing remediation efforts during the design phase of software or infrastructure development. Common frameworks include:
STRIDE: Developed by Microsoft, STRIDE categorizes threats into Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege.
PASTA (Process for Attack Simulation and Threat Analysis): A risk-centric model that aligns technical security requirements with business objectives.
MITRE ATT&CK Matrix: A globally accessible knowledge base of adversary tactics and techniques based on real-world observations, allowing security teams to map defenses against known threat actor behaviors.
By simulating how attackers think and operate (through methodologies like penetration testing and red teaming), organizations can identify systemic weaknesses before malicious actors exploit them.
4. Incident Response, resilience, and Business Continuity
Despite rigorous prevention and detection measures, security incidents remain inevitable. The defining characteristic of a mature security posture is not whether an organization is breached, but how rapidly and effectively it detects, contains, eradicates, and recovers from the event.
An effective Incident Response (IR) lifecycle encompasses six standard phases:
Preparation: Establishing policies, communication channels, tooling (such as SIEM and SOAR platforms), and conducting tabletop exercises.
Identification: Detecting anomalies, triage alerts, and scoping the initial vector of compromise.
Containment: Isolating affected systems to prevent lateral movement without destroying volatile forensic evidence.
Eradication: Removing malware, closing vulnerabilities, and resetting compromised credentials.
Recovery: Restoring systems to normal operations from verified, immutable backups and validating integrity.
Lessons Learned: Conducting post-incident reviews to update threat models and harden defenses against recurrence.
Closely tied to IR is Business Continuity and Disaster Recovery (BCDR), which ensures that critical business functions can persist or quickly resume following catastrophic disruptions, whether caused by ransomware attacks, natural disasters, or critical infrastructure failures.
5. The Human element and Security culture
Technology and architecture alone cannot secure an organization. In many major breaches, the human vector, specifically social engineering, credential harvesting, and accidental misconfigurations, represents the path of least resistance.
Developing a resilient security culture requires moving away from treating employees as "the weakest link" and instead empowering them as the human firewall:
Continuous Awareness Training: Moving past compliance-checkbox annual videos to realistic phishing simulations, interactive workshops, and clear reporting mechanisms.
Blameless Post-Mortems: Encouraging a culture where employees feel safe reporting mistakes (such as clicking a suspicious link) immediately, minimizing dwell time for attackers.
Security-by-Design and Collaboration: Integrating security teams directly into DevOps pipelines (DevSecOps) so that security is treated as an enabler of business velocity rather than an obstructive gatekeeper.
Conclusion
The fundamental concepts of security form a continuous, dynamic loop rather than a static checklist. By anchoring operations in the principles of least privilege, layering defenses through a robust architecture, anticipating risks via threat modeling, planning for inevitable incidents, and cultivating a people-centric security culture, organizations can navigate an increasingly complex threat landscape with confidence and agility.