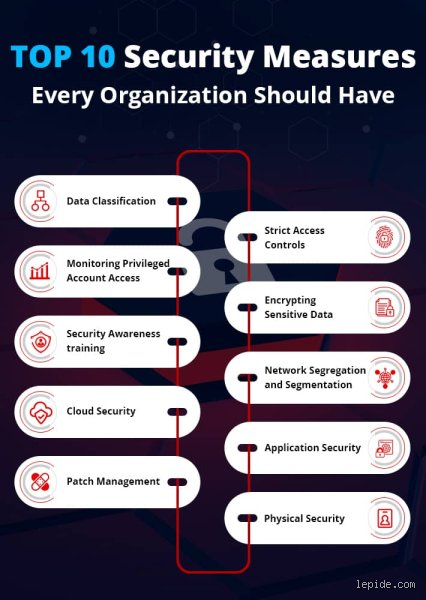
A security measure is any action, device, procedure, technique, or policy designed to protect assets—be they physical, digital, human, or intellectual, from threats such as unauthorized access, theft, damage, espionage, or disruption. However, contemporary security philosophy dictates that no single safeguard is infallible. Consequently, modern security engineering relies heavily on the principle of Defense-in-Depth (or layered security), which deploys multiple, overlapping tiers of defense so that if one layer fails, subsequent layers mitigate or prevent catastrophic failure.
This exhaustive, multi-part expert article explores the intricate taxonomy of security measures, breaking down how disparate layers integrate to form a cohesive, resilient security posture. In this first installment, we examine the foundational concepts of risk management, deep-dive into physical security architectures, and analyze the core technical and cybersecurity mechanisms that protect modern digital ecosystems.
1. The conceptual foundation: Risk, threats, and vulnerabilities
Before deploying any security measure, security architects and risk management professionals must establish a rigorous conceptual framework. Security is fundamentally an exercise in risk mitigation rather than absolute elimination, as 100% security is mathematically and economically impossible.
The security posture of any entity is governed by the traditional risk triad:
Assets: Anything of value that requires protection. This includes physical property, proprietary data, human capital, brand reputation, and operational continuity.
Threats: Any circumstance or event with the potential to adversely impact an asset through unauthorized access, destruction, disclosure, modification, or denial of service. Threats can be human (malicious hackers, disgruntled employees, physical intruders, nation-state actors), environmental (natural disasters, severe weather), or technical (hardware failure, software bugs).
Vulnerabilities: A weakness in an asset, security procedure, internal control, or implementation that can be exploited by a threat actor to gain unauthorized access or cause harm.
Security measures act as controls designed to disrupt this equation. They are typically categorized by their timing and function:
Preventative Controls: Measures designed to deter or stop a security incident before it occurs (e.g., perimeter fences, encryption, firewalls).
Detective Controls: Measures intended to identify and alert security personnel to an ongoing or completed security breach (e.g., intrusion detection systems, CCTV monitoring, audit logs).
Corrective / Responsive Controls: Measures implemented after an incident to mitigate damage, restore operations, and prevent recurrence (e.g., incident response plans, data backups, system patches).
2. Physical Security Measures: Protecting the tangible perimeter
Physical security represents the first and oldest tier of defense. It encompasses all tangible mechanisms and structural designs implemented to protect physical facilities, equipment, personnel, and sensitive materials from physical threats, including unauthorized intrusion, sabotage, theft, and natural hazards.
An effective physical security strategy utilizes a "concentric rings of defense" model, where security measures become progressively stricter the closer one moves toward the core asset.
A. Environmental Design and deterrence
Long before an intruder reaches a building's front door, physical security begins with environmental design. CPTED (Crime Prevention Through Environmental Design) is a multi-disciplinary approach to deterring criminal behavior through natural surveillance, territorial reinforcement, and access management.
Natural Surveillance: Strategic placement of windows, lighting, and clear landscaping ensures that occupants and security personnel have unobstructed views of pathways and entrances, increasing the perceived risk for intruders.
Territorial Reinforcement: Clear demarcations between public, semi-private, and private spaces (using low-profile fencing, paving changes, or signage) establish psychological ownership and make unauthorized visitors immediately apparent.
B. Perimeter Security and Access Control
The outermost boundary of a facility sets the baseline for physical defense.
Physical Barriers: High-tensile fencing, reinforced gates, bollards, and concrete retaining walls are deployed to prevent unauthorized pedestrian and vehicular access (including mitigating hostile vehicle ramming threats).
Access Control Systems (ACS): Modern physical security relies heavily on electronic access control. Rather than traditional metal keys, which are easily lost, duplicated, or stolen, facilities utilize biometric scanners (fingerprint, iris, facial recognition), smart cards, and proximity fobs. These systems log entry attempts and restrict access to authorized personnel based on clearance levels and time-of-day constraints.
Man-traps and Turnstiles: Optical turnstiles and security portals (man-traps) prevent "tailgating" or "piggybacking," where an unauthorized individual attempts to slip through a door directly behind an authorized person.
C. Surveillance, Detection, and Response
When physical barriers are breached, detection mechanisms must trigger immediate awareness.
Closed-Circuit Television (CCTV) and Video Analytics: Modern surveillance utilizes high-definition IP cameras equipped with artificial intelligence and machine learning algorithms. AI-driven video analytics can automatically detect anomalies, such as loitering, unattended bags, line-crossing, or facial matches against watchlists, reducing reliance on human operators staring at monitors.
Intrusion Detection Systems (IDS): Comprising glass-break sensors, motion detectors (infrared and microwave), magnetic door contacts, and laser tripwires, IDS alert security operations centers (SOCs) to unauthorized movement.
Security Personnel: Human guards remain indispensable. They provide dynamic deterrence, rapid physical response, professional judgment during emergencies, and customer service functions. Their effectiveness is maximized when integrated with automated monitoring dashboards.
3. Technical and cybersecurity Measures: Securing the digital frontier
As global infrastructure has migrated to the cloud, reliance on interconnected computer networks, mobile devices, and automated systems has skyrocketed. Consequently, technical security measures, collectively known as cybersecurity, have become critical for safeguarding data integrity, confidentiality, and availability (the foundational CIA Triad of information security).
A. Identity and Access Management (IAM)
In the digital realm, identity is the new perimeter. Because users can access enterprise networks from anywhere in the world, verifying who is accessing data is paramount.
Multi-Factor Authentication (MFA): Requiring two or more verification factors (something you know, something you have, and something you are) drastically reduces the risk of account compromise due to stolen passwords.
Role-Based Access Control (RBAC) and Principle of Least Privilege: Users and software processes are granted only the minimum levels of access necessary to complete their specific job functions, limiting the "blast radius" if an account is breached.
B. Network Security and perimeter defense
Just as physical facilities have walls and gates, digital networks require robust boundaries to filter malicious traffic.
Next-Generation Firewalls (NGFW) and Intrusion Prevention Systems (IPS): NGFWs inspect incoming and outgoing network traffic based on deep packet inspection, application awareness, and threat intelligence feeds, blocking malicious connections before they reach internal endpoints.
Virtual Private Networks (VPNs) and Zero Trust Architecture (ZTA): Traditional VPNs encrypted traffic across public networks, but modern enterprises are transitioning to Zero Trust ("Never trust, always verify"). Under ZTA, every user, device, and application request must be continuously authenticated and authorized, regardless of whether they are connecting from inside or outside the corporate network.
C. Data Encryption and cryptography
Data must be protected both in transit (moving across networks) and at rest (stored in databases, hard drives, or cloud storage).
Symmetric and Asymmetric Encryption: Utilizing advanced cryptographic algorithms (such as AES-256 for data at rest and TLS 1.3 for data in transit), sensitive information is scrambled into ciphertext. Even if data is intercepted or stolen by malicious actors, it remains entirely unreadable without the corresponding cryptographic decryption keys.
End of Part I. In Part II of this expert guide, we will explore Administrative and Operational Security Measures, Incident Response frameworks, and the human element of security.
Building upon foundational physical security concepts, a truly robust organizational defense requires an integrated approach that spans the digital, operational, and administrative domains. Security cannot be treated as a series of isolated silos; rather, it must function as a cohesive ecosystem where every layer reinforces the others.
3. Digital and cybersecurity Measures
As organizations digitize their operations, assets, and communications, protecting the digital perimeter has become just as critical as guarding physical doors. Digital security measures are designed to protect data, software, networks, and computer systems from unauthorized access, disruption, or theft.
Network Security Controls
Network security involves all the protocols, devices, and software deployed to secure data as it travels across internal networks and the public internet.
Firewalls and Next-Generation Firewalls (NGFWs): Firewalls act as gatekeepers between trusted internal networks and untrusted external networks (like the internet). NGFWs go beyond simple packet filtering by integrating deep packet inspection, intrusion prevention, and application-layer filtering.
Intrusion Detection and Prevention Systems (IDPS): These tools continuously monitor network traffic for suspicious activity, policy violations, or known threat signatures, automatically alerting administrators or blocking traffic in real-time.
Virtual Private Networks (VPNs) and Secure Access Service Edge (SASE): VPNs establish encrypted tunnels for remote workers, while SASE modernizes this by converging networking and security-as-a-service functions directly into the cloud edge.
Endpoint Security
Every device that connects to an organization’s network, laptops, smartphones, tablets, and Internet of Things (IoT) sensors, represents a potential entry point for attackers.
Endpoint Detection and Response (EDR): Unlike traditional antivirus software that relies on static signatures, EDR solutions monitor behavioral anomalies on endpoints, allowing security teams to hunt for advanced threats and isolate infected devices instantly.
Mobile Device Management (MDM): MDM software allows organizations to enforce security policies, wipe corporate data remotely, and ensure encryption on employee-owned or company-issued mobile devices.
Data Security and cryptography
Data is often an organization's most valuable asset. Protecting it requires stringent cryptographic controls:
Encryption at Rest and in Transit: Transforming sensitive data into unreadable ciphertext using algorithms like AES-256 ensures that even if data is intercepted or stolen, it cannot be read without the proper decryption keys.
Data Loss Prevention (DLP): DLP systems monitor data usage and movement across endpoints, networks, and cloud storage to prevent unauthorized exfiltration, sharing, or accidental leakage of sensitive information.
4. Administrative and Operational Security Measures
Technology and physical barriers alone cannot secure an enterprise; human behavior and organizational processes are equally vital. Administrative controls dictate how security policies are written, enforced, and maintained.
Identity and Access Management (IAM)
Controlling who has access to what is a cornerstone of operational security.
Principle of Least Privilege (PoLP): Users and systems are granted only the minimum levels of access necessary to complete their specific job functions, limiting the "blast radius" of a compromised account.
Multi-Factor Authentication (MFA): Requiring two or more verification factors (e.g., something you know like a password, something you have like an authenticator app, and something you are like a fingerprint) drastically reduces the risk of credential-stuffing attacks.
Role-Based Access Control (RBAC): Access rights are assigned based on organizational roles rather than individual identities, simplifying management and auditing.
Security awareness and human risk Management
Because humans are frequently targeted via social engineering and phishing, continuous training is essential.
Phishing Simulations: Regular, controlled testing helps employees recognize deceptive emails and links.
Clear Incident Reporting Channels: Creating a blame-free culture where staff feel safe reporting mistakes or suspicious anomalies ensures rapid containment of potential breaches.
Incident Response and business continuity planning
No security posture is 100% impenetrable. Operational readiness requires robust preparation for when things go wrong.
Incident Response Playbooks: Pre-defined workflows that outline roles, responsibilities, and technical steps to contain, eradicate, and recover from a security incident.
Disaster Recovery and Backup Strategies: Implementing the "3-2-1 backup rule" (three copies of data, on two different media types, with one copy stored offsite) ensures resilience against ransomware attacks or catastrophic physical disasters.
5. Emerging paradigms: The shift to Zero Trust
Traditional security models operated on a "trust, but verify" philosophy, often assuming that anything inside the corporate network perimeter was safe. Modern security has largely abandoned this approach in favor of Zero Trust Architecture (ZTA).
Grounded in the principle of "never trust, always verify," Zero Trust assumes breach and mandates continuous, explicit verification of every user, device, and application request, regardless of whether the request originates from inside or outside the traditional network boundary. By combining micro-segmentation, continuous risk scoring, and strict device posture checks, organizations can limit lateral movement by attackers and protect critical assets more dynamically.
Conclusion
Securing an enterprise in the modern era requires a holistic, defense-in-depth strategy that harmonizes physical, digital, administrative, and operational measures. No single control is foolproof; rather, it is the overlapping web of barriers, from reinforced entry doors and biometric readers to zero-trust network policies and employee training, that creates true resilience. As threats continue to evolve, security must remain an agile, continuous process of assessment, adaptation, and integration.