The modern Digital battlefield
In this climate, information security (often abbreviated as InfoSec) is no longer merely an IT compliance checkbox or a reactive departmental silo; it is the fundamental bedrock of modern organizational survival and societal stability. Yet, building an impenetrable digital fortress is an illusion. Advanced persistent threats (APTs), zero-day exploits, sophisticated social engineering, and insider threats mean that absolute security is mathematically and practically impossible.
Instead, modern information security is built upon a philosophy of risk management, resilience, and systematic governance. At the heart of this discipline lie timeless, universally accepted foundational principles that guide security architects, policy makers, and engineers in designing systems capable of withstanding the most determined adversaries.
The paradigm shift: From Perimeter Defense to Principle-Driven resilience
Historically, early computing security mirrored medieval castle architecture: a hard, defensive outer perimeter protecting a soft, trusting interior. This "castle-and-moat" approach relied heavily on firewalls, virtual private networks (VPNs), and physical server room guards to keep malicious actors out. Once an entity authenticated past the perimeter, they were largely trusted implicitly.
The modern reality has shattered this paradigm. With the advent of cloud computing, Internet of Things (IoT) devices, mobile endpoints, and borderless remote work, the traditional perimeter has dissolved. Today’s threat actors routinely breach outer defenses through compromised credentials, phishing, or vulnerable supply chains, operating laterally within internal networks undetected for months.
Consequently, the information security community underwent a seismic philosophical shift toward Zero Trust architecture and principle-driven defense. Rather than assuming safety within a perimeter, security practitioners now design systems based on the premise that breach is inevitable. Security must be baked into every layer of the data lifecycle—from creation and transmission to storage and ultimate destruction. To achieve this, security professionals anchor their strategies in formalized frameworks, starting with the most enduring model in the history of cybersecurity: The CIA Triad.
The foundational bedrock: The CIA Triad
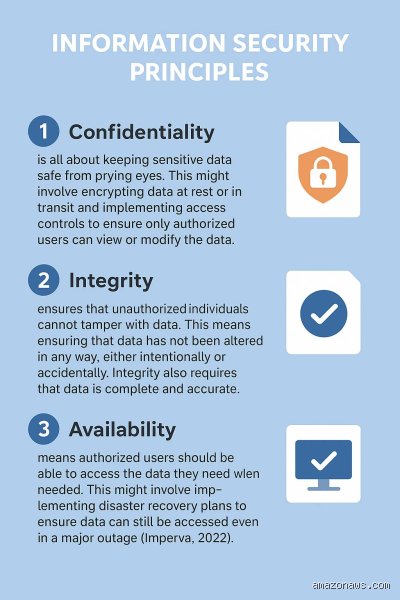
Every security policy, encryption algorithm, access control mechanism, and disaster recovery plan traces its lineage back to three core tenets known collectively as the CIA Triad: Confidentiality, Integrity, and Availability. These three pillars form an interdependent equilibrium; compromising any single leg destabilizes the entire security posture of an organization.
[ CONFIDENTIALITY ]
/ \
/ Info \
/ Security \
/ \
[ INTEGRITY ] --------------- [ AVAILABILITY ]
1. Confidentiality: Guarding the secret
Confidentiality is the principle that sensitive information must be accessed only by authorized individuals, entities, or systems, and strictly denied to all others. It is the digital equivalent of a locked safe or a classified clearance level. When confidentiality fails, the result is a data breach, leading to intellectual property theft, regulatory fines, reputational ruin, and the exposure of personally identifiable information (PII).
Achieving robust confidentiality requires a multi-layered defensive strategy:
Encryption at Rest and in Transit: Data must be scrambled using advanced cryptographic algorithms (such as AES-256 for storage and TLS 1.3 for network transmissions) so that even if intercepted or stolen, the raw data remains incomprehensible ciphertext without the corresponding decryption keys.
Access Control Models: Organizations implement strict access frameworks based on the Principle of Least Privilege (PoLP)—ensuring that users and system processes are given only the bare minimum permissions necessary to perform their specific functions, and nothing more. This is frequently reinforced through Role-Based Access Control (RBAC) and Attribute-Based Access Control (ABAC).
Multi-Factor Authentication (MFA): Passwords alone are notoriously weak defenses against modern credential-stuffing attacks and phishing. MFA introduces additional verification factors, something you know (password), something you have (hardware token or authenticator app), and something you are (biometrics), drastically reducing unauthorized entry.
Data Masking and Tokenization: For highly sensitive databases containing credit card numbers or medical records, masking and tokenization obscure real data values with non-sensitive placeholders during processing and display, minimizing exposure risks.
The challenge of confidentiality lies in striking the delicate balance between security and usability. If security controls are excessively burdensome, such as requiring twelve distinct layers of authentication for low-risk internal data, users will inevitably invent workaround shadow IT practices, inadvertently destroying confidentiality altogether.
2. Integrity: The sanctity of truth
While confidentiality protects secrets, integrity protects truth. Integrity ensures that data and systems remain accurate, complete, and trustworthy throughout their entire lifecycle. It guards against unauthorized creation, alteration, deletion, or corruption of data, whether caused by a malicious hacker altering financial transaction logs, a disgruntled employee sabotaging a database, or a cosmic bit-flip corrupting a hard drive sector.
A system with high confidentiality and availability is useless, and actively dangerous, if its underlying data lacks integrity. Imagine a hospital database where a malicious actor subtly alters a patient's medication dosage, or a financial institution where account balances are silently shifted.
To preserve data integrity, security engineers employ several technical mechanisms:
Cryptographic Hashing: Algorithms like SHA-256 generate a unique mathematical fingerprint (checksum) for a file or data block. If even a single bit of the data is modified, the resulting hash changes drastically, immediately alerting the system to tampering.
Digital Signatures: Combining asymmetric cryptography with hashing, digital signatures verify both the authenticity and the integrity of a message or software update, ensuring it originated from a trusted source and was not altered in transit.
Version Control and Audit Logging: Immutable audit logs and versioning systems maintain a cryptographically verifiable history of who changed what, when, and why. This ensures non-repudiation, preventing users from falsely denying actions they performed within a system.
Input Validation and Sanitization: At the application layer, robust integrity controls ensure that user-supplied input is rigorously filtered and validated to prevent injection attacks (such as SQL injection or Cross-Site Scripting) that attempt to corrupt backend database structures.
3. Availability: Operational resilience
The final pillar of the CIA Triad is availability, which ensures that information, network resources, and critical services are accessible to authorized users whenever they are needed. An organization can have military-grade encryption (confidentiality) and immaculate data accuracy (integrity), but if its systems are offline, the business grinds to a halt.
In the modern threat landscape, availability is frequently targeted by Distributed Denial of Service (DDoS) attacks, ransomware campaigns that lock up operational infrastructure, and sophisticated sabotage. Natural disasters, hardware failures, and human error (such as a misconfigured cloud storage bucket or an accidental database deletion) pose massive threats to uptime.
Ensuring high availability requires engineering for resilience and redundancy across every tier of an IT infrastructure:
Redundancy and Failover Systems: Eliminating single points of failure by duplicating critical components, such as power supplies, network connections, and database servers, ensures that if one component fails, a secondary failover system assumes the workload instantly with zero downtime.
Geographic Load Balancing: Spreading workloads across multiple cloud regions and data centers ensures that a regional outage or cyberattack on one facility does not take down global operations.
Disaster Recovery (DR) and Business Continuity (BC) Planning: Comprehensive DR strategies involve maintaining rigorous, tested backups (adhering to the golden 3-2-1 backup rule: three copies of data, across two different media types, with one copy stored offsite/offline in an immutable state to withstand ransomware).
Capacity Planning and DDoS Mitigation: Deploying intelligent edge-filtering services (such as Cloudflare or AWS Shield) to absorb and deflect volumetric DDoS attacks before they overwhelm origin servers.
Conclusion of Part I
As we have established, the foundational pillars of Confidentiality, Integrity, and Availability form the irreducible trinity of information security. However, understanding these concepts in theory is vastly different from operationalizing them within a complex enterprise.
In Part II of this expert series, we will expand beyond the CIA Triad to explore advanced auxiliary principles that govern modern security engineering, including the Principle of Least Privilege in depth, Defense in Depth architectures, non-repudiation, separation of duties, and how zero-trust frameworks are redefining the future of digital defense.
Building upon the foundational pillars of confidentiality, integrity, and availability (the classic CIA triad), modern information security requires a robust suite of operational, architectural, and cultural principles. As cyber threats evolve in sophistication, organizations can no longer rely solely on perimeter defenses. The continuation and conclusion of this expert analysis explore the advanced principles that form the backbone of resilient cybersecurity frameworks today.
4. The Principle of Least Privilege (PoLP) and identity governance
One of the most effective defensive measures an organization can implement is the Principle of Least Privilege (PoLP). PoLP dictates that every user, process, system, and application must be given only the bare minimum permissions necessary to perform its legitimate functions, and nothing more.
Implementation and operational impact
Privileged Access Management (PAM): Organizations must rigorously control administrative accounts. Permanent super-admin accounts are prime targets for attackers; instead, organizations utilize Just-In-Time (JIT) access and elevation privileges that expire automatically after a set task window.
Granular Role-Based Access Control (RBAC): Access rights should be tied directly to job functions. When an employee changes roles or leaves the organization, their access must be systematically revoked or adjusted in alignment with their new responsibilities.
Mitigating Blast Radius: If a standard user's credentials are compromised via phishing, the attacker's lateral movement is severely restricted if that user only has access to localized files rather than enterprise-wide infrastructure.
5. Defense in Depth: Layered Security architecture
Security through obscurity or relying on a single defensive barrier is a recipe for failure. Defense in depth, also known as layered security, applies multiple independent security controls across an IT environment so that if one layer fails, subsequent layers catch or mitigate the threat.
+-------------------------------------------------------------+
| Perimeter / Edge Firewall |
| +-----------------------------------------------------+ |
| | Network Segmentation | |
| | +---------------------------------------------+ | |
| | | Host & Endpoint Security | | |
| | | +-------------------------------------+ | | |
| | | | Application Security | | | |
| | | | +-----------------------------+ | | | |
| | | | | Data Encryption & IAM | | | | |
| | | | +-----------------------------+ | | | |
| | | +-------------------------------------+ | | |
| | +---------------------------------------------+ | |
| +-----------------------------------------------------+ |
+-------------------------------------------------------------+
Key layers of Defense
Perimeter Defense: Firewalls, Intrusion Detection Systems (IDS), and Web Application Firewalls (WAF) filtering incoming and outgoing traffic.
Network Segmentation: Dividing corporate networks into secure zones (e.g., separating guest Wi-Fi from financial databases) to prevent lateral movement during a breach.
Endpoint Protection: Deploying Endpoint Detection and Response (EDR) solutions on laptops, servers, and mobile devices to monitor anomalous behavior.
Application Security: Conducting regular code reviews, static and dynamic application security testing (SAST/DAST), and dependency scanning.
Data Security: Encrypting data both at rest and in transit, paired with robust backup strategies.
6. Zero Trust architecture: "Never Trust, always Verify"
Traditional security models operated on an "implicit trust" assumption, once a user or device authenticated inside the network perimeter, they were generally trusted. In the era of remote work, cloud computing, and sophisticated insider threats, this perimeter-based model is obsolete.
Zero Trust is an architectural framework that eliminates implicit trust based on physical or network location.
Core tenants of Zero Trust
Verify Explicitly: Always authenticate and authorize based on all available data points, including user identity, location, device health, service or workload, data classification, and anomalies.
Use Least Privilege Access: Limit user access with Just-In-Time and Just-Enough-Access (JIT/JEA), risk-based adaptive policies, and data protection.
Assume Breach: Minimize blast radius by segmenting access by network, user, devices, and application awareness. Encrypt all sessions end-to-end and utilize analytics to gain visibility, drive threat detection, and continuously improve defenses.
7. Accountability, auditing, and Non-Repudiation
Security controls lose their efficacy if administrators cannot trace actions back to their origin. Accountability ensures that every action taken within a system can be attributed unequivocally to an entity.
Comprehensive Logging: Centralized Security Information and Event Management (SIEM) systems aggregate logs from servers, firewalls, and applications. These logs must be tamper-proof and regularly analyzed.
Non-Repudiation: Through cryptographic mechanisms like digital signatures and secure audit trails, non-repudiation ensures that a user or system cannot deny having performed a specific action, such as authorizing a financial transaction or modifying a critical configuration file.
8. Resilience and Incident Response readiness
No security posture is 100% impenetrable. True maturity in information security is measured not just by prevention, but by resilience, the ability to withstand, adapt to, and rapidly recover from security incidents.
Incident Response Plan (IRP): Organizations must have a thoroughly documented, tested, and rehearsed IRP outlining roles, communication channels, and containment procedures during an active breach.
Business Continuity and Disaster Recovery (BCDR): Regular, immutable backups stored off-site or in isolated cloud environments ensure that even in the catastrophic event of a ransomware attack, operations can be restored without capitulating to extortion demands.
9. The human element: Cultivating a Security-First Culture
Technology and architecture are critical, but human error remains one of the largest vectors for security breaches. Phishing, social engineering, and accidental misconfigurations continue to compromise organizations daily.
Continuous Security Awareness Training: Training must go beyond compliance check-boxes; it should involve realistic simulation exercises, engaging workshops, and clear guidance on emerging threat tactics.
Blameless Security Culture: Employees must feel empowered to report suspected security incidents, phishing attempts, or accidental mistakes immediately without fear of punitive retaliation. Rapid reporting drastically reduces dwell time for attackers.
Conclusion
Information security is not a static product that can be purchased off the shelf, nor is it a checklist to be completed once a year. It is a dynamic, continuous discipline that weaves together advanced cryptographic technology, rigorous architectural principles like Least Privilege and Zero Trust, and an empathetic, security-conscious organizational culture. By embracing these key principles holistically, modern organizations can navigate an increasingly hostile threat landscape with confidence, safeguarding their digital assets, maintaining customer trust, and ensuring uninterrupted operational continuity.