This reality makes Information Security (InfoSec) not just an IT department concern, but a foundational pillar of modern civilization, business continuity, and individual privacy. Whether you are a software engineer, a business leader, or a student navigating the digital world, understanding the core principles of information security is no longer optional—it is a critical life skill.
This comprehensive# Demystifying Information Security: The Foundations of the Digital Age (Part 1)
In the twenty-first century, data has surpassed traditional commodities to become the most valuable currency on Earth. From the personal photographs and private messages stored on our smartphones to the proprietary algorithms, financial ledgers, and operational controls of global enterprises, nearly every facet of modern life is digitized. However, this hyper-connected ecosystem introduces unprecedented vulnerabilities. As society becomes increasingly reliant on digital infrastructure, the discipline of information security (InfoSec) transitions from a technical sub-specialty into an essential life skill and a foundational pillar of organizational survival.
This comprehensive guide serves as the first part of an expert exploration into the core principles of information security. Whether you are an aspiring technology professional, a business leader looking to safeguard your enterprise, or an individual seeking to fortify your digital footprint, understanding the bedrock concepts of InfoSec is the first and most critical step toward digital resilience.
1. The core pillar: The CIA Triad
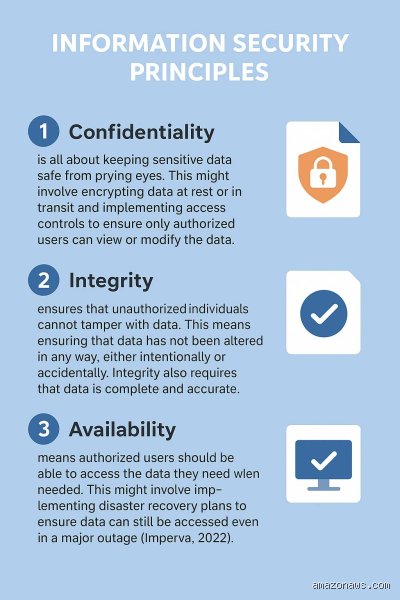
At the very heart of information security lies a foundational framework known as the CIA Triad. While it shares an acronym with a famous intelligence agency, in the context of cybersecurity, CIA stands for Confidentiality, Integrity, and Availability. This triumvirate forms the evaluation standard for every security policy, tool, and architecture deployed in the modern digital landscape. If a security measure fails to protect one or more of these three elements, the system is fundamentally compromised.
Confidentiality
Confidentiality refers to the principle of restricting access to information only to authorized individuals, entities, or processes, while preventing unauthorized access or disclosure. In simpler terms, it ensures that secrets remain secret.
Achieving confidentiality requires a multi-layered approach. At the most fundamental level, this involves Access Control—ensuring that users are authenticated (proving who they are) and authorized (having permission to access specific resources). Techniques such as the Principle of Least Privilege dictate that users and systems should only be granted the bare minimum access necessary to perform their legitimate functions.
Beyond access controls, confidentiality relies heavily on Encryption. Cryptography transforms readable plaintext into unreadable ciphertext using complex mathematical algorithms and cryptographic keys. Encryption is generally categorized into two states:
Data in Transit: Information moving across a network (e.g., browsing a secure website via HTTPS or sending an encrypted email). Protocols like TLS (Transport Layer Security) ensure that even if data is intercepted en route, it cannot be read without the decryption key.
Data at Rest: Information stored on physical or cloud media (e.g., files on a hard drive, databases on a server). Full-disk encryption and database-level encryption ensure that physical theft of a device does not automatically result in data exposure.
Integrity
While confidentiality focuses on keeping data secret, integrity focuses on keeping data trustworthy. Integrity ensures that information, systems, and software are accurate, complete, and protected from unauthorized modification, deletion, or fabrication.
Imagine a scenario where a malicious actor intercepts a financial transaction and changes the recipient's bank account number, or subtly alters the dosage instructions in a digital medical record. The data remains accessible (satisfying confidentiality), but it is no longer true or safe to use.
To maintain integrity, security systems utilize mechanisms such as:
Hashing: Mathematical algorithms (like SHA-256) that take an input file or message and generate a unique, fixed-size string of characters. Even a single-bit change in the original data will result in a completely different hash value, making tampering instantly detectable.
Digital Signatures: Cryptographic mechanisms that verify the authenticity and integrity of a digital message or document, proving both who sent it and that it hasn't been altered in transit.
Version Control and Audit Logs: Tracking systems that maintain a historical record of who made changes to a system or document and when those changes occurred.
Availability
The final leg of the CIA triad, availability, ensures that information, network resources, and critical services are accessible to authorized users whenever they are needed. A security system that is impenetrably confidential and flawlessly accurate is entirely useless if legitimate users cannot access the resources required to perform their daily operations.
Availability threats often manifest as Denial of Service (DoS) or Distributed Denial of Service (DDoS) attacks, where malicious actors flood a target server with overwhelming traffic, crashing the system or rendering it unresponsive. Other availability threats include hardware failures, natural disasters, software bugs, and accidental human errors (such as pulling the wrong power cable in a data center).
To guarantee high availability, organizations implement:
Redundancy: Duplicating critical components (such as power supplies, network connections, and data storage drives) so that if one fails, a backup takes over seamlessly.
Failover Systems: Automated mechanisms that switch operations to a redundant secondary system upon the failure or abnormal termination of the primary application or server.
Disaster Recovery and Business Continuity Plans (DR/BCP): Comprehensive strategies and backup schedules designed to restore operations rapidly in the event of a catastrophic disruption.
2. Understanding the Threat landscape
To build effective defenses, security professionals must understand who they are defending against, what motivates these actors, and how they operate. The modern cyber threat landscape is diverse, dynamic, and increasingly professionalized.
Motivations and Threat actors
Threat actors, often colloquially referred to as "hackers", range from lone individuals operating out of curiosity to highly organized, well-funded nation-state syndicates. Their motivations generally fall into several distinct categories:
Financial Gain: By far the most common motivation. Cybercriminals deploy ransomware to lock organizational data until a cryptocurrency ransom is paid, commit identity theft, steal intellectual property to sell on dark web marketplaces, or engage in corporate espionage.
Espionage and Intelligence Gathering: Nation-states engage in cyber espionage to steal classified government data, monitor geopolitical rivals, or compromise critical national infrastructure (such as power grids and water treatment plants).
Ideology and Activism ("Hacktivism"): Groups or individuals who hack organizations to promote a political agenda, protest perceived injustices, or disrupt operations of entities they oppose.
Thrill and Status ("Script Kiddies"): Inexperienced individuals who use pre-existing software tools or scripts written by others to break into systems, primarily for personal amusement or to gain notoriety within online communities.
3. Common attack vectors and vulnerabilities
A vulnerability is a weakness or flaw in a system, software, hardware, or procedural design that can be exploited by a threat actor. An attack vector is the path or method used by an attacker to gain access to a target system.
Social engineering and the human factor
Despite the sophisticated tools used in modern cybersecurity, the most vulnerable component of any security architecture is almost always human. Social engineering relies on psychological manipulation to trick individuals into voluntarily handing over confidential information, granting system access, or executing malicious files.
The most prevalent form of social engineering is phishing. Phishing attacks typically involve deceptive emails, text messages (smishing), or voice calls (vishing) designed to impersonate a trusted entity, such as a bank, a coworker, or an IT help desk. When the victim clicks a malicious link or opens an infected attachment, malware is deployed, or credentials are harvested. More targeted variants, such as spear phishing and whaling, focus on specific high-profile individuals within an organization, utilizing customized research to make the deception nearly indistinguishable from reality.
Malware (Malicious Software)
Malware is an umbrella term for any software intentionally designed to cause damage to a computer, server, client, or computer network. Common classifications include:
Ransomware: Encrypts a victim's files and demands a ransom payment for the decryption key. Modern ransomware operations often employ "double extortion," threatening to leak sensitive stolen data publicly if the ransom is not paid.
Spyware: Secretly monitors user activity, capturing keystrokes (keyloggers), browsing habits, and credentials without the user's consent.
Trojans: Disguise themselves as legitimate, desirable software to trick users into installing them, subsequently opening a "backdoor" for attackers to control the system remotely.
Worms: Standalone malware programs that replicate themselves to spread from computer to computer across a network without requiring human interaction.
4. The human element as the first line of defense
Because technical controls alone cannot prevent every breach, fostering a strong security culture is paramount. Security awareness training must move away from tedious annual compliance checkboxes and focus on practical, engaging education that empowers individuals to recognize suspicious behavior, practice good password hygiene, and utilize Multi-Factor Authentication (MFA) across all personal and professional accounts. MFA adds a critical layer of defense by requiring users to provide two or more verification factors to gain access (e.g., something you know like a password, plus something you have like a smartphone authentication app).
In Part 2 of this series, we will dive deeper into advanced security architectures, the mechanics of cryptography, endpoint protection, incident response frameworks, and the rising role of artificial intelligence in both defending and attacking modern networks.
...Building directly upon the foundational principles of the CIA Triad (Confidentiality, Integrity, and Availability) and fundamental authentication mechanisms, a robust information security strategy requires translating these concepts into active technical controls, structural frameworks, and organizational habits.
3. Access Control models and the Principle of Least Privilege
Securing digital assets is fundamentally about controlling who, or what, has access to specific resources. Without structured access controls, even the strongest encryption can be bypassed if an attacker compromises a single over-privileged user account.
The Principle of Least Privilege (PoLP)
At the heart of modern access control is PoLP: the practice of providing users, processes, and systems with only the absolute minimum levels of access (or privileges) necessary to complete their specific tasks.
Why it matters: If an attacker compromises an account with standard, restricted permissions, the "blast radius" is limited. If that same account has administrator-level access across the entire network, the potential damage is catastrophic.
Implementation: Organizations routinely audit user permissions, strip away unused administrative rights, and enforce time-bound access elevations for maintenance tasks.
Core Access Control frameworks
To enforce these boundaries, security architects rely on standardized models:
| Model | Acronym | Description | Primary Use Case |
|---|---|---|---|
| Discretionary Access Control | DAC | The owner of a resource decides who has access to it. | Operating system file permissions. |
| Mandatory Access Control | MAC | Access is strictly regulated by a central authority based on multi-level security classifications and clearance labels. | Government, military, and high-security defense environments. |
| Role-Based Access Control | RBAC | Permissions are assigned to specific organizational roles (e.g., "Accountant," "System Admin"), and users are placed into those roles. | Enterprise software, corporate IT infrastructure. |
| Attribute-Based Access Control | ABAC | Access is granted dynamically based on a combination of attributes (user identity, location, device health, time of day, and resource sensitivity). | Modern cloud environments, zero-trust architectures. |
4. Cryptography: Protecting data at Rest and in Transit
Cryptography is the mathematical science of securing information by transforming it into an unreadable format (ciphertext) that can only be decrypted by authorized parties with the correct key.
Data states and Encryption strategies
Information security professionals categorize data into three primary states, each requiring distinct cryptographic safeguards:
Data in Transit: Information moving across a network (e.g., browsing a website or sending an email). This is protected using protocols like TLS (Transport Layer Security) and IPsec.
Data at Rest: Information stored on physical or cloud media (e.g., databases, hard drives, backups). This is protected via full-disk encryption (FDE) and database-level encryption.
Data in Use: Information currently being processed in active memory (RAM). Emerging technologies like homomorphic encryption allow computation on encrypted data without decrypting it first.
Symmetric vs. Asymmetric Encryption
Symmetric Encryption: Uses the same secret key for both encryption and decryption. It is computationally fast and ideal for bulk data encryption (e.g., AES-256). The primary challenge is securely sharing the key between parties.
Asymmetric Encryption (Public-Key Cryptography): Uses a mathematically linked key pair, a public key to encrypt data and a private key to decrypt it. Because anyone can use the public key to send a secure message, but only the holder of the private key can read it, this solves the key distribution problem. Protocols like RSA and Elliptic Curve Cryptography (ECC) form the bedrock of secure internet communications.
5. Threat modeling and risk management
Security is not about achieving absolute protection, which is mathematically and economically impossible, but about managing risk to an acceptable level. Organizations use risk management frameworks to identify, evaluate, and mitigate potential threats.
The Risk Equation
Risk=Threat×Vulnerability×Impact ext{Risk} = ext{Threat} imes ext{Vulnerability} imes ext{Impact}Risk=Threat×Vulnerability×Impact
Threat: Any circumstance or event with the potential to adversely impact an asset (e.g., ransomware group, insider threat, hardware failure).
Vulnerability: A flaw or weakness in a system, security procedure, internal control, or implementation that can be exploited by a threat.
Impact: The resulting damage or financial/operational loss if a threat successfully exploits a vulnerability.
Mitigation Strategies
Once risks are identified and prioritized, organizations choose how to handle them through four classic responses:
Mitigate (Remediate): Apply patches, strengthen controls, or reconfigure systems to reduce the likelihood or impact.
Transfer: Shift the financial risk to a third party, such as through cyber insurance or outsourcing to a secure cloud provider.
Accept: Acknowledge the risk because the cost of remediation outweighs the potential loss (common for low-impact, low-probability events).
Avoid: Eliminate the activity or asset entirely to remove the risk vector.
6. Incident Response and the Security Lifecycle
Even with world-class preventative controls, security breaches will happen. An organization's maturity is defined less by its ability to prevent every attack and more by its ability to detect, contain, and recover from incidents swiftly.
The National Institute of Standards and Technology (NIST) outlines the core phases of an Incident Response Lifecycle:
Preparation: Establishing policies, training staff, deploying monitoring tools, and conducting tabletop exercises before an incident occurs.
Detection and Analysis: Identifying anomalies, reviewing security alerts, and determining whether an incident has occurred and what its scope is.
Containment, Eradication, and Recovery: Isolating affected systems to prevent lateral movement (containment), removing malware or closing compromised entry points (eradication), and restoring systems safely back to production (recovery).
Post-Incident Activity ("Lessons Learned"): Conducting a blameless post-mortem analysis to understand root causes, update defenses, and improve future response readiness.
7. The human factor: Building a Security Culture
Technology and policies alone cannot secure an organization. The human element remains both the most vulnerable link and the most powerful defensive asset.
Social engineering attacks, such as phishing, spear-phishing, vishing, and pretexting, bypass technical controls by manipulating human psychology (fear, urgency, helpfulness, or curiosity) into handing over credentials or executing malicious payloads.
Addressing this requires shifting security from a technical hurdle to an organizational culture:
Continuous Awareness Training: Moving away from once-a-year compliance checkboxes to engaging, real-world simulations and bite-sized training modules.
Just Culture: Encouraging employees to report mistakes (such as clicking a phishing link) immediately without fear of unfair punishment, ensuring rapid containment of potential breaches.
Conclusion
Information security is not a static product you purchase or a single policy document you file away; it is a dynamic, continuous process of adaptation. As technology evolves, from cloud computing and mobile architectures to artificial intelligence and quantum cryptography, the threat landscape shifts in tandem.
By mastering the foundational pillars of confidentiality, integrity, availability, strict access controls, robust encryption, proactive risk management, and a security-first human culture, individuals and organizations can build resilient defenses capable of navigating an increasingly complex digital world.