The High-Stakes collision of Privacy and Law Enforcement
To understand the answer, one must venture past political rhetoric and examine the complex intersection of cryptography, software architecture, and legal compliance. The short answer is both nuanced and absolute: While the government can compel Apple to hand over certain types of metadata and unencrypted backups, end-to-end encryption architectural constraints structurally prevent Apple from handing down the actual text and contents of modern iMessages.
However, looking at the absolute state of "yes" or "no" oversimplifies an ecosystem shaped by user choices, cloud configurations, and hardware-level security. This first part of our comprehensive exploration breaks down the fundamental cryptographic mechanics of iMessage, the role of iCloud backups, and the structural limitations governing what information ultimately reaches state hands.
The cryptographic shield: Understanding End-to-End Encryption
To evaluate government access, one must first master how iMessage secures data during transit. Unlike traditional SMS text messages, which travel across carrier networks in plain text, readily interceptable by telecommunication providers or wiretaps, iMessage was architected with End-to-End Encryption (E2EE).
When a user sends an iMessage from an iPhone, iPad, or Mac, the message text, photos, and attachments are encrypted on the sending device using unique cryptographic keys. Once locked behind this digital barrier, the data can only be decrypted by the intended recipient’s trusted device, which holds the corresponding private key.
No Master Keys or Backdoors: Apple has repeatedly maintained, and independent security audits have largely corroborated, that it has never built a master key, universal backdoor, or hidden trapdoor into iMessage.
In-Transit Protection: Because the encryption keys reside strictly on the user-controlled hardware endpoints rather than on central corporate servers, Apple’s engineering teams lack the technical capability to decrypt the content of a live iMessage stream, even if legally compelled via a court order to do so.
From a purely architectural standpoint, if law enforcement intercepts data packets passing through Apple's push notification or message routing servers, they encounter an indecipherable stream of ciphertext. Apple cannot decrypt what it cannot mathematically open.
The icloud vulnerability: Standard versus Advanced Data Protection
While live transit encryption presents a brick wall to investigators, communication ecosystems rely heavily on cloud infrastructure for synchronization and disaster recovery. This is where the security paradigm shifts dramatically, contingent entirely on user settings and account configurations.
Standard Data Protection (the default state)
For years, the default configuration for most Apple users has been Standard Data Protection. Under this framework, user data in iCloud, including device backups, photos, notes, and crucially, iCloud backups containing message histories, are encrypted, but the encryption keys are secured directly within Apple’s data centers.
The Loophole for Law Enforcement: If a user utilizes Standard Data Protection and has iCloud Backup enabled, a copy of the encryption keys for Messages in iCloud is saved on Apple’s servers to facilitate seamless account recovery.
The Legal Handover: When presented with a valid search warrant or subpoena under statutory frameworks like the Electronic Communications Privacy Act (ECPA) in the United States, Apple is legally mandated to comply. Under Standard Data Protection, Apple can and does pull these server-side backup keys or hand over the accessible iCloud backup data to law enforcement agencies. Consequently, historical message transcripts stored within an unencrypted-at-rest cloud backup can, and frequently do, end up in the hands of investigators.
Advanced Data Protection (the paradigm shift)
Recognizing this vulnerability, Apple introduced Advanced Data Protection (ADP) for iCloud. When a user manually toggles on ADP, the security landscape transforms:
End-to-End Cloud Encryption: The encryption keys for iCloud backups, photos, and Messages in iCloud are stripped entirely from Apple’s cloud servers and restricted solely to the user’s trusted physical devices.
Zero-Access Architecture: Apple enforces a strict zero-access model. If a government agency serves Apple with a warrant for iCloud data belonging to an account with ADP enabled, Apple’s response is structurally absolute: They physically cannot comply with content extraction because they possess no keys to give.
What Law Enforcement can still access: The power of metadata
Even when end-to-end encryption and Advanced Data Protection are fully active, completely sealing message contents and cloud backups away from state oversight, the government is far from powerless. Digital communication leaves behind deep trails of operational exhaust known as metadata.
Metadata consists of data about data rather than the content of the communication itself. In criminal investigations, metadata is frequently just as valuable, if not more valuable, than the message text. Apple routinely collects and retains varying tiers of metadata associated with iMessage usage, which it yields when legally compelled:
Account Registration Data: Basic subscriber information provided during Apple Account creation, including names, recovery email addresses, linked phone numbers, and account creation dates.
Connection Logs (Subscriber Records): IP addresses associated with devices logging into Apple’s iMessage servers, timestamps of connection events, and geographic location identifiers tied to network handshakes.
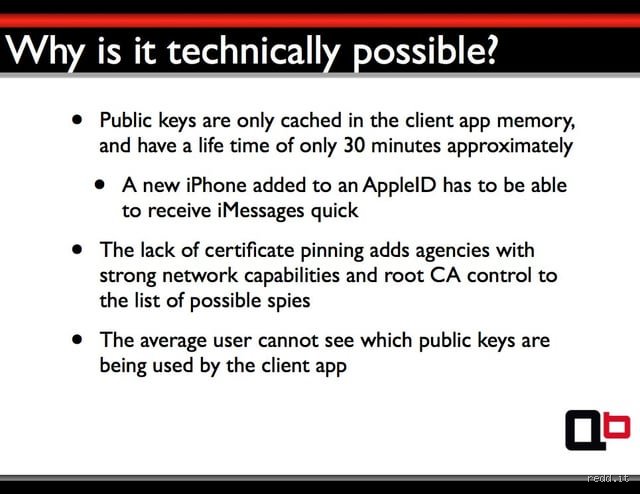
Contact Queries: Historically, when an iPhone attempts to check whether a specific phone number or email address is registered with iMessage, lookup logs have occasionally persisted on servers for brief windows, revealing patterns of who a user attempts to contact.
The "Pen Register / Trap and Trace" Reality: Under specialized legal orders, law enforcement can compel technology companies to collect real-time non-content transactional data. While a pen register cannot legally capture what is said, it can track who is talking to whom, when, and for how long.
Summary of Part 1
The capability of a government to access iMessages is not a single binary reality; rather, it is a sliding scale dictated by system architecture, user choices, and legal jurisdiction. While live transit data remains shielded by end-to-end encryption, historical accessibility relies entirely on whether a user has opted into Advanced Data Protection or relies on default cloud backups.
Metadata and auxiliary Data: What Law Enforcement can access
While the actual content of an end-to-end encrypted iMessage conversation is shielded from real-time interception or server-side retrieval by Apple, investigators are rarely left entirely empty-handed. The architecture of modern smartphone ecosystems requires various auxiliary data points and metadata to function seamlessly, and these secondary records often provide critical leads for criminal investigations.
To understand how government agencies navigate these technical boundaries, one must distinguish between the payload (the text, photos, or documents sent within a message) and the metadata (the operational breadcrumbs generated by communication systems).
Account and Registration Records
When a user sets up an iPhone and activates iMessage, their device communicates with Apple's servers to register phone numbers and Apple Account email addresses. Apple maintains basic subscriber and account information associated with these registrations. Under valid legal processes, such as subpoenas and court orders, law enforcement can request:
Basic account registration details (names, associated email addresses, and phone numbers).
Account creation dates and service connection logs.
Associated IP addresses used during account registration or recent account management actions, depending on retention schedules.
Connection and lookup Logs
For devices to know whether an intended recipient is capable of receiving an iMessage versus a standard SMS text message, the sender's device queries Apple's servers. Apple retains limited logs concerning these address lookups to optimize routing, though these logs are generally purged within short operational windows (often around 30 days). Nonetheless, if a subpoena is served while logs are active, investigators can sometimes ascertain patterns of communication routing between specific identifiers.
The role of icloud backups and Advanced Data Protection
One of the most significant variables in whether law enforcement can access iMessage contents lies in how users configure their cloud storage settings. While iMessage traffic is encrypted in transit between devices, the security posture changes drastically when backups enter the equation.
Standard icloud Backup vs. End-to-End Encryption
By default, many Apple users back up their device data, including standard iCloud backups of the Messages app, to Apple's cloud infrastructure. Under standard configurations, the cryptographic keys required to decrypt these iCloud backups are held by Apple. Consequently, if a government agency serves a search warrant accompanied by a lawful court order for a user's iCloud backup, Apple can legally and technically extract that backup data and turn it over to authorities. This means historical iMessages that have been synced and backed up to iCloud can potentially be read by law enforcement, bypassing the live end-to-end encryption barrier of transit.
Advanced Data Protection (ADP)
To close this gap, Apple introduced a feature known as Advanced Data Protection for iCloud. When a user enables Advanced Data Protection, the encryption level for iCloud backups, alongside photos, notes, and other sensitive categories, is upgraded to true end-to-end encryption. Crucially, the decryption keys are held exclusively on the user’s trusted devices, not on Apple's servers.
If Advanced Data Protection is active on an account, Apple loses the technical capability to decrypt and provide those cloud-backed messages to law enforcement, even when presented with a federal search warrant. This shifts the retrieval burden entirely away from the service provider and onto the physical device itself.
Device-Level access and forensic extraction
When cloud providers and live intercept vectors fail to yield message contents due to robust encryption and Advanced Data Protection, law enforcement agencies turn their attention to physical devices. If an investigator seizes a physical iPhone pursuant to a warrant, the focus shifts from remote data collection to digital forensics.
Local storage and SQLite databases
On an unlocked, powered-on iOS device, messages are stored locally in unencrypted SQLite databases (specifically within the application's sandbox environment). Specialized forensic tools, often developed by private intelligence and cybersecurity contractors, can extract these databases if the device is unlocked or if vulnerabilities allow for bypass techniques.
However, modern versions of iOS incorporate strict security architecture, including Secure Enclave co-processors, hardware-backed encryption, and automatic data protection states. When a phone is locked or has been restarted (known as "Before First Unlock" or BFU state), local message databases remain heavily encrypted by keys tied to the device's passcode. Without the correct passcode or a viable exploit, forensic extraction of local iMessage databases is practically infeasible.
The ongoing policy debate
The tension between digital privacy and public safety remains a central fixture of modern jurisprudence. Law enforcement agencies frequently argue that absolute end-to-end encryption creates "warrant-proof spaces" that hinder investigations into severe crimes, ranging from human trafficking to terrorism. Conversely, civil liberties organizations, cryptographers, and privacy advocates maintain that weakening encryption for the government creates systemic vulnerabilities that malicious actors, authoritarian regimes, and cybercriminals can exploit, thereby undermining the digital security of the general public.
As technology continues to evolve, the balance between privacy-preserving architectures like iMessage and lawful access frameworks will remain a heavily contested frontier at the intersection of law, ethics, and computer science.