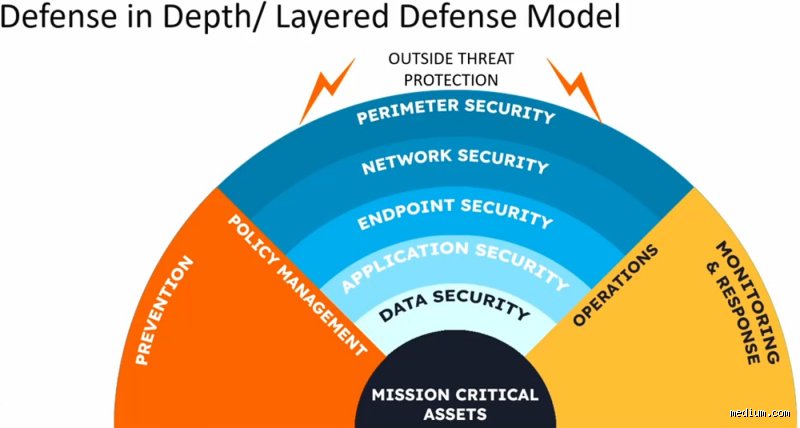
However, treating these concepts as synonyms is a critical architectural error. While layered security represents a tactical implementation of stacked controls around a specific domain, defense in depth (DiD) is an all-encompassing strategic philosophy governing organizational resilience, cross-domain mitigation, and the entire threat lifecycle. Understanding the distinct boundaries, operational mechanisms, and architectural implications of each is essential for security leaders aiming to build systems that survive inevitable compromises rather than merely looking secure on paper.
1. Defining Layered Security: The tactical stack
To understand where layered security diverges from defense in depth, one must first examine its primary focus: concentration and depth within a specific domain or attack surface.
Layered security is precisely what its name implies, the accumulation of multiple security controls stacked sequentially or concurrently around a single asset, network segment, or application stack. Consider, for example, a typical web application deployment. To protect this specific workload, an organization might deploy:
A Web Application Firewall (WAF) at the edge to filter malicious HTTP/HTTPS traffic.
A Next-Generation Firewall (NGFW) enforcing protocol-level inspection.
Host-based intrusion detection and endpoint detection and response (EDR) agents running on the host operating system.
Multi-factor authentication (MFA) requirements for administrative access to the server.
Database-level encryption protecting the underlying data store.
This configuration is unquestionably "layered." If an attacker manages to craft a SQL injection payload that slips past the poorly tuned rules of the WAF, they still face host-based EDR alerts, operating system access controls, and encryption keys.
Yet, despite this apparent robustness, layered security often remains siloed. Its primary objective is to harden a designated perimeter or asset against external or internal threats by building a thick barrier around it. The controls are chosen to protect that specific asset, frequently relying on similar administrative trust domains, overlapping vendor logic, or shared management planes. Consequently, while layered security creates substantial friction for an attacker at the entry point of a particular system, it does not inherently guarantee cross-domain resilience once that initial barrier is breached.
2. Defining Defense in Depth: The strategic blueprint
In contrast, defense in depth (DiD) is a macro-level architectural strategy rooted in military history and adapted to digital systems. Rather than focusing solely on building a thicker wall around a crown jewel, defense in depth assumes that any single control, no matter how robust, will eventually fail or be bypassed.
Defense in depth addresses the entire IT ecosystem, distributing independent, heterogeneous safeguards across multiple structural dimensions: physical security, perimeter boundaries, internal network segments, endpoints, applications, data stores, and human processes. Crucially, a true DiD posture ensures that these layers are functionally independent. If an adversary breaches the perimeter, they do not encounter another variation of the same perimeter control; instead, they transition into a completely different security paradigm governed by separate trust assumptions, distinct administrative credentials, and independent monitoring systems.
A comprehensive defense-in-depth architecture integrates controls across all four phases of the threat lifecycle:
Preventive Controls: Measures designed to block threats before execution, such as network segmentation, strict identity and access management (IAM), and vulnerability management.
Detective Controls: Systems that identify active threats or anomalies in real time, including Security Information and Event Management (SIEM) platforms, User and Entity Behavior Analytics (UEBA), and continuous threat hunting.
Responsive Controls: Mechanisms that minimize blast radius and contain incidents upon detection, such as automated EDR isolation, Just-In-Time (JIT) revocation, and dynamic incident response playbooks.
Recovery Controls: Capabilities ensuring operational continuity and data integrity, including immutable backups, disaster recovery protocols, and forensic readiness.
By orchestrating these phases across every layer of the enterprise stack, defense in depth shifts the security posture from a rigid fortification model to an adaptive, resilient ecosystem.
3. The core divergence: Tactics versus strategy
The fundamental difference between the two terms can be summarized through a simple conceptual dichotomy: layered security is a tactic, while defense in depth is a strategy.
| Dimension | Layered Security | Defense in Depth (DiD) |
|---|---|---|
| Primary Scope | Asset-specific or domain-specific (e.g., securing a single web app or cloud database). | Enterprise-wide, spanning the entire IT stack, physical environments, and human workflows. |
| Architectural Focus | Vertical depth; stacking tools to protect a single point of failure. | Cross-domain resilience; ensuring disparate failure domains and containment boundaries. |
| Underlying Assumption | "Our stacked tools will prevent unauthorized access to this asset." | "Controls will fail; we must contain lateral movement and detect anomalies anywhere in the environment". |
| Lifecycle Integration | Primarily weighted toward prevention and edge filtering. | Balanced across prevention, detection, response, and recovery. |
| Risk of Failure | High risk of single-point cascading failures if layers share common administrative logic or vendor dependencies. | Minimized blast radius; compromise of one layer does not grant unfettered access to another. |
Understanding this divergence illuminates why organizations purchasing dozens of cybersecurity point products often remain vulnerable to sophisticated breaches. Buying multiple tools that perform similar functions at the same network boundary, such as stacking three different signature-based anti-malware scanners on an endpoint, is an example of layered redundancy, but it is not defense in depth. It creates administrative bloat, alert fatigue, and resource drain without expanding the diversity of the security architecture.
4. The anatomy of Failure modes: Homogeneous versus heterogeneous Controls
To fully grasp why defense in depth provides superior resilience compared to standard layered security, one must examine how controls fail under pressure.
In a purely layered security model, organizations frequently deploy homogeneous or interdependent controls. For instance, an enterprise might secure its corporate network using a perimeter firewall from a specific vendor, rely on that same vendor's virtual private network (VPN) gateway for remote workers, and utilize the vendor's internal routing access control lists (ACLs) for segmentation. While this creates multiple physical and logical steps for traffic, all three layers share underlying codebases, administrative trust frameworks, and configuration paradigms.
If a zero-day vulnerability is discovered in that vendor's operating system or authentication daemon, an attacker who exploits the perimeter firewall has effectively compromised the administrative trust assumptions underlying the VPN and internal ACLs as well. The layers, though distinct in placement, are homogeneous in pedigree.
Defense in depth mandates heterogeneity. A true DiD architecture deliberately incorporates multi-vendor solutions, disparate operating systems, independent authentication mechanisms, and fundamentally different security primitives across layers. If an identity provider is compromised via social engineering, a robust defense-in-depth design ensures that endpoint hardware keys (such as FIDO2/WebAuthn phishing-resistant tokens), micro-segmentation policies, and behavioral anomaly detection systems operate independently of that identity provider's core database.
By forcing an attacker to solve completely different cryptographic, logical, and physical problems at every stage of an intrusion, defense in depth raises the economic and technical cost of the attack exponentially.
(End of Part 1)
Scope and Architectural boundaries: Narrow reinforcement vs. Cross-Domain breadth
Once an organization moves past perimeter-only thinking, the practical divergence between layered security and defense in depth becomes clear in how boundaries are drawn. Layered security frequently concentrates multiple safeguards around a specific attack surface, system, or workflow, such as stacking spam filtering, link inspection, and attachment sandboxing around email, or combining web application firewalls with input validation around a public application. When scoped well, this targeted concentration strengthens a high-risk entry point where adversaries routinely probe. However, because its focus is often localized, a layered arrangement around one domain can still leave adjacent domains exposed if those surrounding areas receive less rigorous attention.
Defense in depth, by contrast, operates as a cross-domain architectural strategy across the broader environment. Rather than asking only how to stop an intrusion at a single choke point, it maps controls across physical access, identity and access management, networks, endpoints, applications, and data, paired with continuous monitoring, detection, response, and recovery. Guidance from bodies such as the National Institute of Standards and Technology (NIST) and the Cybersecurity and Infrastructure Security Agency (CISA) frames defense in depth around coordinating safeguards across multiple layers and functions so that protection spans the lifecycle of an asset and its operational mission rather than resting on a single security tier.
Failure modes, independence, and containing the blast radius
A common trap in security engineering is assuming that more layers automatically equal stronger resilience. Two safeguards stacked together can still share the same underlying assumption, administrative trust path, or failure mode. If an attacker compromises a privileged credential or exploits a shared configuration flaw that undermines multiple controls at once, apparent redundancy collapses into a single point of failure.
True defense in depth addresses this risk by emphasizing independence and heterogeneity across controls. If an initial preventive control, such as an email filter or an identity check, is bypassed, downstream controls should confront the adversary with materially different obstacles. Examples include:
Identity and access controls: Enforcing phishing-resistant multi-factor authentication and least-privilege permissions so stolen credentials do not grant broad lateral movement.
Network and workload segmentation: Isolating segments or workloads so a foothold on one host cannot freely reach critical servers or sensitive data stores.
Data-centric protections: Encrypting data in transit and at rest, classifying sensitive records, and maintaining tested backups so exposure or destructive tampering has a smaller blast radius.
Detection and recovery mechanisms: Pairing telemetry and behavioral monitoring with tested restoration procedures so incidents are spotted earlier and systems can recover cleanly.
In practice, layered security often describes placing multiple barriers in front of a threat, whereas defense in depth explicitly designs for graceful failure and blast-radius containment, buying defensive time, raising attacker cost, and preserving business continuity even when an individual control is defeated.
People, process, and Governance beyond tooling
Another critical distinction lies in how heavily an approach relies on operational discipline versus standalone technology. Layered security discussions frequently center on technical controls and product stacks, firewalls, gateways, endpoint agents, and security tools. While tools are indispensable, buying overlapping products without clear ownership or operational follow-through can create siloed tools, blind spots, and unverified assumptions (such as backups that exist on paper but have never been tested for restoration).
Defense in depth explicitly integrates people, processes, and technology. Policies, patch management routines, access reviews, security awareness training, incident response playbooks, and auditability are not secondary add-ons; they are structural pillars that keep technical controls aligned and effective over time. When teams treat defense in depth purely as a software procurement exercise, they miss the governance and operational coordination that turn separate controls into a cohesive defensive posture.
| Dimension | Layered Security | Defense in Depth |
|---|---|---|
| Primary Focus | Reinforcing specific surfaces, workflows, or security controls with multiple barriers | Building cross-domain resilience across the broader environment and lifecycle |
| Architectural Scope | Often narrower or domain-specific (e.g., email, network edge, or an application tier) | Broad and multi-layered across physical, identity, network, host, application, and data domains |
| Resilience & Failure Handling | Aims for overlapping checks so one miss does not immediately succeed, though controls may sit in silos | Emphasizes independent controls, graceful failure, reduced blast radius, and detection/recovery |
| Operational & Governance Role | Can skew toward technical controls and tooling if ownership is not defined | Integrates people, policies, processes, monitoring, and response alongside technical safeguards |
Trade-Offs, complexity, and how to choose
Neither approach is free of trade-offs. Stacking redundant controls without disciplined engineering adds operational overhead, configuration complexity, administrative friction, and alert fatigue. Security teams can end up managing overlapping consoles that generate noisy alerts without improving actual containment or mean time to recovery. Conversely, attempting a sweeping, enterprise-wide rollout all at once can stall execution if teams lack clear asset priorities or foundational hygiene such as patching, identity hygiene, and tested backups.
When deciding how to allocate effort and budget, practitioners should evaluate a few concrete criteria:
Asset criticality and exposure: Prioritize high-value systems, sensitive data, and internet-facing or identity-critical paths first rather than spreading controls evenly without risk weighting.
Control independence: Verify whether an added control genuinely catches attacks missed by upstream controls or simply duplicates the same check and shares the same failure domain.
Detection, containment, and recovery readiness: Ensure controls do not only attempt prevention; confirm that teams can detect anomalies, contain lateral movement, and restore operations reliably.
Alignment with modern access models: Pair layered safeguards and defense in depth with principles like least privilege, segmentation, and continuous verification (often associated with Zero Trust architectures) rather than relying on static network perimeters.
Conclusion
Layered security and defense in depth are closely related, frequently conflated concepts, yet conflating them obscures important architectural choices. Layered security captures the practical value of placing multiple barriers in the path of a threat so a single missed check does not end the story. Defense in depth elevates that principle into a comprehensive, cross-domain strategy uniting people, processes, and diverse technical controls to limit blast radius, withstand partial failures, and sustain operations under pressure. The strongest security programs do not treat these ideas as rival slogans or tool checklists; they use clear ownership, independent controls, and tested recovery to turn layered defenses into genuine, verifiable resilience.