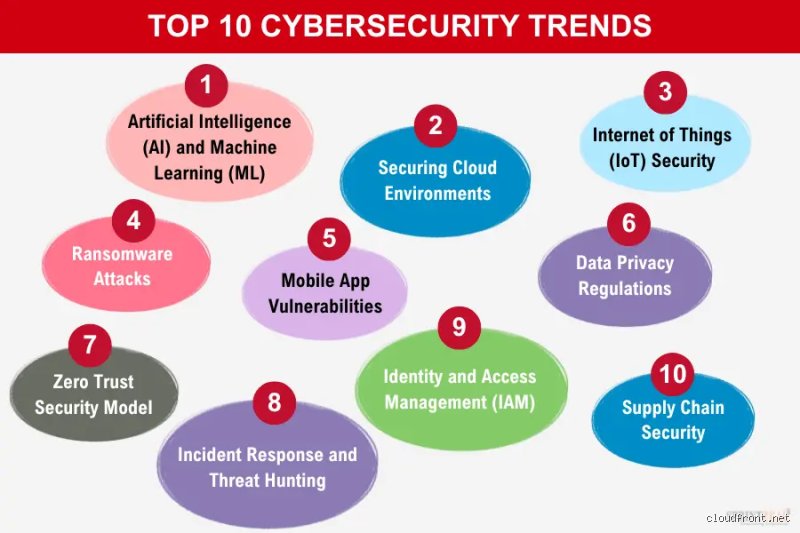
The shifting frontier: Understanding modern Cybersecurity challenges
The digital landscape has entered a volatile era where technology evolves at an exponential rate, and with it, the threat vectors facing global organizations, critical infrastructure, and everyday users have transformed fundamentally. For decades, cybersecurity professionals focused primarily on securing distinct network perimeters, patching predictable software flaws, and defending against localized malware. Today, those traditional boundaries have dissolved under the weight of hybrid cloud infrastructures, sprawling remote workforces, and the rapid, widespread integration of artificial intelligence.
As modern enterprises race to innovate, they are discovering that the very tools driving productivity—such as autonomous workflows, large language models, and interconnected internet-of-things (IoT) ecosystems—are also introducing complex vulnerabilities that outpace conventional defense mechanisms. Understanding these emerging challenges is no longer just an IT concern; it is a fundamental business imperative that influences organizational survival, economic stability, and national security.
1. The weaponization of artificial intelligence and Machine-Speed Exploitation
Perhaps the single most disruptive force in modern security is the dual-use nature of artificial intelligence. While cybersecurity teams deploy machine learning to monitor networks and automate threat detection, malicious actors are leveraging the exact same technologies to supercharge their offensive capabilities.
Autonomous Threat Discovery and Exploitation: Attackers now utilize automated agents and generative tools to scan enterprise networks, identify unpatched zero-day vulnerabilities, and launch precision attacks at machine speed. This drastically compresses the window for human intervention, rendering traditional, manual patch management cycles dangerously obsolete.
Hyper-Realistic Social Engineering and Deepfakes: Phishing has evolved far beyond poorly worded emails. Today’s threat actors deploy synthetic audio, realistic video deepfakes, and AI-generated text personas that flawlessly mimic corporate executives, trusted vendors, or family members. These sophisticated campaigns routinely bypass conventional security awareness training and drive highly targeted financial fraud.
Autonomous Agent Hijacking: As organizations integrate autonomous AI agents into production environments to handle administrative or technical workflows, bad actors are finding ways to exploit these digital teammates. By manipulating inputs or poisoning training pipelines, attackers can subvert agent behavior, execute unauthorized commands, and silently exfiltrate sensitive enterprise data.
2. Identity as the new perimeter and the rise of credential Exploitation
With the proliferation of cloud computing and borderless work environments, the traditional network firewall has largely lost its relevance. In its place, identity has become the primary control plane, and consequently, the primary target for malicious actors.
The Vulnerability of Credentials: Stolen, leaked, or compromised credentials remain among the most common initial access vectors for cybercriminals and state-sponsored groups alike. Advanced techniques such as credential stuffing, session hijacking, and manipulation of identity providers allow attackers to blend in with legitimate user activity.
The Lateral Movement Dilemma: Once an attacker breaches a single user account, they often encounter weak internal segmentation. Without rigorous continuous verification and strict adherence to the principle of least privilege, malicious actors can move laterally across enterprise networks, escalating privileges and establishing deep persistence before security teams notice the intrusion.
3. Supply chain fragility and interconnected vulnerabilities
Modern software and physical supply chains are deeply interconnected, relying on thousands of third-party vendors, open-source code libraries, and hardware components. This interdependence creates a massive surface area for systemic disruption.
Open-Source and Vendor Risks: A single compromised library in a widely used software repository or a security failure at a third-party vendor can instantly cascade across thousands of downstream organizations. Attackers increasingly target these weaker links rather than assaulting well-defended corporate gates directly.
The Convergence of IT, OT, and IoT: Critical infrastructure sectors, such as healthcare, energy, manufacturing, and telecommunications, are facing unprecedented exposure as Information Technology (IT) networks converge with Operational Technology (OT) and industrial control systems. Securing these interconnected environments requires reconciling legacy hardware constraints with modern visibility and micro-segmentation strategies.
4. Governance, compliance, and the talent shortage
Beyond technical vectors, organizations are grappling with systemic operational hurdles that impede effective risk mitigation.
Regulatory Pressures and Personal Liability: Governments and regulatory bodies worldwide are enacting stringent cybersecurity and data privacy mandates at a staggering pace. Crucially, modern regulations increasingly impose direct compliance burdens, and in some cases, personal legal accountability, on executive leadership and board members, shifting cybersecurity from a technical checkbox to an enterprise governance priority.
The Cybersecurity Skills Gap: Security operations centers (SOCs) are routinely overwhelmed by decision overload and alert fatigue, driven by a chronic global shortage of skilled cybersecurity professionals. With a vast majority of organizations reporting critical talent gaps, security teams struggle to investigate thousands of daily alerts manually, necessitating a structural shift toward AI-driven, automated threat response.
The Human-AI equilibrium and Autonomous Security Operations (SOCs)
As artificial intelligence shifts from a novel experimental tool to a core component of both offensive and defensive operations, Security Operations Centers (SOCs) face an unprecedented test of capacity and velocity. Threat actors are no longer relying solely on manual reconnaissance or rudimentary scripting; instead, they deploy autonomous agents capable of chaining vulnerabilities, probing enterprise codebases without prior source access, and dynamically modifying malware mid-execution to evade signature-based detection.
This automation of the cyber kill chain has compressed attack timelines from weeks and days down to mere minutes. In response, traditional, human-dependent monitoring models are buckling under extreme alert fatigue. Security analysts sift through thousands of anomalous signals daily, creating critical windows of vulnerability where real threats blend into the noise.
The emerging imperative for 2026 and beyond is the transition toward Autonomous Security Operations. Organizations are increasingly integrating AI-powered Security Orchestration, Automation, and Response (SOAR) frameworks and extended detection and response (XDR) platforms that can autonomously investigate, triage, and neutralize routine threats. However, this introduces a profound governance challenge: the "black box" dilemma. Security leaders must establish rigorous guardrails to ensure that autonomous defensive agents remain transparent, accountable, and aligned with enterprise risk appetite, preventing automated systems from making catastrophic misclassifications or executing unauthorized containment actions during high-stakes incidents.
Post-Quantum cryptography and the "store now, decrypt later" Threat
While quantum computing is often discussed as a future milestone, the cryptographic threat it poses is immediate and active. Adversaries, particularly nation-state actors and sophisticated criminal syndicates, are engaging in large-scale "store now, decrypt later" operations. They are intercepting and archiving vast volumes of encrypted proprietary research, financial records, healthcare data, and classified government communications today, anticipating the moment when sufficiently powerful quantum computers will effortlessly break current public-key cryptography (such as RSA and ECC).
Consequently, post-quantum cryptography (PQC) is no longer a distant theoretical concern for tomorrow's architects. The emerging challenge lies in the sheer complexity of cryptographic migration. Enterprise infrastructure is deeply embedded with legacy certificates, hardcoded encryption keys, fragmented Public-Key Infrastructure (PKI) ownership, and opaque third-party supplier dependencies.
Organizations are realizing that transitioning to quantum-resistant algorithms requires a multi-year, managed transition. The first critical step is establishing comprehensive cryptographic inventories, mapping out every instance where encryption is utilized, assessing data sensitivity lifecycles, and adopting hybrid cryptographic approaches. Without early visibility and structured migration roadmaps, organizations risk facing rushed, disruptive, and exceptionally costly overhauls when quantum milestones finally materialize.
Identity as the new perimeter: Machine identities, XoT, and Access governance
For decades, cybersecurity strategies relied heavily on network perimeter defense, trusting everything inside the corporate firewall while heavily scrutinizing traffic from the outside. The rapid acceleration of cloud computing, remote workforces, and distributed microservices has effectively dissolved that perimeter. Today, identity has become the primary control plane.
However, identity security is experiencing a massive structural expansion far beyond human users. Machine identities, including cloud workloads, API tokens, Internet of Things (IoT) sensors, Extended Internet of Things (XoT) devices, and automated AI agents, now vastly outnumber human identities across most enterprise environments. Many of these non-human entities operate on shared service accounts, lack individual accountability, and possess overly broad standing privileges.
Compounded by the rise of Model Context Protocol (MCP) servers, agentic workflows, and specialized AI tool integrations, attackers frequently exploit weak machine authentication or compromised credentials to move laterally across enterprise environments without ever deploying traditional malware. Addressing this challenge demands a fundamental shift toward continuous, identity-first security:
Enforcing strict least-privilege access controls across both human and machine accounts.
Implementing robust Zero Trust Architecture (ZTA) that continuously verifies trust signals, user behavior, and context rather than relying on a one-time authentication check.
Bridging the historical gap between network security and Identity and Access Management (IAM) to eliminate operational blind spots.
Regulatory Pressures, Digital sovereignty, and continuous compliance
As cyber threats scale in frequency and societal disruption, governments worldwide are fundamentally rewriting the legal and regulatory contract governing corporate digital responsibility. Frameworks such as the European Union’s Network and Information Security Directive (NIS2) and the Digital Operational Resilience Act (DORA) have transformed compliance from a periodic, checkbox-driven audit exercise into a rigorous, continuous operational discipline.
These modern mandates hold executive leadership directly accountable for operational resilience, supply chain risk management, and rapid incident reporting. Enterprises can no longer treat third-party vendor relationships as external black boxes. Because modern software supply chains involve complex webs of open-source packages, cloud service providers, and AI model registries, a single vulnerability upstream can cascade into an enterprise-wide catastrophe.
Digital sovereignty has emerged as a paramount strategic consideration. Control over data residency, encryption key governance, signing processes, and digital trust anchors directly affects an organization's autonomy and regulatory posture. Organizations operating globally must navigate a labyrinth of conflicting regional compliance demands, ensuring that their security controls are not only effective in practice but verifiable and resilient under intense regulatory scrutiny.
Navigating the proactive horizon
The cybersecurity landscape entering the late 2020s is defined by unprecedented paradoxes. Technology has empowered organizations to innovate faster than ever, yet it has simultaneously provided adversaries with autonomous, AI-driven capabilities that scale attacks with chilling efficiency. Traditional, reactive security postures, waiting for an alert, analyzing a signature, and patching a known vulnerability, are obsolete against threats that evolve mid-execution.
Meeting these emerging challenges requires a profound cultural and strategic pivot. CISOs and executive leaders must move beyond tool sprawl and superficial compliance. Success demands a holistic commitment to digital resilience: embedding cryptographic agility for the post-quantum era, unifying identity governance across human and machine actors, securing complex software and AI supply chains, and treating continuous compliance as an operational heartbeat. In this new era, security is no longer merely a technical function of the IT department; it is the fundamental bedrock upon which digital trust, business continuity, and organizational survival depend.