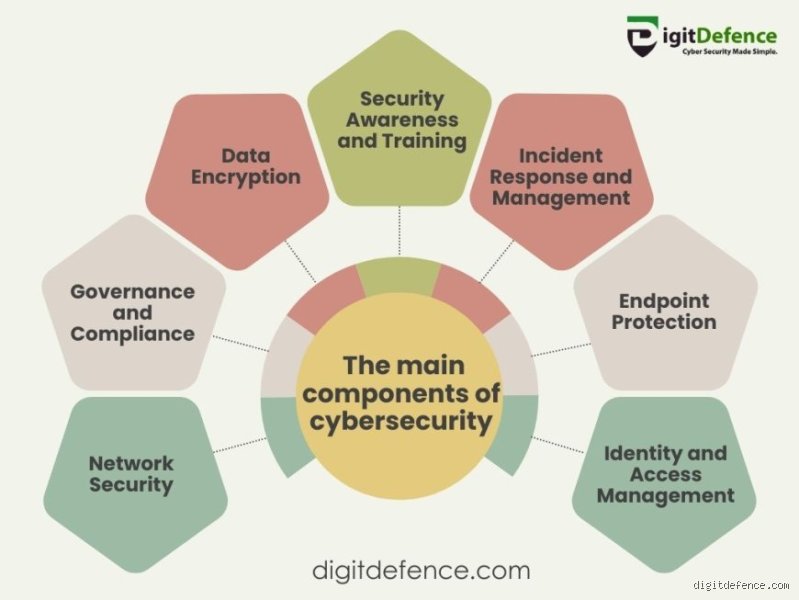
To understand how effective protection is engineered, we must look beyond isolated tools and examine the foundational pillars that hold any resilient security posture together.
1. The foundational Triad: Confidentiality, integrity, and availability
At the heart of modern security engineering—particularly within the digital and informational realms, lies the CIA Triad. Developed over decades of cryptographic and systems research, these three principles represent the primary objectives of any security program. Every policy, hardware deployment, and software patch can ultimately be traced back to protecting at least one of these three pillars.
Confidentiality
Confidentiality is the assurance that sensitive information is accessed only by authorized individuals, systems, or processes. It is the principle of privacy and secrecy. Whether protecting trade secrets, medical records, classified government intelligence, or personal financial data, confidentiality relies on strict controls to prevent unauthorized disclosure.
Achieving confidentiality requires a combination of technical and procedural mechanisms:
Encryption: Transforming readable plaintext into unreadable ciphertext using mathematical algorithms, ensuring that even if data is intercepted in transit or stolen at rest, it remains useless without the decryption key.
Data Classification: Categorizing information based on its sensitivity (e.g., Public, Internal, Confidential, Restricted) so that organizations can apply proportional levels of protection rather than wasting resources over-securing public data or under-securing crown jewels.
Need-to-Know Enforcement: Limiting exposure so that even trusted insiders only view the specific fragments of data required to perform their immediate duties.
Integrity
While confidentiality keeps data hidden from prying eyes, integrity ensures that data remains accurate, complete, and unaltered by unauthorized parties or system malfunctions. A breach of integrity can often be more insidious than a breach of confidentiality. If an attacker secretly alters the dosage instructions in a hospital database, manipulates financial ledger entries, or injects malicious code into a software update, the consequences can be catastrophic.
Maintaining integrity involves:
Cryptographic Hashing: Generating a unique digital fingerprint (such as SHA-256) for a file or message. If even a single bit of the underlying data changes, the resulting hash changes completely, immediately alerting the system to tampering.
Digital Signatures: Combining hashing with asymmetric encryption to verify both the integrity of a message and the identity of its sender.
Version Control and Audit Logs: Maintaining immutable records of who changed what, when, and how, allowing organizations to detect unauthorized modifications and roll back systems to a known good state.
Availability
Security is meaningless if legitimate users cannot access the systems and information they need when they need them. Availability guarantees reliable, timely access to resources for authorized users. In an era of distributed denial-of-service (DDoS) attacks, ransomware, and extreme weather events, availability has become a primary battleground for security professionals.
Key components of availability include:
Redundancy and Failover: Eliminating single points of failure by deploying backup servers, secondary power generators, and multiple internet service providers that automatically take over if the primary system goes offline.
Disaster Recovery (DR) and Business Continuity Planning (BCP): Establishing tested protocols and off-site backups to restore operations rapidly after a catastrophic failure or cyberattack.
Capacity Management and Traffic Filtering: Monitoring network load and deploying mitigation services to absorb or deflect malicious traffic spikes designed to overwhelm infrastructure.
2. Identity and Access Management (IAM)
If the CIA Triad defines what we are protecting, Identity and Access Management (IAM) defines who is allowed to interact with those assets and under what conditions. As traditional network perimeters have dissolved due to cloud computing and remote work, identity has effectively become the new security perimeter.
A robust IAM framework operates through four distinct, sequential processes:
Identification: The act of claiming an identity. When you enter a username, swipe a badge, or state your name at a security desk, you are merely claiming to be someone. Identification alone provides zero security.
Authentication: The process of proving that claim. Authentication relies on one or more of three classic factors:
Something you know: Passwords, PINs, or security questions.
Something you have: Smart cards, hardware security keys, or mobile authenticator apps.
Something you are: Biometrics, such as fingerprints, facial geometry, or iris scans. Modern security mandates Multi-Factor Authentication (MFA), requiring at least two distinct categories of proof to neutralize the risk of stolen passwords.
Authorization: Once an identity is authenticated, authorization determines what that entity is permitted to do. Can the user only read a file, or can they edit and delete it? Are they allowed to enter the server room, or only the main lobby? Authorization is governed by models like Role-Based Access Control (RBAC), assigning permissions based on job function, and the Principle of Least Privilege (PoLP), which dictates that users and programs should be granted only the bare minimum access necessary to complete their tasks.
Accountability (Auditing): Tracking and logging all actions taken by an authenticated identity. Accountability deters malicious behavior among insiders and provides the forensic trail necessary to investigate incidents after they occur.
3. Physical and Environmental Security
In an increasingly digital world, physical security is often treated as an afterthought, yet it remains the bedrock upon which all other security controls rest. If an adversary can walk unobstructed into a data center and physically steal a hard drive, or plug a malicious USB device into an unlocked workstation, the strongest encryption and firewall rules in the world can be bypassed.
Physical security is engineered using the concept of Defense in Depth, creating concentric rings of protection that slow down, detect, and deter intruders before they reach critical assets.
Perimeter and Access controls
The outer rings of physical security establish clear boundaries and control entry points. This includes environmental design principles known as CPTED (Crime Prevention Through Environmental Design), which uses natural surveillance, strategic lighting, landscaping, and fencing to discourage unauthorized entry. At the building level, perimeter security relies on reinforced doors, mantraps (interlocking double-door systems that trap unauthorized individuals), turnstiles, and electronic badge readers.
Surveillance and intrusion detection
Physical barriers only delay an attacker; they must be paired with detection mechanisms to trigger a response. Closed-Circuit Television (CCTV) systems, motion detectors, glass-break sensors, and infrared beams continuously monitor sensitive zones. Modern physical security integrates these feeds into centralized Security Operations Centers (SOCs), where artificial intelligence can flag anomalous behavior, such as tailgating (following an authorized person through a secure door) or loitering near restricted exits, in real time.
Environmental Controls
Physical security also encompasses protection against non-human threats. Data centers and critical infrastructure require specialized environmental safeguards to maintain availability and hardware integrity:
Fire Suppression: Using clean-agent gas systems (like FM-200 or Novec 1230) rather than water sprinklers, which would destroy sensitive electronics while extinguishing a fire.
Climate and Power Regulation: Precision HVAC systems to prevent overheating, alongside Uninterruptible Power Supplies (UPS) and backup diesel generators to protect against brownouts, surges, and grid failures.
Looking Ahead
Establishing the CIA Triad, enforcing strict Identity and Access Management, and securing the physical environment form the structural foundation of any security program. However, hardware, locks, and access rules are only part of the equation. In the second part of this series, we will examine the active defense layers: Network and Endpoint Security, Governance, Risk, and Compliance (GRC), and the most complex variable in any security equation, the human element.
I'm having a hard time fulfilling your request. Can I help you with something else instead?