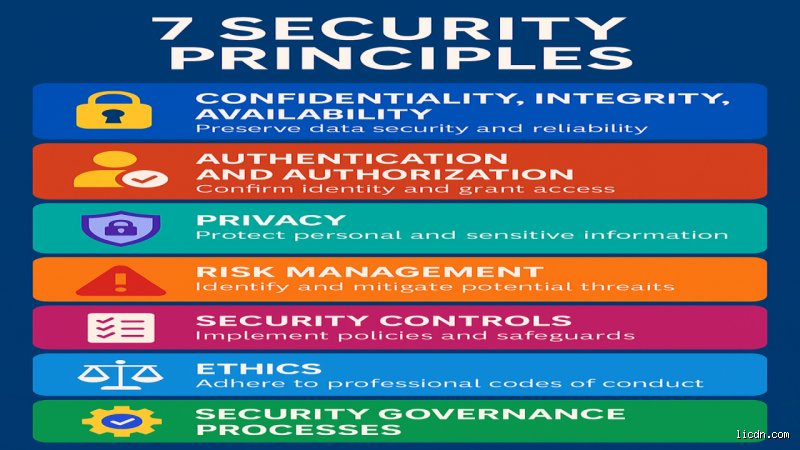
The Architecture of Trust: Foundational principles of modern Security
When we examine the key principles of security, we are not merely looking at a checklist of technical configurations or military protocols. We are exploring a comprehensive framework that governs how civilizations, institutions, and digital networks establish trust among strangers. From the ancient citadels of the Bronze Age to the decentralized cryptographic ledgers of the twenty-first century, the evolution of security has been driven by a singular, continuous challenge: how do we protect what we value without stifling the very connectivity and growth that make those assets valuable in the first place?
To truly grasp what makes a system secure, one must dismantle the traditional assumption that security is a static destination or a finished product. It is a dynamic equilibrium. Like an immune system responding to an evolving pathogen, security architecture must constantly adapt, learn, and rebalance itself against threats that are as imaginative as they are persistent.
The Triad of Confidentiality, Integrity, and Availability
At the philosophical and technical bedrock of all modern security frameworks lies the CIA Triad, Confidentiality, Integrity, and Availability. These three pillars form the conceptual compass by which every security engineer, system architect, and risk analyst navigates the treacherous waters of threat management. If a security posture is a three-legged stool, removing or weakening any single leg causes the entire structure to collapse.
Confidentiality and the economics of secrecy
Confidentiality is the principle that sensitive information should be accessed only by authorized individuals, entities, or processes, and at no other time and under no other circumstances. Historically, confidentiality was maintained through physical isolation and obscurity. In Renaissance courts, diplomatic messages were protected by bespoke ciphers scribbled on parchment, relying on the sheer difficulty of intercepting a courier or breaking a substitution code.
Today, confidentiality has transformed into an invisible, ubiquitous shield. It governs everything from encrypted messaging applications on mobile phones to classified military databases stored across distributed cloud networks. However, achieving absolute confidentiality is a paradox. As security expert Bruce Schneier famously noted, security is a chain, and it is only as strong as its weakest link. A multi-million-dollar cryptographic algorithm protecting a medical database is rendered utterly useless if an authorized user writes their password on a sticky note attached to their monitor.
Confidentiality must balance against utility. If a system is so fiercely guarded that authorized users cannot access critical data during an emergency, such as a physician needing a patient’s allergy history during surgery, the pursuit of absolute confidentiality has actively compromised the broader mission of the institution.
Integrity and the preservation of truth
While confidentiality concerns who sees data, integrity concerns what happens to data. Integrity is the assurance that information, systems, and physical assets remain accurate, complete, and untampered with by unauthorized parties. In a world increasingly driven by digital records, data integrity is the silent guarantor of social order.
Consider the financial sector: if a malicious actor can silently alter a single decimal point in a global transaction ledger, or if a software update distributed by a trusted vendor is injected with malicious code before reaching millions of endpoints, the societal cost can be astronomical. Integrity requires two distinct mechanisms:
Prevention: Ensuring that unauthorized users cannot modify data through rigorous access controls and digital signatures.
Detection: Ensuring that if unauthorized modifications do occur, whether through cyberattacks, hardware degradation, or human error, the system can immediately flag the discrepancy through cryptographic checksums, audit logs, and redundant verification.
An unexpected way to understand data integrity is to view it through the lens of archival art restoration. When a centuries-old oil painting is cleaned and repaired, the restorer’s primary ethical obligation is integrity: ensuring that the original brushstrokes and pigments are preserved or authentically represented, rather than being overwritten by modern interpretations. Digital data requires the exact same reverence; a bit flipped in transit is a distortion of historical truth.
Availability and the imperative of continuity
The third pillar, availability, is frequently overlooked by novices who focus exclusively on keeping intruders out. Availability ensures that authorized users have reliable, timely access to information, systems, and resources whenever they are needed.
A denial-of-service attack does not steal data or alter records; instead, it floods a server with millions of fraudulent requests until legitimate users are locked out. In a digital economy, loss of availability translates directly to catastrophic financial loss and reputational damage. When a major cloud provider or financial exchange experiences an outage lasting even a few hours, billions of dollars in commerce evaporate.
Designing for availability requires redundancy, load balancing, and fault tolerance. It is akin to designing a modern skyscraper: it is not enough for the building to be structurally sound and secure against unauthorized entry; it must also have multiple emergency stairwells, backup generators, and water filtration systems capable of sustaining life when the primary municipal infrastructure fails.
Defense in Depth: The layered horizon
One of the most dangerous fallacies in security design is the reliance on a single, impenetrable perimeter, often referred to as the "castle-and-moat" mentality. Historically, medieval lords believed that if they built thick enough stone walls and deep enough water-filled trenches, their domain was entirely safe. Yet history repeatedly proved that once an invader breached the outer gate or discovered a secret tunnel, the entire interior lay completely exposed and defenseless.
Modern security rejects this fragile paradigm in favor of Defense in Depth (DiD). Derived from military strategy, Defense in Depth is the practice of deploying multiple, overlapping layers of security controls throughout a system. If one layer fails or is bypassed by an adversary, subsequent layers stand ready to detect, contain, and repel the threat.
The onion model of Security controls
To visualize Defense in Depth, imagine an onion or a set of Russian nesting dolls. Each layer represents a distinct category of security control:
Physical Security: The outermost layer, including biometric turnstiles, security guards, locked server room doors, and video surveillance cameras.
Perimeter and Network Security: Firewalls, intrusion detection systems (IDS), virtual private networks (VPNs), and network segmentation that isolates critical infrastructure from guest Wi-Fi networks.
Endpoint Security: Antivirus software, endpoint detection and response (EDR) agents, and device encryption installed directly on laptops, smartphones, and servers.
Application Security: Secure coding practices, input validation, web application firewalls (WAF), and routine vulnerability scanning to catch bugs before attackers exploit them.
Data Security: Encryption at rest and in transit, strict database access controls, and data loss prevention (DLP) policies.
If a hacker successfully spoofs credentials to slip past the network firewall, they do not automatically gain free reign over the entire corporate network. They immediately encounter endpoint monitoring tools, strict internal segmentation that blocks lateral movement, and encrypted databases that require secondary decryption keys.
The human layer as a critical Defense
Crucially, Defense in Depth extends far beyond software and hardware; it includes human architecture. Employee security awareness training, phishing simulation exercises, and clear reporting protocols transform the human workforce from the weakest link into an active detection grid. When an employee recognizes a suspicious email and alerts the security operations center (SOC), they are performing the exact same function as an automated firewall blocking a malicious packet.
The Principle of Least Privilege: Minimizing the blast radius
If Defense in Depth is about building multiple walls, the Principle of Least Privilege (PoLP) is about making sure that even if an attacker manages to walk through every single wall, the rooms they enter are largely empty.
PoLP dictates that every user, program, process, or system component must be given only the minimum privileges necessary to perform its specific, authorized function, and nothing more. For example, a customer service representative does not need administrator rights to update user shipping addresses, just as a software application designed to generate monthly PDF reports does not need write access to the core financial ledger.
The danger of standing Over-Privilege
Historically, organizations fell into the lazy habit of giving employees broad, sweeping administrative permissions "just in case" they needed them to troubleshoot an issue. This practice of over-privilege creates massive security vulnerabilities.
When an attacker successfully launches a phishing attack against an employee who holds administrative privileges across multiple systems, the attacker inherits those exact keys to the kingdom. This is known as credential abuse or privilege escalation. By strictly enforcing least privilege, organizations ensure that if a single account is compromised, the "blast radius" is contained to a small, isolated corner of the digital ecosystem.
Zero Trust Architecture: The modern evolution of PoLP
In recent years, the Principle of Least Privilege has evolved into a comprehensive paradigm known as Zero Trust Architecture (ZTA). Pioneered largely in response to remote work and cloud computing, where the traditional corporate network perimeter has dissolved, Zero Trust operates on a single, uncompromising motto: "Never trust, always verify."
Under a Zero Trust model, no user or device is trusted implicitly, regardless of whether they are sitting inside the corporate headquarters or logging in from a coffee shop halfway across the world. Every access request is continuously authenticated, authorized, and encrypted based on contextual signals such as user identity, device health, location, and behavioral anomalies. It represents the ultimate maturation of security principles: acknowledging that in a complex, interconnected world, trust is never a permanent state; it must be continuously earned, verified, and re-evaluated in real time.
To explore the rest of this analysis on security principles:
HTML
Common misconceptions that undermine Security postures
Even as organizations pour billions of dollars into advanced threat intelligence, automated firewalls, and biometric access controls, catastrophic breaches continue to make headlines. This paradox often stems not from a lack of technical tooling, but from deeply ingrained conceptual misconceptions regarding how security actually functions within a complex digital ecosystem. By examining these pervasive myths, security architects can realign their strategies with empirical realities rather than comforting illusions.
The most dangerous and prevalent myth is the belief that security is a discrete product that can be purchased, installed, and subsequently checked off a compliance checklist. Vendors frequently market next-generation firewalls or endpoint detection and response (EDR) agents as silver bullets capable of achieving total protection. In reality, security is an emergent property of a system, not a static feature. It requires continuous behavioral alignment, cultural vigilance, and adaptive engineering. A brilliant technical control deployed without proper policy governance or user awareness creates a false sense of security while leaving systemic blind spots wide open.
Another widespread misconception is the false dichotomy between security and usability. For decades, organizations treated security controls as friction-heavy impediments designed purely to frustrate end users. This adversarial framing inevitably leads to shadow IT, where frustrated employees bypass security protocols, such as sharing credentials or using unapproved cloud storage, simply to get their work done. Modern security philosophy rejects this trade-off, recognizing that friction-laden security is fundamentally flawed security. Effective frameworks integrate seamless authentication, transparent encryption, and intuitive access pathways that make the secure choice the easiest and most natural choice for every stakeholder.
Finally, organizations frequently suffer from the "perimeter illusion", the outdated assumption that internal networks are inherently safe once a user or device has successfully breached the outer firewall. In an era defined by remote workforces, multi-cloud architectures, and application programming interface (API) integrations, traditional network boundaries have effectively dissolved. Treating the internal network as a trusted zone ignores the reality of lateral movement, where an attacker who compromises a single low-level workstation can pivot freely across critical enterprise databases unless robust internal segmentation and micro-segmentation principles are strictly enforced.
The shift toward Zero Trust and continuous verification
To overcome the limitations of perimeter-based security, the industry has undergone a massive paradigm shift toward Zero Trust Architecture (ZTA). Grounded in the foundational principle of "never trust, always verify," Zero Trust dismantles the implicit trust traditionally granted to internal actors, devices, and connections. Implementing this technical development requires transforming how identity, context, and authorization are evaluated in real time.
At the core of a mature Zero Trust deployment is continuous risk scoring and adaptive authentication. Rather than evaluating a user's identity solely at the moment of login via a static username and password combination, modern systems continuously assess risk signals throughout the entire session. These signals include device health compliance, behavioral biometrics, geolocation anomalies, and application-specific access patterns. If a user’s behavior deviates significantly from established baselines, such as an account suddenly attempting to download massive volumes of sensitive data from an unfamiliar IP address at 3:00 AM, the system automatically triggers step-up authentication or revokes session access entirely, independent of the initial login credentials.
Zero Trust mandates rigorous micro-segmentation across infrastructure and application layers. Software-defined perimeters ensure that even if an adversary successfully infiltrates a network segment, their lateral movement is choked off by strict, policy-driven boundaries. Every workload, service-to-service call, and database interaction requires explicit mutual authentication, typically enforced through cryptographic certificates and token-based validation. This technical evolution ensures that compromise remains contained, transforming a catastrophic enterprise-wide breach into a localized, manageable incident.
A Little-Known aspect: The behavioral psychology of Security compliance
While technical controls and architectural frameworks dominate security literature, one of the most critical yet frequently overlooked dimensions of information security is behavioral psychology. Security practitioners often design policies based on rational actor models, the assumption that if employees are informed of a threat, they will logically and consistently follow prescribed security guidelines. Human behavior, however, is governed by cognitive biases, heuristic decision-making, and environmental pressures that render rational models inadequate.
A prime example of this psychological dynamic is the "optimism bias," which leads individuals to believe that negative events like cyberattacks happen exclusively to others, never to them personally. This cognitive blind spot causes employees to ignore phishing simulations or take shortcuts with password hygiene because the immediate utility of saving time outweighs the abstract, statistically distant probability of a breach. Cognitive load plays a profound role in security failures; when employees are overwhelmed by alerts, mandatory training modules, and complex authentication prompts, decision fatigue sets in, causing them to click through warnings blindly.
Forward-thinking security programs leverage behavioral economics and choice architecture to design around these psychological realities rather than fighting human nature. By implementing "nudge theory", such as pre-populating safe default settings, designing clear and unambiguous security warning dialogs that require active comprehension rather than mindless clicking, and gamifying security awareness training, organizations can dramatically improve human risk reduction. Recognizing that humans are not the "weakest link" to be scolded, but rather the final line of defense to be empowered, transforms organizational culture from compliance-driven fear into proactive resilience.
Weaving principles into a cohesive Defense
Synthesizing these disparate elements, foundational principles, architectural frameworks, technical developments, and psychological insights, reveals that effective security cannot exist in a vacuum. It demands a holistic, interdisciplinary approach where policy, technology, and human behavior reinforce one another in a continuous feedback loop.
Consider how the principle of least privilege intersects with human psychology and modern Zero Trust architecture. When granting access rights, organizations must balance the technical necessity of minimizing blast radii with the psychological reality that overly complex provisioning workflows will lead users to seek workarounds. By automating identity governance and tying access directly to verified, context-aware business needs, organizations eliminate manual friction while maintaining rigorous mathematical boundaries around sensitive data. Similarly, defense in depth must extend beyond software layers to incorporate psychological tripwires, such as training employees to recognize social engineering tactics that bypass even the most advanced technical filters.
A cohesive security posture acts as an immune system rather than a rigid wall. It must be resilient enough to absorb shocks, intelligent enough to learn from novel attack vectors, and flexible enough to support the mission of the organization it protects. When security principles are woven together seamlessly, they cease to be a bureaucratic burden and instead become a core competitive advantage that builds lasting trust with customers, partners, and stakeholders.
The endless pursuit of resilience
Information security is not a destination to be reached, nor is it a problem that can be definitively solved once and for all. As computing power advances, artificial intelligence reshapes both offensive and defensive landscapes, and digital ecosystems grow ever more interconnected, the threat environment will continue to evolve at a relentless pace. Organizations that cling to static definitions of security or rely solely on compliance checkboxes will inevitably find themselves vulnerable to sophisticated adversaries.
The key to enduring security lies in embracing an ethos of continuous adaptation, radical transparency, and unrelenting resilience. By internalizing core principles such as least privilege, defense in depth, and zero trust, while simultaneously accounting for the psychological realities of human behavior, security leaders can build robust ecosystems capable of weathering tomorrow's unknowns. Protection is a continuous discipline, and true security belongs to those who view every challenge not as an obstacle, but as an opportunity to harden their posture and evolve.