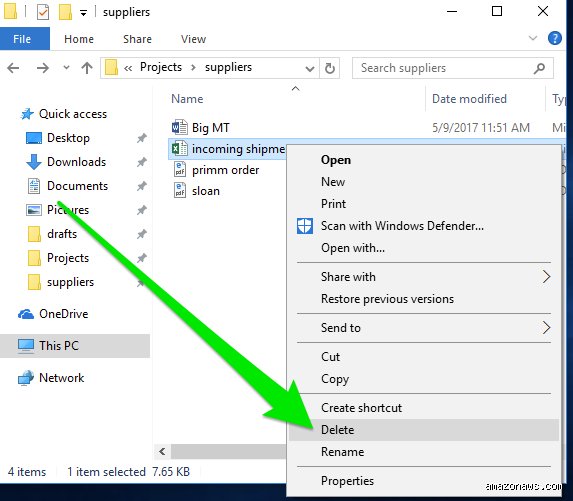
Because we interact with digital operating systems using physical metaphors—desktops, folders, trash cans, and wastebaskets—we naturally project physical permanence onto digital actions. We assume that a digital file behaves like a physical document. When we send it to the digital trash, we expect it to undergo a digital shredding process.
However, the inner workings of modern computer architecture, storage hardware, and operating systems tell a vastly different story. in digital data, deleting a file almost never means destroying it immediately. Instead, standard file deletion is an act of administrative bookkeeping. The operating system simply unhooks the file's index, marks its storage space as "available" for future use, and hides it from your view. The actual data bits and bytes remain intact, sitting quietly on your storage media, waiting either to be overwritten by new data or to be recovered by specialized forensic software.
Understanding this reality is crucial not only for data privacy and cybersecurity but also for digital forensics, data recovery, and appreciating how modern operating systems manage storage.
1. The anatomy of a File System: Pointers, inodes, and Metadata
To understand how files are deleted, we must first understand how they are stored. Your computer's storage drive, whether it is a spinning platter or a solid-state chip, is fundamentally a massive, continuous ocean of binary data: millions of zeros and ones grouped into sectors, blocks, or pages.
Left entirely on its own, an operating system would have an impossible time finding a specific document or photograph in this ocean of raw data. If you wanted to open a 5-megabyte vacation photo, the operating system would otherwise have to scan every single sector of the drive from start to finish until it happened to stumble across the correct sequence of bytes.
To solve this problem, operating systems use a File System (such as NTFS on Windows, APFS or HFS+ on macOS, and ext4 on Linux). The file system acts as the master librarian of your computer. It maintains an organized catalog, known variously as the Master File Table (MFT) in NTFS, inodes in Unix-based systems, or a catalog file in macOS.
When you create a file, several things happen simultaneously behind the scenes:
Data Allocation: The operating system finds a cluster of empty storage space on the drive and writes the actual contents (the payload data) of your file into those sectors or blocks.
Metadata Creation: The file system creates an entry in its master catalog (the MFT or inode table). This entry records critical details about the file, including its name, file extension, creation date, modification date, security permissions, and crucially, pointers (the precise physical addresses or map coordinates telling the system where the file's data blocks are located on the drive).
When you double-click a file icon on your desktop, the operating system does not search the entire drive for the file's contents. Instead, it looks up the file name in the catalog, reads the pointers, jumps directly to the specified storage coordinates, gathers the data blocks, and loads them into your computer's RAM so you can view or edit them.
2. The traditional paradigm: What happens on a Hard Disk Drive (HDD)
For decades, the standard storage medium for computers was the Hard Disk Drive (HDD). Even though SSDs have largely taken over modern laptops and desktops, understanding HDDs is vital because the foundational logic of file deletion was built around their mechanical architecture.
An HDD consists of one or more rigid magnetic disks (platters) that spin at high speeds, accompanied by a read/write head mounted on a moving arm. Data is written to these magnetic platters by altering the magnetic polarity of microscopic domains on the surface.
The Two-Step Deletion process
When you delete a file on an HDD and empty your Recycle Bin, the operating system executes a deceptively simple two-step process:
The Pointer Removal: The operating system goes into the Master File Table (or inode table) and alters the very first character of the file’s name entry, often replacing it with a special hexadecimal flag (such as 0xE5 in older FAT systems) or removing the index link entirely.
The Status Update: The system marks the clusters containing the actual data as "free" or "unallocated space" in its allocation map.
Notice what did not happen in those two steps: The read/write head did not move to the physical location of the file on the spinning platter. It did not emit a magnetic pulse to wipe the binary data. It did not zero-out the sectors.
To the operating system, that space is now officially vacant. If you save a new movie, download a large game, or create a new document tomorrow, the OS is free to write that new data directly on top of the old clusters. Until that exact moment arrives, however, your "deleted" file remains completely intact on the physical disk surface, just waiting to be read.
The forensic reality of HDDs
This mechanism explains why data recovery software is so frequently successful on traditional hard drives. If you accidentally delete a family photo album and have not written massive amounts of new data to the drive since then, a recovery utility can scan the unallocated space, look for the recognizable headers of image files, follow the fragmented blocks, and reconstruct the files perfectly. The data was never truly destroyed; only the directory listing pointing to it was removed.
3. The Solid-State revolution: Flash memory and the TRIM complication
While the "unlinking" model governed computing for decades, the rise of Solid-State Drives (SSDs) introduced a radically different hardware foundation that complicates the concept of file deletion even further.
SSDs do not have moving parts, spinning platters, or magnetic heads. Instead, they rely on NAND flash memory, grids of microscopic transistors traps that store data electronically. Because flash memory operates on entirely different physical principles than magnetic platters, it handles data writes and deletions through a unique set of constraints:
Asymmetry of Operations: In an SSD, data can be read and written in small chunks called pages (typically 4KB to 16KB in size). However, data cannot be overwritten directly. Before new data can be written to a page that already holds old data, that entire larger structure, called an erase block (comprising dozens or hundreds of pages), must be completely erased with a surge of electrical voltage.
Write Endurance and Wear Leveling: Flash memory cells degrade slightly every time they undergo an erase-and-write cycle. To prevent specific areas of the drive from burning out prematurely, SSD controllers use complex algorithms called wear leveling to distribute writes evenly across the entire physical chip.
Enter the TRIM command
Because of these architectural quirks, leaving an SSD to handle deleted files using the old HDD method (just unlinking pointers in the file system) created severe performance degradation. If the OS treated blocks as "free" without telling the SSD controller, the SSD would only discover that blocks were empty when the OS tried to write new data there. This forced the SSD to execute a sluggish read-modify-write-erase cycle on the fly, severely slowing down drive performance.
To solve this, modern operating systems and hardware utilize a command called TRIM.
When you delete a file on a modern operating system running an SSD with TRIM enabled, the OS sends an active notification to the SSD controller: “Hey, the data located in these specific logical block addresses is no longer needed by the user.”
Does TRIM mean secure Deletion?
The introduction of TRIM introduces a fascinating nuance to file permanence:
Background Garbage Collection: Upon receiving a TRIM command, the SSD controller marks those blocks for cleaning. During idle periods, the SSD runs an internal maintenance routine called garbage collection, where it sweeps through those flagged blocks, wipes them clean, and prepares them for future writes.
Immediate vs. Deferred Erasure: Depending on the specific SSD controller firmware, garbage collection may happen almost instantly or may be deferred until the drive requires the space. Consequently, immediately after deleting a file on an SSD with TRIM, the data might be temporarily unreadable or entirely wiped depending on whether garbage collection has already run.
Encryption Layer: Modern SSDs (especially in mobile devices like smartphones and modern laptops) implement hardware-level Full Disk Encryption (FDE). When a file is deleted on an encrypted drive utilizing TRIM, the cryptographic keys or metadata blocks associated with that file are often immediately discarded or invalidated. Without the encryption key, even if the raw physical flash memory cells still hold the scrambled ciphertext bits, the data is mathematically unrecoverable.
Looking Ahead
As we have established in this foundational first part, deleting a file is fundamentally a transaction of permissions and indexing, not an act of immediate physical destruction. Whether dealing with the magnetic inertia of a traditional hard drive or the high-speed flash transistors and background garbage collection of a modern solid-state drive, "deleted" data often lingers in the digital shadows.
In the upcoming second part of this expert analysis, we will explore the practical implications of these mechanisms: how forensic software recovers deleted files, the difference between standard deletion and cryptographic erasure, what happens to deleted files in cloud storage and network shares, and how individuals and organizations can ensure their sensitive data is truly, permanently destroyed beyond recovery.
When you delete a file on a modern operating system, the immediate disappearance of its icon from your desktop or file explorer is largely an illusion of convenience. As explored in the foundational sections of data management, the operating system simply updates its file allocation table or master file table, marking the clusters or blocks occupied by that file as "available" or "free" space. Until new data overwrites those specific sectors, the original binary sequences remain physically intact on the storage medium.
To truly understand whether deletion is permanent, we must examine the diverging architectures of traditional magnetic storage versus modern solid-state drives, the complexities of cloud storage infrastructure, and the specialized forensic techniques used to recover or obliterate data.
The mechanical reality: Hard Disk Drives (HDDs)
On a traditional Hard Disk Drive (HDD), data is stored magnetically on spinning platters coated in ferromagnetic material. Read/write heads float fractions of a micron above these platters, magnetizing microscopic domains to represent ones and zeros.
When a file is deleted on an HDD:
Pointers are Removed: The file system removes the directory entry pointing to the file's clusters.
Space is Reclaimed: The sectors containing the file are added to the file system's free allocation pool.
Data Remains: The actual magnetic charges on the platter remain completely untouched until the operating system happens to write new data into those exact sectors.
Because HDDs write data sequentially or allocate space based on efficiency algorithms (like finding the nearest available free cluster), old files can linger for weeks, months, or even years if the drive has sufficient free capacity. Forensic software can easily scan the raw sectors of an HDD, locate the unreferenced magnetic patterns, and reconstruct files byte-for-byte, provided they haven't been overwritten.
The electronic complexity: Solid-State Drives (SSDs) and flash memory
Solid-State Drives operate on entirely different principles using NAND flash memory chips. Unlike HDDs, SSDs do not have moving parts, and they cannot overwrite data in place.
To write new data to a block of flash memory, an SSD must first erase an entire block, which is a relatively slow and energy-intensive process. To optimize performance and lifespan, SSDs employ sophisticated microcontrollers running Wear Leveling and Garbage Collection algorithms.
Wear Leveling: Spreads write operations evenly across all memory blocks to prevent premature wear of any single section.
Garbage Collection: Periodically background processes sweep through the drive, consolidating valid data into fresh blocks and erasing old blocks that contain obsolete or deleted data.
The role of the TRIM command
To assist garbage collection, modern operating systems use the TRIM command. When you delete a file on an SSD, the OS sends a TRIM signal to the drive's controller, notifying it that those specific logical blocks no longer contain useful data.
Before the next garbage collection cycle runs, the SSD controller knows it can wipe those blocks entirely. However, the exact timing of TRIM execution depends on the operating system, file system, and drive firmware. In some cases, TRIM runs immediately; in others, it is batched for maintenance windows. Consequently, data recovery on SSDs is far more unpredictable than on HDDs: fragments might vanish within seconds due to aggressive background wiping, or they might persist until the next full garbage collection run.
Cloud infrastructure and Multi-Tiered Deletion
When data moves from local hardware to cloud storage providers (such as AWS, Google Cloud, Microsoft Azure, or consumer services like Dropbox and iCloud), the definition of "deletion" becomes even more abstract.
Cloud storage is built on distributed architectures designed for resilience, fault tolerance, and redundancy. When you delete a file in a cloud environment:
Front-End Deletion: The user interface immediately hides the file and revokes your access token.
Replication Layers: Cloud providers replicate data across multiple physical data centers and server racks to protect against hardware failures. Deleting a file requires propagating the deletion command across all replicas, which does not always happen instantaneously.
Object Versioning and Soft Deletes: Many cloud services implement soft deletion by default, retaining "deleted" files in a hidden recycle bin or snapshot tier for 30 to 90 days to protect against accidental user error or ransomware attacks.
Erasure Coding and Chunking: Cloud files are often broken into encrypted chunks, compressed, and distributed across disparate storage nodes with erasure coding parity blocks. True erasure requires garbage-collection sweeps across massive distributed file systems.
Forensic recovery vs. Cryptographic errase
When data must be rendered unrecoverable, standard deletion tools are wholly inadequate. Organizations and individuals dealing with sensitive information rely on rigorous sanitization standards.
1. Software Overwriting (Wiping)
Specialized software utilities (such as DBAN, Eraser, or built-in OS tools) overwrite the target sectors multiple times with randomized patterns of ones and zeros. Standards like the Department of Defense (DoD) 5220.22-M specification or the NIST 800-88 Guidelines for Media Sanitization dictate multi-pass overwriting protocols to ensure that even residual magnetic force variations cannot be read by advanced laboratory equipment.
2. Cryptographic Erasure (Crypto-Shredding)
Modern SSDs and mobile devices encrypt all stored data by default using hardware-based encryption chips (such as AES-256). When you perform a factory reset or cryptographic wipe, the device does not painstakingly overwrite every gigabyte of flash memory. Instead, it securely destroys the master encryption key. Without the key, the underlying ciphertext is rendered permanently unreadable, appearing as pure random noise. This method is exceptionally fast and secure, provided the encryption implementation has no cryptographic backdoors or flaws.
3. Physical Destruction
For high-security environments, software wiping is insufficient. Physical destruction methods include:
Degaussing: Exposing magnetic media to an immensely powerful magnetic field that neutralizes the ferromagnetic alignment of the platters.
Shredding and Crushing: Mechanically grinding HDDs or SSDs into microscopic metallic and silicon fragments, making physical reconstruction impossible.
Conclusion
So, does deleting a file permanently delete it? The short answer is: almost never immediately, and often not at all without deliberate action.
While the digital user interface creates a comforting illusion of instantaneous erasure, underlying file systems, hardware wear-leveling controllers, cloud replication networks, and hidden backups conspire to keep data alive far longer than expected. Understanding the lifecycle of digital data, from the moment a file is created to its ultimate cryptographic or physical destruction, is essential for anyone navigating privacy, data security, and digital forensics in the modern era.