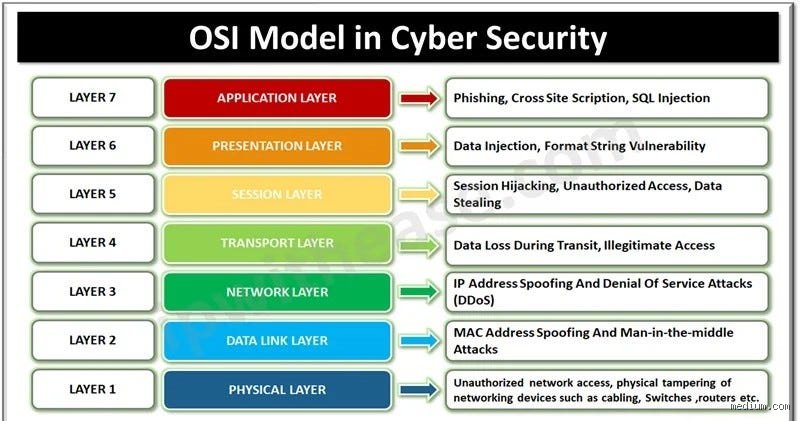
Understanding Layer 4 (Transport Layer) in cybersecurity: Foundations and architecture
For cybersecurity professionals, understanding Layer 4 is vital because it is the exact domain where pivotal network operations—such as session management, port-based traffic filtering, and stateful inspection—take place. Vulnerabilities at this tier can expose infrastructure to devastating cyber threats, including SYN floods, Distributed Denial of Service (DDoS) attacks, port scanning, and session hijacking. This comprehensive guide explores what Layer 4 is, how core protocols operate, its inherent security risks, and how organizations protect this vital segment of the network stack.
Core functions of the Transport Layer
To secure Layer 4 effectively, one must first master its fundamental operational responsibilities. The Transport Layer takes large blocks of data from the upper layers, breaks them down into smaller segments, ensures they reach their destination accurately, and reassembles them before passing them up the stack.
Segmentation and Reassembly: Applications rarely send data in neat little packets. Layer 4 slices incoming application data streams into manageable chunks called segments (in TCP) or datagrams (in UDP) to fit the Maximum Transmission Unit (MTU) constraints of the underlying network. Upon arrival, the receiving transport layer reassembles them into the original message sequence.
Flow Control: To prevent a fast transmitting host from overwhelming a slower receiver with data it cannot process, Layer 4 employs flow control mechanisms (such as sliding window protocols). This regulates the volume and velocity of data traffic, maintaining optimal network throughput.
Error Control and Reliability: Certain Layer 4 protocols guarantee that data is delivered completely and without corruption. If a segment is dropped or corrupted during transit, error-detection mechanisms trigger automated retransmissions.
Process-Level Addressing (Port Numbers): While Layer 3 (Network Layer) uses IP addresses to route data to the correct physical machine, Layer 4 uses ports (ranging from 0 to 65,535) to route data to the exact software application or service running on that machine. For instance, web traffic defaults to Port 443 (HTTPS), while secure shell access uses Port 22 (SSH).
The titans of Layer 4: TCP vs. UDP
Two primary protocols dominate Layer 4 traffic, each presenting distinct architectural advantages and security considerations:
1. Transmission Control Protocol (TCP)
TCP is a connection-oriented protocol designed to guarantee reliable, ordered delivery of data. Before any application data can flow, TCP establishes a synchronization state using a famous mechanism known as the three-way handshake:
SYN (Synchronize): The client sends a segment with the SYN flag set to initiate a connection.
SYN-ACK (Synchronize-Acknowledgment): The server responds with a segment acknowledging the request and signaling its own readiness.
ACK (Acknowledgment): The client sends a final acknowledgment back to the server, establishing the active session.
While this design ensures high integrity and error recovery, it also introduces a massive footprint for stateful tracking, making TCP a frequent target for connection-exhaustion attacks.
2. User Datagram Protocol (UDP)
Unlike TCP, UDP is a connectionless protocol. It fires datagrams off to a destination port without performing a handshake, verifying readiness, or tracking delivery confirmation. This lightweight design prioritizes speed and low latency over reliability, making it the preferred choice for real-time applications like VoIP (Voice over IP), video streaming, and online gaming. From a security standpoint, UDP's lack of state tracking makes it exceptionally vulnerable to reflection and volumetric amplification attacks.
Major cybersecurity threats targeting Layer 4
Because Layer 4 sits at the intersection of network transmission and application processing, it is a prime target for malicious actors looking to disrupt services or bypass perimeter defenses.
SYN flood attacks
A classic volumetric DDoS attack, the SYN flood exploits the TCP three-way handshake. An attacker floods a target server with thousands of spoofed SYN requests. The server obligates memory and resources to open half-open connections, waiting for the final ACK that never arrives. This exhausts the server's connection table, rendering it unable to handle legitimate user traffic.
Port scanning and reconnaissance
Attackers frequently use tools like Nmap to scan Layer 4 port ranges (0–65,535) on target infrastructure. By observing how ports respond (e.g., open, closed, filtered), malicious actors map out the active services, operating system versions, and potential entry points for future exploits.
Session Hijacking
Because TCP sessions rely on sequence numbers to track data streams, advanced attackers can attempt to guess or predict these numbers to inject malicious payloads into an active connection between a client and a server, bypassing authentication gates entirely.
Securing the Transport Layer: Best practices
Hardening Layer 4 requires a combination of network controls, stateful inspection, and proactive monitoring:
Stateful Firewalls: Deploy stateful packet inspection firewalls that track the context of TCP sessions. Unsolicited packets, malformed headers, or packets that do not align with an established handshake state should be dropped instantly.
SYN Cookies and Rate Limiting: Mitigate SYN flood risks by implementing SYN cookies, which allow servers to respond to connection requests without allocating memory until the handshake is completely verified. Pair this with strict rate-limiting policies on incoming connection rates.
Port Minimization and Hardening: Close all unnecessary ports on public-facing servers. Run regular internal and external vulnerability scans to detect rogue services running on non-standard ports.
Transport Layer Security (TLS): While technically operating above Layer 4, implementing TLS encryption directly on top of TCP wraps transport-layer streams in cryptographic protection, safeguarding data from eavesdropping and tampering as it moves across networks.
---Understanding Layer 4 transport layer protocols
This video provides a helpful visual breakdown of how Layer 4 handles data transport and session management within network models.
...Securing this foundational tier demands a shift from simple packet filtering to context-aware traffic inspection. Because Layer 4 governs end-to-end communication sessions, defense mechanisms must track the actual state of every network connection passing through the perimeter.
Stateful inspection and Layer 4 Firewalls
Traditional Layer 3 firewalls evaluate packets individually, inspecting source and destination IP addresses without context regarding preceding or succeeding packets. This static approach leaves networks vulnerable to spoofing and unauthorized inbound traffic that mimics legitimate responses.
Layer 4 firewalls introduce stateful packet inspection, maintaining a dynamic connection state table. When a client initiates a connection using the TCP three-way handshake, the firewall records the source IP, destination IP, source port, destination port, and sequence numbers. Subsequent packets belonging to that exact session are cross-referenced against this table. If an incoming packet arrives without a matching entry in the state table, the firewall drops it immediately, blocking unsolicited connection attempts.
This tracking capability prevents attackers from bypassing network boundaries with arbitrary packets. However, maintaining millions of simultaneous state entries creates its own operational challenge: memory exhaustion. Malicious actors exploit this architectural constraint through targeted resource-consumption attacks designed to saturate the firewall's connection table.
Primary Transport Layer vulnerabilities and attack vectors
Because Layer 4 protocols prioritize reliable delivery and speed, they contain inherent design characteristics that adversaries weaponize. Understanding these attack vectors is essential for building resilient network architectures.
1. SYN floods and resource exhaustion
The TCP three-way handshake requires the server to allocate memory for a half-open connection queue upon receiving an initial SYN packet. An attacker initiates a SYN flood by generating thousands of spoofed SYN requests from unreachable IP addresses. The server responds with SYN-ACK packets and waits for the final ACK response, which never arrives. The half-open connection queue fills rapidly, exhausting available memory and preventing legitimate users from establishing connections.
2. UDP amplification attacks
Unlike connection-oriented TCP, User Datagram Protocol (UDP) is stateless and connectionless. It performs no handshake, meaning packets can be sent to a receiver without prior verification. Attackers exploit this by sending small spoofed UDP requests to vulnerable services (such as DNS, NTP, or SNMP servers) with a forged source IP matching the victim's address. The servers respond with massive data payloads, amplifying the original traffic volume and overwhelming the target's network bandwidth at Layer 4.
3. Port scanning and Service enumeration
Before launching an application-layer exploit, attackers probe Layer 4 to map active services. Using tools like Nmap, scanning utilities transmit crafted TCP or UDP packets, such as SYN, FIN, or NULL scans, to every port on a target host. Analyzing the response codes (SYN-ACK versus RST) reveals which ports listen for incoming connections, exposing unmanaged administrative interfaces, legacy databases, or misconfigured services.
Hardening and mitigation strategies
Defending Layer 4 requires a combination of algorithmic defenses, protocol tuning, and hardware-accelerated traffic scrubbing.
SYN Cookies: To defeat SYN floods, modern operating systems implement SYN cookies. Instead of allocating memory for a half-open connection, the server encodes connection parameters into the initial sequence number sent within the SYN-ACK packet. The server allocates no resources until the client returns a valid ACK containing that cryptographic token, neutralizing memory exhaustion attacks.
Rate Limiting and Traffic Shaping: Administrators configure edge routers and firewalls to enforce strict rate limits on connection establishment rates per source IP. Sudden spikes in half-open connections or anomalous UDP volume trigger automated mitigation rules that drop suspicious packets before they reach core internal infrastructure.
Port Knocking and Stealth Configurations: To protect administrative ports (like SSH on port 22), administrators employ port knocking. The firewall drops all traffic by default until a specific, predetermined sequence of connection attempts across multiple ports occurs from a client IP, dynamically opening access for that specific host.
The modern evolution: Transport Layer Security and QUIC
The traditional boundary between Layer 4 and higher layers continues to blur. Historically, Transport Layer Security (TLS) operated as a separate session layer sitting directly above TCP, adding encryption after the transport connection had already been established in the clear.
Modern networking standards reshape this relationship. The QUIC protocol, developed by Google and standardized by the IETF, integrates transport and cryptographic security directly into UDP. By merging connection establishment, multiplexing, and cryptographic handshakes into a single round trip, QUIC eliminates head-of-line blocking while cryptographically binding the transport session parameters. This shift ensures that Layer 4 attributes, such as connection identifiers and packet numbers, are heavily protected against pervasive monitoring and tampering by intermediate network nodes.
Securing Layer 4 remains an ongoing priority for enterprise security teams. As cloud adoption, microservices, and high-frequency communication protocols expand modern network topologies, maintaining strict state tracking, aggressive anomaly detection, and robust transport-layer hardening ensures that the critical bridge between network routing and application logic stays resilient against evolving threats.