Understanding the core architecture and historical context of security models
Evolution from perimeter defense to Defense-In-Depth
Back in 1994, corporate networks resembled medieval castles with thick stone walls and a single drawbridge. Perimeter-only strategies crumbled the moment remote access protocols arrived on the scene. We are far from those naive architectures today, yet legacy mindsets persist in surprising ways. Specialists don't agree on whether perimeter security is completely dead, but it's unclear why anyone relies on a single wall anymore. As a result, security leaders must adopt overlapping safeguards that catch attackers if one layer fails entirely.
The psychology behind Multi-Layered protection mechanisms
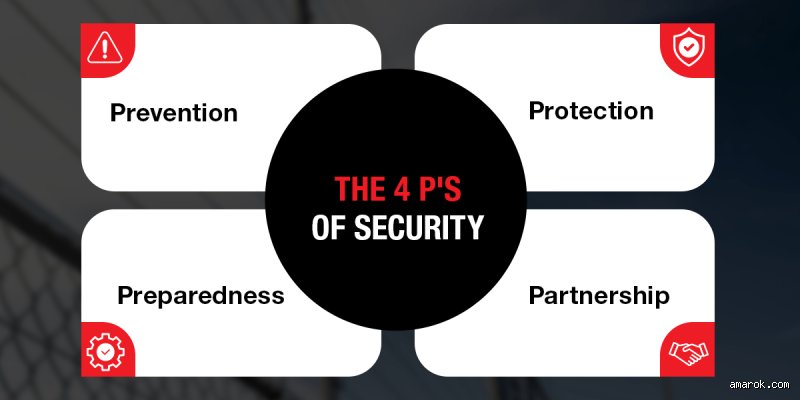
Human error causes over 80 percent of data breaches according to recent industry telemetry. Technology alone cannot fix a careless employee clicking a phishing link on a Tuesday morning. So the four ps of security weave human behavior directly into the hardware and software matrix. That's why modern chief information security officers spend massive budgets on cognitive conditioning alongside encryption tools.
Deconstructing physical and personnel safeguards in enterprise environments
Physical security controls and hardware hardening
Locks, cameras, and biometric turnstiles form the tangible barrier keeping unauthorized bodies away from sensitive server racks. In July 2018, a major financial institution in London suffered a hardware tampering incident because a visitor badge was left unattended for 45 minutes. That changes a lot about how facility managers view guest logs. Still, physical intrusion remains vastly underestimated by software-focused engineers who stare at terminal screens all day. The issue remains: if an attacker touches the motherboard, your 4096-bit encryption keys mean absolute zero.
Personnel security and insider threat mitigation
Screening candidates before handing over root privileges is tedious, expensive, and completely non-negotiable. Background checks, continuous monitoring, and strict clearance levels act as internal filters against malicious insiders. But when a trusted sysadmin goes rogue—like the infamous 2013 contractor leaks in unauthorized data dissemination—the damage strikes from the inside out. Because trust is inherently fragile, organizations implement the principle of least privilege across every department. (Did we really expect blind loyalty to substitute for proper access controls?)
Common misconceptions
Assuming perimeter equals protection
Many organizations believe that buying an expensive firewall solves every threat vector instantly. Yet, this static mindset ignores insider threats entirely. The real issue is that attackers bypass strong walls through hijacked credentials daily. If you lock the front door while leaving the windows wide open, what happens next? Network security fails because defenders focus solely on outer boundaries instead of internal segmentation.
Treating security as a software purchase
Another dangerous trap involves throwing budget at shiny tools without clear policies. That's the reason 60% of data breaches stem from human error rather than sophisticated zero-day exploits. Software cannot fix sloppy habits. As a result, information security degrades when employees reuse passwords across corporate and personal accounts.
Neglecting physical access controls
People often forget that digital safety relies heavily on tangible barriers. Still, a hacker with a rubber ducky payload can compromise a server room in under 30 seconds if doors remain unlocked. (Physical vulnerability is often the weakest link in any defense strategy.) You must secure hardware just as aggressively as cloud databases.
A detail worth knowing
The psychology of social engineering defense
Technical controls mean nothing if your team falls for basic manipulation. Insiders remain the primary target for malicious actors seeking entry. Training programs usually fail because they rely on boring compliance videos instead of realistic simulation drills. Security awareness training needs to change from an annual chore into an engaging, ongoing culture of skepticism. To fix this, security leaders must gamify phishing tests and reward employees who successfully spot anomalies.
Frequently asked questions
How much do companies typically lose during a security breach?
Recent data indicates that the global average cost of a data breach reached 4.45 million dollars in recent tracking cycles. Recovery expenses often include legal fees, regulatory fines, and extensive customer notification processes. Smaller businesses suffer even worse fates, with roughly 60% closing their doors within six months of a major cyberattack. Security measures act as financial insurance against these catastrophic losses.
What is the difference between physical security and digital protection?
Physical protection safeguards tangible assets like buildings, servers, and personnel from theft or damage. Digital protection shields intangible data, networks, and applications from unauthorized cyber interference. Both domains overlap heavily when unauthorized individuals walk into offices to plug rogue devices directly into local area networks. Physical security forms the bedrock upon which all digital safety relies.
How often should security policies be updated?
Industry standards recommend reviewing core security frameworks at least once every quarter. Threat landscapes evolve rapidly, meaning policies written two years ago are completely obsolete today. Organizations must adapt to emerging vectors like automated AI-driven phishing campaigns and advanced persistent threats. Regular audits ensure that risk management strategies match the current threat reality.
Where this leaves you
The pursuit of absolute safety is an illusion that drains resources and breeds dangerous overconfidence. Organizations must shift away from passive compliance toward active, adaptive resilience across every domain. If you refuse to evolve your defenses alongside modern threats, total failure is only a matter of time. The four P's provide a structured compass, yet human vigilance remains the ultimate differentiator in the digital wilderness. Stop treating protection as an IT checkbox and start treating it as a core survival instinct.