Introduction: Protecting Your Digital Hub
In the modern digital landscape, a single Google Account is much more than just an email inbox. It serves as the master key to your digital life—bridging your documents in Google Drive, personal memories in Google Photos, financial information in Google Pay, communication history in Gmail, and often serving as the single sign-on credential for dozens of external third-party websites and applications. Because of this central role, a compromised Google Account can have cascading, severe consequences for your personal privacy, data security, and financial well-being.
Detecting unauthorized access early is your strongest line of defense against identity theft, data loss, and malicious exploitation. Cybercriminals continually deploy sophisticated phishing schemes, credential-stuffing attacks, and automated malware to siphon user credentials. Fortunately, Google provides robust, built-in diagnostic and monitoring tools designed to help you audit your account integrity.
This comprehensive first part of our expert guide walks you through the foundational steps of identifying warning signs, performing official security checkups, and analyzing device access logs to ensure your Google Account remains entirely under your control.
1. Recognizing the Early Warning Signs of Compromise
Before diving into manual settings and security dashboards, it is vital to understand the behavioral and environmental red flags that indicate someone else might be accessing your Google Account.
Keep a vigilant eye out for the following anomalous behaviors:
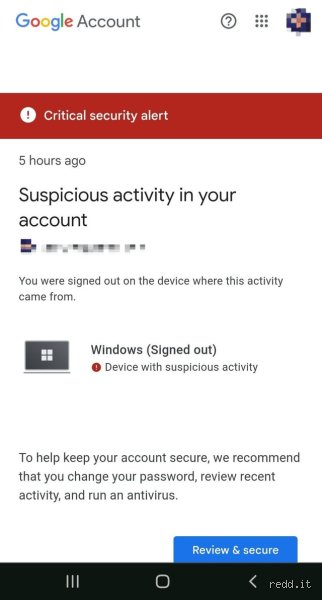
Unfamiliar Activity Notifications: Google continuously monitors sign-in attempts for anomalies such as unusual geographic locations, unrecognized devices, or strange IP addresses. If you receive security alerts via your recovery email or phone number warning you of a new login, never ignore them.
Discrepancies in Sent Items: Finding emails in your Gmail "Sent" folder that you never wrote, or receiving bounce-back notifications for messages you didn't dispatch, strongly indicates that an unauthorized party is using your mail relay.
Missing or Deleted Messages: If important emails are mysteriously absent from your inbox and cannot be found in the Trash folder, a malicious actor may have established automated forwarding rules or data-harvesting scripts to clear their tracks.
Altered Account Settings: Discovering that your recovery phone number, recovery email address, password, or security preferences have been modified without your direct intervention is a critical emergency indicator.
Unrecognized Purchases or Financial Activity: Spotting unfamiliar transactions on Google Pay, unauthorized charges on linked credit cards, or strange app purchases on Google Play point directly to financial exploitation through your account ecosystem.
Altered Content Across Google Services: Finding YouTube videos you did not upload or comments you did not make, altered Blogger posts, or unfamiliar file sharing configurations in Google Drive and Photos are classic signs of a breach.
2. Leveraging the Official Google Security Checkup
The fastest, most comprehensive way to evaluate your account's safety posture is through Google’s native Security Checkup tool. This automated diagnostic suite walks you through a step-by-step review of your connected devices, recent security events, and account recovery options.
How to Access and Run the Security Checkup:
Navigate to your browser and go to your Google Account management page at
myaccount.google.com.In the left-hand navigation menu or on the main welcome dashboard, select Security.
Locate and click on the Security Checkup panel (alternatively, you can visit
[myaccount.google.com/intro/security-checkup](directly).The diagnostic tool will automatically analyze your account and present a categorized breakdown of potential vulnerabilities, green-lighting secure areas while highlighting fields that require your immediate attention.
Key Sections Evaluated During the Checkup:
Your Devices: A visual inventory of every phone, tablet, laptop, and desktop computer that has signed into your Google Account within the last 28 days.
Recent Security Events: A chronological log tracking critical structural modifications made to your account, such as password changes, recovery method updates, or the addition of 2-Step Verification factors.
Third-Party Access: A roster of external websites, mobile apps, and software services that you have granted permission to access parts of your Google data.
Sign-in & Recovery: Verification that your recovery phone number and backup email address are up to date and fully accessible by you alone.
3. Auditing Connected Devices and Active Sessions
One of the most effective maneuvers in hunting down suspicious activity is scrutinizing the exact hardware and software sessions currently holding active tokens for your account. Even if an attacker no longer has your password, an active session token on an unrecognized device can grant them continuous, uninterrupted access to your data.
Step-by-Step Device Audit:
Go to your Google Account (
myaccount.google.com) and click on Security.Scroll down to the Your devices section and click on Manage all devices.
Carefully examine the comprehensive list of hardware currently or recently signed into your account. Look closely at:
Device Models and Operating Systems: Do you recognize every phone, tablet, and computer listed?
Keep in mind that generic names or unrecognized operating system builds should immediately raise suspicions. Locations and IP Contexts: Note the geographic locations associated with the last sign-in activity. If a device shows an active session in a city, state, or country you have never visited, it warrants immediate action.
Timestamps: Check when the device was last active. An active session on an old laptop you sold years ago or a device left in a public venue represents an open security risk.
Securing Unrecognized or Outdated Devices:
If you spot a device you do not recognize, or an old device you no longer possess, click on it to expand its details:
Click the prominent Sign out button. This instantly revokes the device's authorization token, terminating its active session.
If you suspect the compromise was malicious rather than just an old device left logged in, Google will prompt you to secure your account by changing your password immediately.
This concludes the first part of our guide. In the subsequent sections, we will explore advanced log auditing for Gmail, third-party app permission revocations, and hardening your defense mechanisms with hardware-backed 2-Step Verification.
Inspecting App Permissions and Third-Party Access
Beyond monitoring active hardware sessions, one of the most common vectors for persistent, hidden unauthorized access is through malicious or compromised third-party applications. Over time, many users grant various websites, mobile apps, and browser extensions permissions to view their profile info, read emails, manage Google Drive files, or post on their behalf. If an attacker cannot log into your account directly through a traditional browser session, they may leverage an OAuth token granted to an external app to siphon data continuously without triggering standard login alerts.
To audit and neutralize these connections, navigate to the Security tab of your Google Account and locate the Data sharing with third-party apps & services section. Here, you will find a comprehensive ledger of every application that has been granted varying levels of access to your ecosystem.
Review the Permissions List: Carefully click through each entry. Ask yourself whether you actively use the application and whether its stated purpose justifies the permissions it holds (e.g., a simple PDF converter does not need full administrative control over your Gmail or Google Drive).
Revoke Unrecognized Access: If you spot an app you do not recognize, or one you no longer use, click on it and select Revoke Access.
This immediately invalidates its security tokens, cutting off any background data extraction. Inspect Browser Extensions: Open your web browser (such as Google Chrome) and review installed extensions. Unauthorized or shady extensions can inject scripts that log your keystrokes or hijack active sessions. Remove any extension that looks unfamiliar or hasn't been updated recently.
Deep-Dive Audit of Google Workspace Products
Attackers who manage to breach a Google Account rarely leave it untouched; they frequently target specific Google Workspace services to execute secondary scams, steal personal documents, or establish long-term persistence mechanisms. Conducting product-specific checks ensures that no residual damage or hidden traps remain.
1. Gmail Settings and Filters
Your email inbox is often the master key to your entire digital identity because it is used for password resets across other platforms. A sophisticated intruder will often set up stealthy rules to hide their tracks.
Check Forwarding Rules: Go to Gmail Settings, select See all settings, and open the Forwarding and POP/IMAP tab. Ensure that incoming mail is not being automatically forwarded to an unknown external address.
Examine Filters and Blocked Addresses: Look under the Filters and Blocked Addresses tab. Attackers often create rules that automatically archive, delete, or mark security alert emails from Google as spam so you never notice them.
Inspect Delegation: Check if any other user accounts have been granted delegation access to read and send emails on your behalf.
2. Google Drive and File Sharing
If an unauthorized party gains access, they may harvest sensitive documents, tax forms, or personal photographs stored in the cloud.
Review Trash and Activity: Check your Google Drive Trash bin for mass deletions or unusual file movements. Use the activity pane (the small info icon in Drive) to check if files have been shared or downloaded by unknown entities.
Check Shared Links: Ensure that confidential folders have not been set to "Anyone with the link can view."
3. Financial and Payment Profiles
Compromised accounts are frequently weaponized for fraudulent purchases, digital advertising campaigns, or unauthorized transactions.
Google Pay and Google Play: Check your transaction history for unfamiliar charges, subscription renewals, or newly linked payment methods (credit cards, debit cards, or bank accounts).
Remove any payment instruments that do not belong to you. Google Ads / AdSense: If you have an advertising or publisher profile, verify that your campaign budgets, billing profiles, and payout destinations haven't been altered to funnel funds to malicious actors.
Immediate Remediation Steps If Compromise Is Confirmed
If your audit reveals unauthorized devices, unexpected login locations, malicious filters, or stolen files, you must act decisively to regain absolute control over your digital perimeter.
Change Your Password Immediately: Create a strong, completely unique passphrase that you have never used on any other website or service. Avoid using easily guessable personal information like birthdays or pet names.
Sign Out Everywhere: When prompted during the password change process, choose the option to Sign out of all other sessions. This forces every single device currently holding an auth token to re-authenticate with your new credentials.
Upgrade Your Two-Step Verification (2SV): If you were only using SMS-based verification, consider upgrading to a more secure physical security key or an authenticator app (like Google Authenticator). SMS codes can be intercepted via SIM-swapping attacks.
Refresh Recovery Options: Verify that your recovery phone number and recovery email address have not been changed by the intruder.
Update them to secure, trusted alternatives. Run a Local System Security Scan: Because account compromises often stem from malware, keyloggers, or info-stealers residing on your personal computer or smartphone, run a comprehensive scan using reputable anti-malware software before logging back in.
By maintaining a routine habit of running Google's built-in Security Checkup, auditing your connected applications, and monitoring critical workspace settings, you can drastically reduce your attack surface and ensure your personal data remains private and secure.