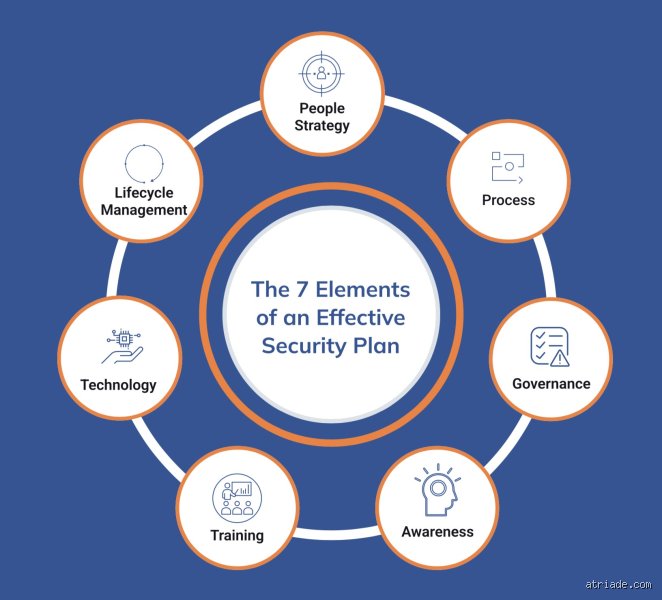
To build an effective, enduring security posture—whether for a sovereign nation, a multinational enterprise, a digital platform, or an individual life, we must look beyond surface-level defenses and examine the core, foundational elements that underpin all robust security frameworks. This first part of our comprehensive expert analysis explores the philosophical underpinnings, the classic triads of information security, risk modeling, and the critical human element that dictates whether security measures succeed or fail.
1. Defining Security in a complex ecosystem
At its core, security is the degree of protection against danger, damage, loss, and criminal activity. Yet, in practice, security is rarely absolute; zero risk is an economic and operational impossibility. Instead, modern security experts define security as a continuous, dynamic state of managed risk, a balance between vulnerability, threat, and mitigation.
When analyzing the essential elements of security, we must evaluate security across four intersecting dimensions:
Physical Security: Safeguarding tangible assets, facilities, equipment, and personnel from physical threats such as unauthorized entry, natural disasters, sabotage, and theft.
Information and Cybersecurity: Protecting digital data, intellectual property, networks, software, and hardware from unauthorized access, modification, disruption, or destruction.
Operational Security (OpSec): The analytical process that denies potential adversaries information about capabilities and intentions by identifying, controlling, and protecting generally unclassified indicators associated with specific operations.
Systemic and Structural Resilience: The capacity of an organization, community, or system to anticipate, absorb, recover from, and adapt to adverse events or systemic shocks.
Understanding these dimensions reveals a vital truth: security is not a static product you purchase and install; it is an ongoing process, a cultural mindset, and an integrated system of interdependent controls.
2. The core Triad: Confidentiality, integrity, and availability (CIA)
While physical security relies on barriers, locks, and guards, information and system security worldwide is anchored by the CIA Triad, the foundational model of information security. Every security policy, technology, and protocol is ultimately designed to uphold at least one of these three pillars.
A. Confidentiality: Protecting data from prying eyes
Confidentiality is the principle that sensitive information should be accessed only by individuals, systems, or processes authorized to do so. A breach of confidentiality occurs when unauthorized entities gain access to restricted data, whether through espionage, phishing, insecure storage, or accidental leakage.
Key Mechanisms: Encryption (at rest and in transit), multi-factor authentication (MFA), role-based access control (RBAC), and strict data-classification policies.
Real-World Application: Ensuring that medical records, financial transactions, or classified state secrets are locked down so that only verified stakeholders can view them.
B. Integrity: Ensuring accuracy and trust
Integrity refers to the accuracy, completeness, and reliability of data and systems. It ensures that information has not been improperly altered, tampered with, or destroyed by unauthorized parties. If data integrity is compromised, decision-makers cannot trust the information they rely on.
Key Mechanisms: Cryptographic hash functions, digital signatures, version control, change management logs, and redundancy checks.
Real-World Application: Preventing a malicious actor from altering the dosage amounts in a hospital's automated drug-dispensing software or modifying financial ledger entries.
C. Availability: Guaranteeing access when needed
Availability is the promise that systems, networks, and data are accessible to authorized users whenever they are needed. A security system that locks out everyone, including legitimate users, fails its availability requirement. Denial-of-Service (DoS) attacks, hardware failures, and power outages are classic threats to availability.
Key Mechanisms: High availability clusters, failover systems, load balancing, geographically distributed data backups, and robust disaster recovery plans.
Real-World Application: Ensuring an e-commerce platform remains operational during peak traffic spikes or that critical emergency services communication networks never experience downtime.
3. Threat modeling and risk management: Anticipating the adversary
Security cannot be reactive; waiting for a breach to occur before building defenses is a recipe for failure. An essential element of any professional security program is proactive risk management and threat modeling.
Risk is calculated using a standard formula:
Risk=Threat×Vulnerability×Impact ext{Risk} = ext{Threat} imes ext{Vulnerability} imes ext{Impact}Risk=Threat×Vulnerability×Impact
To manage risk effectively, security architects must systematically answer four fundamental questions:
What are we trying to protect? (Asset identification and valuation).
What can go wrong? (Threat identification and attack surface mapping).
How likely is it to happen? (Probability and likelihood assessment based on historical intelligence and current threat landscapes).
What are the consequences if it does? (Impact analysis on operational continuity, financial stability, and reputation).
By mapping out threat actors, ranging from opportunistic script kiddies and organized cybercrime syndicates to insider threats and state-sponsored actors, security teams can prioritize resource allocation. Because budgets and time are finite, effective security requires focusing heavy defenses on high-value, high-risk assets rather than attempting to secure everything equally.
4. The human element: The strongest shield and the weakest link
Across every domain of security, whether securing a top-secret military installation or a corporate cloud network, technology, barriers, and policies are ultimately operated by humans. Consequently, human behavior is universally acknowledged as both the greatest vulnerability and the most potent defense mechanism.
No matter how advanced a firewall or biometric lock may be, security can be bypassed instantly if an authorized user is manipulated into handing over their credentials, ignoring a security protocol, or leaving a secure door propped open.
The Psychology of Security
Adversaries frequently exploit human psychology rather than technical flaws through tactics such as:
Social Engineering: Manipulating people into performing actions or divulging confidential information (e.g., pretexting, phishing, and baiting).
Authority Bias: Exploiting the tendency of individuals to comply blindly with perceived figures of authority.
Fatigue and Complacency: When repetitive security tasks lead to burnout, causing users to bypass protocols for the sake of convenience.
Fostering a Security culture
Because human vulnerabilities cannot be patched with software updates, cultivating an organizational security culture is paramount. Essential practices include:
Continuous Education and Training: Moving away from once-a-year compliance checkbox seminars toward dynamic, engaging, and realistic simulations (such as simulated phishing campaigns).
Just-in-Time Assistance: Making secure behaviors easy and frictionless. If a security measure is excessively cumbersome, users will inevitably find workarounds that defeat its purpose.
Blameless Reporting: Encouraging employees to report mistakes or near-misses immediately without fear of punitive retaliation, ensuring swift incident containment.
Looking ahead to Part II
However, defining the core elements is only the beginning.
In Part II of this expert series, we will delve deeper into advanced defensive strategies, exploring zero-trust architecture, incident response lifecycles, automated threat detection, and the future impact of artificial intelligence on both offensive cyber tactics and defensive security paradigms.
Common mistakes to avoid
Making mistakes when starting out is completely normal, but knowing what to look out for saves a lot of time. Most errors happen because people rush through the fundamentals or rely on guesswork instead of checking how things actually work.
Skipping the planning phase
Jumping straight into building without a clear outline usually leads to messy results. You end up having to tear down your own work halfway through just to fix structural issues. Taking ten minutes to map out the pieces beforehand keeps everything aligned and saves hours of backtracking later.
Ignoring basic testing
A lot of people finish a task and assume it works perfectly without checking it on different screens or devices. Small visual bugs or broken elements tend to hide in plain sight until someone else points them out. Running a quick check on a phone and a desktop catches these silly errors before they cause bigger headaches.
Overcomplicating the setup
Trying to use advanced techniques right away almost always slows you down. Beginners often add unnecessary layers or fancy features that make simple tasks way harder than they need to be. Sticking to straightforward methods first builds a solid foundation before you try anything complex.