Decoding the myth of the "unhackable" digital vault: What Password manager has never been breached?
The short, realistic answer requires a nuanced understanding of cybersecurity architecture. In the strict definition of software security, proving a negative is notoriously difficult. No internet-connected infrastructure, commercial enterprise, or open-source project can ever claim absolute immunity to every conceivable zero-day exploit, sophisticated spear-phishing campaign, or state-sponsored attack. However, when security researchers, penetration testers, and privacy advocates look at the historical record, a distinct tier of password managers emerges. Platforms like Bitwarden, 1Password, and Proton Pass have maintained an unblemished record regarding what matters most: zero user vault data has ever been lost, stolen, or decrypted.
To truly understand what it means for a password manager to be "un-hacked," we must look beyond sensationalized media headlines and examine the foundational pillars of modern zero-knowledge security, client-side encryption, and the vital difference between a corporate network security incident and an actual vault compromise.
The anatomy of a Password manager: Why architecture trumps perfection
When evaluating whether a password manager has "never been hacked," security experts immediately draw a sharp line between two entirely separate events:
Infrastructure or corporate network incidents: Situations where attackers gain unauthorized access to a company's internal development systems, support ticketing systems, or cloud storage buckets.
Vault data breaches: Catastrophic scenarios where an attacker manages to steal users' encrypted master vaults and successfully brute-force or decrypt the contents to expose plaintext passwords.
This distinction is crucial. A password manager built on a true zero-knowledge architecture ensures that your master password, your encryption keys, and your unencrypted data never leave your local device. The company hosting the servers, whether it is Bitwarden, 1Password, or another leading provider, literally cannot read your data because they do not possess the mathematical keys required to decrypt it.
Therefore, even in a hypothetical worst-case scenario where an adversary manages to infiltrate a provider's cloud servers and copy every single stored database file, they walk away with digital ciphertexts that look like randomized garbage. Without the user's unique master password, which is hashed locally and never transmitted across the internet, that stolen data remains mathematically impenetrable. This architectural brilliance is why several major password managers have maintained a stellar safety record over decades of operation.
The architecture that defies breaches: Zero-Knowledge vs. Zero-Possession
To truly understand which password managers have maintained an unblemished security record, one must look past marketing slogans and examine the underlying cryptographic architecture. In the cybersecurity industry, a common maxim dictates that there is no such thing as 100% security; there is only risk management. Therefore, asking "Which password manager has never been hacked?" requires nuance. A better question is: "Which providers have structures so robust that even if their servers are compromised, the user's data remains mathematically impenetrable?"
Most mainstream cloud-based password managers operate on a zero-knowledge architecture. Under this model, data is encrypted and decrypted exclusively on the user’s local device using keys derived from a master password. When the encrypted vault is synced to the provider’s cloud servers, the company stores only ciphertext. They do not possess the decryption keys, meaning even if a nation-state actor or cybercriminal breaches the vendor's cloud storage, they walk away with unreadable scrambled text.
However, a newer paradigm, often termed zero-possession or local-first storage (utilized by tools like Enpass), takes security a step further. Instead of storing encrypted vaults on a third-party vendor's central cloud (which forms an attractive "honeypot" for hackers), these managers allow users to sync their vaults through their own personal cloud accounts (such as iCloud, Google Drive, OneDrive, or WebDAV) or keep them strictly offline. In this scenario, a breach of the password manager company's infrastructure yields zero user data, because the company never held the data in the first place.
Examining the track records of industry leaders
When evaluating the major players in the password management landscape, several providers have maintained a clean track record free of major data breaches or unauthorized vault exposures.
1. Bitwarden: The Open-Source standard
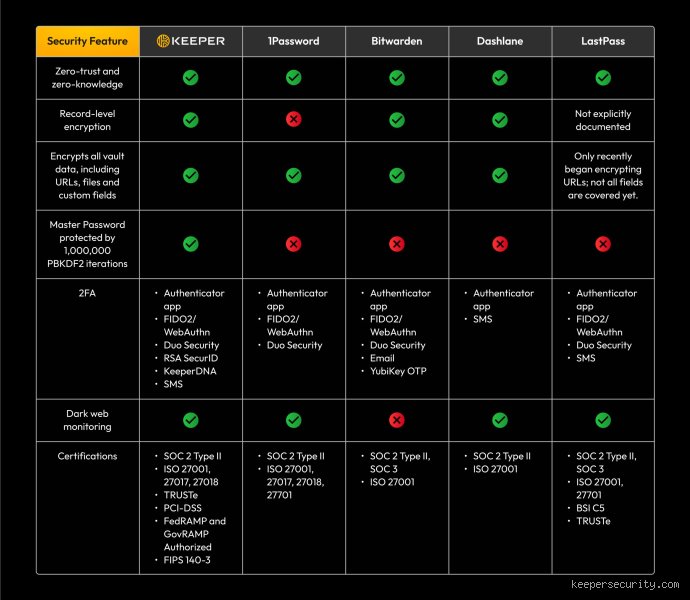
Bitwarden has built an exceptional reputation through transparency. Because its codebase is entirely open-source, security researchers across the globe constantly scrutinize its architecture for vulnerabilities. Bitwarden employs end-to-end AES-256 bit encryption for all data before it leaves the local device.
While Bitwarden has occasionally patched vulnerabilities discovered during routine bug bounties or independent security audits, it has never suffered a catastrophic data breach where user vaults were compromised or exposed. Bitwarden's unique offering allows advanced users to self-host their synchronization server entirely, eliminating reliance on any external cloud infrastructure.
2. 1Password: Defense-in-Depth Pioneer
1Password is widely regarded as the gold standard for enterprise and consumer security, largely due to its introduction of the Secret Key. In addition to a user-chosen master password, 1Password generates a random 128-bit secret key locally on the user's device. This key is combined with the master password to derive the encryption key.
Even if an attacker intercepts a user's master password through a sophisticated keylogger or phishing campaign, they cannot decrypt the vault without that physical device-bound Secret Key. 1Password has never suffered a major breach of its customer data vaults, consistently passing rigorous SOC 2 Type II compliance audits and independent penetration tests.
3. Proton Pass: Privacy-First ecosystem
Backed by the privacy infrastructure of Proton (renowned for ProtonMail and ProtonVPN), Proton Pass entered the market with a heavy emphasis on zero-knowledge encryption and open-source transparency. Proton Pass encrypts not only passwords, but also metadata, such as website URLs, usernames, and custom notes, ensuring that even usage patterns remain obscured. To date, Proton's core security architecture has maintained a pristine record, reinforced by client-side auditing and zero-access encryption keys.
4. Enpass and NordPass: Local control and alternative ciphers
NordPass utilizes the cutting-edge XChaCha20 encryption algorithm instead of traditional AES, offering rapid and secure encryption across mobile and desktop environments. Backed by the security pedigree of Nord Security, NordPass has maintained a secure operational history.
Meanwhile, Enpass's local-first architecture ensures that user vaults reside only where the user dictates. Because Enpass servers do not centralize master databases of user vaults, the company has avoided the systemic vulnerabilities that plague cloud-heavy competitors.
Why open source and Independent Audits matter
In the wake of historical industry failures, most notably the multi-stage security incidents faced by LastPass between 2021 and 2022, which resulted in stolen encrypted vault backups and subsequent offline brute-force attacks against weak user master passwords, consumer trust shifted dramatically. Those events proved that even zero-knowledge encryption can be undermined if an attacker obtains the ciphertext and the user has chosen a weak or predictable master password.
Consequently, modern security experts place little faith in proprietary, "security-through-obscurity" models. The password managers that have successfully avoided security scandals share common operational pillars:
Frequent Independent Third-Party Audits: Reputable firms regularly hire external white-hat hackers to stress-test their infrastructure, browser extensions, and native desktop/mobile apps.
Public Codebases: Open-source transparency allows the global developer community to verify that no backdoors exist within the encryption implementation.
Proactive Bug Bounties: Rewarding external researchers for discovering vulnerabilities before malicious actors can exploit them ensures continuous hardening.
The human element: How "secure" managers still get compromised
A password manager's unblemished server record can be entirely bypassed by poor operational security on the user's end. Statistically, very few password managers are ever truly "hacked" at the server level; instead, individual accounts are compromised through user-facing vectors:
Weak Master Passwords: If a user protects a massive vault of complex passwords with a short, predictable master password (such as a pet's name followed by a birth year), an attacker who steals an encrypted vault file can crack it offline using brute-force GPU clusters.
Infested Endpoints (Malware): If a user's local machine is infected with infostealer malware (such as RedLine or Raccoon Stealer) that captures keystrokes or harvests active session cookies, an attacker can bypass the master password prompt entirely by hijacking an already-authenticated session.
Phishing and Fake Extensions: Users occasionally install malicious browser extensions disguised as legitimate password managers, voluntarily handing over their credentials.
Mitigating these risks requires more than just picking a secure provider; it demands enabling hardware-backed multi-factor authentication (such as FIDO2/WebAuthn YubiKeys), utilizing long passphrase-style master credentials, and maintaining strict device hygiene.
The Final Verdict
When searching for a password manager that has never been hacked, the absolute safest answer lies in choosing providers built upon verifiable zero-knowledge architecture, open-source codebases, and flawless compliance histories, with top recommendations including Bitwarden, 1Password, and Proton Pass.
No software vendor can completely insulate a user from compromised local hardware or a weak master password. However, by selecting a platform that refuses to store unencrypted data, subjects its code to open peer review, and enforces strict zero-knowledge principles, you ensure that even in the worst-case scenario of a corporate network compromise, your digital identity remains locked behind a mathematical fortress that no hacker can open.