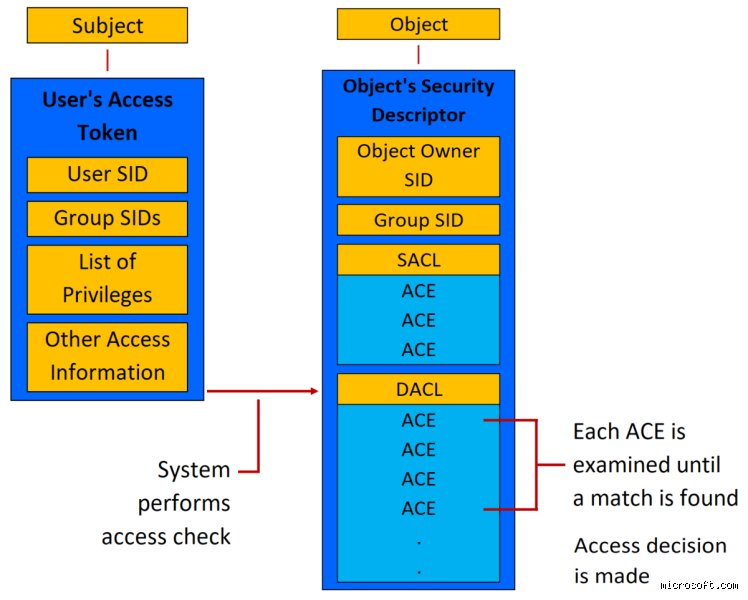
To understand modern Identity and Access Management (IAM), Zero Trust architecture, and least-privilege enforcement, one must first master the principal. This first part of our comprehensive expert series will unpack what a security principal is, explore its various taxonomies, trace its lifecycle across modern IT systems, and analyze why managing non-human principals has become one of the most critical security challenges of our time.
1. Defining the Security principal: Beyond the human User
In colloquial terms, people often use the words "user," "identity," and "principal" interchangeably. However, in rigorous computer science and cybersecurity terminology, these terms have distinct definitions.
A security principal is any entity that can be authenticated by a system and granted permissions to perform actions or access resources.
Breaking down this definition reveals three vital characteristics:
Identifiability: The entity possesses a unique identifier (such as a Username, User ID (UID), Security Identifier (SID), or an Amazon Resource Name (ARN)) that distinguishes it from all other entities within the domain.
Authenticability: The entity can present verifiable proof of its identity (such as a password, cryptographic key, multi-factor token, or digital certificate) so the system knows who (or what) is knocking at the door.
Authorization-Ready: The entity serves as the target or subject to which access control policies, roles, and permissions can be legally attached.
Crucially, a principal is not exclusively human. While a human employee logging into a corporate portal is a classic example of a principal, software applications, virtual machines, serverless functions, database engines, and external API integrations are also principals in their own right. If a system can authenticate it and assign permissions to it, it is a security principal.
2. The taxonomy of Principals: Who (and what) can be one?
To understand how modern authorization engines function, we must categorize the various manifestations of security principals found in enterprise environments.
A. Human Principals (User Principals)
Human principals represent physical people, employees, contractors, partners, or end-users, who interact with systems via graphical user interfaces (GUIs), command-line interfaces (CLIs), or APIs.
Characteristics: High entropy in behavior, prone to social engineering, require credential management (passwords, MFA hardware tokens, biometric verifications).
Security Implications: Humans are often considered the "weakest link" in security chains, making human principals the primary target for credential theft, phishing, and privilege escalation attacks.
B. Non-Human Identities (NHIs) / Service Principals
In modern cloud-native, containerized, and automated architectures, the vast majority of principals are actually non-human. These include:
Service Accounts: Accounts created explicitly for applications or services to run background tasks, connect to databases, or communicate with other internal systems.
Workload Identities: Ephemeral workloads running in containers (like Kubernetes pods) or cloud functions (like AWS Lambda) that require temporary, scoped access to cloud APIs.
Device / Machine Principals: Hardware devices, IoT sensors, or corporate laptops that authenticate directly with a network domain controller or enterprise certificate authority.
Expert Insight: In many modern cloud environments, non-human principals outnumber human principals by a factor of 50 to 1, yet they are frequently under-monitored, suffer from "shadow" administrative rights, and often use static, unrotated secrets like hardcoded API keys.
C. Group Principals
While individual users and services are the actors, groups act as collections of principals designed to simplify administrative overhead.
Instead of assigning read/write access to a shared database bucket for five hundred individual engineering contractors, an administrator creates a group principal called Engineering-Contractors and assigns the permissions to the group.
When a new contractor joins, they are added to the group; when they leave, their membership is revoked. The underlying access control lists (ACLs) remain untouched, drastically reducing configuration drift and permission errors.
3. The lifecycle of a Security principal
A security principal does not exist in a vacuum; it follows a strict lifecycle from inception to decommissioning. Understanding this lifecycle is essential for preventing orphaned accounts and unauthorized lingering access.
[ Provisioning ] ---> [ Authentication ] ---> [ Authorization ] ---> [ Auditing ] ---> [ Deprovisioning ]
1. Provisioning (Creation)
The principal is born. An identity provider (IdP) like Azure Active Directory, Okta, or AWS IAM provisions the principal, assigning it a unique identifier, initial credentials, and default baseline group memberships or permissions.
2. Authentication (Verification)
The principal attempts to interact with a system. The system challenges the principal to prove its identity. Through mechanisms like OAuth, SAML, Kerberos, or mutual TLS (mTLS), the principal presents credentials. If valid, the system issues a session token, ticket, or cryptographic assertion.
3. Authorization (Enforcement)
Once authenticated, the system evaluates the principal’s identity, group memberships, and current context against access control policies to determine whether the principal is allowed to perform a specific action (e.g., DELETE /database/records).
4. Auditing & Monitoring
Throughout its active session, the principal's actions are logged. Security Information and Event Management (SIEM) systems and User and Entity Behavior Analytics (UEBA) monitor the principal for anomalous behavior, such as logging in from an impossible geographic location at 3:00 AM.
5. Deprovisioning (Revocation)
When an employee leaves the company, a project concludes, or a microservice is retired, the principal must be deprovisioned. Failing to do so creates dormant accounts or orphaned credentials, which are prime targets for attackers looking for stealthy, persistent entry points into a network.
4. How systems recognize Principals: Access Control models
When a principal requests access to a protected resource (like a file, an API endpoint, or an encryption key), the operating system or application security layer must evaluate who is asking. Different security models handle principals in unique ways:
Discretionary Access Control (DAC): The owner of a resource decides which principals have access to it (e.g., file permissions in Linux or sharing a document in Google Drive).
Mandatory Access Control (MAC): A centralized authority dictates access based on security clearances and sensitivity labels assigned to both the principal and the resource (commonly used in military and high-security government systems).
Role-Based Access Control (RBAC): Permissions are assigned to specific roles (e.g., Administrator, Auditor, Developer), and principals are assigned to those roles. This decouples the principal from direct permission management.
Attribute-Based Access Control (ABAC): Access is evaluated dynamically based on a rich set of attributes, including characteristics of the principal (e.g., department, clearance level), characteristics of the resource (e.g., classification, project ID), and environmental factors (e.g., time of day, corporate network vs. public Wi-Fi).
5. Modern challenges: The proliferation of Non-Human Principals
As we look toward the remainder of this series, it is impossible to discuss security principals without highlighting the contemporary shift in threat vectors. Traditional security tools were built with human users in mind: enforcing password complexity, deploying multi-factor authentication (MFA), and training employees on phishing awareness.
However, modern cloud architectures rely heavily on machine-to-machine communication. Software pipelines, serverless functions, and third-party SaaS integrations require credentials to operate autonomously. Because these non-human principals cannot easily complete human MFA prompts, organizations often rely on long-lived static secrets, such as API tokens, private keys, and connection strings.
When these non-human principals are over-permissioned (a violation of the Principle of Least Privilege), they become devastating blast radiuses if compromised. An attacker who gains control of an over-privileged service account can quietly traverse an entire cloud infrastructure without tripping standard user-behavior tripwires.
Looking ahead to Part II
We have established what a security principal is, how principals are categorized, and how they interact with modern identity lifecycles and access control systems.
In Part II of this series, we will dive deeper into practical implementation, exploring advanced topics such as cryptographic principal validation in Zero Trust architectures, mitigating privilege creep, managing service account sprawl in Kubernetes and cloud environments, and auditing principal permissions using automated graph-based security analysis.
HTML
<div class="content-section">
Structural integrity and design
Modern web architecture relies on semantic elements to organize information effectively. Proper use of structural tags enhances accessibility and ensures consistent rendering across different viewing environments.
<div class="card-grid">
<div class="card">
Component Design
Modular components allow developers to maintain clean stylesheets and reusable code blocks throughout the development lifecycle.
</div>
<div class="card">
Responsive Grids
Flexible layout systems adapt seamlessly to varying screen dimensions without compromising readability or visual hierarchy.
</div>
</div>
</div>