However, a massive disconnect exists between what happens locally on your personal device and what happens globally across the network infrastructure. If you share a connection with a home network administrator, a landlord, a school IT department, or an office manager, a lingering question often causes anxiety: Can the owner of the WiFi see what I am searching for?
To protect your digital privacy effectively, you first have to understand how data moves from your device, across a wireless router, and out to the wider internet. This first part of our expert guide breaks down the architecture of home and public wireless networks, exposes the myths surrounding private browsing, and examines precisely what a network administrator can—and cannot—see.
1. Local History vs. Network History: Clearing up the confusion
The biggest misconception in modern web browsing is treating "browser history" and "network traffic" as the exact same thing. They are entirely separate entities stored in completely different locations.
Local Browser History: This is the history saved directly on the hard drive or internal storage of the specific device you are holding. If you search for something on Google Chrome, Safari, or Firefox, the application records that text string, the exact timestamp, and the URL link so it can auto-complete your searches later.
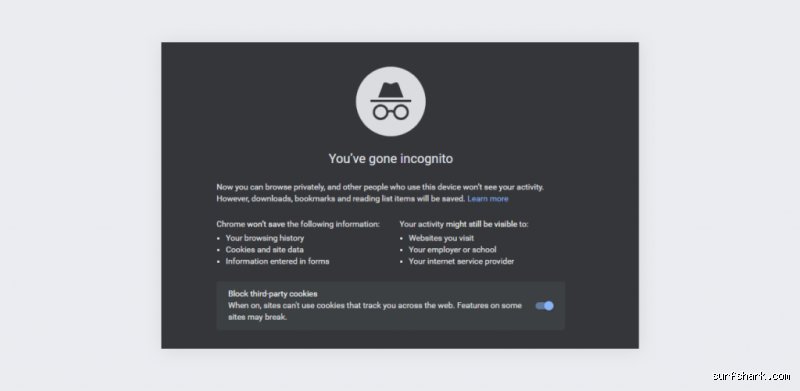
Incognito / Private Mode: When you open a private browsing window, the browser explicitly stops writing these data points to your local storage. Once you close the tab, cookies, temporary files, and local history vanish from that specific machine.
The Catch: Incognito mode is strictly a local feature. It prevents someone who picks up your phone or computer later from seeing what you looked at. It does absolutely nothing to hide your data from the network router, your Internet Service Provider (ISP), or network administrators monitoring the traffic passing through the airwaves.
2. What a WiFi Router can actually see
To understand what data a network owner can extract, you have to look at how a standard home or enterprise router operates. Every piece of data leaving your device must pass through the wireless access point. Depending on how advanced the router is, the administrator has varying degrees of visibility into your habits.
Domain name System (DNS) requests: The open book
Even when a website is heavily encrypted, your device usually has to ask a translator, called a DNS server, where that website lives on the internet. For example, when you want to visit a website, your device asks: "Where is this specific domain located?"
By default, many standard routers handle local DNS routing or log the domain names (e.g., google.com, reddit.com, or any other domain) that connected devices request.
What this means: If a tech-savvy person logs into the router’s administrative dashboard or utilizes local network monitoring software (such as Pi-hole or custom firmware like DD-WRT/OpenWrt), they can typically view a chronological log of the domain names your device connected to, along with timestamps and data transfer volumes.
The power of HTTPS (Secure hypertext transfer protocol)
Fortunately, modern web architecture provides a crucial shield known as TLS/SSL encryption (HTTPS). Decades ago, internet traffic was primarily transmitted in plain text (HTTP), meaning anyone snooping on the local network could use packet-analyzing tools (like Wireshark) to read your exact search queries word-for-word, see what passwords you typed, and read the messages you sent.
Today, nearly all reputable websites utilize HTTPS encryption.
What this means for your searches: When you type a search query into Google, Bing, or any other HTTPS-secured search engine, the connection between your browser and the server is encrypted using a cryptographic tunnel. While the router admin can see that your device is communicating with google.com (via DNS requests and IP routing), they cannot see the actual search terms you typed, the specific articles you read, or the contents of your secure sessions. The granular details inside the website remain completely scrambled to outside observers.
3. Common scenarios: Who is actually watching?
The level of risk to your privacy depends heavily on who owns and manages the network you are connected to:
Home Networks (Parents, Roommates, Landlords): Most standard home routers provided by internet providers have basic, stripped-down administrative interfaces. While an aggressive roommate or parent could theoretically check connected device logs or look at basic traffic routing if they know how to access the router gateway, they rarely see granular search history unless they have installed specialized monitoring software or hardware inspection tools directly on your device.
Work and School Networks: Corporate and educational networks are an entirely different beast. Institutions frequently install enterprise-grade firewalls and mandate the installation of custom security certificates on school- or work-issued devices. This allows network administrators to perform SSL decryption (deep packet inspection), meaning they can intercept and view your web traffic, search queries, and login credentials, regardless of whether HTTPS is active.
(This concludes Part 1 of this guide. In Part 2, we will explore actionable technical strategies, configuration adjustments, and privacy tools, such as encrypted DNS settings and Virtual Private Networks (VPNs), to safeguard your browsing data from local network visibility.)
Advanced Privacy layers: Moving beyond basic settings
When exploring how to safeguard your digital footprint on a shared local network, understanding the boundary between local device storage and network-level packet inspection is crucial. Many users mistakenly believe that clearing a browser's cache or opening an "Incognito" or "Private Browsing" window shields their activity from the router owner. In reality, private browsing only prevents local artifacts, such as cookies, autofill data, and local history logs, from being saved on the physical device itself. It does nothing to stop the Wi-Fi router, network switch, or Internet Service Provider (ISP) from logging the destination domain names of the packets flowing through the air.
To genuinely prevent a network administrator or Wi-Fi owner from viewing the websites and search domains you interact with, you must implement robust encryption and traffic-rerouting strategies. Below is an exhaustive breakdown of the technical methods required to secure your traffic completely, along with an analysis of their strengths and limitations.
1. The gold standard: Deploying a Virtual Private Network (VPN)
The single most effective tool for hiding your search history and browsing activity from a Wi-Fi router is a Virtual Private Network (VPN).
How a VPN protects your traffic
When you connect to the internet without a VPN, your device sends raw domain name system (DNS) requests and web traffic through the local gateway (the Wi-Fi router). Even though modern HTTPS encryption hides the specific paths and search terms within a website, the router can still log the root domain names (e.g., seeing that you connected to google.com or reddit.com).
When you activate a reputable VPN client on your device:
Full Encryption Tunnel: All data leaving your device is encapsulated in an encrypted wrapper using advanced protocols like WireGuard or OpenVPN (typically utilizing AES-256 or ChaCha20 encryption) before it ever hits the Wi-Fi hardware.
Obfuscated Router Visibility: The Wi-Fi router can no longer see individual websites, search queries, or specific destinations. To the router, your device is engaged in a single, opaque data stream communicating exclusively with the remote VPN server's IP address.
Encrypted DNS Resolution: DNS lookups, the process of translating human-readable web addresses into numeric IP addresses, are routed directly through the VPN's private tunnel rather than the local network's DNS server, eliminating DNS sniffing at the router level.
Important caveats for VPN usage
While a VPN hides your traffic from the Wi-Fi owner, it is not a silver bullet for total anonymity:
Account-Level Tracking: If you remain logged into personal accounts (such as Google, Microsoft, or social media platforms), those platforms track your activity at the application layer regardless of your network connection.
Device Monitoring Software: If you are using a corporate or school-issued device equipped with endpoint management or monitoring agents, those programs record activity directly on the hardware before the VPN tunnel encrypts it.
2. Encrypting the metadata layer: DNS-over-HTTPS (DoH)
If installing a VPN is not feasible, addressing the DNS layer provides a vital secondary line of defense. By default, your computer queries your local network or ISP's DNS servers in plain text. This allows network administrators to effortlessly compile a text log of every domain name your device attempts to visit.
Enabling Secure DNS
You can bypass local DNS logging by enabling DNS-over-HTTPS (DoH) or DNS-over-TLS (DoT) directly within your operating system or browser settings. DoH wraps your DNS queries in standard HTTPS encryption, disguising them as regular web browsing traffic.
In Browsers (Chrome, Firefox, Edge): Navigate to settings, locate the Privacy and Security section, find the security settings, and turn on Secure DNS. Select a trusted public resolver (such as Cloudflare 1.1.1.1 or Google 8.8.8.8).
At the Operating System Level (Windows 11 / macOS / Linux): Access your network adapter properties, switch manual DNS server assignments to a trusted public resolver, and enable the DNS-over-HTTPS template option.
Note: While DoH prevents the Wi-Fi router from seeing your DNS queries, it does not hide your ultimate destination IP addresses or encrypt your overall data volume in the way a full VPN does.
3. Enforcing strict transport Security (HTTPS-Only Mode)
Many older or poorly configured websites still fallback to unencrypted HTTP connections, exposing search terms, URL parameters, and page contents to local network sniffing.
To mitigate this risk:
Activate HTTPS-Only Mode: Modern web browsers feature a toggle that forces every connection to upgrade to HTTPS. If a website does not support secure connections, the browser warns you before loading the page.
Preventing Plaintext Leaks: This ensures that even if a network tool is actively capturing packet headers, your search queries and form inputs remain cryptographically scrambled and unreadable.
4. Hardware and Network workarounds
When software-level configurations are restricted or insufficient, physical network isolation offers a straightforward alternative:
Switching to Mobile Cellular Data: The most absolute way to hide activity from a home or public Wi-Fi router is to disconnect from the network entirely and use cellular data (4G/5G). Your cellular provider manages that traffic, entirely bypassing the local router's logs. However, be mindful of data caps and carrier monitoring policies.
Personal Travel Routers / Hotspots: Connecting a personal cellular hotspot or travel router to an untrusted local network creates an isolated subnet, giving you granular control over your encryption protocols.
Summary and best practices
Achieving true privacy on a shared network requires a multi-layered approach:
| Privacy Method | What It Hides from Wi-Fi Router | What It Does NOT Hide |
|---|---|---|
| Incognito Mode | Nothing (local device storage only) | Everything on the network |
| DNS-over-HTTPS (DoH) | Specific domain name lookups | Destination IP addresses and data volume |
| HTTPS-Only Mode | Page content, search terms, and passwords | Root domain names visited |
| Virtual Private Network (VPN) | Everything (complete traffic encryption) | Account logins and device-level software logging |
By deploying a trusted VPN as your primary safeguard, backing it up with secure DNS settings, and maintaining operational security regarding your logged-in accounts, you can effectively ensure that your browsing habits remain private, regardless of who owns or monitors the local network.