The evolving landscape of digital threats
To combat this shifting paradigm, security architects and Chief Information Security Officers (CISOs) must move beyond reactive postures. Relying solely on perimeter defenses like basic firewalls or traditional antivirus software is no longer sufficient when breaches are not just a possibility, but an inevitability. Modern security requires a resilient, multi-layered framework that anticipates attacks, withstands disruptions, and ensures rapid operational continuity.
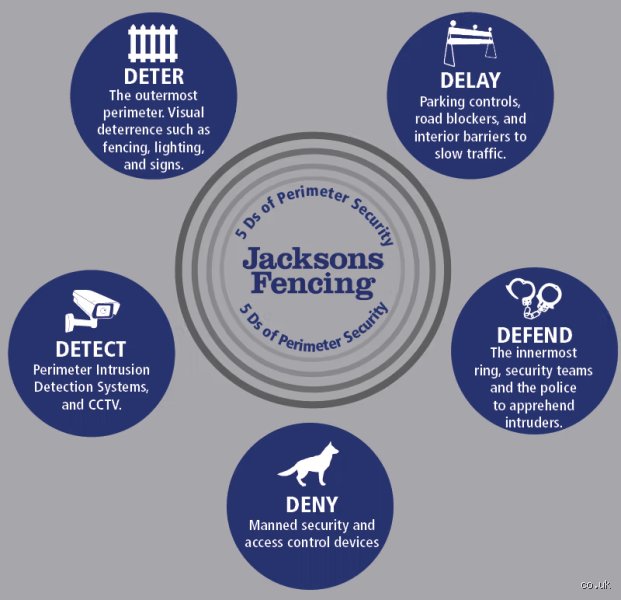
Enter the Five D's of Cybersecurity: Deter, Detect, Delay, Deny, and Disrupt (alongside Defend and Data Protection variations in broader strategic models). This comprehensive framework provides a structured methodology for organizations to design robust security architectures, allocate resources effectively, and neutralize threats at every stage of the cyber kill chain. This first part of our in-depth series explores the foundational concepts of the framework, examining how organizations can proactively safeguard their digital assets.
1. Deter: Raising the cost of entry for cybercriminals
The first pillar of the Five D's is Deterrence. In the physical world, deterrence is represented by high fences, security cameras, and visible guards designed to make a potential burglar think twice before targeting a property. In the digital realm, deterrence involves implementing technical, procedural, and legal hurdles that significantly increase the effort, cost, and risk required for an attacker to successfully compromise a system.
Psychological and technical barriers
Cybercriminals are economically motivated actors seeking the highest return on investment with the least amount of resistance. If a network is difficult to penetrate, adversaries will frequently abandon the target in favor of softer, more vulnerable alternatives. Effective technical deterrence includes:
Strong Authentication Protocols: Mandating multi-factor authentication (MFA) across all enterprise endpoints and cloud services immediately stops credential-stuffing and brute-force attacks in their tracks.
Network Segmentation: Dividing corporate networks into isolated zones ensures that even if an attacker breaches the perimeter, they cannot easily move laterally across the entire infrastructure.
Public Security Posture: Demonstrating compliance with rigorous industry standards such as ISO 27001, SOC 2, or HIPAA signals to potential attackers that an organization maintains active, audited security controls.
Legal and operational Deterrence
Beyond technical safeguards, organizations must leverage legal and operational frameworks to deter malicious behavior. Clearly displaying warning banners on login portals informing unauthorized users that their activity is monitored and will be prosecuted under computer fraud laws establishes legal clarity. Participating in threat intelligence sharing communities demonstrates an active defense posture, signaling to cybercriminal syndicates that the organization is prepared to collaborate with international law enforcement agencies.
2. Detect: The art and science of early identification
No security perimeter is entirely impenetrable. Highly motivated adversaries utilizing zero-day vulnerabilities or sophisticated social engineering techniques will eventually breach initial defenses. Consequently, the second pillar, Detection, is critical. Detection focuses on identifying unauthorized access, anomalous behavior, or active security incidents as early as possible to minimize potential damage and dwell time.
From static signatures to behavioral Analytics
Traditional security tools relied heavily on static signature matching, scanning systems for known malware hashes. However, modern adversaries constantly mutate their code using polymorphic techniques and fileless malware designed to evade signature-based detection. As a result, contemporary detection strategies prioritize behavioral analytics and machine learning:
Security Information and Event Management (SIEM): Centralizing log data from servers, firewalls, and endpoints allows security teams to correlate events across the entire enterprise ecosystem in real time.
Endpoint Detection and Response (EDR) & Extended Detection and Response (XDR): These advanced solutions continuously monitor endpoint activities, capturing process execution, file modifications, and network connections to identify suspicious patterns indicative of malicious intent.
User and Entity Behavior Analytics (UEBA): By establishing a baseline of normal user behavior, UEBA tools can instantly flag anomalies, such as an accountant downloading gigabytes of sensitive source code at 3:00 AM from an unfamiliar geographic location.
Reducing dwell time and alert fatigue
A primary metric for evaluating detection efficacy is dwell time, the duration an attacker remains undetected inside a network. Reducing dwell time from months to minutes prevents data exfiltration and ransomware deployment. However, security analysts frequently suffer from alert fatigue due to high volumes of false positives. Tuning detection engines, leveraging automated triage playbooks, and integrating threat intelligence feeds are essential steps to ensure genuine threats are identified and prioritized without overwhelming security operations center (SOC) personnel.
3. Delay: Buying critical time for incident Response
When an intrusion is detected, every second counts. The third pillar, Delay, encompasses strategies designed to slow down an attacker's progress, impeding their ability to achieve their objectives, such as privilege escalation, data harvesting, or encryption, before security teams can intervene.
Implementing Defense-in-Depth
Delay is achieved through a robust defense-in-depth architecture, where multiple independent layers of security must be breached sequentially. If an attacker bypasses the perimeter firewall, they should immediately encounter internal firewalls, strict role-based access controls (RBAC), database encryption, and monitoring tripwires. Each additional layer forces the adversary to spend more time, energy, and resources, increasing the statistical probability that automated security systems or human analysts will detect and neutralize the threat.
Deception technology and honeypots
A highly effective method of delaying sophisticated adversaries is the deployment of deception technology. By strategically placing honeypots, fake credentials, and decoy databases within the network, organizations create a maze of distractions. When an attacker interacts with a honeypot, the system immediately triggers high-fidelity alerts while simultaneously trapping the adversary in a simulated environment. This not only delays their attack lifecycle but also provides security researchers with invaluable intelligence regarding the attacker's tactics, techniques, and procedures (TTPs).
Summary and outlook for part two
Building a resilient cybersecurity posture requires a holistic approach that seamlessly integrates deterrence, early detection, and strategic delay mechanisms into daily operations. By raising the cost of entry for malicious actors, identifying intrusions before they escalate into catastrophic breaches, and forcing adversaries through a labyrinth of technical obstacles, organizations can drastically reduce their overall risk profile.
In the second part of this comprehensive analysis, we will explore the remaining pillars of the framework, focusing on Denial, Disruption, and the integration of automated response orchestration to complete the modern digital defense lifecycle.
It looks like the beginning of your prompt or the topic of the article got cut off. What is the topic or subject of the article you are writing?