Silicon Semiconductors
Silicon forms the physical foundation of microchips. Manufacturers etch billions of transistors onto a single wafer. Purity in material composition ensures electrical signals travel without distortion or resistance delays.
Instruction Pipelines
Processors break tasks into sequential stages to maximize speed. Fetching, decoding, and executing occur simultaneously across different hardware segments. This parallel flow prevents bottlenecks during intensive computations.
Data storage and retrieval
Information retention requires distinct physical approaches for short-term and permanent needs. Random access memory maintains active application states using capacitive cells that refresh constantly. Solid state drives trap electrons inside floating-gate transistors, preserving files without power.
Volatile memory architecture
Dynamic chips store temporary variables needed by open programs. Speed takes priority over permanence in these components. Power loss immediately clears all contents within these microscopic capacitors.
Non-Volatile flash media
Persistent storage alters physical cell properties to retain data indefinitely. Block management controllers organize clusters efficiently to extend drive longevity. Wear-leveling algorithms distribute write cycles evenly across the entire storage grid.
Type 3: Man-in-the-Middle (MitM) Attacks
A Man-in-the-Middle attack occurs when a malicious actor intercepts communication between two parties. This insertion into a network conversation allows the adversary to eavesdrop, capture sensitive data, or manipulate the traffic flowing between the sender and receiver. Victims often believe they are communicating securely and directly with a legitimate service, such as their online banking portal or a corporate database, unaware that an unauthorized third party is quietly inspecting every packet of data.
Mechanisms of Interception
Attackers execute MitM strategies through various techniques, frequently targeting vulnerable network infrastructure:
Session Hijacking: The attacker steals session tokens or cookies after a user successfully logs into an application, allowing the adversary to impersonate the user without needing their credentials.
IP Spoofing: By altering packet headers, an attacker disguises their computer as a trusted host inside a local area network, tricking routers and switches into forwarding traffic meant for the legitimate device.
Wi-Fi Eavesdropping: Rogue access points set up in public locations (such as coffee shops or airports) mimic legitimate networks. When unsuspecting users connect, all their web traffic routes through the attacker's device.
Real-World impact and prevention
The consequences of a successful MitM attack range from financial theft to corporate espionage. Credentials, personal identifiable information (PII), and proprietary trade secrets frequently leak during these incidents.
Defending against MitM threats requires robust encryption protocols. Transport Layer Security (TLS) ensures that data transmitted between a browser and a web server remains scrambled and unreadable even if intercepted. Organizations and individuals must also utilize Virtual Private Networks (VPNs) when connecting to untrusted public networks, as VPN tunnels encrypt all traffic passing through local routers. Implementing strict certificate pinning and disabling outdated cryptographic algorithms drastically reduces vulnerability windows.
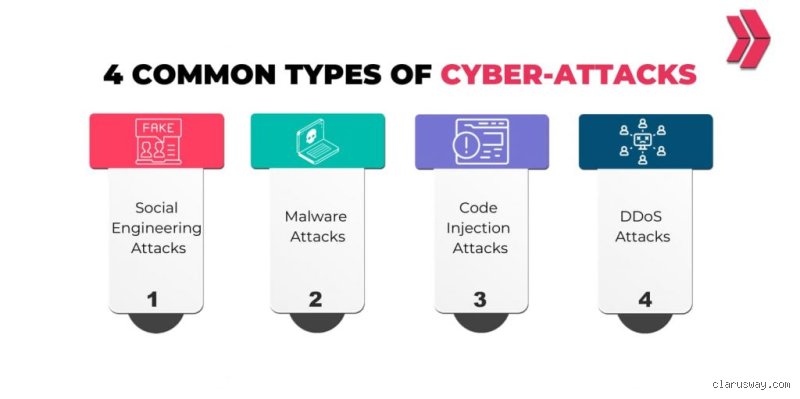
Type 4: Denial of Service (DoS) and Distributed Denial of Service (DDoS) Attacks
While the previous categories focus on data theft, espionage, and unauthorized access, Denial of Service attacks target system availability. A DoS attack overwhelms a target network, server, or application with a massive volume of illegitimate traffic or resource requests, rendering the service unusable for legitimate users. When the attack originates from multiple distributed sources simultaneously—often utilizing compromised networks of infected devices known as botnets—it becomes a Distributed Denial of Service (DDoS) attack.
How DoS and DDoS operators exceed capacity
Web servers, database clusters, and network bandwidth possess finite operational capacities. Attackers exploit these limits using specific tactics:
Volume-Based Floods: Methods like UDP floods and ICMP floods overwhelm the target's network bandwidth with excessive data packets, choking the connection until normal user traffic cannot get through.
Protocol Attacks: SYN floods target connection handshakes, exhausting server memory by leaving half-open TCP connections dangling until the system runs out of resources.
Application Layer Attacks: These sophisticated assaults target specific web application vulnerabilities, such as HTTP floods or slowloris attacks, which consume server resources by sending slow, incomplete HTTP requests that tie up worker threads.
Mitigation and Resilience
Mitigating DDoS incidents demands advanced traffic-filtering solutions and scalable infrastructure. Content Delivery Networks (CDNs) and dedicated DDoS mitigation services (such as Cloudflare or AWS Shield) absorb abnormal traffic spikes by routing incoming requests through global scrubbing centers. These scrubbing centers analyze traffic patterns in real-time, instantly blocking malicious packets while allowing legitimate users uninterrupted access. Organizations also build resilience by provisioning redundant server architecture, implementing rate-limiting policies, and establishing automated incident response runbooks to handle sudden traffic surges.
Comprehensive defense strategies for modern Networks
Protecting enterprise networks and personal devices against these four primary attack vectors requires a layered security posture, commonly referred to as defense-in-depth. Relying on a single security tool leaves systems exposed to sophisticated multi-stage threats.
1. Identity and access management (IAM)
Authentication controls serve as the primary gatekeeper for digital assets. Organizations must enforce Multi-Factor Authentication (MFA) across all employee accounts and administrative portals. Passwords alone remain highly susceptible to credential stuffing and phishing campaigns. Integrating hardware tokens, authenticator apps, or biometric verification drastically raises the barrier for unauthorized intruders.
2. Network segmentation and Zero Trust architecture
Adopting a Zero Trust security model ensures that no user or device receives implicit trust, regardless of whether they reside inside or outside the corporate perimeter. Network segmentation divides infrastructure into isolated zones, preventing lateral movement if an attacker successfully breaches a single endpoint or server. Micro-segmentation policies restrict access permissions strictly to what is required for specific business functions.
3. Continuous patch management and vulnerability assessment
Software vendors frequently release security patches to address newly discovered zero-day exploits and vulnerabilities. Maintaining a rigorous patch management schedule ensures that operating systems, firmware, third-party libraries, and applications remain updated against known vectors. Automated vulnerability scanners assist security teams in identifying misconfigurations and unpatched software before malicious actors exploit them.
4. Employee education and Security awareness
Human error remains one of the largest vulnerabilities in cybersecurity. Regular training programs simulate phishing campaigns, teach staff members how to spot social engineering red flags, and establish clear reporting protocols for suspicious emails or anomalous system behavior. Cultivating an organizational culture of security awareness transforms employees from potential liabilities into active defenders of the network.