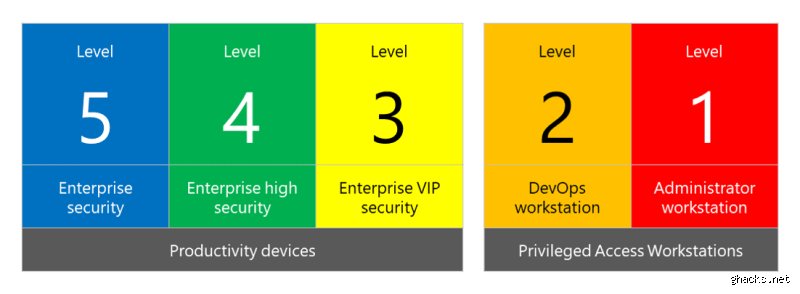
The pinnacle of systemic resilience
Among these elite benchmarks, Level 5 security stands out as the ultimate frontier. Whether evaluated through the lens of process maturity models, advanced hardware-software co-design, or cutting-edge frameworks designed to protect frontier artificial intelligence, Level 5 represents the absolute zenith of security capability. It is a state where security is no longer an overlay or an afterthought, but an immutable, self-optimizing property woven into the very fabric of an organization or technological architecture.
This comprehensive two-part article explores the multi-faceted definition of Level 5 security.
1. Defining "Level 5": Contextualizing the ultimate tier
To understand Level 5 security, one must first recognize that the term is utilized across several advanced technical and operational domains, each sharing a common philosophy: uncompromising resilience against the most capable adversaries under conditions of extreme uncertainty.
A. The Maturity perspective (process optimization)
In classical maturity frameworks—such as the Capability Maturity Model Integration (CMMI) adapted for cybersecurity and software engineering—Level 5 represents Optimizing. At this tier, an organization’s security processes are not merely defined or quantitatively managed; they are continuously improved through both incremental pilot innovations and innovative disruptive technologies. Quantitative performance goals for security are established, continually revised to reflect changing business objectives, and used as criteria in managing process improvement.
B. The Frontier AI and Advanced infrastructure perspective
In newer, specialized security taxonomies, such as those addressing the governance and protection of frontier artificial intelligence models and high-stakes infrastructure (often aligned with frameworks like RAND's Security Level 5 guidelines), Level 5 signifies defenses robust enough to withstand targeted, well-funded nation-state intrusions. This includes protecting massive model weights, specialized training pipelines, and distributed data clusters against sophisticated insider threats, supply chain subversion, and advanced persistent threats (APTs) equipped with zero-day arsenals.
Key Takeaway: Level 5 security is never static. It is a dynamic equilibrium of continuous monitoring, automated adaptation, and absolute cryptographic and physical isolation designed to neutralize elite threat actors.
2. Core pillars of Level 5 Security architecture
Achieving Level 5 status requires a radical departure from conventional IT and security deployment strategies. It demands an architectural philosophy built upon several non-negotiable pillars:
I. Heterogeneous open secure Hardware and Hardware roots of Trust
At lower security levels, systems often trust underlying commercial-off-the-shelf (COTS) hardware components implicitly, assuming firmware and silicon are secure. Level 5 architectures invert this assumption.
Hardware Redundancy: Level 5 systems frequently utilize heterogeneous open secure hardware connected via redundant pathways. This ensures that even if a flaw or backdoor is discovered in one silicon architecture or instruction set, independent hardware barriers mitigate catastrophic failure.
Verifiable Provenance: Every piece of hardware, firmware update, and boot sequence must possess cryptographic provenance, ensuring that the hardware running critical workloads has not been tampered with physically or logically during transit or manufacturing.
II. Algorithmic Zero-Trust and Automated Real-Time enforcement
While "Zero Trust" has become an industry buzzword, Level 5 implementation goes far beyond identity-and-access management (IAM) tools.
Continuous Verification: Every transaction, API call, and memory access request is evaluated in real time based on dynamic contextual risk scoring.
Active Blocking and Proactive Interdiction: Level 5 frameworks do not merely log and alert upon anomalous behavior; they execute active blocking protocols instantly. For instance, in advanced API and network security metrics, Level 5 denotes real-time inspection engines that intercept and neutralize malicious payloads before they can execute code or exfiltrate data.
III. The principle of radical compartmentalization and least privilege
In a Level 5 environment, blast radiuses are mathematically constrained. No single user, administrator, process, or microservice possesses universal privileges.
Systems operate on strict, cryptographically enforced multi-level security (MLS) policies.
Lateral movement within a network or cluster is rendered virtually impossible through automated micro-segmentation and ephemeral compute instances that vanish or rotate continuously.
3. The modern threat landscape driving the need for Level 5
Why are organizations, governments, and AI labs pushing toward the immense complexity of Level 5 security? The answer lies in the dramatic evolution of modern cyber adversaries.
+-------------------------------------------------------------+
| THE ESCALATING THREAT SPECTRUM |
+-------------------------------------------------------------+
| Level 1-2: Automated Scanners & Script Kiddies |
| Level 3: Organized Cybercrime & Ransomware Syndicates |
| Level 4: Advanced Persistent Threats (APTs) & Espionage |
| Level 5: State-Sponsored Campaigns & Frontier AI Attacks |
+-------------------------------------------------------------+
As illustrated above, lower security tiers are generally sufficient to thwart automated malware, opportunistic cybercriminals, and basic script kiddies. However, as enterprises transition into storing massive repositories of sensitive user data, training multi-billion-parameter artificial intelligence models, and managing critical national infrastructure, they enter the crosshairs of Level 4 and Level 5 adversaries.
Nation-state actors and sophisticated syndicate groups possess deep financial resources, custom malware development teams, quantum-computing decryption horizons, and infinite patience. They utilize living-off-the-land techniques, blend in with legitimate administrative traffic, and exploit subtle flaws in software supply chains. Against these adversaries, a standard firewall or an isolated patch management routine is utterly inadequate. Level 5 security is the direct response to this asymmetric warfare, establishing a defensive posture that makes successful intrusion economically and technically prohibitive for even the most well-resourced attackers.
4. Operationalizing Level 5: Cultural and human capital realities
Technology and architecture alone cannot achieve Level 5 security maturity. The human element remains both the greatest vulnerability and the most vital line of defense.
An organization operating at Level 5 embeds security culture into every operational layer:
Rigorous Vetting and Continuous Evaluation: Personnel with access to Level 5 assets undergo stringent, continuous background checks and multi-factor behavioral monitoring to mitigate insider threats.
Blameless Post-Mortems and Red Teaming: Level 5 entities routinely subject their own infrastructure to aggressive, unannounced red-team attacks conducted by elite internal or external adversaries. Every vulnerability discovered is treated as a systemic failure of the engineering lifecycle rather than an isolated incident.
Friction vs. Security Balance: A major challenge at Level 5 is maintaining developer velocity and user experience without compromising security invariants. Organizations must build sophisticated developer tooling that automates security compliance, ensuring that writing secure code is frictionless while bypassing security controls is technically impossible.
Looking ahead to part two
We have established that Level 5 security is not merely a product or a certificate, but a holistic ecosystem of rigorous hardware trust, real-time automated defense, process maturity, and uncompromising organizational culture.
In the second part of this expert analysis, we will dive deeper into the practical implementation roadmap, exploring how organizations can audit their current posture, bridge the gap from intermediate tiers to Level 5, and manage the complex trade-offs between system performance, cost, and absolute security assurance.
Implementing Level 5 Security: Architectural blueprint and protocols
Moving an enterprise ecosystem or a specialized high-assurance infrastructure to a Level 5 security posture requires a paradigm shift from reactive defense to proactive, mathematically validated resilience. At this elite tier, standard perimeter defenses and heuristic-based monitoring are insufficient. Organizations must deploy integrated, multi-layered control stacks that can withstand persistent, sophisticated adversaries.
Core technical pillars of Level 5 architecture
To achieve and maintain a Level 5 operating standard, systems must be built upon rigid engineering and cryptographic principles:
Zero-Trust Execution Spaces: Complete abandonment of implicit trust zones. Every microservice, user session, and hardware component must continuously authenticate and authorize its state before data exchange occurs.
Heterogeneous Hardware Redundancy: Utilizing diverse, open, secure hardware roots of trust to prevent single points of systemic hardware failure or widespread supply chain compromise.
Advanced Cryptographic Enforced Isolation: Implementation of hardware-backed encryption keys and isolated memory enclaves that protect sensitive assets, such as model weights, high-value intellectual property, or mission-critical unclassified data, even if the host operating system is partially compromised.
Continuous Automated Attestation: Real-time verification of boot integrity, runtime memory states, and network routing tables against immutable baselines.
Operational Governance and compliance frameworks
Achieving technical excellence at Level 5 is only half the battle; institutional governance must mirror the rigorous technical controls. Organizations operating at this level are subjected to meticulous regulatory and operational oversight.
| Governance Domain | Level 5 Requirement | Operational Impact |
|---|---|---|
| Identity & Access Management | Multi-factor cryptographic identity with strict least-privilege enforcement. | Eliminates reliance on static passwords; restricts lateral movement entirely. |
| Supply Chain Verification | Comprehensive provenance tracking using secure hardware standards and NIST guidelines. | Ensures zero hardware or software tampering from origin to deployment. |
| Incident Response & Recovery | Automated containment protocols backed by resilient business continuity planning. | Reduces containment timeframes from hours to milliseconds, mitigating catastrophic failure. |
Strategic value and future outlook
The adoption of Level 5 security frameworks is rapidly expanding beyond defense agencies into commercial sectors handling critical societal infrastructure, frontier artificial intelligence development, and sensitive mass-scale data processing.
As interconnected systems grow more complex, the economic and operational fallout of a security breach scales exponentially. Organizations that master Level 5 controls safeguard their assets against modern threat actors and establish a trusted foundation for digital innovation. The commitment to this highest tier of security guarantees that operational integrity remains unbroken, preserving user trust and system availability under any operational condition.
How is your team currently evaluating security maturity frameworks, or are you looking at specific compliance standards for your infrastructure?