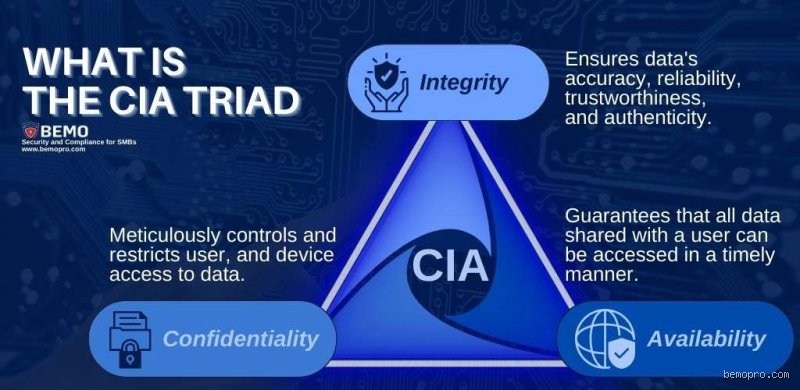
When professionals encounter the acronym "CIA" within the context of information security governance and compliance, they are not referring to the American intelligence agency. Instead, the letters represent three cardinal pillars of security: Confidentiality, Integrity, and Availability. This triad serves as the conceptual blueprint for designing, implementing, and auditing an information security management system (ISMS). Understanding these three pillars in depth is essential for any enterprise seeking to safeguard sensitive intellectual property, comply with international regulations, and maintain the trust of its customer base.
The genesis and significance of the CIA triad in Information Security
The origin of the CIA triad traces back to the early decades of modern computing, evolving organically as computer scientists recognized that data breaches and system failures threatened more than just hardware. As networks expanded and organizations transitioned from paper records to centralized databases, the need for a universal taxonomy of security objectives became apparent. By the time ISO and the International Electrotechnical Commission formalized the ISO/IEC 27001 standard, the triad had solidified into the core baseline for defining security requirements.
Every security control mandated by ISO 27001—whether it involves cryptographic protocols, access control lists, physical security measures, or incident response planning—maps back to one or more of these three dimensions. During a formal risk assessment, security officers evaluate threats and vulnerabilities precisely through the lens of how they might compromise confidentiality, integrity, or availability. If a vulnerability exposes data to unauthorized parties, confidentiality is breached. If data can be altered maliciously or accidentally without detection, integrity is compromised. If authorized users are locked out of critical systems during a ransomware attack, availability is shattered.
Pillar one: Confidentiality
Confidentiality ensures that sensitive information is accessed exclusively by individuals, entities, or processes that possess explicit authorization. In an era marked by sophisticated cyber espionage, insider threats, and pervasive data harvesting, maintaining strict confidentiality is both a technical challenge and a regulatory imperative. Regulations such as the General Data Protection Regulation (GDPR) and the Health Insurance Portability and Accountability Act (HIPAA) heavily penalize organizations that fail to keep personal and proprietary data secure.
Within an ISO 27001-compliant environment, confidentiality is achieved through a multi-layered defense strategy. This includes robust encryption standards for data both at rest (stored on servers, databases, and endpoint devices) and in transit (moving across internal networks or the public internet). Organizations implement the principle of least privilege, ensuring that employees are granted only the minimum level of access necessary to perform their specific job functions. Access controls, multi-factor authentication (MFA), role-based access control (RBAC), and strict data classification policies work in concert to prevent unauthorized disclosure, whether resulting from external cyberattacks or inadvertent human error.
Pillar two: Integrity
While confidentiality focuses on keeping secrets secret, integrity addresses the accuracy, completeness, and reliability of data and systems. Information has little value if it cannot be trusted. If a financial database is subtly manipulated, or if software code is injected with unauthorized modifications during transmission, the resulting operational decisions can be catastrophic.
Integrity encompasses two distinct dimensions: data integrity and system integrity. Data integrity guarantees that information has not been altered, destroyed, or fabricated by unauthorized actors. System integrity ensures that a system performs its intended function in an unimpaired manner, free from unauthorized manipulation. ISO 27001 mandates specific controls to uphold integrity, including cryptographic hash functions, digital signatures, version control systems, change management protocols, and rigorous audit logging. By maintaining comprehensive audit trails, organizations can detect anomalies immediately, identifying precisely when and how data modifications occurred and tracing accountability back to specific users or processes.
Pillar three: Availability
The third pillar of the triad, availability, is often underappreciated until an outage occurs. Availability ensures that authorized users have timely and reliable access to information, systems, and network resources whenever they are needed. A secure system that is inaccessible to its legitimate users is practically useless, failing to meet the operational demands of the business.
Modern threats to availability extend far beyond hardware failures or natural disasters. Distributed Denial of Service (DDoS) attacks, sophisticated ransomware campaigns, and cascading software bugs can bring enterprise infrastructure to a grinding halt. Under ISO 27001 guidelines, achieving high availability requires proactive resilience engineering. This involves deploying redundant system architectures, load balancing, automated failover mechanisms, continuous power supplies, and rigorous backup and disaster recovery (DR) testing. By anticipating potential points of failure and establishing comprehensive business continuity plans, organizations ensure that operational continuity is preserved even in the face of major disruptions.
Deep-Dive: Operationalizing Confidentiality, Integrity, and Availability
Continuing our exploration of the ISO 27001 standard, understanding what the CIA triad stands for, Confidentiality, Integrity, and Availability, is only the first step. The true power of ISO 27001 lies in how it operationalizes these three principles through a systematic Information Security Management System (ISMS). Rather than treating security as a patchwork of technical fixes, ISO 27001 forces organizations to evaluate every piece of information and system asset through the lens of these three pillars.
Let us examine how each pillar translates into daily organizational governance, risk treatment, and control frameworks under the modern ISO 27001:2022 standard.
1. Confidentiality in practice: Beyond access Control
When auditors assess confidentiality within an ISO 27001 framework, they look far beyond simple password policies. Confidentiality is about ensuring that sensitive data is accessible only to those authorized to have access, safeguarding both data at rest, data in transit, and data in processing.
Classification and Labeling: Organizations must classify information based on its sensitivity (e.g., Public, Internal, Confidential, Restricted). This ensures that encryption, masking, and tokenization are applied proportionately.
The Principle of Least Privilege (PoLP): Users, processes, and systems are granted only the minimum necessary permissions required to perform their specific functions. ISO 27001 Annex A controls explicitly mandate rigorous identity and access management (IAM) lifecycles.
Cryptographic Controls: Confidentiality relies heavily on robust encryption standards (such as AES-256 for data at rest and TLS 1.3 for data in transit). ISO 27001 requires a formal cryptographic policy that dictates key management, rotation schedules, and compliance with regulatory standards.
2. Integrity: Ensuring trust and accuracy
Integrity protects the accuracy and completeness of information and processing methods. In an era plagued by sophisticated cyber attacks, supply chain tampering, and insider threats, data that has been silently altered can be just as dangerous as data that has been stolen.
Non-Repudiation and Logging: ISO 27001 requires comprehensive audit trails. If a financial record or configuration file is modified, the system must log who made the change, when it was made, and what was altered. This prevents entities from denying their actions.
Checksums and Version Control: Technical controls such as cryptographic hashing (e.g., SHA-256) ensure that files and software code have not been tampered with or corrupted during transmission or storage.
Input Validation and Error Handling: Application security controls ensure that data entering a database or system meets strict formatting and business logic criteria, preventing injection attacks or accidental corruption by users.
3. Availability: The Often-Overlooked pillar
While confidentiality and integrity often grab headlines during data breaches, availability is critical for operational resilience. If a system is secure and accurate but completely unreachable, the business suffers a catastrophic failure.
Redundancy and High Availability: ISO 27001 mandates robust infrastructure design, including failover clusters, load balancers, and redundant cloud architectures to eliminate single points of failure.
Business Continuity and Disaster Recovery (BCDR): Organizations must establish, maintain, and regularly test BCDR plans. This ensures that even in the event of a ransomware attack, natural disaster, or major hardware failure, critical business operations can resume within acceptable Recovery Time Objectives (RTO) and Recovery Point Objectives (RPO).
Capacity Management: Monitoring resource utilization (CPU, memory, storage, bandwidth) prevents service degradation and sudden outages caused by unexpected traffic spikes or resource exhaustion.
Connecting the CIA triad to ISO 27001 Risk Assessment
The brilliance of ISO 27001 is that it does not dictate a one-size-fits-all security posture. Instead, it uses the CIA triad as the core metric for Risk Assessment.
During the risk assessment phase, an organization identifies its information assets and evaluates them against three security dimensions:
Confidentiality Impact: What is the damage if this data is leaked to competitors or the public?
Integrity Impact: What is the cost if this data is corrupted, manipulated, or falsified?
Availability Impact: What is the financial and reputational loss if this service goes offline for an hour, a day, or a week?
By scoring risks based on these three pillars, organizations can filter through thousands of potential threats and focus their resources where protection is most desperately needed. This risk-driven approach forms the foundation of the Statement of Applicability (SoA), wherein the organization selects from the Annex A controls (such as access control, cryptography, operations security, and incident management) to mitigate identified risks.
Why the CIA triad matters for ISO 27001 compliance
The CIA triad, Confidentiality, Integrity, and Availability, serves as the foundational compass for information security management. When integrated into an ISO 27001-certified ISMS, these three concepts transform from abstract academic principles into rigorous, auditable operational requirements.
Achieving ISO 27001 certification demonstrates to clients, partners, and regulators that an organization does not merely talk about security; it systematically preserves the confidentiality of sensitive data, ensures the unwavering integrity of its processes, and maintains the continuous availability of its services. In today's interconnected digital economy, mastering the CIA triad is not just a compliance checkbox, it is the ultimate competitive advantage and the bedrock of digital trust.