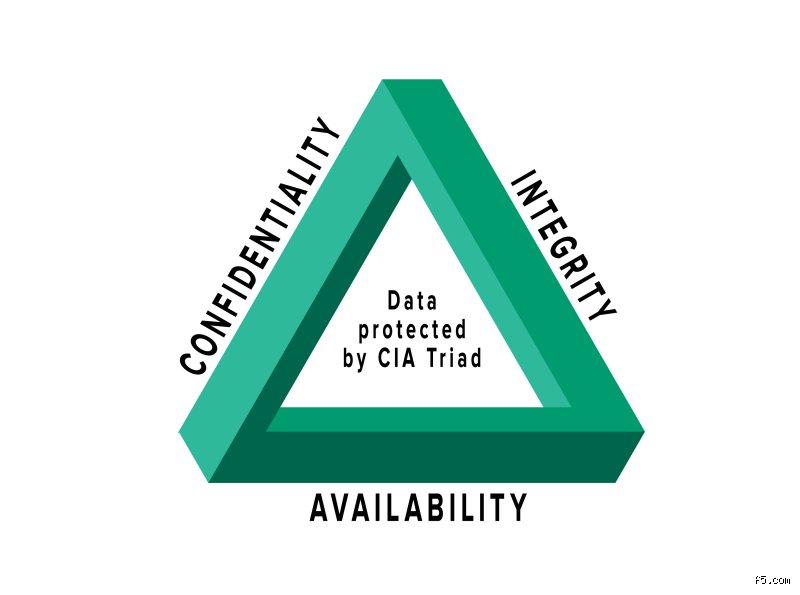
The CIA triad is a three‑principle model that defines the core goals of information security: keeping data secret, ensuring it stays correct, and making sure it is accessible to those who need it.
confidentiality: protecting secrets
Confidentiality means only authorized subjects can read or use data. Encryption, access controls, and strong authentication are common tools. A breach such as the 2013 Target incident shows that compromised credentials can expose millions of records, highlighting the need for robust credential management.
integrity: guaranteeing data accuracy
Integrity involves preserving the trustworthiness of information throughout its lifecycle. Techniques like cryptographic hashes (e.g., SHA‑256) act as digital fingerprints, alerting administrators when a file has been changed. The SolarWinds supply‑chain attack demonstrated how attackers can inject malicious code into trusted software, violating integrity on a massive scale.
availability: keeping services online
Availability ensures that systems, applications, and data are reachable when required. Redundant infrastructure, load balancing, and regular stress testing help mitigate disruptions. Distributed denial‑of‑service attacks, such as the 2016 Mirai botnet incident, illustrate how overwhelming traffic can temporarily knock out even well‑designed services.
applying the triad in modern environments
In cloud platforms, the shared‑responsibility model splits duties: providers secure the underlying hardware and network availability, while customers manage data confidentiality and access permissions. Misconfigured storage buckets remain a common cause of data exposure, reinforcing the need for clear policy enforcement.
common pitfalls and best practices
- Over‑restricting confidentiality can hinder productivity and lead to shadow‑IT workarounds.
- Neglecting availability during design creates single points of failure.
- Assuming backups equal integrity ignores the risk of silently corrupted data.
Balancing all three pillars—confidentiality, integrity, and availability—provides a resilient security posture that can adapt to evolving threats.