Beyond the magic number
The pursuit of arbitrary step counts often obscures a more fundamental question: what are we actually trying to achieve? Movement isn't a one-size-fits-all prescription. For some, covering several kilometers outdoors is a meditative ritual; for others, it is a deliberate strategy for metabolic health and longevity.
Rather than chasing a universal figure that lacks rigid physiological backing for every individual body, exercise physiologists emphasize consistency, intensity, and sustainability. The distinction lies not merely in the distance covered, but in how seamlessly movement integrates into your daily rhythm.
The comprehensive framework of GDPR's core mandates
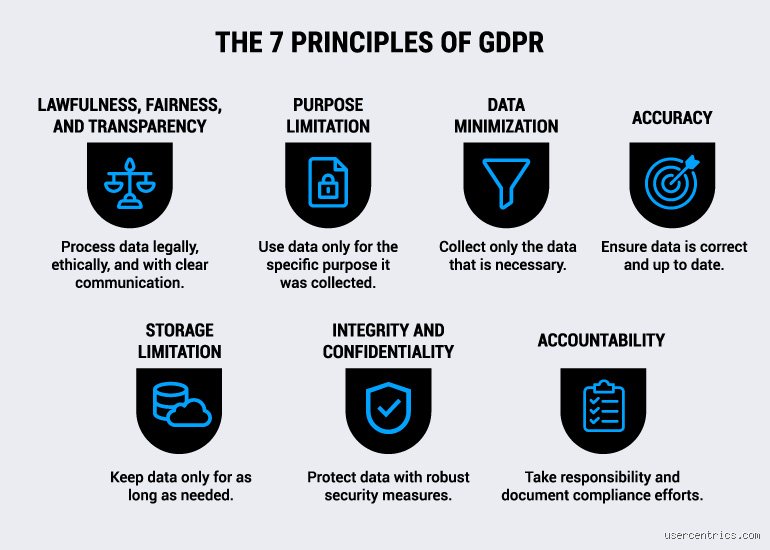
Building upon the foundational overview of the General Data Protection Regulation (GDPR), understanding how these requirements translate into daily operations is critical for any entity handling European personal data. Governed primarily by Article 5 of the regulation, there are precisely seven key principles that dictate the lawful treatment of personal data.
The continuation of this expert analysis explores the remaining principles, operational compliance strategies, and the severe implications of non-compliance.
Deep dive into the seven core principles
While the first three principles—Lawfulness, Fairness, and Transparency—set the baseline for how data collection begins, the remaining four pillars ensure that data is managed responsibly throughout its lifecycle.
4. Accuracy
The accuracy principle mandates that personal data must be accurate and, where necessary, kept up to date. Every reasonable step must be taken to erase or rectify inaccurate data without delay, considering the purposes for which it is processed.
Operational Impact: Organizations cannot rely on static databases if information changes frequently. Implementing self-service user profiles and routine data-cleansing schedules helps maintain compliance.
The Risk: Inaccurate data can lead to flawed automated decisions or wrongful actions against a data subject, triggering rights to rectification and potential compensation claims.
5. Storage Limitation
Under this rule, personal data can only be kept in a form that permits identification of data subjects for no longer than is necessary for the purposes for which the personal data are processed.
Operational Impact: Companies must establish strict data retention policies. Once the original purpose has been fulfilled, information must be securely deleted, anonymized, or archived.
The Risk: Indefinite data hoarding increases vulnerability during data breaches and directly violates European privacy mandates.
6. Integrity and Confidentiality (Security)
Often referred to as the security principle, Article 5(1)(f) requires personal data to be processed in a manner that ensures appropriate security. This includes protection against unauthorized or unlawful processing and against accidental loss, destruction, or damage, using appropriate technical or organizational measures.
Technical Measures: End-to-end encryption, pseudonymization, multi-factor authentication, and robust firewall barriers.
Organizational Measures: Employee cybersecurity training, strict access control hierarchies, and vetted vendor agreements.
7. Accountability
Accountability is the capstone principle of the GDPR. Unlike the preceding six rules which govern how data is handled, accountability states that the data controller is responsible for, and must be able to demonstrate compliance with, all the preceding principles.
Demonstrating Compliance: Documentation is everything. Organizations must maintain comprehensive Records of Processing Activities (ROPA), execute Data Protection Impact Assessments (DPIAs) for high-risk processing, draft explicit data processing agreements with third-party vendors, and potentially appoint a Data Protection Officer (DPO).
Practical implementation: Privacy by Design and Default
To effectively satisfy these seven principles, organizations operationalize two core concepts embedded within the regulation:
Privacy by Design: Embedding data protection considerations directly into the development stages of any new product, system, or business process rather than treating it as an afterthought.
Privacy by Default: Ensuring that default settings are automatically privacy-friendly. For instance, a newly created social media account should automatically restrict public profile visibility to the highest privacy tier without requiring manual user toggles.
The Cost of Non-Compliance
Failing to respect these seven principles carries severe regulatory consequences. Supervisory authorities possess the power to issue corrective measures, temporary or permanent bans on data processing, and staggering administrative fines.
Violations of the core principles under Article 5 can result in fines of up to €20 million or 4% of the enterprise's total worldwide annual turnover from the preceding financial year, whichever is higher. Beyond monetary penalties, the reputational fallout and loss of consumer trust can permanently impair an organization's market viability.
Conclusion
Navigating the GDPR landscape requires viewing personal data not as corporate property, but as a temporary trust granted by individuals. By embedding the seven key principles into the organizational DNA, from initial collection through secure storage to final deletion, businesses transform data protection from a legal checkbox into a profound competitive advantage.